
ABCD ransomware: what it is and how to restore .abcd files
ABCD ransomware is the first version of LockBit:
- it encrypts your files
- adds
.abcdto their names - leaves
Restore-My-Files.txt
No free decryptor for .abcd files is listed, so backups are the way back; do not pay.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Before you restore backups, a full scan can confirm the program that added .abcd is gone.
Do it yourself · free Remove ABCD ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps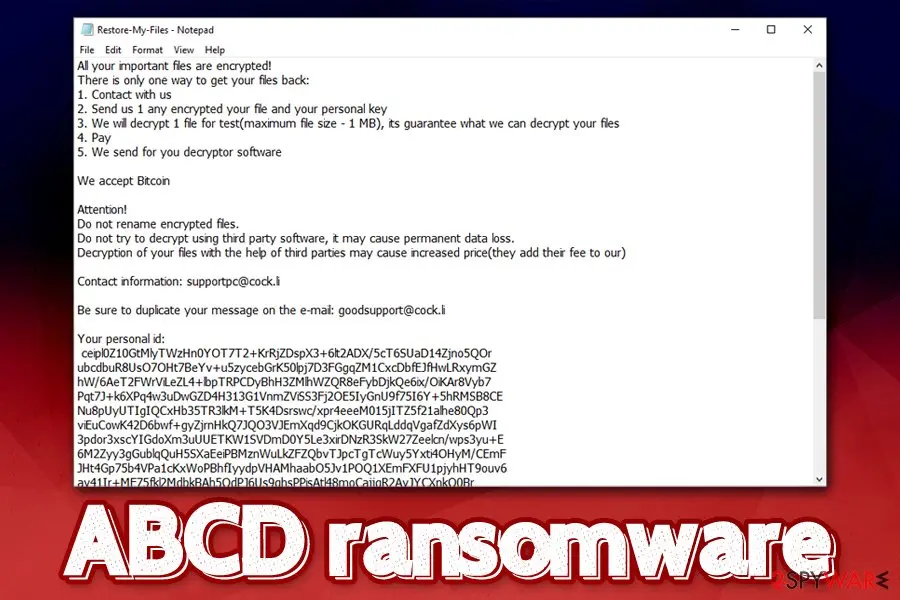
ABCD ransomware: summary
| Type | File-encrypting ransomware (AES), the first version of LockBit |
|---|---|
| Risk | High: files on the PC and network drives are encrypted, and no free decryptor for .abcd is listed |
| Symptoms | Files renamed name.ext.abcd, Restore-My-Files.txt in most folders |
| How to get rid of it | Disconnect, copy the encrypted files, scan in Safe Mode with Microsoft Defender, close Remote Desktop, change passwords; see the plan |
| Our check | Source check on 6 October 2026 (Akamai, Intel 471, CISA, No More Ransom); we did not run the malware |
| First seen | September 2019 (Intel 471); our first report 19 December 2019 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 13 more facts
| Name | ABCD ransomware, also LockBit 1.0 |
|---|---|
| Encrypted file extension | .abcd, for example picture.jpg.abcd |
| Ransom note | Restore-My-Files.txt, quoted below |
| Decryptor | None listed for .abcd; a LockBit 3.0 one exists on No More Ransom, not confirmed for .abcd |
| Contact | supportpc@cock.li and goodsupport@cock.li; other versions used other addresses |
| Distribution | Mostly weakly protected Remote Desktop; also phishing, unpatched software and stolen accounts |
| Damage | Files encrypted, shadow copies deleted, backups on connected drives at risk |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Encrypted files | .abcd |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| Microsoft Defender name | Ransom:Win32/LockBit.A!MTB |
| Detection names | Microsoft: Ransom:Win32/LockBit.A!MTB |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Akamai's LockBit glossary, Intel 471's LockBit report, CISA's LockBit 3.0 advisory, the No More Ransom tools list and our own 2019 screenshots. We did not run the malware.
What ABCD ransomware is
ABCD ransomware is the first version of what became LockBit: a Windows file encryptor that adds .abcd to your files and leaves Restore-My-Files.txt in the folders, and no free decryptor for .abcd files is listed today.
Our 2019 guide called it a variant of MegaCortex and LockerGoga. Akamai and Intel 471 both say it is the early form of LockBit instead, so this page follows them.
- Also called
- LockBit 1.0, the ".abcd" ransomware (Intel 471, Akamai)
- First seen
- September 2019 (Intel 471); our report on 19 December 2019 says mid-October 2019
- Extension
.abcd, for examplepicture.jpg.abcd; later versions use.lockbit- Note
Restore-My-Files.txt, dropped in most folders- Encryption
- AES (Intel 471); the files keep their own name with
.abcdadded - Payment
- Bitcoin, arranged by e-mail; the note holds no wallet address
- Main targets
- Companies, through weakly protected Remote Desktop
How the ABCD story went
September 2019
First seen
Intel 471 dates the first LockBit sightings to September 2019, when files were still renamed
.abcd.Mid-October 2019
Companies start reporting it
Our guide said it had been hitting companies worldwide since mid-October 2019. Encrypted files looked like this in File Explorer.
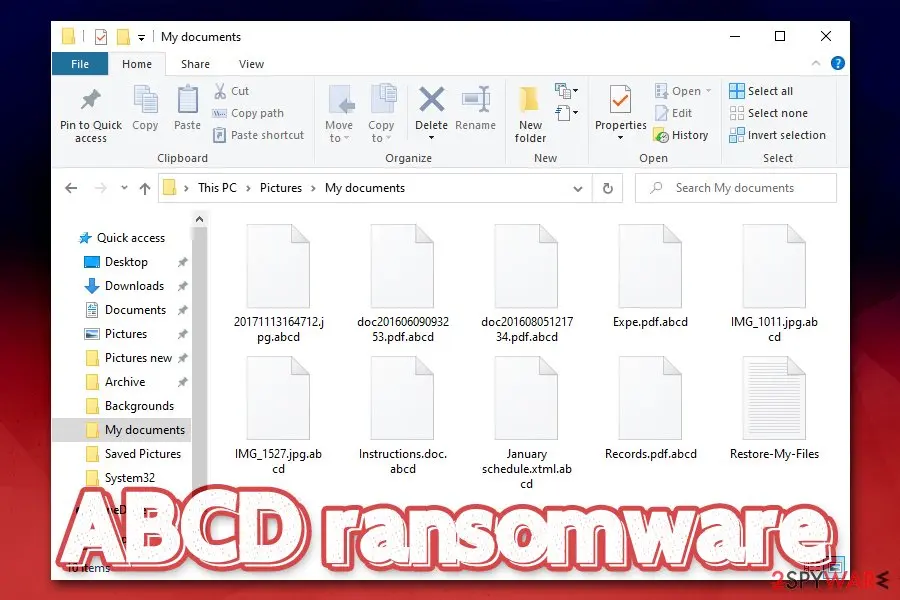
Our 2019 screenshot of a folder after the attack: every file has .abcdadded to its name andRestore-My-Filessits beside them (the title text is report artwork).19 December 2019
Our first report
We called it a variant of MegaCortex and LockerGoga that attacks through Remote Desktop. The Remote Desktop part holds up; the family claim does not.
The note and the renamed files together in our 2019 report. The woman is stock artwork, not a victim or a suspect. January 2020
The extension changes to .lockbit
Akamai dates the files renamed
.lockbitto January 2020, and CISA says LockBit has run as an affiliate service since then.June 2021
LockBit 2.0
Akamai lists version 2.0 with a built-in data-stealing tool called StealBit.
March 2022
LockBit 3.0 (LockBit Black)
CISA describes it as more modular and evasive than the earlier versions.
February 2024
Police take over the leak sites
Europol and the UK National Crime Agency announced Operation Cronos, and released a LockBit 3.0 decryptor through No More Ransom. Akamai notes the group was back within days.
What we checked and what we did not
We did not run this malware, and ABCD has no website, so there is no site test; this is a check of sources.
ABCD ransomware · source check · 6 October 2026
- FamilyAkamai and Intel 471 both name ABCD as the early form of LockBit. Our 2019 "MegaCortex and LockerGoga variant" claim was wrong.
- Ransom note textRead from our own 2019 screenshots of
Restore-My-Files.txtin Notepad. - Free decryptor for .abcdNone is listed. No More Ransom lists a LockBit 3.0 decryptor only, with no mention of
.abcd. - Does the LockBit 3.0 decryptor work on .abcd?Not confirmed. We did not test it, and the page for it does not name earlier versions.
- 2019 detailsProcess Hacker 2, startup repair, the exact
vssadminline and Dropbox deletion are not in the sources we read: unconfirmed. - The ABCD sampleWe do not have a sample, so we could not confirm file names, registry keys or hashes ourselves.
No free way back is confirmed Files encrypted with AES cannot be reversed by guessing. Only backups, or a decryptor that someone proves works on .abcd, will bring them back, and we found neither for sure.
- File extension:
.abcd - Note file:
Restore-My-Files.txt
What antivirus programs call it
Detection names change often.
The list below is what the 2019 guide read from a VirusTotal result and is only useful to confirm the right family.
| Who | Name | Where it comes from |
|---|---|---|
| Microsoft | Ransom:Win32/LockBit.A!MTB | Our 2019 report; the name already points to LockBit |
| Kaspersky-style generic | Win32.Trojan-Ransom.Filecoder.BO | Our 2019 report |
| ESET | A Variant Of Win32/Filecoder.NXQ | Our 2019 report |
| Generic detections | Win32:Trojan-gen, BehavesLike.Win32.Emotet.lh, W32.Trojan.TR.Downloader | Our 2019 report; these are generic and not specific to ABCD |
How ABCD ransomware behaves
What it does on the PC, step by step
The 2019 guide listed preparations before the encryption starts.
Some are confirmed for LockBit in general, some only come from our 2019 report, and the steps say which.
- 1
An attacker gets in, usually through Remote Desktop
Intel 471 and Akamai name phishing, unpatched software, stolen passwords and an exposed Remote Desktop port as the ways LockBit got a foothold. Our 2019 guide saw mostly the last one.
- 2
The program is started by hand
Once the executable runs, the infection routine starts. Intel 471 adds that LockBit spreads on its own to other reachable computers, without the attacker doing it machine by machine.
- 3
Defences and backups are switched off
Intel 471 reports that LockBit disables security services and deletes shadow copies. Our 2019 guide gave the command
vssadmin delete shadows /all /quiet; we have not seen that exact line in the sources we read. It also said backups in cloud storage such as Dropbox are deleted; we found no source for that either. - 4
Startup repair is disabled
Our 2019 guide said Windows startup repair is turned off. Not confirmed in any source we read.
- 5
A legitimate tool is installed
The 2019 guide said Process Hacker 2, a system monitor, was installed on infected machines. Not confirmed in any source we read; treat it as a clue only if you find it.
- 6
Files are encrypted on the PC and on network drives
AES is used on local and network files; system and executable files are skipped so Windows keeps running. Each file gets
.abcdafter its own name. - 7
The note is dropped
Restore-My-Files.txtappears in most folders, and Intel 471 says the wallpaper is changed in LockBit attacks. Our 2019 screenshots show the note in Notepad.
What the note demands
The note is in English with the writer's own grammar.
The 2019 screenshot shows the five steps it gives, and the text here follows it.
| Item | What the note says | What it means |
|---|---|---|
| Proof | One encrypted file (up to 1 MB) and your personal key, sent to them, decrypted free as a test | A way to look trustworthy before the demand. The personal key is the long block of text at the bottom of the note. |
| Payment | "We accept Bitcoin" | The note holds no wallet address; it is given after you write. We do not print any. |
| Contact | supportpc@cock.li, with a copy to goodsupport@cock.li | Our 2019 guide also listed goeila@countermail.com, gupzkz@cock.li and abcd-help@countermail.com for other versions. |
| Warning | "Do not rename encrypted files" and do not use third-party software | Renaming is harmless to the encryption, but the warning is meant to keep you from trying other help. |
| Price | Not in the note | Reports collected in 2019 said as much as 3 BTC per victim, whatever the number of computers. That figure is from affected users, not confirmed by us. |
Some victims who paid said they received a working decryptor. Others cannot be known: there is no way to hold a criminal to a promise, and the next section explains why paying is a poor bet.
How ABCD reaches a network
The 2019 guide stressed Remote Desktop but said that other ways are possible.
CISA's LockBit advisory and Akamai agree, and list the same spread of entry points.
- High
Remote Desktop with a weak password
Credentials are bought on underground forums or guessed by a program that tries many passwords (Akamai, CISA). The attacker then logs in and runs the program.
- Medium
Phishing e-mails
Akamai lists phishing for LockBit. The 2019 guide named spam, fake updates and cracks too.
- Medium
Unpatched software
Akamai lists exploited software vulnerabilities, so patching remains part of the defence.
Remote Desktop: how to close the door
The old guide explained why Remote Desktop is attacked and how to protect it.
The ideas below keep its list, with the points that changed.
- 1
Do not leave port 3389 open to the internet
Reach the PC through a VPN or a Remote Desktop Gateway instead. The 2019 guide suggested changing the port; that only hides it from the laziest scans, so treat it as a minor extra.
- 2
Limit who can log in
In the Remote Desktop settings, choose who may connect (Microsoft: select users that can remotely access this PC, then Add) and remove everyone else.
- 3
Use a long, unique password and two-step sign-in
A password that cannot be guessed stops the program that tries thousands of them. CISA and Akamai both recommend multi-factor sign-in.
- 4
Turn Remote Desktop off when you do not use it
A switched-off service cannot be attacked.
- 5
Require Network Level Authentication
This makes the visitor prove who they are before a session opens. The setting is in the Remote Desktop settings; its exact menu name changes between Windows builds, so we do not quote a path.
- 6
Keep Windows updated and backups apart
General habits matter as much as this one door: patching, security software and a copy the attacker cannot reach.
Similar names and lookalikes
Several names get mixed up with ABCD, and following the wrong instructions can cost days.
| Name | How it relates | What to do |
|---|---|---|
LockBit, .lockbit files | The later versions of the same family (Akamai, Intel 471) | Same reading of the note; LockBit 3.0 has a decryptor on No More Ransom |
| MegaCortex | Intel 471 says LockBit's methods are similar; we have no source that .abcd is MegaCortex | Do not use MegaCortex tools on .abcd files |
| LockerGoga | Same remark | As above |
| STOP/Djvu files | Home-user ransomware with other extensions | Their decryptors do not apply to .abcd |
Was anything stolen?
Assume yes for any company network. LockBit's later versions copy files out before encrypting; for .abcd we cannot say.
- Medium
Passwords and accounts
Attackers who log in over Remote Desktop can read what the account sees. Change the passwords of every account used on that PC, from a clean device.
- Medium
Files copied out
Intel 471 says important data was uploaded to services such as MEGA before encryption in LockBit attacks. The 2019 note makes no data-leak threat.
- Low
Other computers on the network
Our 2019 guide said it tries to infect all connected computers and servers, and Intel 471 says it spreads by itself. Check them before you reconnect.
What to do in the first hour
Do not start copying or deleting yet: first stop the attack from spreading, then protect the evidence.
- 1
Disconnect from the network
Pull the cable or turn off Wi-Fi on this PC, and on any computer showing
.abcdfiles. The malware reaches network drives. - 2
Turn off remote access
Close Remote Desktop to the internet at the router, and change the password of every account that could log in.
- 3
Photograph the note
Take a photo of the screen and keep
Restore-My-Files.txt; you will need the personal key text if a decryptor appears. - 4
Copy the encrypted files
Copy them to an external drive before you remove anything, then unplug the drive.
- 5
Boot into Safe Mode with Networking and scan
The 2019 guide advised this because the program may interfere with security software. Run a full Microsoft Defender scan; the plan below gives the Windows 11 and Windows 10 steps.
- 6
Do not rely on System Restore to remove it
The 2019 guide offered System Restore as a removal method. It restores system files, not your documents, and ransomware often deletes its restore points, so use it only as an extra.
The ABCD ransomware note
All your important files are encrypted!
There is only one way to get your files back:
1. Contact with us
2. Send us 1 any encrypted your file and your personal key
3. We will decrypt 1 file for test (maximum file size - 1 MB), its guarantee what we can decrypt your files
4. Pay
5. We send for you decryptor software
We accept Bitcoin
Attention!
Do not rename encrypted files.
Do not try to decrypt using third party software, it may cause permanent data loss.
Decryption of your files with the help of third parties may cause increased price (they add their fee to our)
Contact information: supportpc@cock.li
Be sure to duplicate your message on the e-mail: goodsupport@cock.li
Your personal id: [a long block of text, left out here]
Can ABCD ransomware files be decrypted?
Can .abcd files be restored?
Not by anything we can promise: AES encryption has no shortcut, and no decryptor for .abcd is listed on No More Ransom. The old guide said the same, and it still holds.
There is one thing to check. After Operation Cronos in 2024, No More Ransom added a LockBit 3.0 decryptor. It is meant for version 3.0 and its page does not mention .abcd, so do not count on it, but it costs nothing to read its guide.
- 1
Copy the encrypted files first
Copy files ending
.abcdandRestore-My-Files.txtto a USB drive or a second disk. Removing the malware can change the files, as the old guide warned, and a copy is your insurance. - 2
Keep one sample and the note
A decryptor, if one appears, needs a pair: an encrypted file and its original. Keep an encrypted file under 1 MB and a photo of the note.
- 3
Read the No More Ransom page
Open nomoreransom.org, then Decryption Tools, and search for LockBit. Read the how-to guide before you download anything. Never use a decryptor from a website you reached through an ad.
- 4
Check later
Researchers sometimes publish keys years later, as happened for LockerGoga and MegaCortex in 2022. We do not know of one for
.abcd.
Should you pay the ransom?
No. The 2019 guide said some victims who paid received a working decryptor, others were asked for more, and users reported demands of up to 3 BTC whatever the size of the network.
- High
You pay and get nothing
The decryptor is sold by the same people who locked the files; nothing makes them answer you.
- High
You are marked as a payer
Paying tells the criminals that your network gives money, and it supports the next attack.
- Medium
The malware stays
A decryptor does not remove the way in. Without closing Remote Desktop, the same people can come back.
How to remove ABCD ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove ABCD ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so ABCD ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
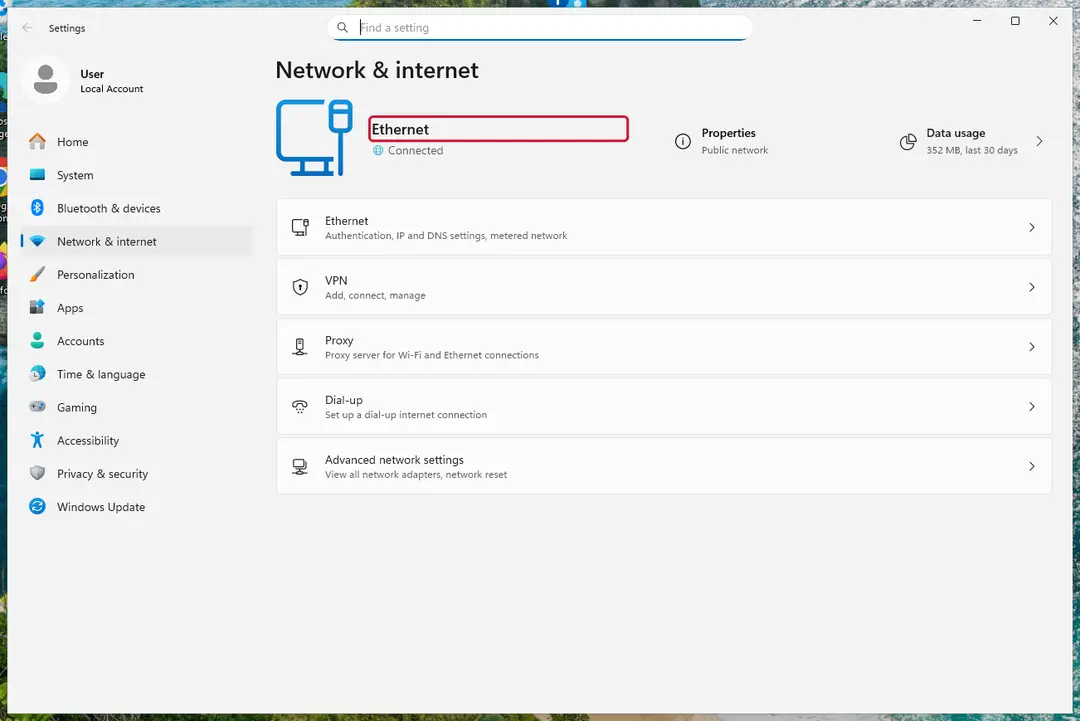
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.abcdand the instructions are inRestore-My-Files.txt. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
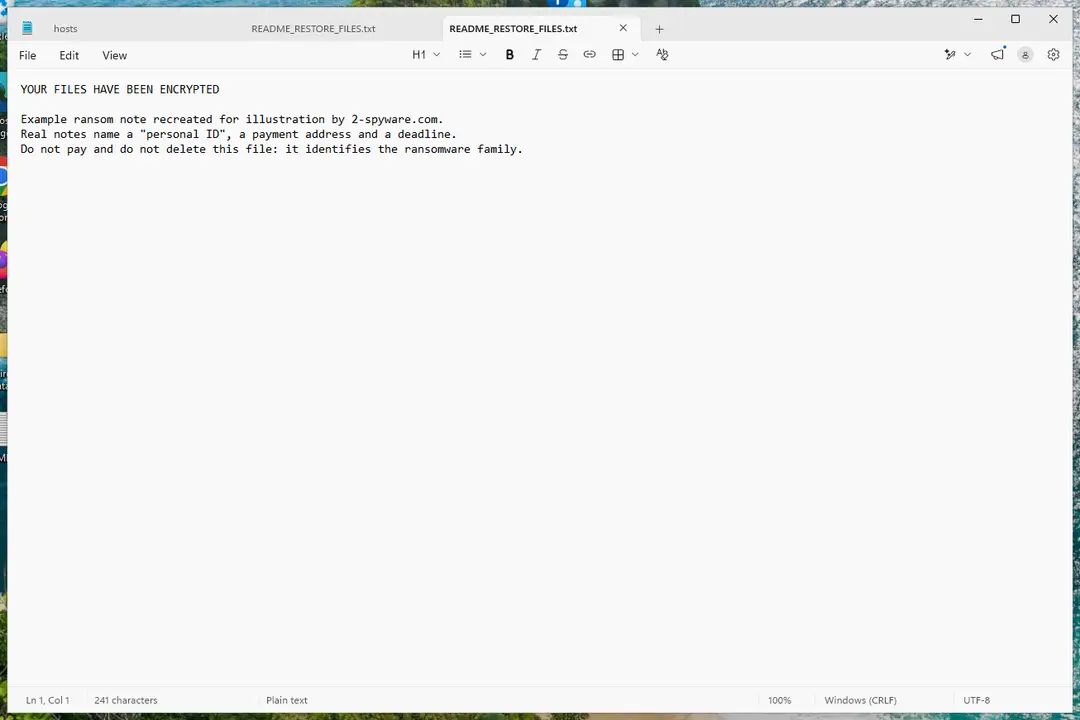
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for ABCD ransomware, no free decryptor is known (checked 6 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing ABCD ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
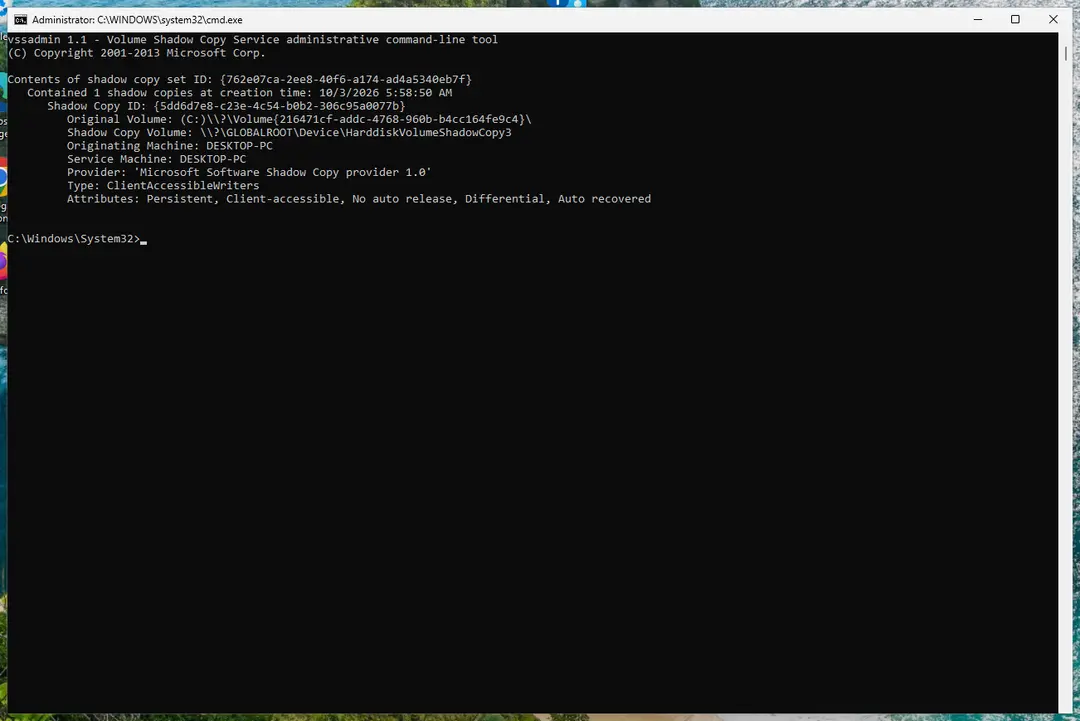
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that ABCD ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Other ways to get files back
If no backup exists, these are the options the old guide listed.
They are partial: always work on copies.
- 1
Your own backups
An external drive, a NAS or cloud storage that was not connected during the attack is the only fully reliable source. Plug it in only after the PC is clean.
- 2
Previous Versions
Right-click a folder, choose Properties, then Previous Versions (on Windows 11 choose Show more options first). This works only if System Protection was on and the copies survived.
- 3
Shadow copies
Run
vssadmin list shadowsin an administrator Command Prompt. Microsoft's page says it lists existing copies. Our 2019 guide said ABCD deletes them, but where any remain, a viewer such as ShadowExplorer can open them. - 4
File recovery software
A recovery program can find the unencrypted originals that the malware deleted, if they have not been overwritten. Stop using the PC first. Results vary and the 2019 guide made no promises.
- 5
Wait for a decryptor
Researchers and police sometimes publish keys later; this happened for other LockBit versions. Keep the encrypted files and the note.
Back up with the 3-2-1 rule
The only secure and free way to get files back is a backup that the attacker could not reach.
CISA's guidance for ransomware recommends offline copies.
| Number | Rule | Example |
|---|---|---|
| 3 | Three copies of every important file | The working file and two backups |
| 2 | Two kinds of storage | Your disk and a USB drive |
| 1 | One copy offline or away from the PC | A drive in a drawer, or cloud storage with version history |
How to prevent ABCD ransomware and the next attack
The old guide said closing one door is not enough.
These habits cover the routes in this page.
Do
- Keep Windows and your software updated
- Close Remote Desktop to the internet, or protect it with a strong password, a VPN and two-step sign-in
- Keep security software on and run a full scan after anything odd
- Turn on file extensions in File Explorer (View > Show > File name extensions)
Don't
- Do not open attachments you did not expect
- Do not install cracks or fake updates
- Do not reuse one password on several accounts
Questions about ABCD ransomware
Is there a decryptor for .abcd files?
No decryptor for .abcd files is listed on No More Ransom, and AES encryption cannot be broken by guessing. The site does list a LockBit 3.0 decryptor, published after Operation Cronos in 2024, but its page does not mention .abcd and we did not test whether it works on the early version.
Keep copies of the encrypted files and the note, so that you can try a decryptor if one is shown to work. Do not trust sites that sell an ABCD decryptor, since they are a common way to deliver more malware.
Should I pay the ABCD ransom?
No, we do not recommend paying. Some victims in 2019 said they received a working decryptor after paying, but there is no way to hold criminals to a promise, and affected users reported demands of up to 3 BTC whatever the size of the network.
Paying also shows the attackers that your network pays, and it does not close the Remote Desktop hole they used. Keep the note, report the attack to the police, and try your backups and the recovery options first. Some people with no backup have no other choice, and that is their decision.
How did ABCD ransomware get onto my computer?
Most likely through Remote Desktop. Attackers buy stolen logins or guess passwords with software, sign in and run the program themselves. Akamai and Intel 471 list other routes for LockBit:
- phishing e-mails
- unpatched software
- stolen VPN accounts
Our 2019 guide also named spam, fake updates and software cracks. Check which of these your network has left open, because closing one door is not enough. The program is not something a web page can install by itself.
Is ABCD the same as LockBit, MegaCortex or LockerGoga?
ABCD is the same as LockBit: it is the first version of that family. Intel 471 calls LockBit "previously known as the .abcd ransomware", and Akamai says the first version used the .ABCD extension. Files were renamed .lockbit from January 2020, with LockBit 2.0 in 2021 and 3.0 in 2022.
MegaCortex and LockerGoga are different families; Intel 471 only says their methods are similar, and our 2019 "variant" claim was wrong. Use tools meant for the name on your files, and check the extension before you download anything.
How do I open .abcd files?
You cannot open .abcd files: they are encrypted with AES, and renaming them back to .jpg or .docx does not decrypt anything. Windows will not know a program for the extension.
If you have a backup, restore the original files from it after the PC is clean. Otherwise keep the .abcd copies safe, because a decryptor might be published later. Do not download an .abcd converter or opener; such sites are a common way to spread more malware.
Do paid decryption services work for ABCD files?
We found no evidence that they do. Paid services that promise to unlock .abcd files either pay the attackers on your behalf, which adds their fee to the ransom, or sell nothing at all. The ABCD note itself warns that third parties "may cause increased price", which is the attackers protecting their business.
The one route we know to be free and honest is No More Ransom, run by Europol and partners, where nothing costs money. Ask what a service will do for you before you send any file or payment.
Was data stolen in an ABCD attack?
Assume it could have been for any company network, though we cannot say for the early .abcd version. Intel 471 says that in LockBit attacks important files were uploaded to services such as MEGA before the encryption, and later versions threaten to publish them.
The ABCD note in our 2019 screenshots makes no such threat. Anyone who logged in over Remote Desktop could read what that account saw, so change the passwords of every account used on the infected PC from a clean device.
Will Fortect remove ABCD ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For ABCD ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Akamai: What is LockBit ransomware? (read October 6, 2026)
- Intel 471: LockBit ransomware (read October 6, 2026)
- CISA: #StopRansomware: LockBit 3.0 (read October 6, 2026)
- No More Ransom: decryption tools (read October 6, 2026)
- Europol: Law enforcement disrupt world's biggest ransomware operation (read October 6, 2026)
- US Department of Justice: LockerGoga, MegaCortex and Nefilim administrator charged (read October 6, 2026)
- Microsoft Learn: vssadmin list shadows (read October 6, 2026)
- Microsoft Learn: Enable Remote Desktop on your PC (read October 6, 2026)