
Brkdown.com e-mail scam on Mac: how to spot it and what to do
Brkdown. com is a malicious website that you could encounter at any time when browsing the web via Google Chrome, Mozilla Firefox, MS Edge, or another web browser. While the web page could be encountered on all platforms, iPhone or Mac users are the ones who are most commonly targeted.
Facts checked October 7, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
Do it yourself · free Remove Brkdown.com e-mail scam yourself 5 steps, about 15 minutes, no software needed.
Start the steps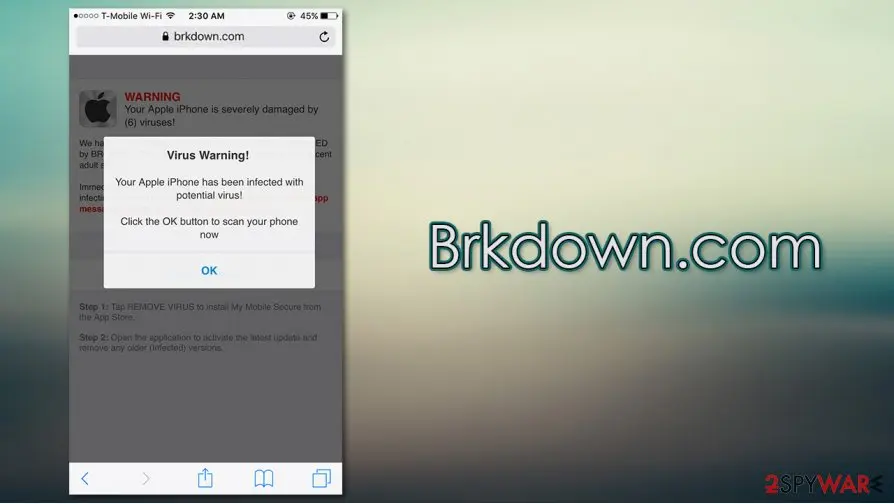
Brkdown.com e-mail scam: summary
| Distribution | The popups and redirects to the site can be encountered after clicking on a malicious link or after being redirected by adware or another potentially unwanted program |
|---|---|
| Name | Brkdown.com |
| Type | Phishing, scam, fake alert |
| Claim | The message says that malware was found on the device, and that the login credentials of Facebook and other social networks, personal photos, and other sensitive data will be stolen |
| Goal | The main goal is to make users download a suspicious application for the fake virus elimination |
| Related | Your Apple iPhone is infected, Your system is infected with 3 viruses |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Symptoms | A phishing e-mail asking you to sign in |
|---|---|
| Evidence | 4 write-ups by security sites; details still limited |
| Arrives as | |
| Pretends to be | |
| Asks for | Your password |
| First seen | 20 November 2020 |
| Facts checked | 7 October 2026 |
What the Brkdown.com e-mail scam e-mail looks like
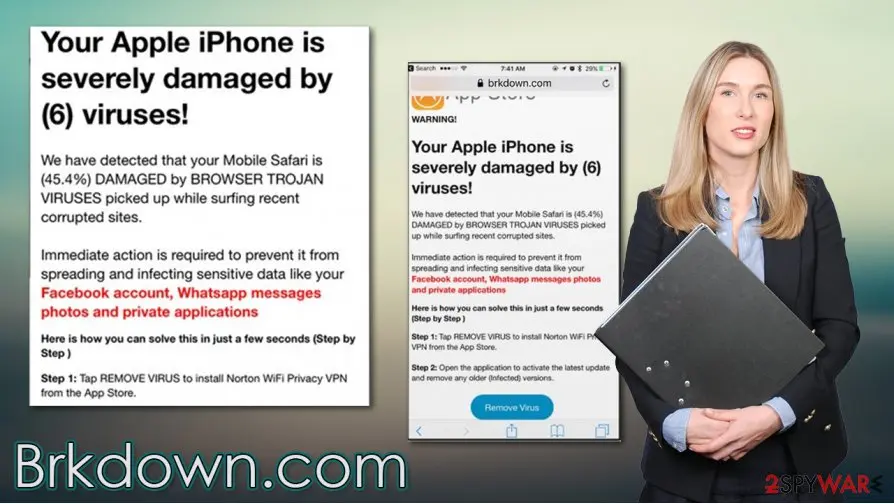
Your Apple iPhone is severely damaged by 19 viruses!
We have detected that your Browser is (59%) DAMAGED by BROWSER TROJAN VIRUSES picked up while surfing recent corrupted sites.
Immediately install mobile security application or sensitive data like your Facebook account, WhatsApp messages, photos and private applications will be infected and stolen.
How to tell the Brkdown.com e-mail scam e-mail is fake
From our report of Nov 2020 · not reviewed since
As mentioned above, adware could be one of the main causes you see scams on your device.
These PUPs might take over the web browser and inserts ads everywhere. Unfortunately, some of those ads or redirects might be deceptive and, in some cases, even dangerous. Therefore, it is best to ensure that your phone or desktop computer is adware-free. For that, consider practicing the following:
Online scams might also be encountered randomly on thousands of malicious websites. Therefore, it is important to recognize them not to be tricked. As previously noted, phishing and scam sites are often used to make users download malicious software, provide sensitive information, or waste money on useless apps. Never downloads anything from sites that claim your device is infected with malware - they can not diagnose such intricacies.
Always check the URL of the page you are visiting, as it will be an unknown address that has nothing to do with official sources such as Apple.
- If possible, only download apps from official sources (App Store, Google Play, etc.);
- Never visit torrent or similar sites that distribute software cracks or pirated application installers;
- During the installation of third-party software, always opt for Advanced/Custom settings instead of Recommended/Quick ones - it will let you stay in control of the process;
- Remove all the ticks from the pre-ticked boxes, read the fine print, and watch out for misplaced buttons.
Is Brkdown.com e-mail scam dangerous? What the senders want
From our report of Nov 2020 · not reviewed since
Brkdown.com is a scam site you should never download software from
Brkdown.com is a malicious website that you could encounter at any time when browsing the web via Google Chrome, Mozilla Firefox, MS Edge, or another web browser.
While the web page could be encountered on all platforms, iPhone or Mac users are the ones who are most commonly targeted. The website is known to promote all sorts of fake claims and scams with the intention to make users download potentially dangerous software on their devices.
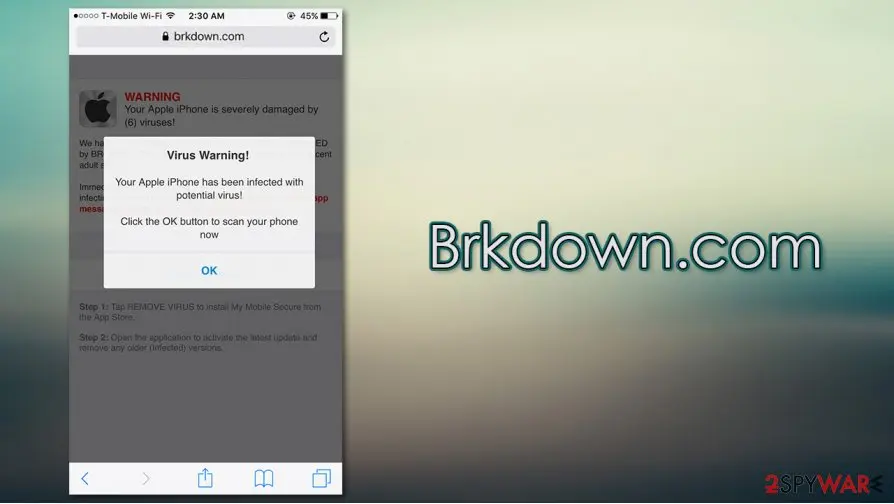
The Brkdown.com popup claims that "they" (whoever they are) have detected a number of Trojans, viruses, and other malware on the device due to browsing of "corrupted sites." According to the message, the offered security application needs to be installed in order to prevent theft of sensitive data, such as Facebook/WhatsApp logins and private messages, as well as photos located on the device.
It is important to note that no websites can detect malware on your system, hence Brkdown.com is a scam and should never be trusted.
First of all, before understanding the goals and principles of the Brkdown.com scam operation, it is important to know how you can get there. Without a doubt, you did not type in the web address to land on the site.
However, you are likely to be redirected to it after visiting a suspicious website (torrents, video-streaming, gambling, X-rated, and similar). These automatic redirects are typically executed thanks to JavaScript or other background processes.
You might also encounter the Brkdown.com virus alert after clicking on a link.
In some rare cases, you might be infected with adware - a variation of a potentially unwanted program category, which specializes in browser takeover, redirects to suspicious websites, intrusive ad campaigns, as well as background information tracking for marketing purposes. Thus, if Brkdown.com redirect is persistent, you should either check for PUPs manually or scan the device with powerful anti-malware, such as or .
However, please keep in mind that all the claims you see on the message that is shown to you on the site it bogus - Trojans and other malicious programs are unlikely to reside on your device. Even if so, it would not be related to this "detection," as websites generally can't detect and diagnose infections of the device.
Upon Brkdown.com entry, you might encounter several different variations of the scam. Here is an example that promotes the "Your Apple iPhone is infected" scam:
The Brkdown.com popup looks very plain, although it does include the Apple devices' settings logo, which might make some people think that the message is legitimate. The first red flag is that the pop-up is not coming from an official source. It also attempts to intimidate users by applying a timer, creating a sense of urgency.
Do not worry, your social media accounts are safe. However, you should remove Brkdown.com popup by simply closing down the web page immediately. No matter what you do, do not download and install the promoted applications, as it could easily result in malware infections.
If you did install something, Brkdown.com removal might become a bit more difficult. First of all, you should check the installed program section of your device. However, the best way to eliminate all potentially malicious software is by scanning your Mac or another device with , , or another reputable software. To remediate the system, experts also recommend using .
From our report of Nov 2020 · not reviewed since
Eradicate Brkdown.com scam pop-ups for good
First of all, it is important to note that if you saw the Brkdown.com virus notification for the first time, you should not panic and simply close down the tab or the web browser. However, if you downloaded and installed software suggested to you after being intimidated by the message, Brkdown.com removal would work slightly differently.
First of all, if you are using an iPhone, go to Settings > Safari and then enable Block Pop-ups and Fraudulent Website Warning feature. This will prevent websites from showing you scam notifications in the future.
Now, you should ensure that your system is safe and not infected. For that, you can either visit the installed app section of your device and look for inconsistencies. If you are not quite sure what you are doing, you should instead rely on powerful security tools - they could remove Brkdown.com scam leftovers and all the associated malicious programs within just a few minutes.
How to get rid of Brkdown.com on a Mac
Close the page safely and stop it coming back.
If you called, paid or let someone in, the last steps matter most.
Step 1: Close the page without touching its buttons
Nothing on the Brkdown.com page is safe to click: its buttons only open more pages or start a download.
Quit the browser with Command + Q, or with Command + Option + Esc > Force Quit if it will not close. Start Safari again while holding Shift, so it does not reopen the same tabs.
Step 2: Remove the site's permission to send notifications
In Safari open Settings > Websites > Notifications and remove any site you do not know, or set it to Deny. In Chrome open
chrome://settings/content/notifications, in Firefox Settings > Privacy & Security > Notifications > Settings. Then check System Settings > Notifications for browser alerts you did not expect.Step 3: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 4: If you called, paid or gave access
If you called the number on the page, let someone connect to the Mac, or paid, act now. Remove any remote access app they asked you to install from the Applications folder, then change your e-mail and bank passwords from another device.
Call your bank or card issuer, tell them it was a scam and ask to block or dispute the payment. Apple does not show alerts with phone numbers in a browser and does not ask for payment to fix a Mac.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 5: Report it and watch your accounts
Report the site and the command to the authorities in your country, and tell your bank if any card was saved in a browser or in Keychain.
Over the next weeks watch your e-mail, bank and exchange accounts for sign-ins and transfers you did not make. Keep the notes you made, such as the process names and the file dates, in case a bank or the police ask for them.
Full procedure with screenshots: Report a cyber attack or scam to the authorities
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
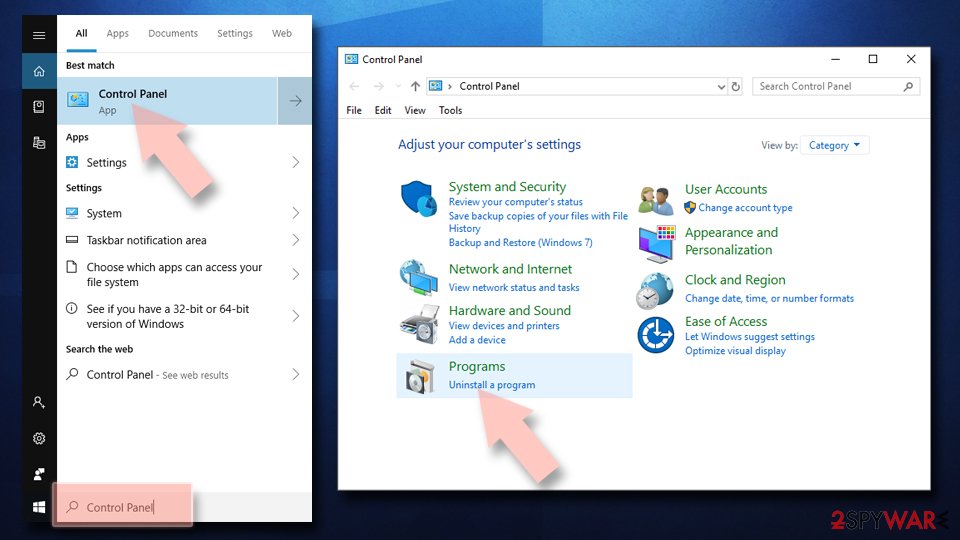
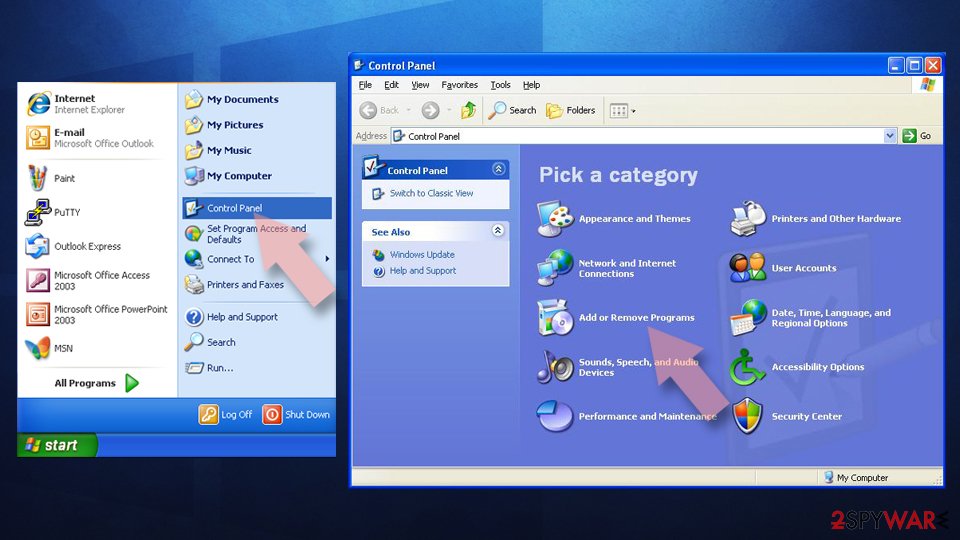
To uninstall potentially unwanted programs from Windows machines, access the Programs and Features section via the Control Panel:
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
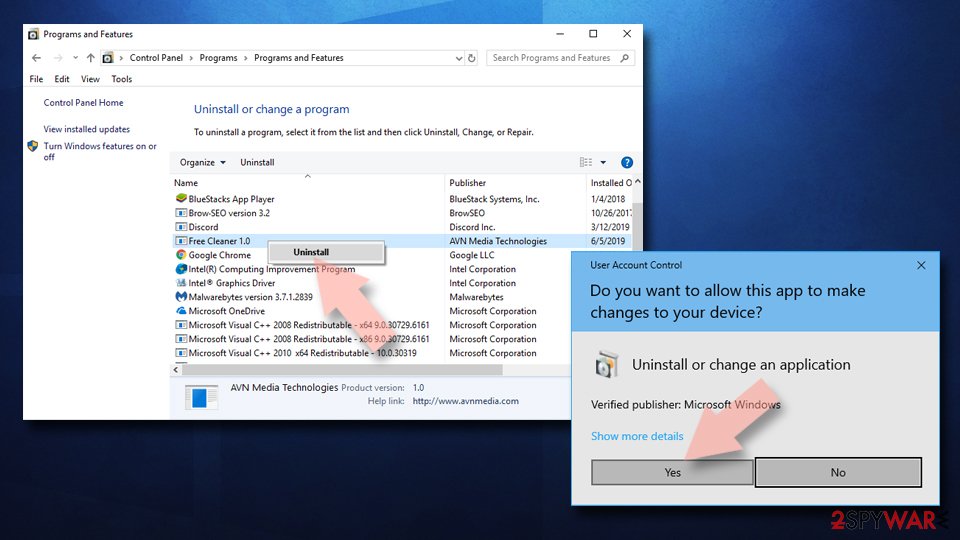
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
You should eliminate all the extensions from Chrome, as they could be the reason why you are facing redirects and ads:
Delete malicious extensions from Google Chrome:
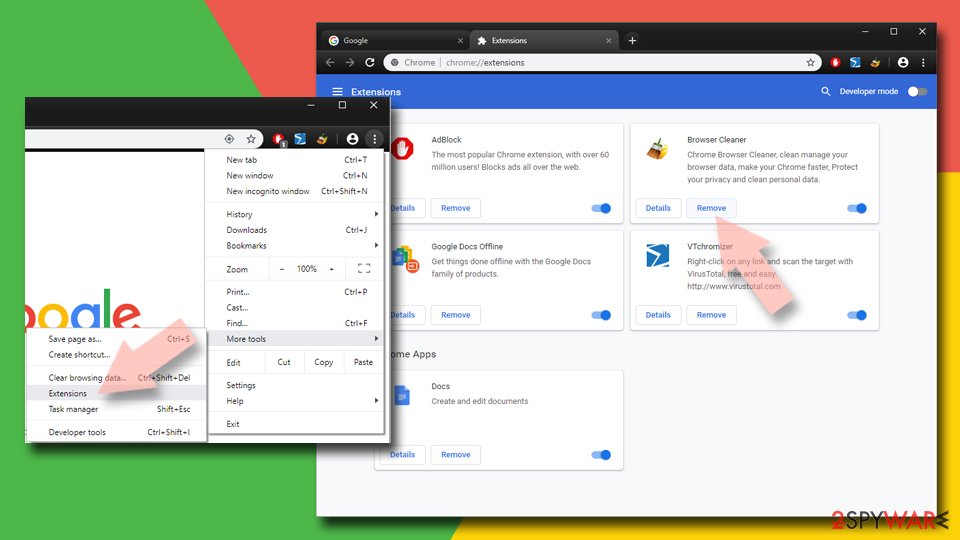
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
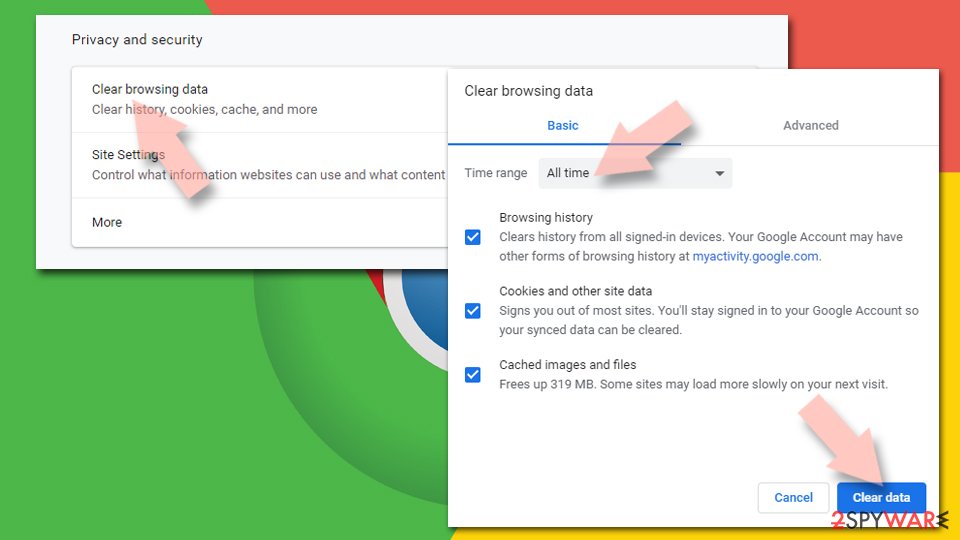
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
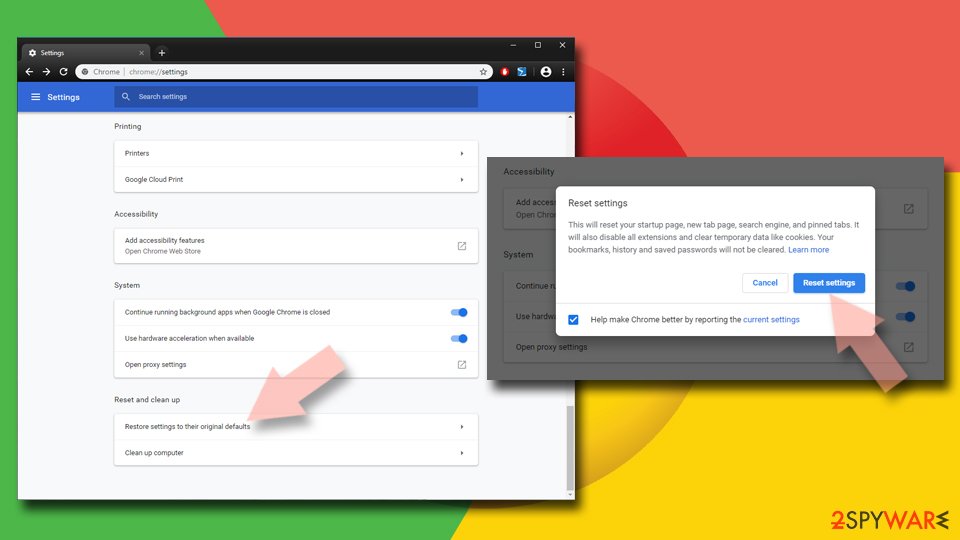
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
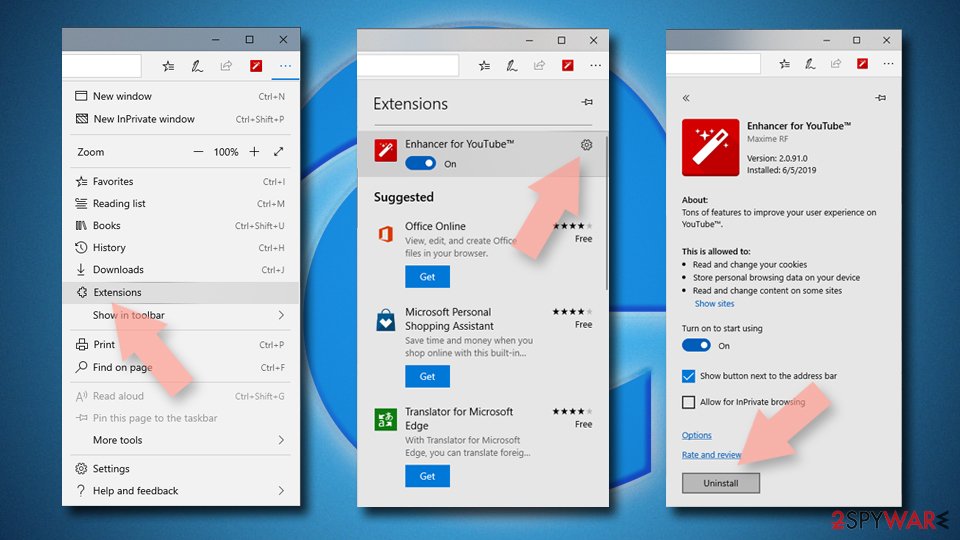
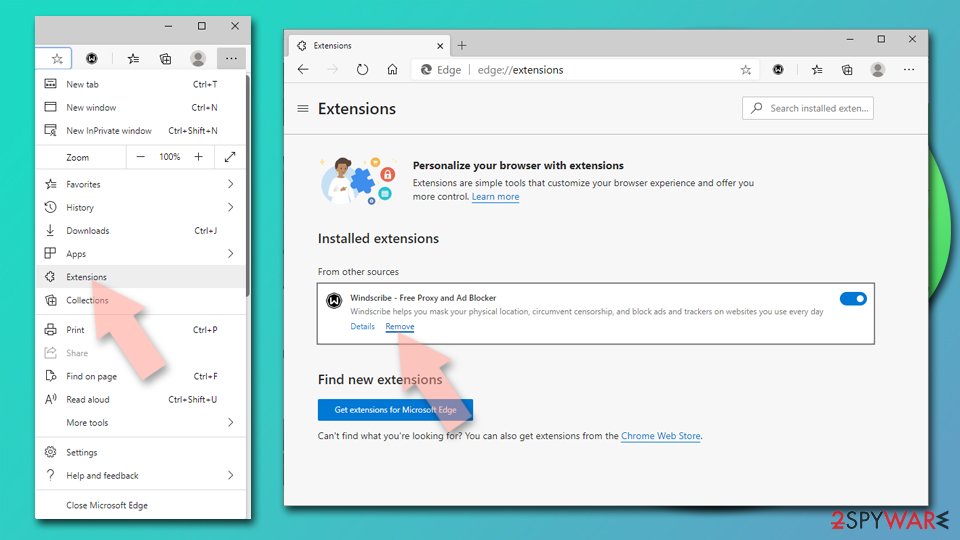
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
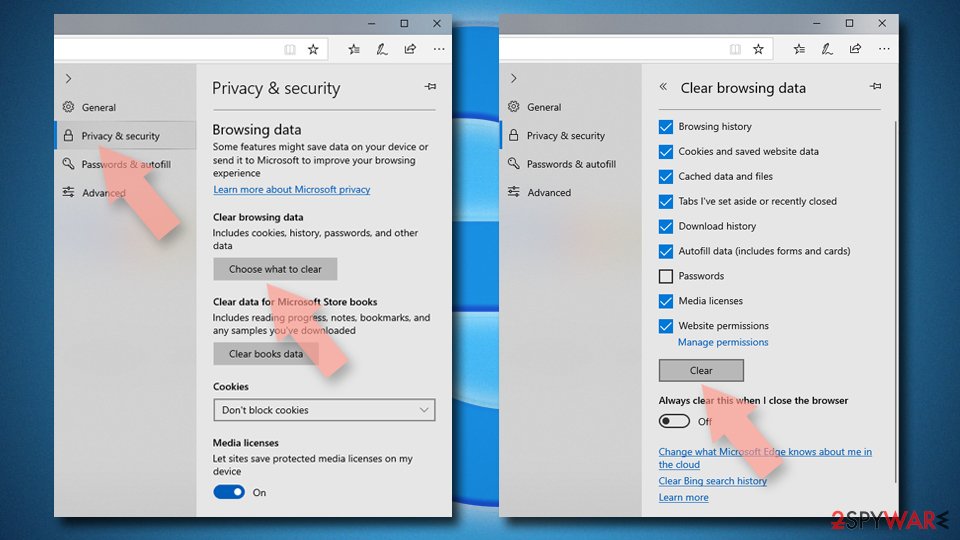
Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
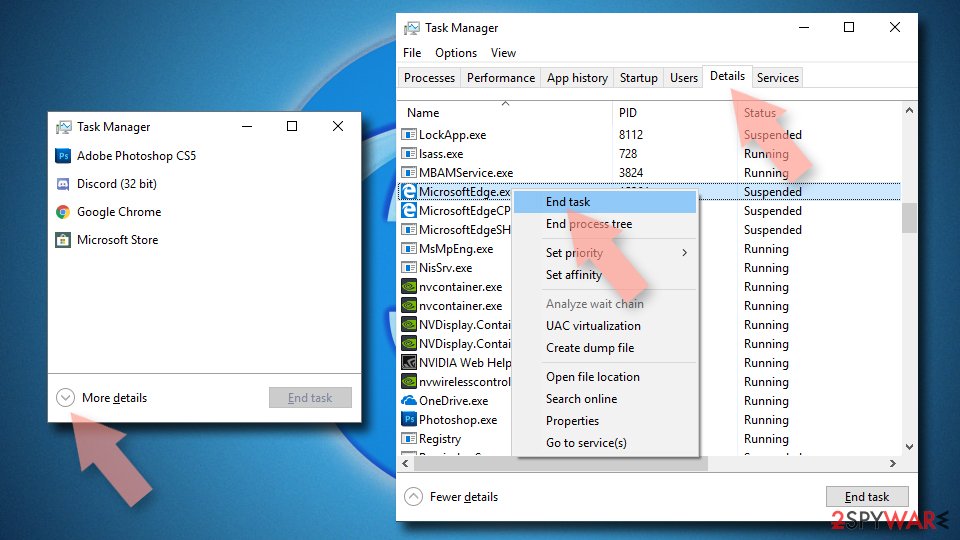
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
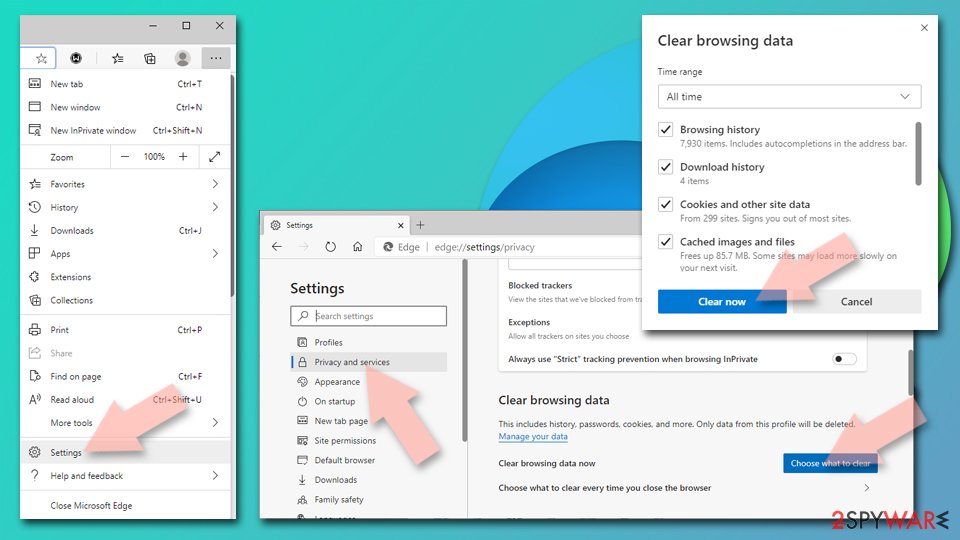
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
Reset Chromium-based MS Edge:
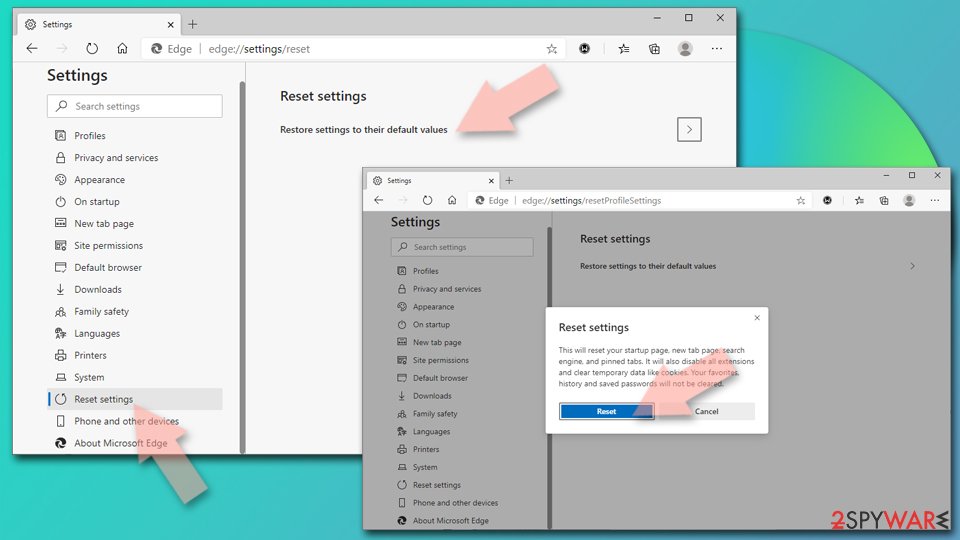
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
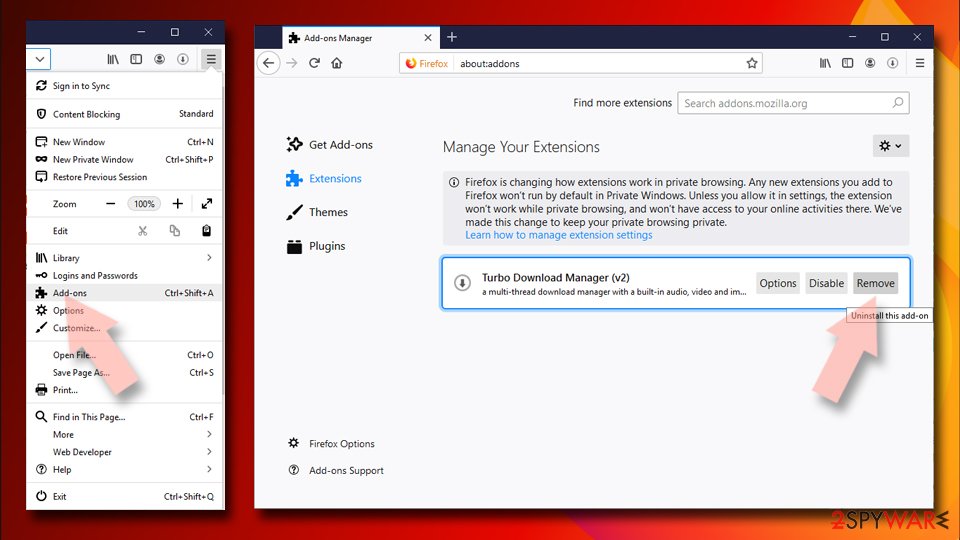
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
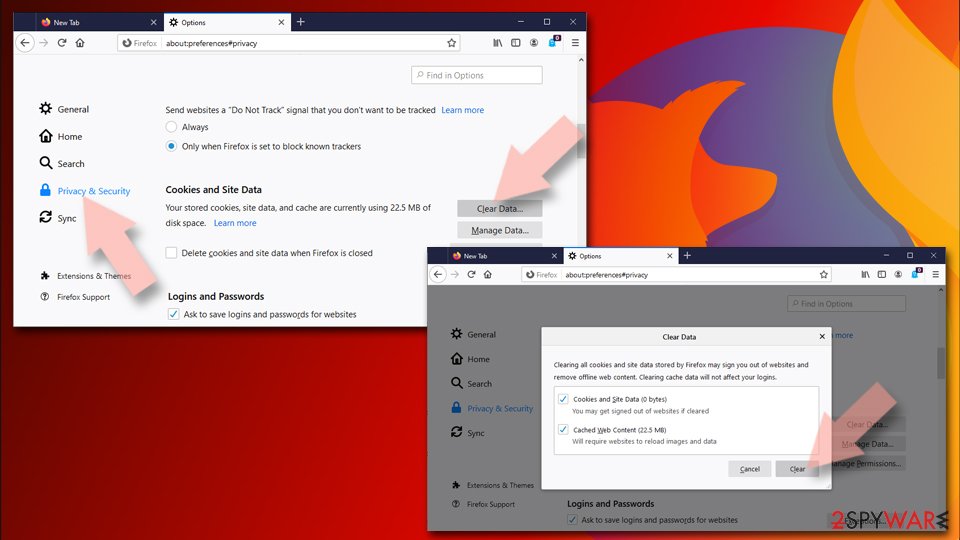
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
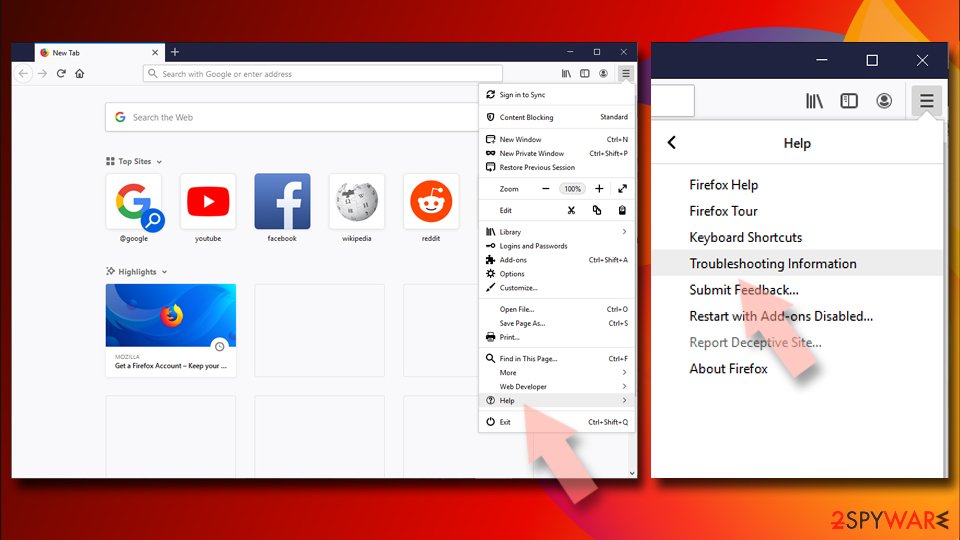
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
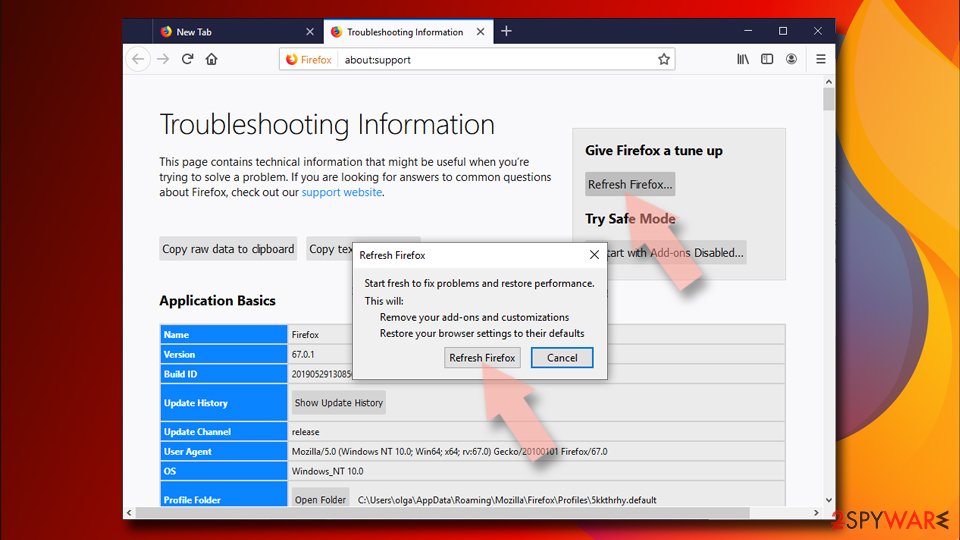
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
You can reset Safari to ensure that no suspicious settings are present on it:
Remove dangerous extensions:
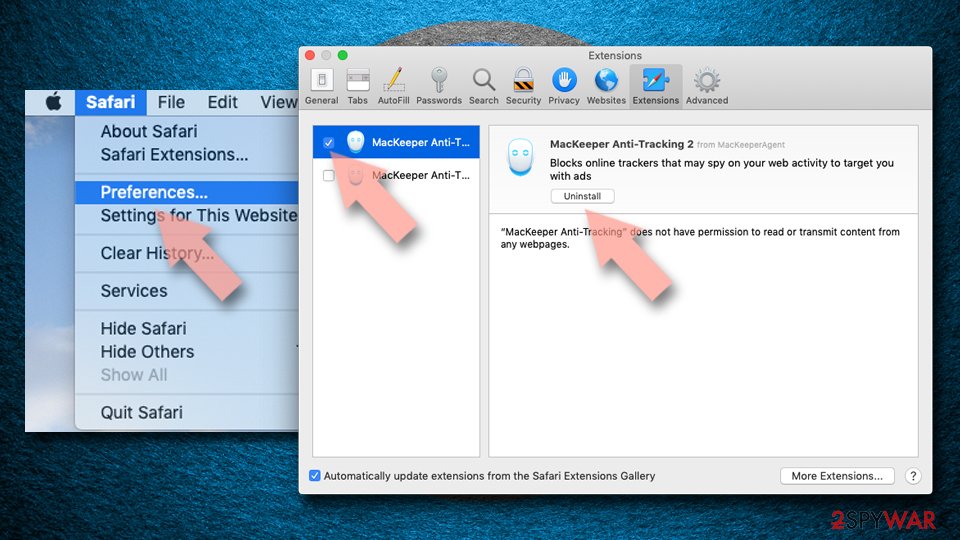
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
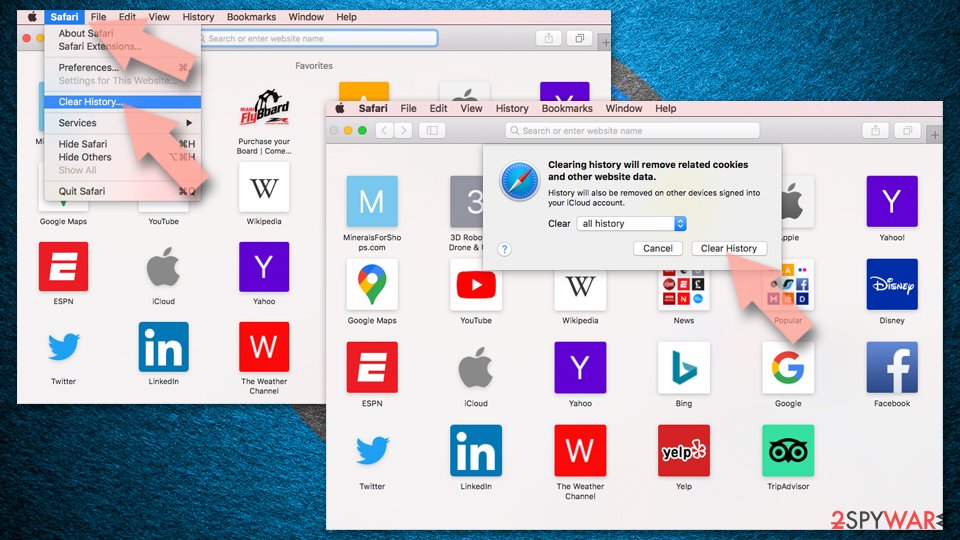
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
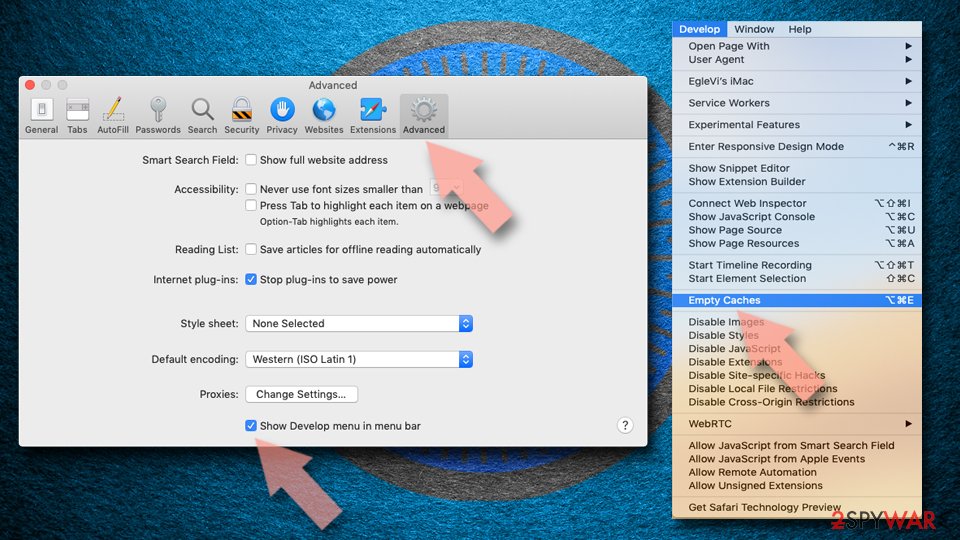
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
If your Mac is showing adware infection signs, proceed with the following instructions:
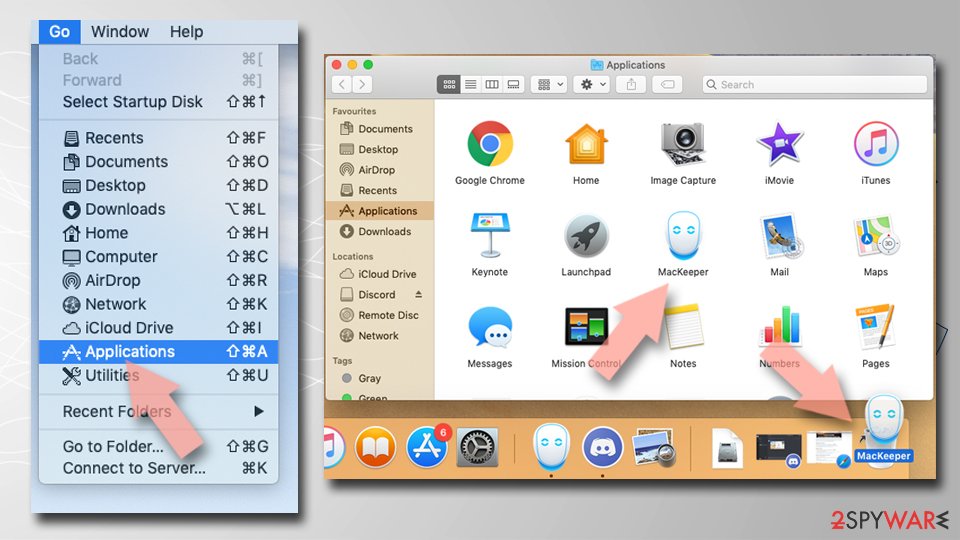
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
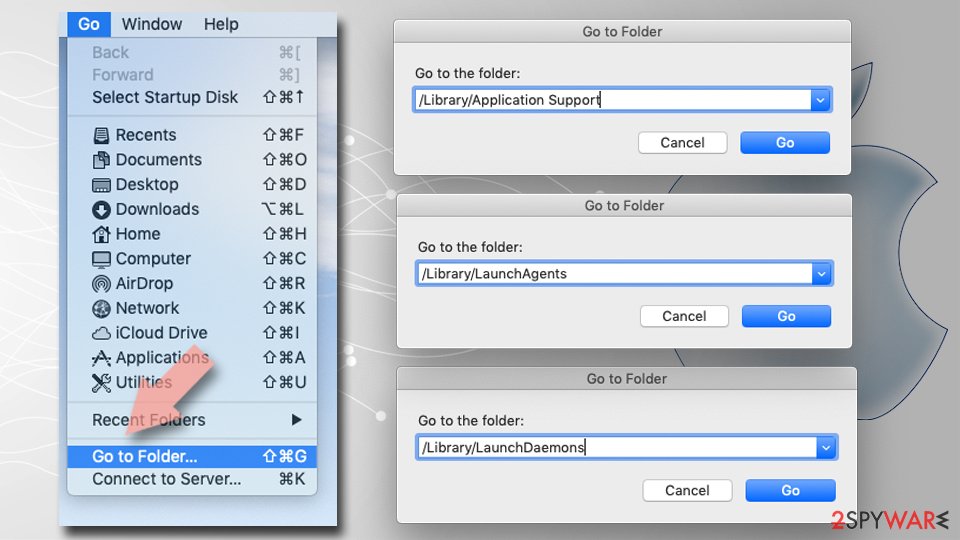
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Reset Internet Explorer
Remove dangerous add-ons:
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
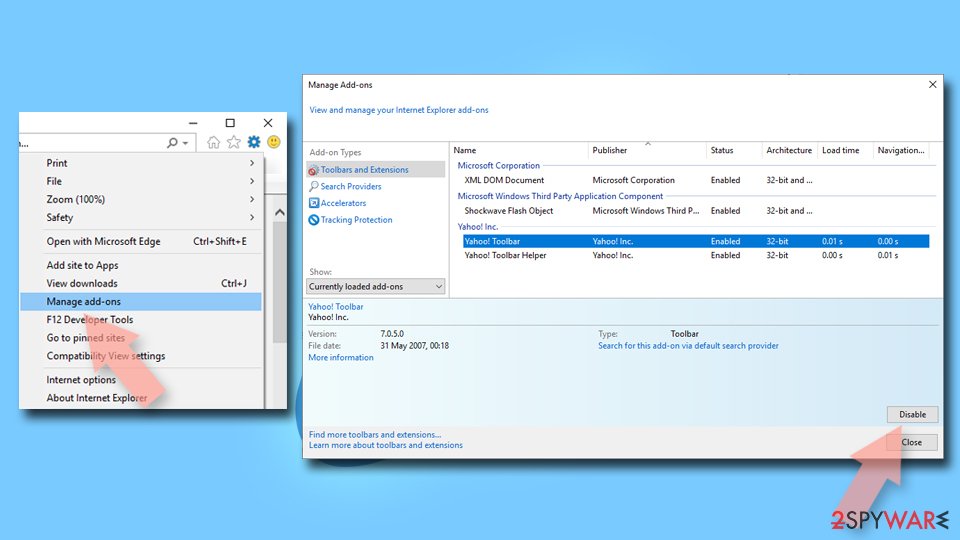
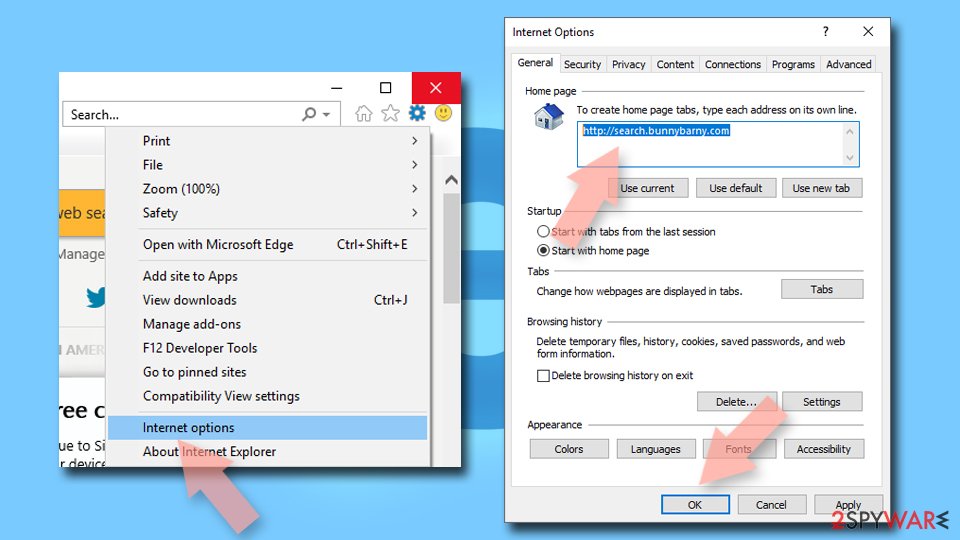
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
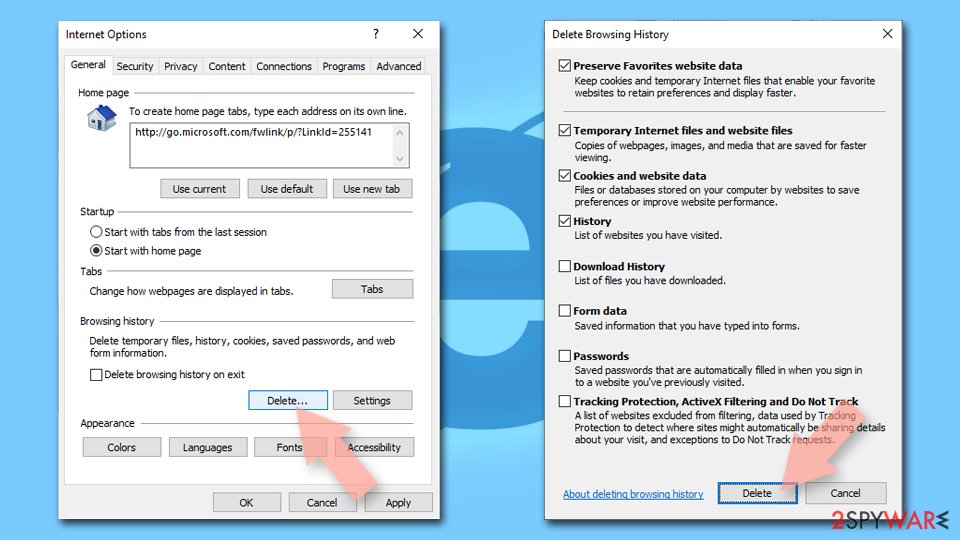
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
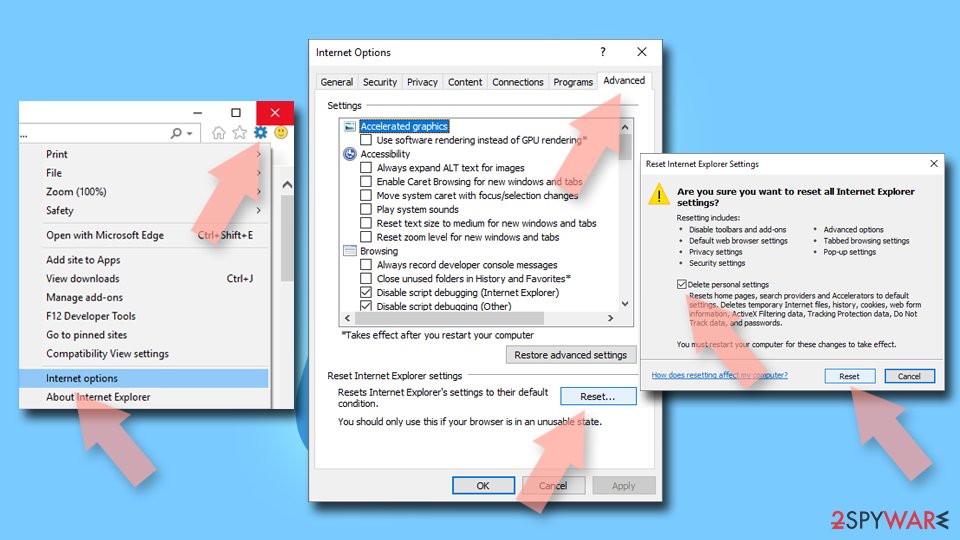
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Brkdown.com e-mail scam
Does getting "Your Apple iPhone is severely damaged by 19 viruses!" mean my account was compromised?
Not by itself. Phishing waves are sent to long lists of addresses collected from old breaches, websites and guessing, and the sender does not know whether you even have the account the message mentions. Getting "Your Apple iPhone is severely damaged by 19 viruses!" only means your address is on such a list.
It becomes a problem if you sign in through the link. To be sure, open the real service from a bookmark and check recent activity and security alerts. If you see nothing unusual and you did not type your password into the fake page, your account is fine.
How fast do I need to react after signing in on the "Your Apple iPhone is severely damaged by 19 viruses!" page?
As fast as you can. Stolen passwords are often tried within minutes, and the first thing an attacker usually changes is the recovery e-mail or phone, which locks you out. Change the password from a clean device first, then sign out everywhere and review the recovery settings.
If you are already locked out, use the provider's account recovery form straight away and mention that the page behind "Your Apple iPhone is severely damaged by 19 viruses!" took your password. Warn your contacts, since a taken-over mailbox is often used to send the same phishing to them.
Is Brkdown.com really from Facebook?
No. It is sent by scammers who copy the name and look of Facebook. The sender address and the links do not belong to it, and the message asks for your password, which a real company does not request through an unexpected message.
If you want to be sure about your account, open the website or app of Facebook the way you normally do, not through the message, and look for notices there. Then delete the message and report it as phishing. If you already followed its instructions, use the steps in this guide for your case.
Is it true that your account needs urgent attention?
No. The claim that your account needs urgent attention is the hook of Brkdown.com, invented to give you a reason to act quickly. Scammers pick a story that could plausibly apply to many people, so it may feel relevant to you, but nothing in the message is based on your real accounts or devices.
If the claim concerns a service you use, check it there directly, by opening the website or app yourself. You will find no such problem. Then delete the message and report it as phishing.
What happens if I do what Brkdown.com asks?
The scammers get your password, and they use it quickly. Passwords are tried on the real service within minutes, cards are charged or added to phone wallets, remote access is used to open your bank, and crypto is moved on at once.
Documents surface later as accounts in your name. If you already did what the message asked, do not wait to see what happens; follow the steps in this guide for your case today. Speed matters more than anything else here.
Will Facebook refund me if I fell for Brkdown.com?
Facebook did not send the message and is not responsible for it, so a refund usually comes from your bank or card issuer, not from the brand. Call the bank first if you paid.
It still helps to tell the real company: they can secure your account, add notes for their fraud team and take down pages that use their name. Contact them through their official website or app only, never through the message or a search ad. Keep the message as evidence.
How quickly do scammers use a phished password?
Often within minutes. Phishing kits send each password to the operators as soon as it is typed, and many test it automatically on the real service. Some kits also pass the two-step code through in real time.
That is why the first hour matters: change the password, end all sessions and check that the recovery details are still yours. If nothing has changed by then, you were probably fast enough, but keep watching for login alerts and password-reset e-mails for a few weeks.
How can I spot messages like Brkdown.com in future?
Check the sender's actual address, not only the name. Hover over links before clicking and compare the domain with the real one. Be suspicious of urgency, threats, prizes, unexpected invoices and requests for passwords, codes, card data or crypto.
Do not call phone numbers from unexpected messages; use the number on the official site or your card. When in doubt, go to the service directly through its app or a bookmark. Phishing protection and two-step verification limit the damage when a scam gets through.
Can just reading Brkdown.com harm my PC?
No. Reading the e-mail does nothing to the PC. The risk lies in what the message wants you to do: your password. Every one of those needs an action from you, such as a click, a typed password, a payment or a call.
If you stopped at reading, you are fine. Delete it and report it. If you are unsure whether you clicked something, check your browser history for the time you read the message, and act on what you find there.
Will Fortect remove Brkdown.com?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For Brkdown.com, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Wikipedia: Trojan horse (computing) (read October 7, 2026)
- Heimdal Security: JavaScript Malware – a Growing Trend Explained for Everyday Users (read October 7, 2026)
- FTC: How to recognize and avoid phishing scams (read October 7, 2026)
- CISA: Recognize and report phishing (read October 7, 2026)
- Microsoft Support: Protect yourself from phishing (read October 7, 2026)