
Code 055BCCAC9FEC e-mail scam: how to spot it and what to do
Code 055BCCAC9FEC is the fake error message that appears on the browser as a full screen and displays additional pop-ups that keep the person frustrated. The primary aim is to make people scared and eager to call the technical support hotline where scammers can directly lie to the person and obtain personal information, demand payment for the service.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Code 055BCCAC9FEC e-mail scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps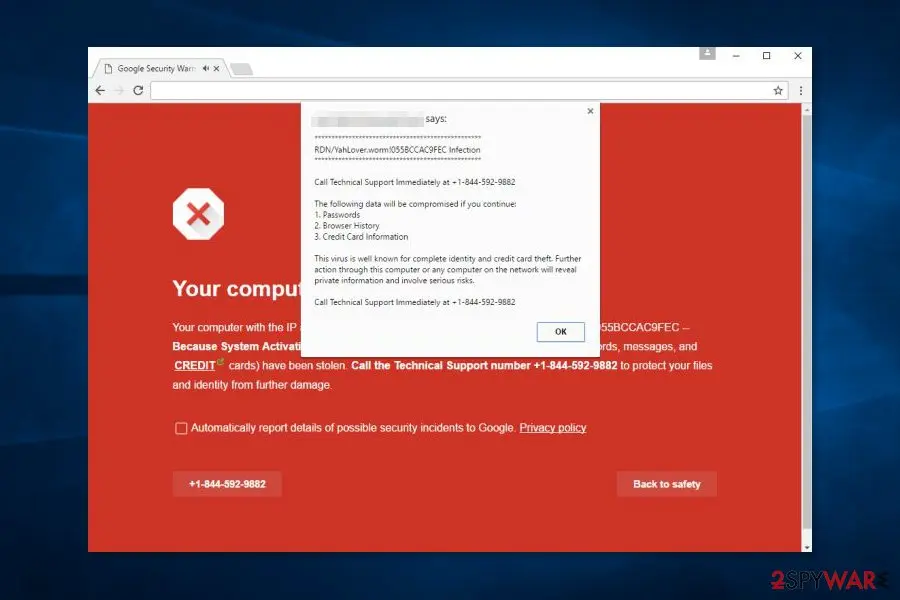
Code 055BCCAC9FEC e-mail scam: summary
| Distribution | Freeware installations and deceptive sites lead to adware and PUP infiltrations. Such cyber threats cause fake errors and scam messages |
|---|---|
| Name | Code 055BCCAC9FEC |
| Type | Technical support scan/ adware |
| Tactics | Showing fake alerts, warning messages with errors and system issues, so the person believes and calls the technical support number or installs the suggested software |
| Symptoms | Advertisements not coming from the original site appears filling up the screen, redirects open new tabs and browser windows with fake system alerts and errors stating about damage or malware to lure people into contacting the scammers |
| Danger | Calling the technical support number may cost you a fortune, people behind the phone number, in most cases, only care for your personal data, credentials or money that can be obtained directly from you. Stolen personal information can be used in the later scam campaigns |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Evidence | 4 write-ups by security sites; no sample analysed yet |
|---|---|
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| Phone number | +1-833-337-6555 |
| First seen | 10 June 2021 |
| Facts checked | 7 October 2026 |
What the Code 055BCCAC9FEC e-mail scam e-mail looks like
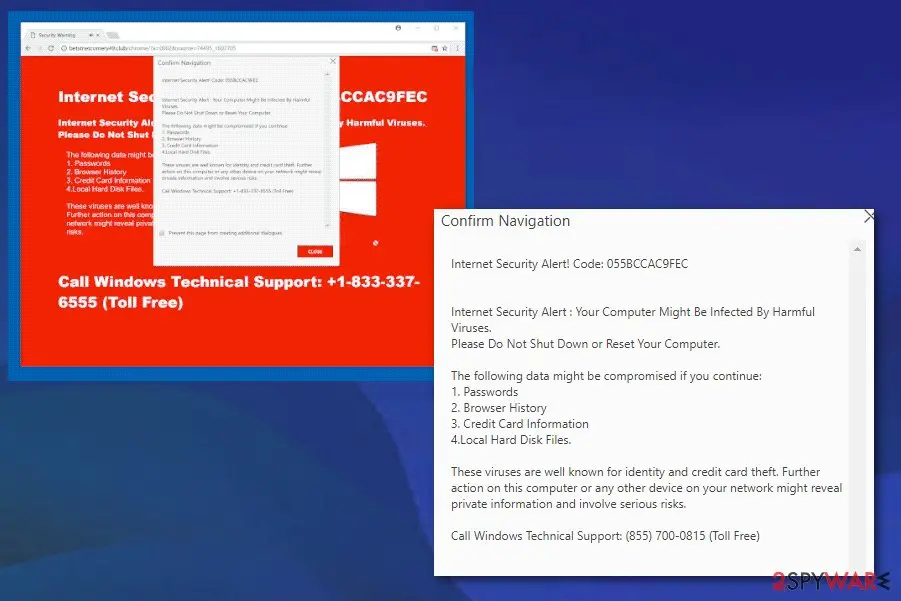
Internet Security Alert! Code: 055BCCAC9FEC
Internet Security Alert : Your Computer Might Be Infected By Harmful Viruses.
Please Do Not Shut Down or Reset Your Computer.
The following data might be compromised if you continue:
1. Passwords
2. Browser History
3. Credit Card Information
4.Local Hard Disk Files.
These viruses are well known for identity and credit card theft. Further action on this computer or any other device on your network might reveal private information and involve serious risks.
Call Windows Technical Support: +1-833-337-6555 (Toll Free)
How to tell the Code 055BCCAC9FEC e-mail scam e-mail is fake
- Phone number:
+1-833-337-6555
From our report of Jun 2021 · not reviewed since
More from our earlier report on Code 055BCCAC9FEC
- Perform a full scan with anti-malware software
Is Code 055BCCAC9FEC e-mail scam dangerous? What the senders want
From our report of Jun 2021 · not reviewed since
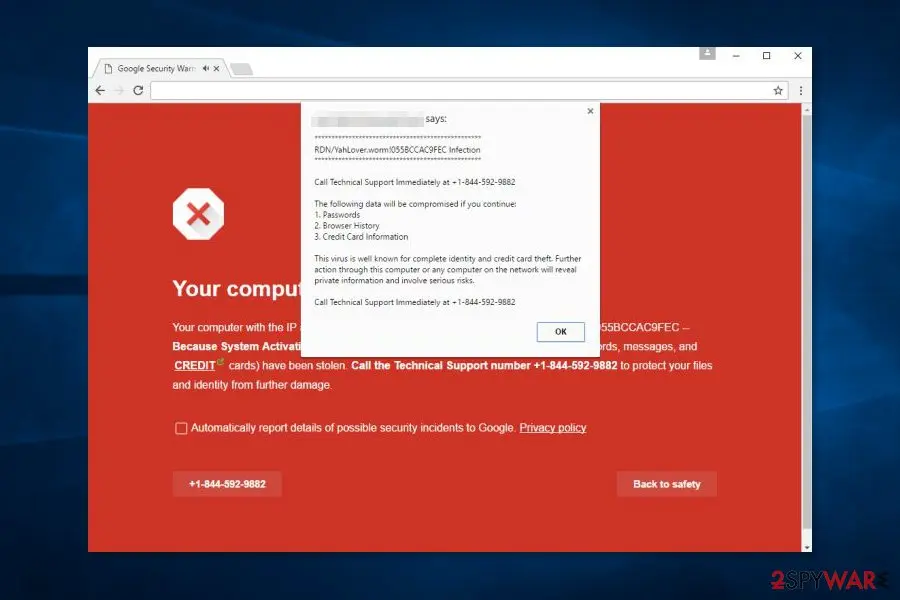
Internet Security Alert! Code: 055BCCAC9FEC is yet another tech support scam which has nothing in common with Google
Code 055BCCAC9FEC is the fake error message that appears on the browser as a full screen and displays additional pop-ups that keep the person frustrated.
The primary aim is to make people scared and eager to call the technical support hotline where scammers can directly lie to the person and obtain personal information, demand payment for the service.
Internet Security Alert! Code: 055BCCAC9FEC is a fraudulent message which belongs to tech support scammers. They try to convince their victims that this message belongs to Google, Microsoft, and similar well-known companies. Typically, it shows up on the desktop while people are browsing the Internet and informs them that their computers are infected with serious malware.
Additionally, they are asked to call "Windows Technical support" at +1-833-337-6555, +1-844-592-9882, or a similar number. However, we want to stress that this number belongs to cybercriminals, and you should never use it.
Typically redirects to scam websites start when adware is installed on the computer. This potentially unwanted program (PUP) usually gets into the system unnoticed with the help of various free downloads and initiates needed system updates. As a result, it can start showing the fake error message as soon as a user starts browsing the Internet.
The main activity of adware is to redirect victims to the technical support scam website that displays this alert:
The purpose of this "Internet Security Alert" virus is to trick users into calling the provided number and following "specialists" instructions. However, people who are going to pick up the phone are not willing to help you. They might have other purposes, such as:
Therefore, you should NOT call the provided phone number. All the information provided by the alert is not real. The only problem your computer has is an adware infection which might be wiped out quickly with an anti-malware tool.
All these problems pose a danger to your privacy and make internet browsing complicated. Thus, you should remove adware causing redirects to malicious sites from your computer immediately. As we have already explained, you can do it automatically with security software. However, you can find manual removal give at the end of the article too.
- Tricking you into purchasing useless security tools that are supposed to clean computers from a virus. In this way, scammers can get your credit card information or other sensitive data. Thus, it may lead to money loss or identity theft.
- Convincing you to install remote access tools in order to let "technicians" do the removal for you. In this case, criminals can install malware or spyware on your computer and perform other cyberattacks in the future.
- display intrusive ads that include potentially dangerous or malicious content;
- trigger redirects to affiliate sites out of sudden or when you click links or buttons;
- track information about users and use it for marketing reasons;
- sell aggregated information to third-parties that might be advertising networks.
From our report of Jun 2021 · not reviewed since
The success of adware infiltration lies under bad user's habits
The ad-supported application usually spreads in freeware or shareware packages as an optional component.
Malicious application is usually presented as a useful add-on, PC optimization tool, or similar app. Thus, users who are using Advanced/Custom settings can be tricked into installing it.
However, researchers from viruss.lv tell that users rarely choose to install new programs using Advanced settings. Usually, they rely on Quick/Standard settings that do not reveal additional components.
The trick is that users give indirect permission to install the whole package when using a Quick setup. Thus, these settings should not be used in order not to install unknown programs without realizing it.
From our report of Jun 2021 · not reviewed since
Stop redirects to "Internet Security Alert! Code: 055BCCAC9FEC"
You can remove adware either manually or automatically.
In the virus description, we have mentioned that automatic elimination is performed with anti-malware/anti-spyware software. However, a browser reset is also recommended to get rid of tracking cookies.
However, we are aware that not everyone wants to use additional software for PUPs removal. For this reason, our team has prepared a manual removal guide. Do not rush, and be attentive! If you leave at least one of the adware-related components, you will need to perform the procedure again.
What to do after the Code 055BCCAC9FEC e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you typed a password on the page the Code 055BCCAC9FEC message opened, assume the sender has it. Go to the real site by typing its address yourself and change the password there, choosing one you have never used.
Change it anywhere else the same password was used, and sign out all other sessions if the service offers it. Any browser on Windows 11 or Windows 10 will do, as long as you do not follow the e-mail's link.
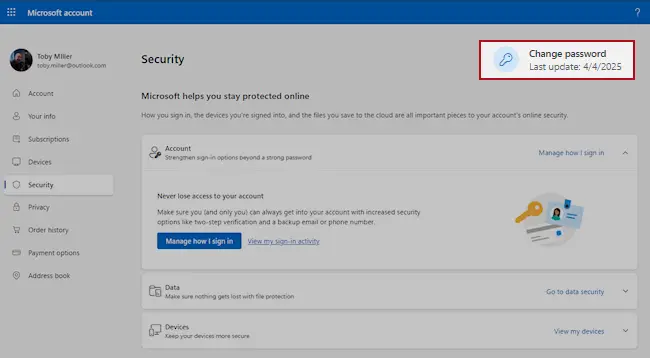
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
With two-step verification on, a stolen password alone no longer opens the account, because a sign-in from a new device also needs a code from your phone.
Switch it on for the e-mail account first, then for banking, shopping and social accounts that use that address.
Check the recovery phone, the recovery e-mail and any forwarding rules while you are in the settings, since attackers change them to come back. The pages are the same on Windows 11 and Windows 10.
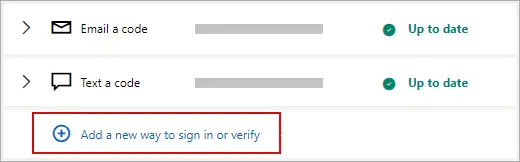
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Do not reply and do not click anything else in the message. In Outlook select the e-mail and choose Report > Report phishing; in Gmail open the three-dot menu next to Reply and pick Report phishing.
That trains the filter for everyone on the service, and the message goes to the junk folder. If the e-mail came to a work address, forward it to your IT team as an attachment first.
The steps are the same in the web mail and the mail apps on Windows 11 and Windows 10.
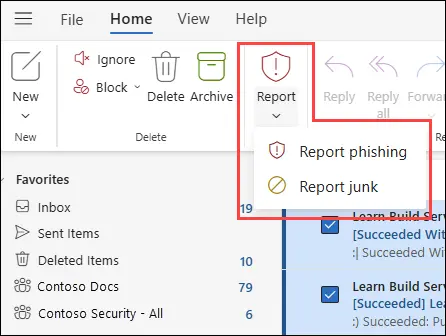
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A fake sign-in page only steals what you type, so most readers can skip this step. If the Code 055BCCAC9FEC e-mail made you download or open a file, delete it and scan the PC.
In Windows Security > Virus & threat protection > Scan options, run a Full scan and then Microsoft Defender Antivirus (offline scan) > Scan now. The offline scan restarts Windows 11 or Windows 10 and takes about 15 minutes.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
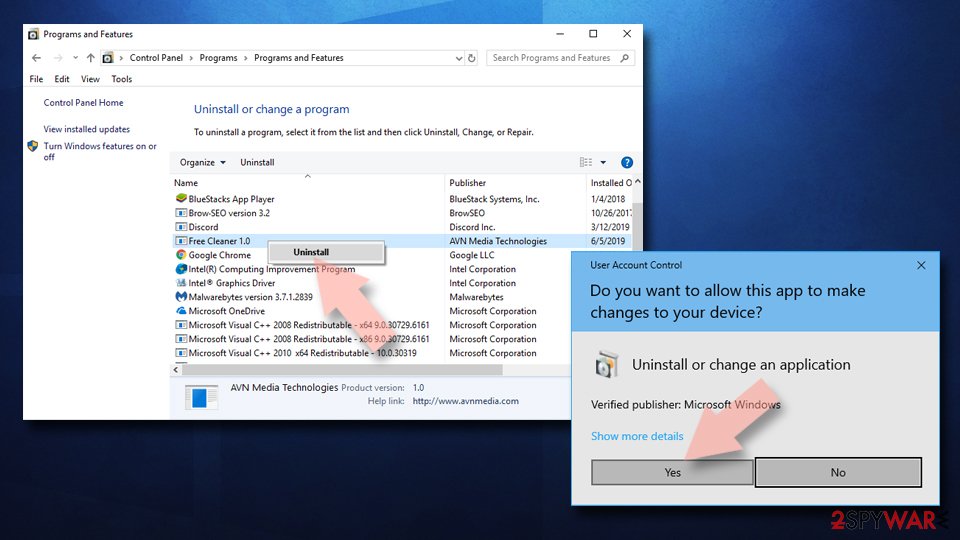
To remove the fake error message, you have to look up adware and its related components in the system. Follow the steps below, and do not forget to take care of your browsers:
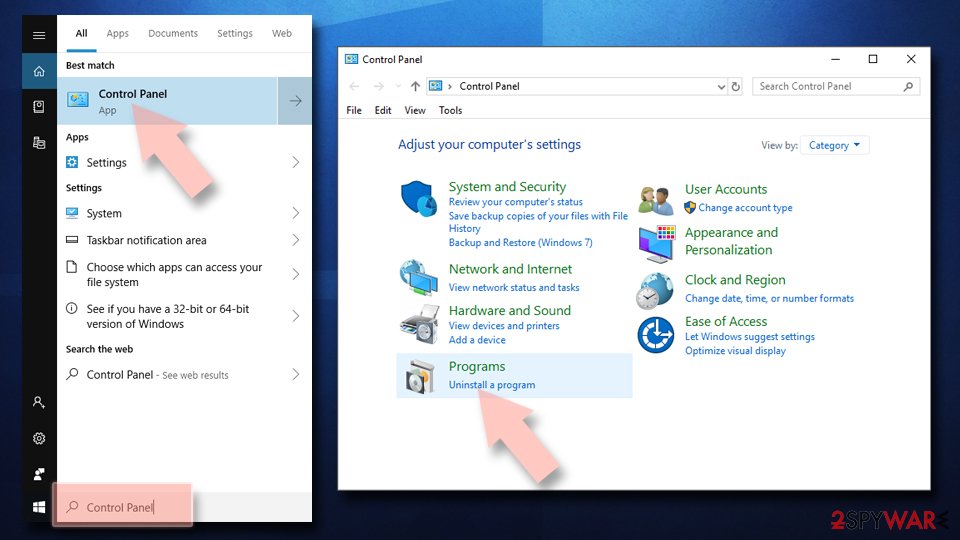
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
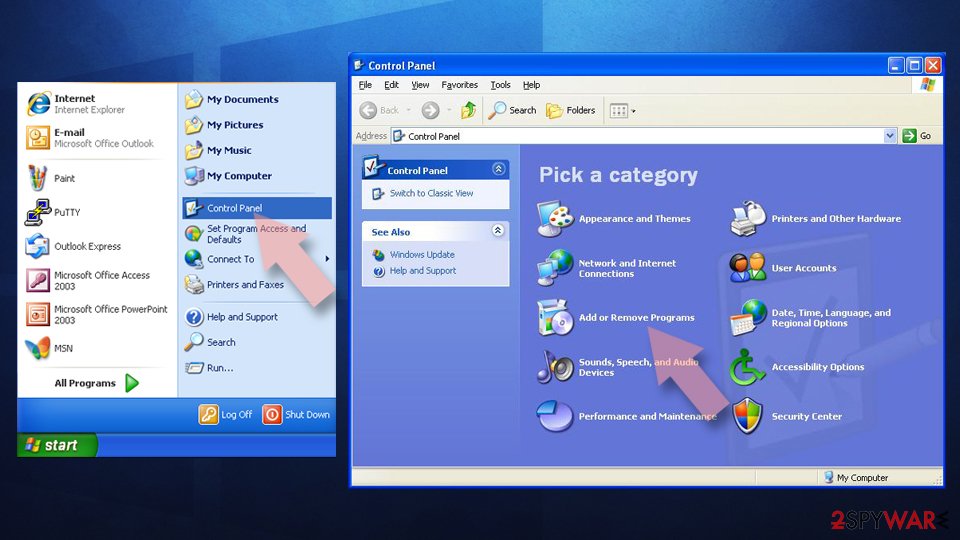
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
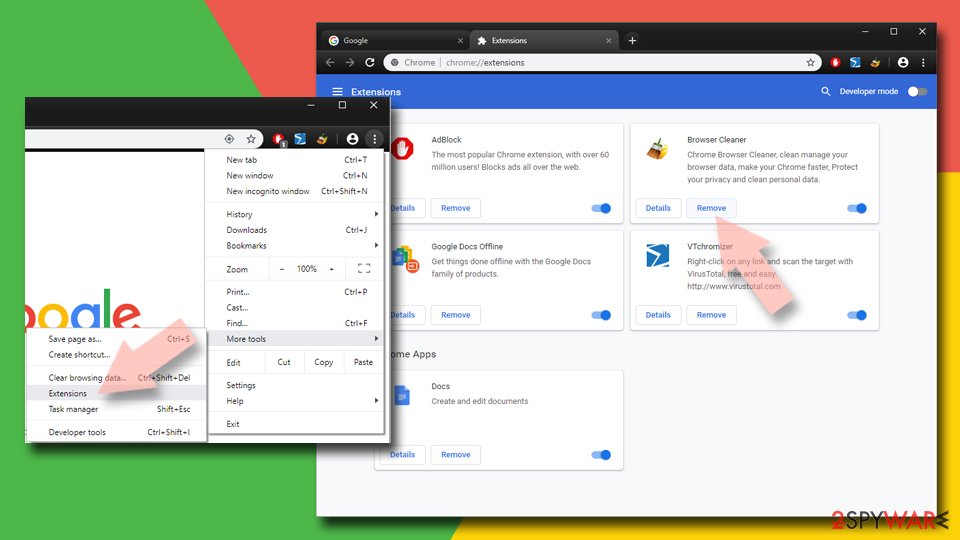
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
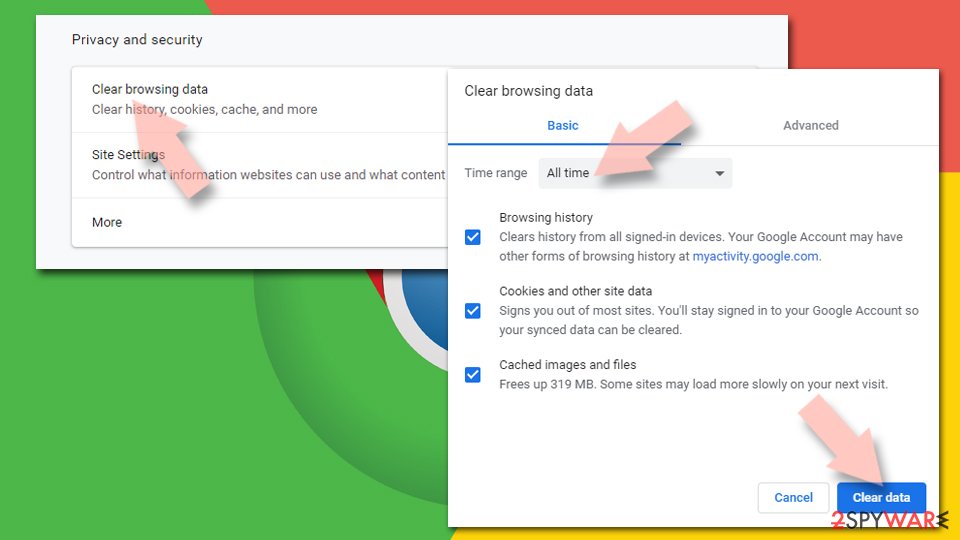
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
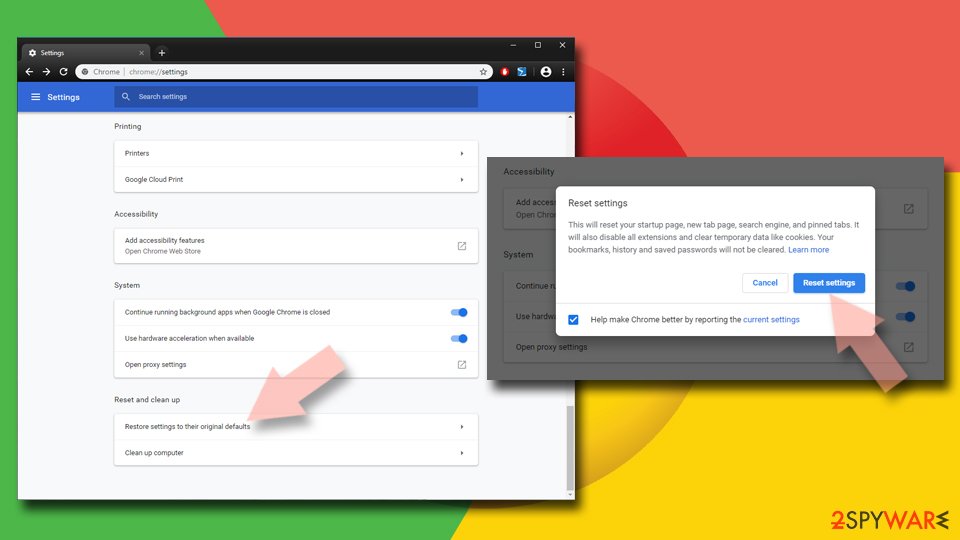
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Microsoft Edge
After the hijack, you should fix Microsoft Edge by following these steps:
Delete unwanted extensions from MS Edge:
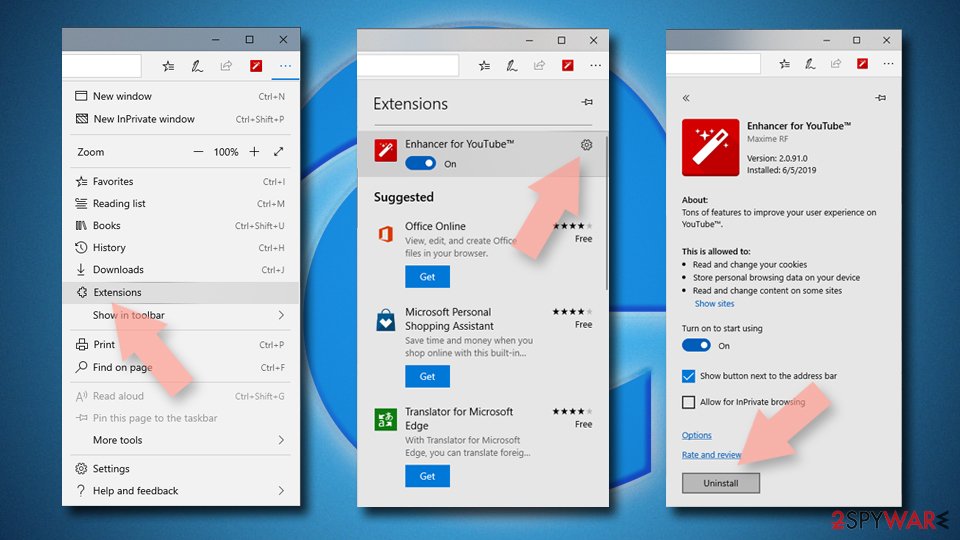
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.
Clear cookies and other browser data:
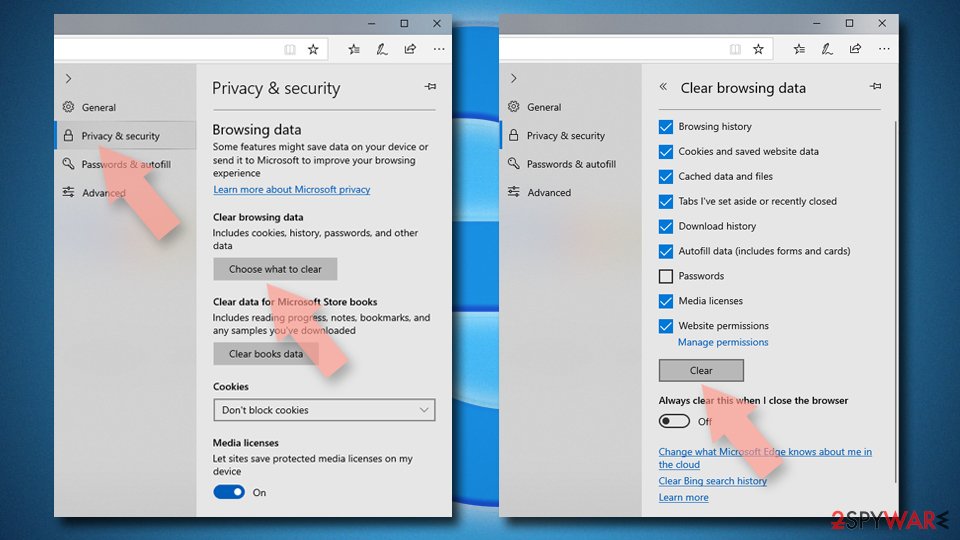
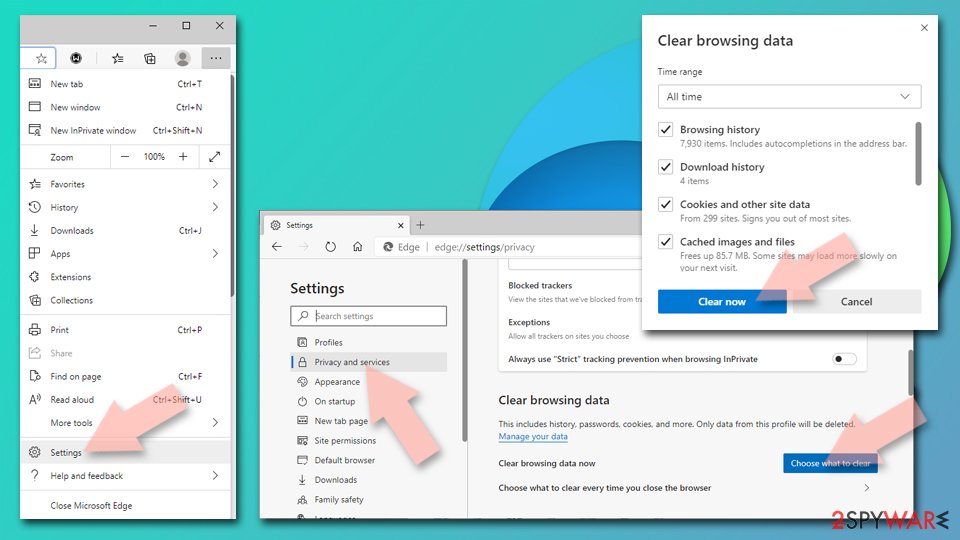
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.
Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
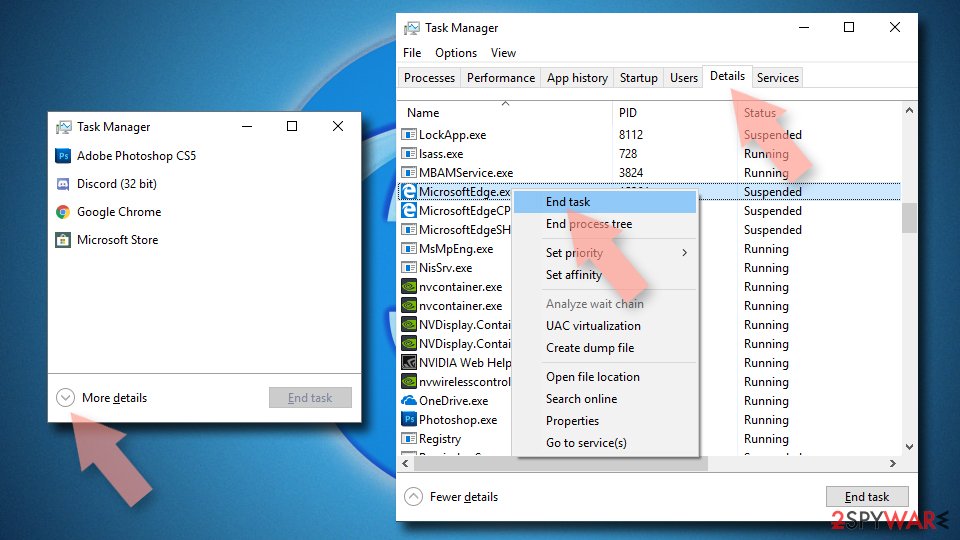
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.
Delete extensions from MS Edge (Chromium):
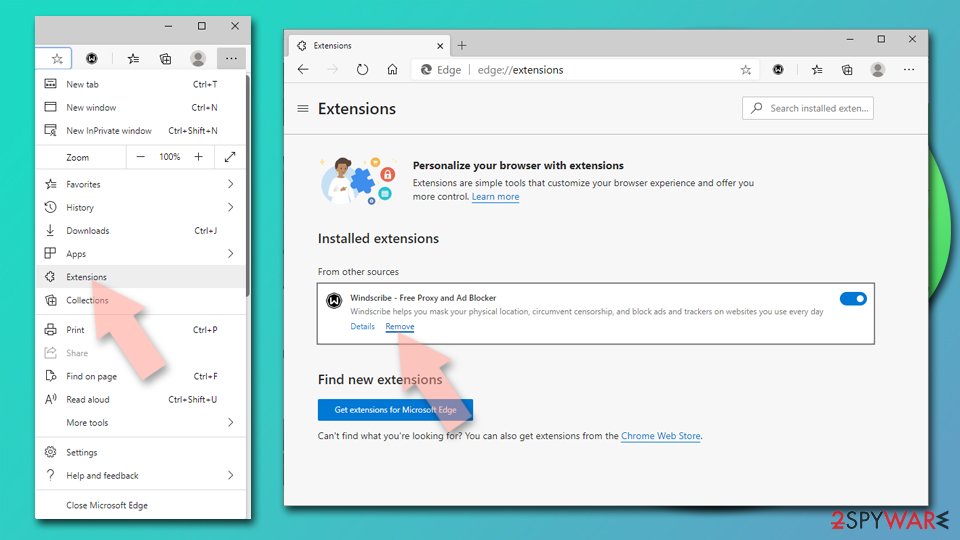
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.
Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.
Reset Chromium-based MS Edge:
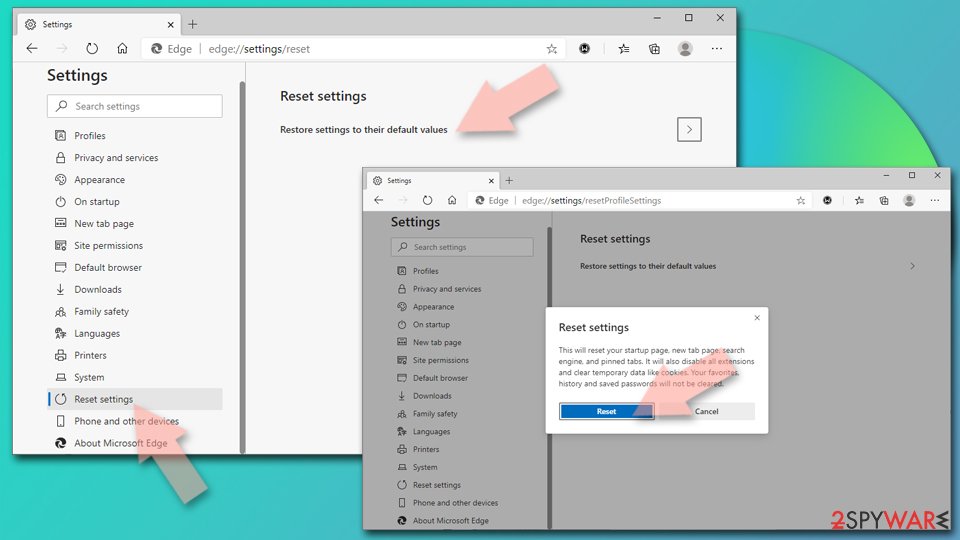
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.
Remove from Mozilla Firefox (FF)
Uninstall questionable Firefox extensions that might be responsible for forcing you to visit this shady tech support website:
Remove dangerous extensions:
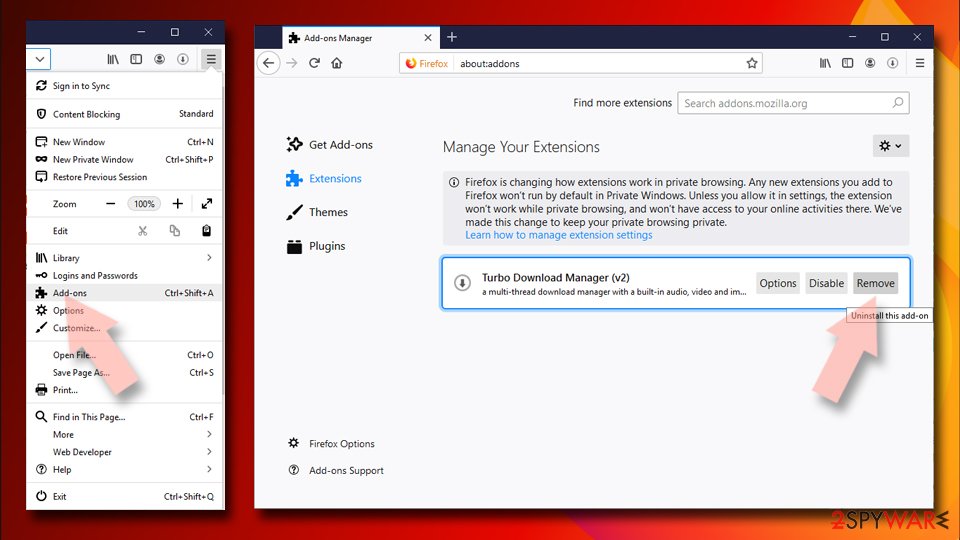
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
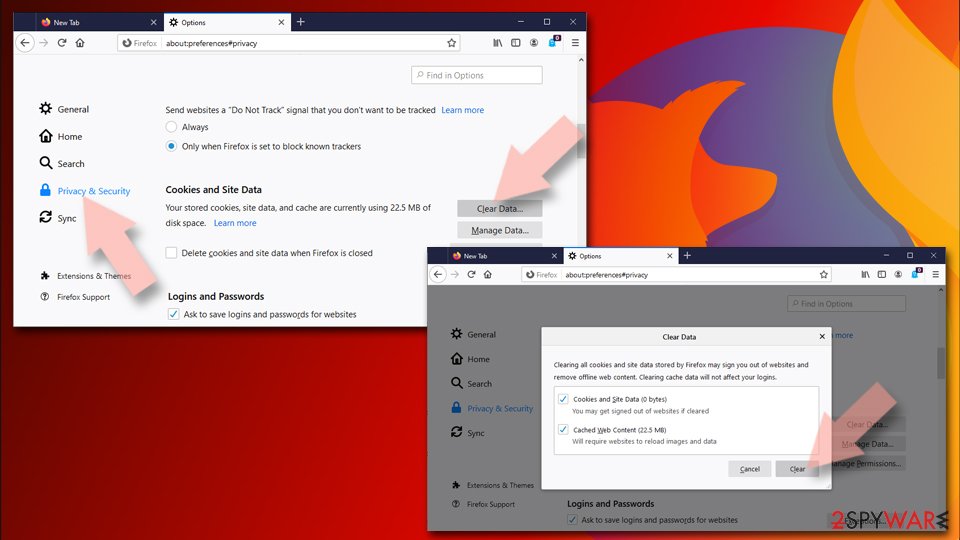
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
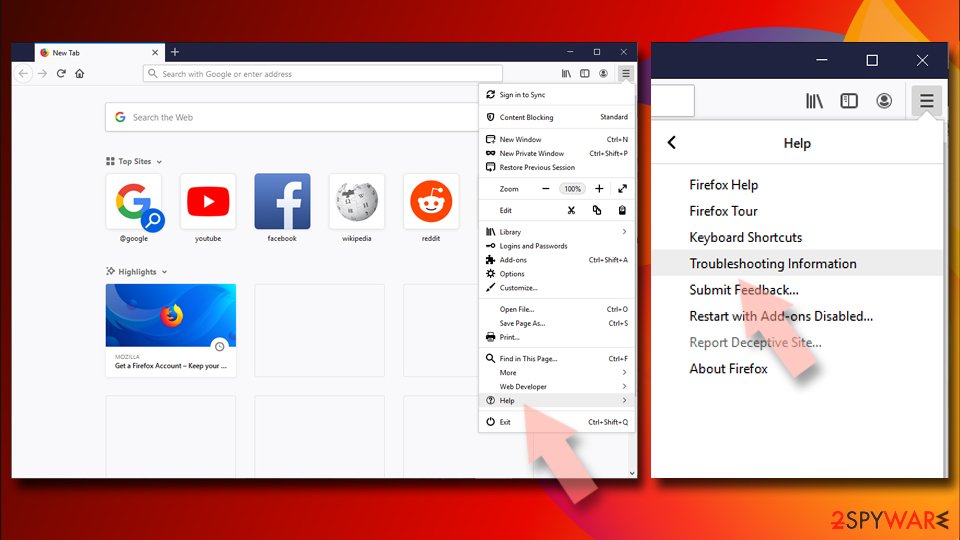
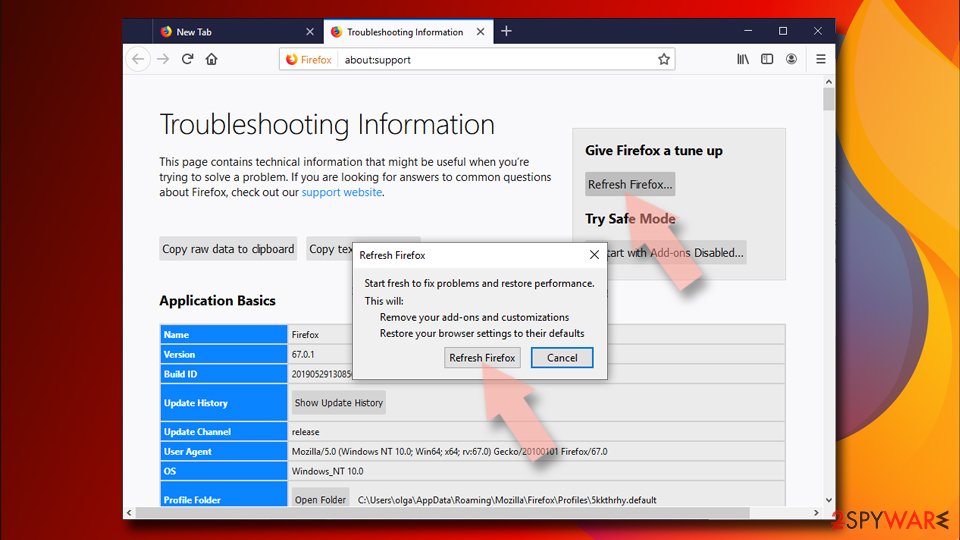
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
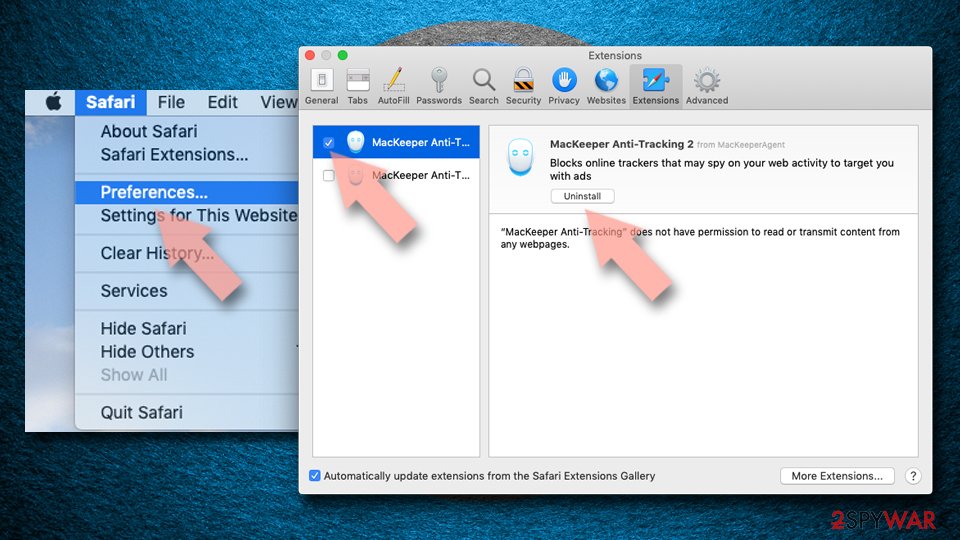
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
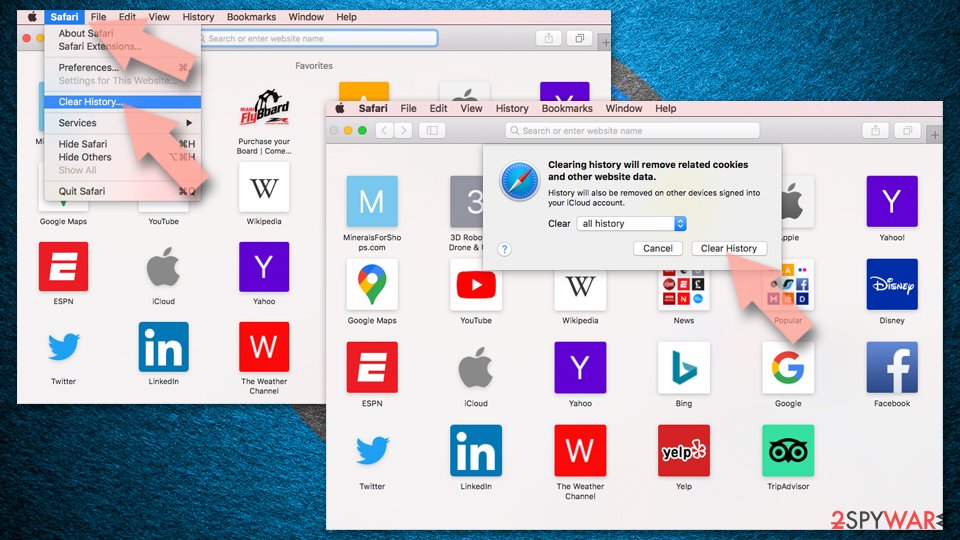
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
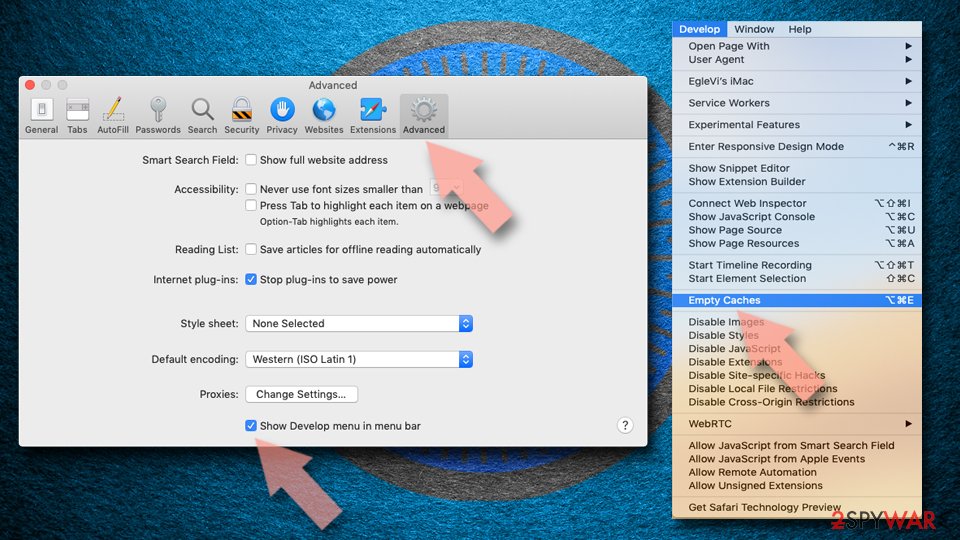
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Remove the unwanted application:
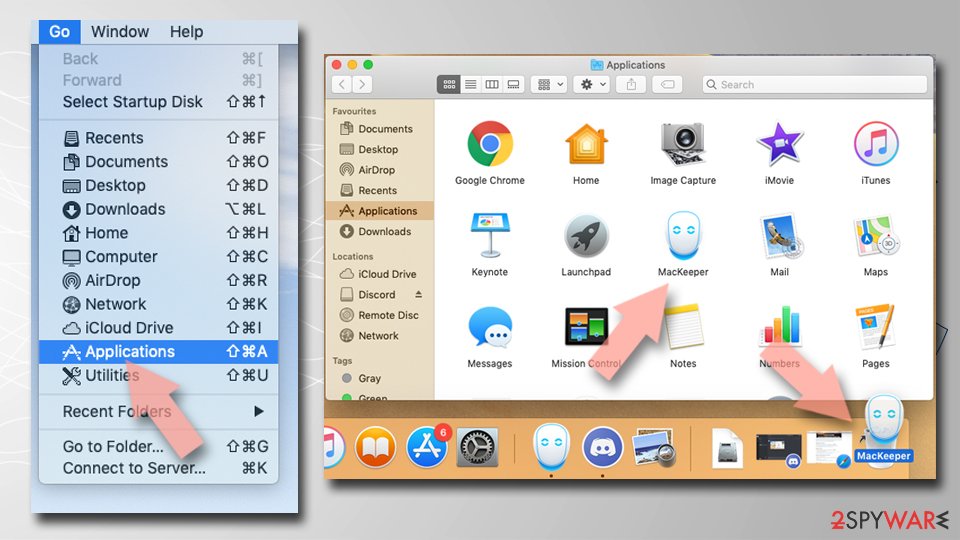
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
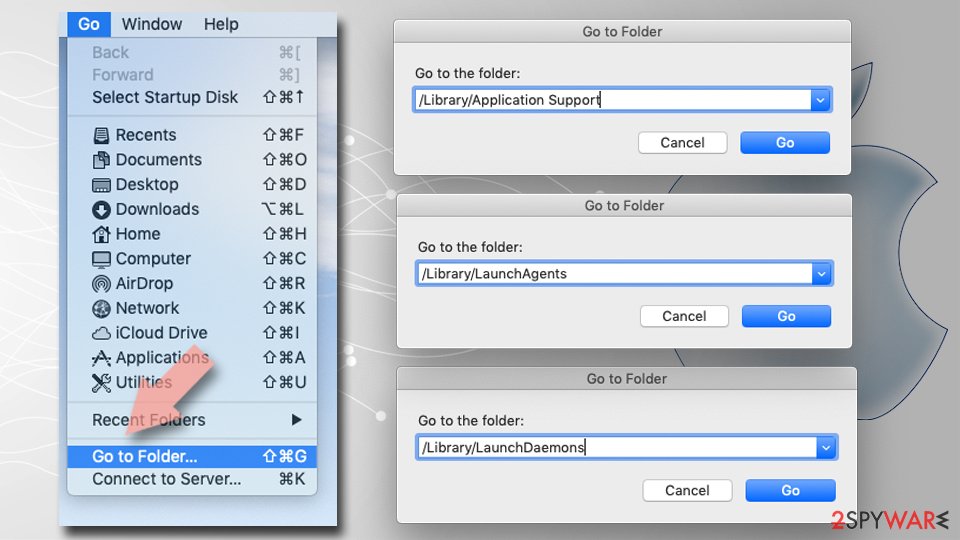
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
Questions about Code 055BCCAC9FEC e-mail scam
I opened the "Internet Security Alert!" e-mail. Am I hacked?
No. Opening and reading a phishing e-mail does not give anyone access to your account or your PC. Modern mail programs block scripts and remote content by default, so reading the message "Internet Security Alert!" only showed you text and pictures.
The danger comes from clicking the button and typing your password on the page it opens, or from opening an attached file. If you did neither, report the message as phishing and delete it.
If you clicked but closed the page without typing anything, there is also nothing to fix. If you did type a password, change it from another device and turn on two-step verification.
Is +1-833-337-6555 a real Microsoft support number?
No. Microsoft does not put phone numbers in warnings, pop-ups or error messages, and its support never calls you first about a virus. The number +1-833-337-6555 is used by a scam call centre that pays for traffic to fake warning pages.
If you need help from Microsoft, go to support.microsoft.com yourself and start from there. Never use a number that appeared in a pop-up, an unexpected e-mail or a search ad that looks like a support listing. If you already called, follow the steps in this guide for callers:
- remove any remote tool
- change passwords from another device
- contact the bank if you paid
I typed my password after "Internet Security Alert!". What now?
Act within the hour. From another device, open the real site of the account the message "Internet Security Alert!" imitated and change the password. If the same password is used anywhere else, change it there too.
Sign out of all other sessions, check the recovery e-mail and phone number, and look for mail forwarding rules or filters you did not create. Then turn on two-step verification with an authenticator app or a passkey.
If the fake page also asked for a card number or a bank login, call your bank and ask them to block the card. Finally, report the e-mail so others are warned.
They called me back from +1-833-337-6555 offering a refund. Is it real?
No. The refund call is a second scam by the same people. They say they will return your money, ask you to log in to online banking while they are connected, then claim they sent too much and ask you to send the difference back, by transfer or gift cards.
In reality they moved your own money between your accounts or edited the page. Hang up on any call from +1-833-337-6555 or anyone who mentions your earlier repair.
If you want a refund, ask your bank or card issuer directly. If they had remote access, remove their tool and change your passwords from another device.
Could Code 055BCCAC9FEC be a genuine message?
We checked it, and it is not. A well-known company is only the costume. The message exists to get your password, and real companies handle that inside your account, after you sign in normally, not through links, attachments or phone numbers in a message you did not expect.
Scammers copy logos and footers perfectly, so the design proves nothing. The sender address, the link target and the request are the reliable signs, and all three point to a scam here. Delete it, and if you are worried, check your account directly.
Who answers +1-833-337-6555?
Not the company named in the message. +1-833-337-6555 leads to a call centre that runs Code 055BCCAC9FEC, often far from the country it claims to be in. The agents follow a script: they confirm a charge you never made, then offer a refund that requires remote access to your PC.
Scammers change numbers often and may also spoof caller ID when they call you back. If you want to talk to the real company, find its number on its official site or on your card or statement, never in the message.
What is the single best habit against scams like this?
Never act on a message through the message itself. If something claims to be from a well-known company and asks you to sign in, pay, call or open a file, close it and go to the service the way you always do:
- a bookmark
- the app
- the number on your card
Real problems will be visible there. This one habit defeats almost every phishing, invoice, delivery and account-suspension scam, regardless of how convincing the design is, because the scammers can copy the look but not the real account.
Can I trick the scammers or waste their time?
Better not. Replying to Code 055BCCAC9FEC confirms that your address or number is live and puts it on lists that sell for more. Scammers who are teased sometimes switch to harassment or try to use any detail you reveal, such as your name, employer or location.
Playing along also risks a slip, like opening a link or a file they send. Report the message, block the sender and delete it. Your report does more damage to the operation than a conversation would.
I entered my password on the fake page. What should I do?
Change the password on the real site right away, through its own website or app, and sign out of all sessions.
If you use the same password anywhere else, change it there too. Turn on two-step verification with an authenticator app or a passkey. Check the account for changes:
- recovery e-mail
- phone number
- forwarding rules
- recently sent messages
If you can no longer sign in, use the provider's account recovery page. Tell your contacts if the account sent messages in your name.
Will Fortect remove Code 055BCCAC9FEC?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Code 055BCCAC9FEC, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft Windows support: Protect yourself from tech support scams (read October 7, 2026)
- Wikipedia: Spyware (read October 7, 2026)
- FTC: How to recognize and avoid phishing scams (read October 7, 2026)
- CISA: Recognize and report phishing (read October 7, 2026)
- Microsoft Support: Protect yourself from phishing (read October 7, 2026)