
CoViper: what it is and how to remove it
CoViper is a type of malware that destroys Windows computer's MBR (Master Boot Record) by rewriting it. Security researchers spotted the virus in early April as a coronavirus-themed file.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Unsure whether COVID-19.exe is safe? A free scan checks the file and what starts it.
Do it yourself · free Remove CoViper yourself 6 steps, about 18 minutes, no software needed.
Start the steps
CoViper: summary
| Name | CoViper |
|---|---|
| Type | MBR locker, wiper |
| Related files | COVID-19.exe, coronavirus.bat, mainWindow.exe, run.exe, cursor.cur, Update.vbs, wallpaper.jpg |
| Developer | Angel Castillo |
| Operating principle | Rewrites Master Boot Record on Windows, preventing users to load the system correctly |
| Symptoms | Inability to boot into Windows; a black wallpaper with "Your Computer Has Been Trashed" is displayed instead |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Infiltration | No clear attack vectors were observed, although researchers believe that malware can be spread via phishing messages on Discord communications app |
|---|---|
| Termination | In order to prevent malware from impacting the MBR, you should press CTRL+ALT+ESC, and then the PC will restart. After that, you should access Safe Mode with Networking as explained below and then eliminate the infection (end.exe binary) with the help of security software |
| Detection names | No Microsoft detection name is known |
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Evidence | 5 write-ups by security sites; details still limited |
| File names | COVID-19.exe and C:\Users\ |
| First seen | 19 May 2020 |
| Facts checked | 7 October 2026 |
What CoViper does on an infected PC
From our report of May 2020 · not reviewed since
CoViper is a wiper-type malware that abuses COVID-19 crisis to its own advantage
CoViper is a type of malware that destroys Windows computer's MBR (Master Boot Record) by rewriting it.
Security researchers spotted the virus in early April as a coronavirus-themed file. As it turns out, malicious actors are clearly trying to abuse the pandemic to install malware on users' machines (a common phenomenon among cybercriminals, as such malware strains like Maze or Sodinokibi, are actively infecting hospitals and other industries).
CoViper virus belongs to the so-called "MBR locker" family that is often associated and delivered with ransomware. The latter would show victims a ransom note, claiming that the machine and files can only be restored after they pay the attackers a particular sum of money.
However, this wiper does not display any ransom notes and simply prevents Windows from booting (researchers believe that it is still in a development stage). As a result, users are unable to access their machines, making CoViper removal extremely difficult for those less IT-savvy.
They said that the installer, which was titled as COVID-19.exe, was found accidentally, and there are little implications that malware is being widespread. Nonetheless, it is highly likely that its main attack vector is phishing messages delivered by a chatting app Discord.
Nonetheless, if CoViper malware will be developed further and combined with ransomware, it might be delivered in various other ways in order to be more successful. For example, the following methods could be used:
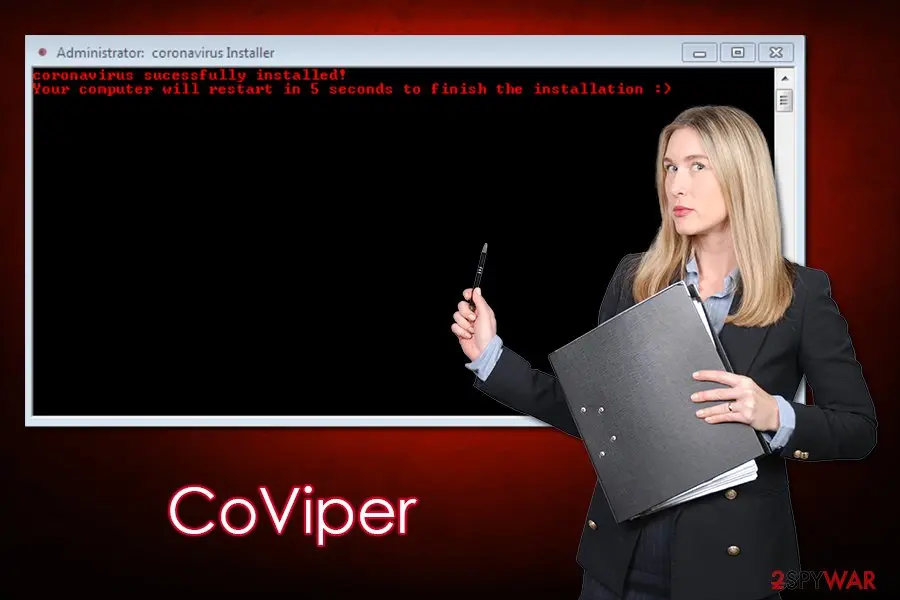
Once inside the system, CoViper delivers several files into the Temp folder on the machine, which is located in C:\Users\ \AppData\Local\Temp. From there, the virus copies all these files to a new location in the home directory, which is titled "COVID-19."
Five seconds later, the malware executes three executables: run.exe, Update.vbs, and end.exe, with the latter being the main file, which causes MBR to malfunction and prevents normal Windows boot sequence.
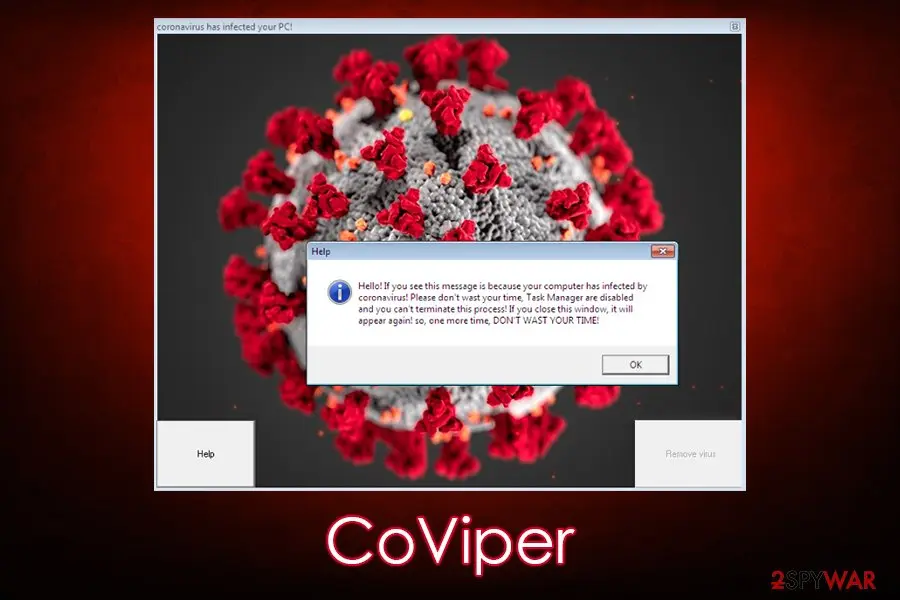
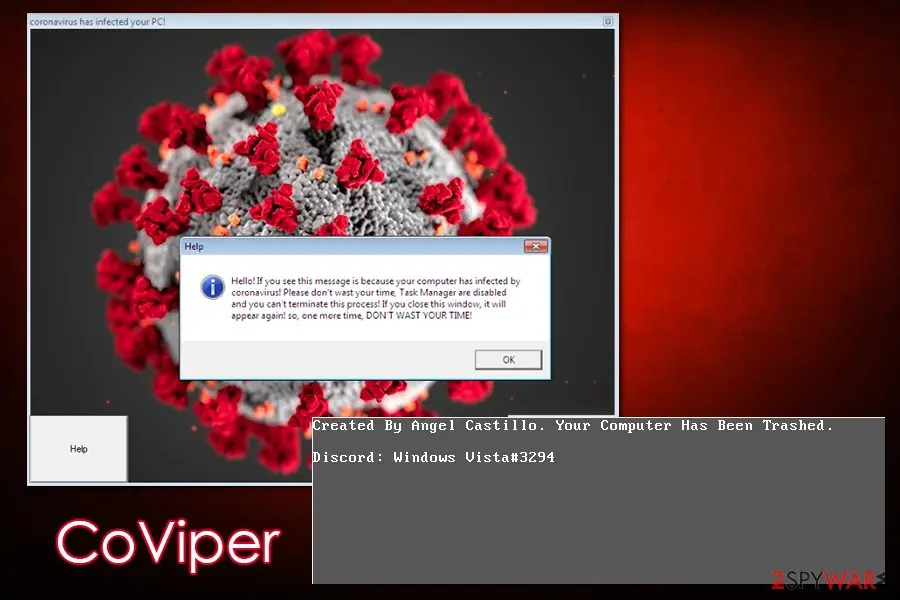
After the system is booted, victims will find that they are unable to use the Task Manager and that the appearance of their mouse cursor is now different. Then, CoViper malware will launch a pop-up window that is titled "coronavirus has infected your PC!" which includes the famous COVID-19 related picture. In the corners of this window, users can see two buttons - "Help" and "Remove virus."
The former opens another pop-up, which claims that the Task Manager has been disabled and that it is impossible to do anything about that. The latter button is grayed out/disabled, so this might be a pre-release function that would allow users to disable malware functionality after a ransom is paid.
If the system is rebooted once more, users will not be able to see anything apart from a black wallpaper which states:
Researchers claimed that CoViper was compiled thanks to an open-source tool that is available online, but will not disclose its name, or the author's name, to the public:
Although CoViper is a wiper, researchers managed to find a way to trick its operation and allow users to boot into normal Windows mode themselves.
The trick is to press CTRL+ALT+ESC on the keyboard and then allow the system to reboot - a normal MBR boot sequence would be initiated in such a way. However, this does not solve all the problems, as the malware will begin the reinfection process as soon as Windows is booted.
To bypass that and remove CoViper safely, users should boot into Safe Mode with Networking and perform a full system scan with powerful security software, such as or . Once malware is terminated, users should also scan their machines with to ensure that all Windows settings and functions are back to normal.
Currently, it is hard to say what the main goal of CoViper malware is, as it does nothing to benefit the attackers. Considering naming patterns and its functionality, it is highly likely that the malware is currently operated as a prank, and might be later developed into something more sinister.
- Spam email attachments and embedded hyperlinks;
- Fake updates and scam messages on malicious sites;
- Software cracks and pirated program installers;
- Software vulnerabilities and exploit kits, etc.
From our report of May 2020 · not reviewed since
More from our earlier report on CoViper
- CoViper is a relatively new wiper-type malware that was discovered by security researchers from Avast.
- Furthermore, we would like to mention that while investigating CoViper, it is clear that this malware was actually generated by a custom tool publicly available on the Internet, for free.
- Because we have come to a conclusion that the author of this tool is not actually the author of CoViper itself, we will not disclose his name.
- We will also not disclose the tools's name so that we don't bring more attention to it.
What CoViper can steal or download
From our report of May 2020 · not reviewed since
If users get infected with malware sample that is still in the development stage, it is typically not difficult to eliminate and avoid more serious consequences, such as financial losses, loss of access to personal files, or even identity theft. However, in most cases, malware is well polished by the attackers and functions as intended - it can compromise users' online safety and computer security.
What makes matters worse is that threats like keyloggers or remote access trojans (RATs) are designed to sustain low visibility on the host system, preventing users from noticing it on time. As a result, malware can sit on computers for weeks, months, or even years before it is detected.
Therefore, it is always important to secure the machine from cyberattacks and practice precautionary measures. As mentioned above, malicious actors can use a variety of methods for malware infiltration, so comprehensive preventive measures should be performed at all times. Here are some tips from industry experts:
- When dealing with Discord or other chat applications, do not click on links that come from unknown individuals as this action can result in malware infection;
- Update your Windows OS and all the installed applications as soon as security patches are shipped by developers;
- Employ comprehensive anti-malware software and keep it updated at all times;
- Protect all your accounts with strong passwords and never reuse them for different accounts;
- Do not download software cracks or pirated application installers;
- Backup all your personal files on a removable drive, such as USB Flash;
- Never allow email attachments to ruin the macro function and never click on links inside suspicious emails.
How to check the PC for CoViper
- Path:
C:\Users\ - File:
COVID-19.exe
How to remove CoViper
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Check where COVID-19.exe runs from and stop it
COVID-19.exeis the part you can see, and its location tells you whether it belongs there. Right-click it on the Processes page of Task Manager and choose Open file location, then right-click the file > Properties > Digital Signatures to see who signed it.An unsigned file, or one in a user folder such as
%AppData%, is the one to remove: end the task, then delete the file.Note the folder name, because the same folder usually holds its other files. This is the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 2: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to CoViper or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 3: Remove it from startup
Whatever CoViper installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 5: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
From our report of May 2020 · not reviewed since
Eliminate CoViper virus and avoid personal data loss
If you have never heard about CoViper virus or similar MRB wiper around, its actions performed on the machine might come as a shock - regular wallpaper is gone, the taskbar is not accessible, and the PC does not work as it is supposed to all.
Even calling up the Task Manager is impossible (this would allow killing the main process of the malware, although it can be done with apps like Process Explorer). Besides, the button to remove CoViper does not work, either. As a result, it is impossible to launch any apps or even navigate throughout the PC normally.
However, the malware is relatively flawed, and it has a backup mechanism that can be initiated with a simple CTRL+ALT+ESC combination. Once this is pressed, you should interrupt the boot sequence three times (simply press the Power button for a few seconds), and you should be able to access Safe Mode.
Then, use a portable anti-virus application that you should place into the USB stick or another removable device and then scan the computer fully for CoViper removal.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed an unfamiliar process called COVID-19.exe in Task Manager, a sign of a program that could read browser data, the clean-up is only half of the work.
The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about CoViper
Is COVID-19.exe safe?
It depends on where the file is and who signed it, not on the name. Open Task Manager, go to the Details tab, right-click COVID-19.exe and choose Open file location. A file inside Program Files or System32 with a valid digital signature from a known company is usually part of a legitimate program.
A file in AppData, Temp or ProgramData with no signature, especially one that restarts itself after you end it, is suspicious. If you cannot tie the process to anything you installed, uninstall recent unfamiliar programs and run a Microsoft Defender Offline scan.
Can I end COVID-19.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending COVID-19.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
Can I just delete COVID-19.exe?
Deleting COVID-19.exe by hand rarely removes CoViper. While the trojan runs, Windows may refuse to delete the file, and if you succeed, a scheduled task, a service or a second copy may bring it back at the next restart.
The file can also be only one part of the infection: loaders and remote access tools often install other programs. Use the Microsoft Defender offline scan, which removes the file together with its startup entries before Windows loads, and then check startup items and scheduled tasks as described in the plan.
Can CoViper spread to other devices on my network?
Most trojans aimed at home users stay on the PC they infected, but an attacker with remote access can look at the network, open shared folders and try passwords on other devices. Loaders sometimes deliver worms or ransomware that do spread.
Disconnect the PC while cleaning, run a full scan on other Windows PCs, change the router's admin password and the Wi-Fi password if they were saved on the infected PC, and update the router's firmware. If other PCs show the same detection, treat them as infected too.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught CoViper before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming CoViper, they are a strong reason to follow the full plan.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
Can I keep using the PC while CoViper is on it?
Not for anything that matters. As long as the program behind an unfamiliar process called COVID-19.exe in Task Manager runs, it can see what you type and what the browser stores, and it may download more malware. Disconnect the PC from the internet while you remove it, and do your banking, e-mail and password changes from another device.
Once the offline scan finds nothing and the sign does not return after a few restarts, normal use is fine. If the scan keeps finding new items, or you cannot remove the startup entry, a reset of Windows is the safer choice.
Is CoViper a known trojan?
Not as a documented family, at least not yet. What is known is the visible sign, an unfamiliar process called COVID-19.exe in Task Manager, which matches a hidden program working for someone else.
New threats are often seen by victims weeks before researchers publish anything about them. Treat CoViper as you would any trojan:
- remove what starts it
- run an offline scan
- change passwords from another device
If a scan reports a detection name, keep it; it usually reveals the family and whether it is known to download other malware. We update this guide when an analysis appears.
Will Fortect remove CoViper?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For CoViper, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- BankInfoSecurity: No COVID-19 Respite: Ransomware Keeps Pummeling Healthcare (read October 7, 2026)
- Decoded: CoViper locking down computers during lockdown (read October 7, 2026)
- Wikipedia: Vulnerability (computing) (read October 7, 2026)
- FTC: How to recognize, remove and avoid malware (read October 7, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 7, 2026)