
Exinariuminix.info redirect: what it is and how to stop it
Exinariuminix.info is a forwarding address that sends visitors through a click-redirect to ad and offer pages, and it has been in our reports since November 2020. The address itself installs nothing, but if it opens by itself the cause is an ad, a hacked site or adware on your device, and the steps below find it.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
A scan of the PC is a quick way to confirm that nothing installed is behind the exinariuminix.info redirects.
Do it yourself · free Remove Exinariuminix.info yourself 1 step, about 5 minutes, no software needed.
Exinariuminix.info: summary
| Type | Redirect address that forwards visitors to ad and offer pages; not a program |
|---|---|
| Risk | Medium: the address only forwards, the risk is the page at the end and any adware that opens it |
| Symptoms | Redirects to Exinariuminix.info and on to other sites, pop-ups, banners and pop-unders, prompts to click Allow |
| How to get rid of it | Close the tab; if it keeps returning, remove unknown extensions and programs, check scheduled tasks, DNS and notifications, run Microsoft Defender scans and reset the browser (steps below) |
| Our check (6 October 2026) | Forwards at once through bulkred.com to the English-language site of a game; no notification request or pop-up on that one visit |
| Running since | Domain registered 1 February 2018; in our reports since 27 November 2020 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 12 more facts
| Installed on the PC | Nothing by visiting the address; programs only if you ran something a redirect offered |
|---|---|
| Microsoft detection | None: an address is not a file, and nothing is installed by visiting it, so Microsoft Defender has no detection name to give |
| Evidence | Our test and command-line check of the forward, the domain's RDAP record and the three pictures in our 2020 report |
| Name | Exinariuminix.info |
| Domains | exinariuminix.info |
| Domain registered | 1 February 2018 |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 27 November 2020 |
| Distribution | Typically ad scripts on free streaming, file-hosting and adult sites, typo domains and hacked websites |
| Damage | Redirects to scam pages, fake updates and tech support scams |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against our own test of the address (desktop Chromium, Lithuania, one visit), a command-line check of the first forward, the RDAP record for exinariuminix.info and our November 2020 report with its three pictures.
We did not download anything from the pages at the end of the chain. The Task Scheduler and DNS steps were not tested on an infected machine, and we could not confirm that this address creates a scheduled task, as the old guide said.
What Exinariuminix.info is and where it sends you
Exinariuminix.info is a web address that forwards every visitor to other pages, not a program. Typing it or landing on it installs nothing; the pages at the end of the chain are where the risk is.
- 1
You reach the address
A link, an ad, a hacked page or a program on your device opens
exinariuminix.info. On our visit the server answered with a forward (status 302) at once, so there is no page of its own to read. The old path/nextpage.html, which our 2020 picture shows as a page of sponsors, gave the same forward. - 2
A click-redirect server takes over
The forward pointed to
bulkred.com/bens/vinos.jswithmode=redirin the link. That is the same forwarding server we met behind another address of this kind, dinoraptzor.org, which suggests one traffic network behind both. We did not establish who runs it. - 3
An offer page opens
On 6 October 2026 the chain ended on
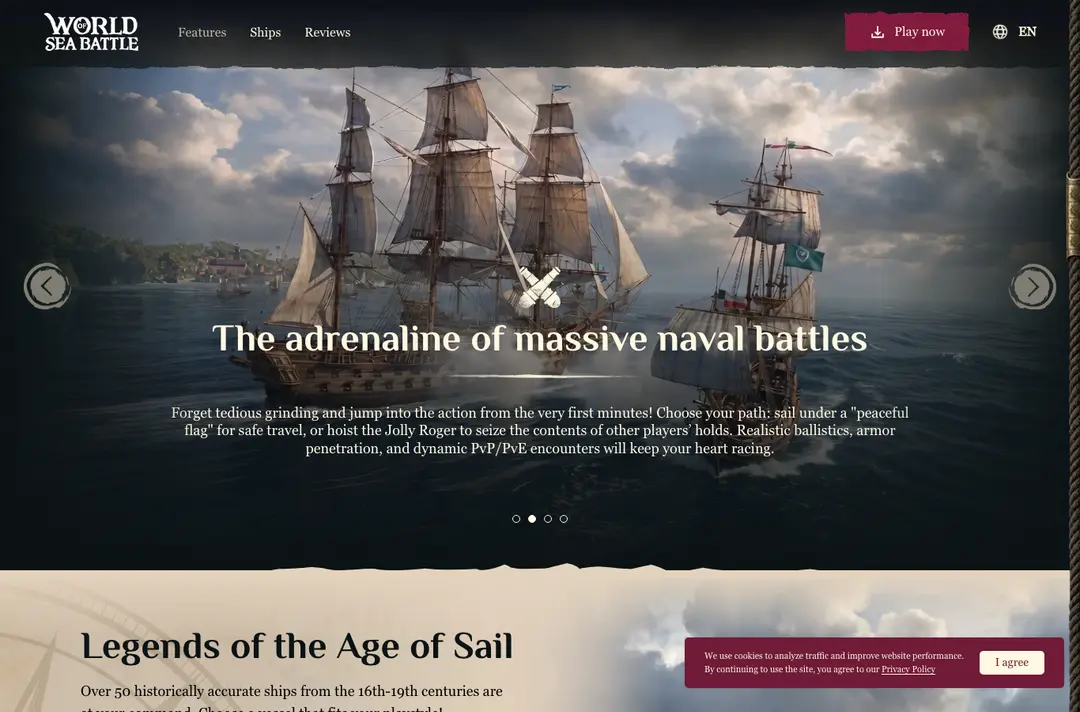
play.wosb.online, the English-language site of the game World of Sea Battle, withaffise_user_id,utmandf=cpa_...labels in the address. Who sees which page is decided by the traffic seller, not by you.
- Address
exinariuminix.info, a forwarding domain with no content of its own- What the old guide called it
- Adware (a potentially unwanted program) that shows ads and redirects. The address is not a program; what shows the ads is whatever on your device or in the pages you visit opens it
- Chain on 6 October 2026
exinariuminix.info>bulkred.com>play.wosb.online- Labels at the end of the chain
affise_user_id,utm=6andf=cpa_6_4_.... The names point to paid-traffic tracking (cpa = cost per action), so the visit is probably being paid for; we did not confirm which platform or who the buyer is- Domain registered
- 1 February 2018 (RDAP record read on 6 October 2026, registrar NameCheap, Inc.), expiring 1 February 2027; the record was last changed on 12 August 2026
- Who owns it
- Not established from the public record, so we name no owner, advertiser or traffic seller
Some domains that appear in redirects are ordinary, safe sites; this one is not a destination at all. It exists to hand visitors on, so the useful question is where it sent you and why your browser opened it. The old guide said the owners of promoted sites pay adware makers for traffic, and the paid-traffic labels at the end of the chain fit that picture, though we cannot name who pays. It also said the makers promote whoever pays most; we could not check that, and what you are sent to can change from one visit to the next.
Is Exinariuminix.info dangerous?
Our test on 6 October 2026
We loaded https://exinariuminix.info/ in a fresh desktop Chromium profile in Lithuania, without a referrer, and logged each address and request. This was a single visit, and a quiet one clears nothing.
exinariuminix.info · desktop Chromium · Lithuania (EU) · 6 October 2026
- Redirect to another domainYes, with no click at all: the browser finished on
play.wosb.online, its link full of tracking labels. A bare command-line request that used no browser received the same first forward tobulkred.com; the old path/nextpage.htmldid too. - Where it endedAn English-language page titled "World of Sea Battle", a game, with a button to download a launcher (the page names a 1.5 GB client), a Steam link and a cookie notice. We did not download or run anything from it.
- Notification requestNone on this one visit, on any page of the chain. Our 2020 picture showed a page that asked you to click Allow to prove you are not a robot, so the address has been tied to that trick before.
- Pop-ups and new tabsNo new tab or window opened, and no service worker was registered.
- Ad networksNone named by our detector. The final page contacted Facebook, Google Tag Manager and Yandex Metrica for visitor statistics, a Cloudflare Workers address and
trckcp.com, whose purpose we do not know. - Not testedOther countries, phones, a visit coming from an ad, a repeat visit and a visitor who clicks. Redirect chains often vary by country, device or time, so your page may differ.
A forwarder, not a destination On this one visit the chain led to a game's website, not to a scam page, and asked for nothing. That does not clear the address: its only job is to forward visitors through a click-redirect, it showed very different pages in 2020, and a quiet visit proves nothing about what it sends to others.
What we know about the address, in order
February 2018
The domain is registered
The RDAP record gives 1 February 2018 as the registration date, with NameCheap, Inc. as registrar.
November 2020
Our first report: a "Click Allow" page and a block message
We published our guide on 27 November 2020 and described the address as adware that pushes ads, banners and redirects. The first picture shows a white page that says "Click Allow to confirm that you are not a robot", with a line below it about accepting sponsored content, and in front of it a Malwarebytes Premium window "Website blocked". The window names the domain, the address 51.15.2.200, port 49316, type Outbound and the file
C:\Program Files (x86)\Internet Explorer\iexplore.exe, so in that case Internet Explorer made the request. The "Allow" button is the usual bait for a browser notification permission; we cannot say from the picture which prompt it was.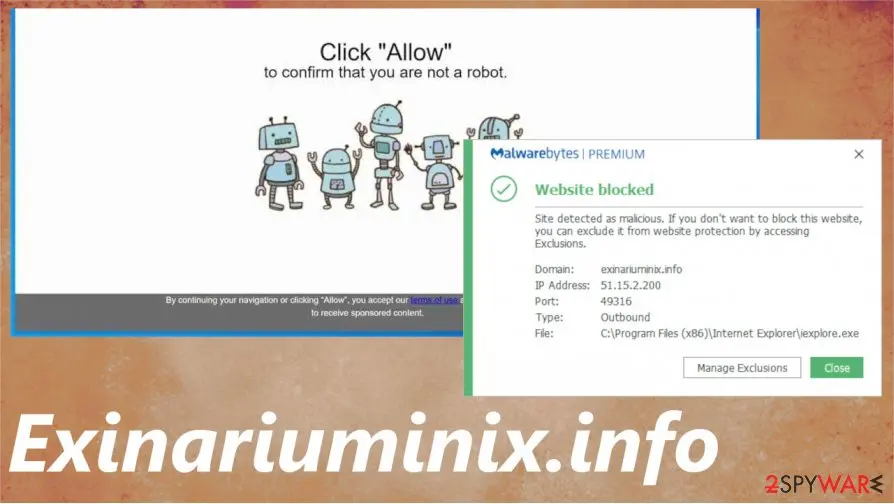
Our 2020 picture: a "Click Allow" page and the Malwarebytes Premium block message for exinariuminix.info, a connection made by Internet Explorer (iexplore.exe). November 2020
A "sponsors" page at /nextpage.html
The second picture, a browser window at
exinariuminix.info/nextpage.html, shows a tab titled "Страница спонсоров" (Russian for "sponsors page"). It is a grid of dating-style adverts in English and Russian, and over it a pop-up advert for a taxi mini-game in Russian. Behind it is the same Malwarebytes block. Our guide had a third picture of the same page with a stock photo of a woman pointing at it, which adds nothing, so we show this one only.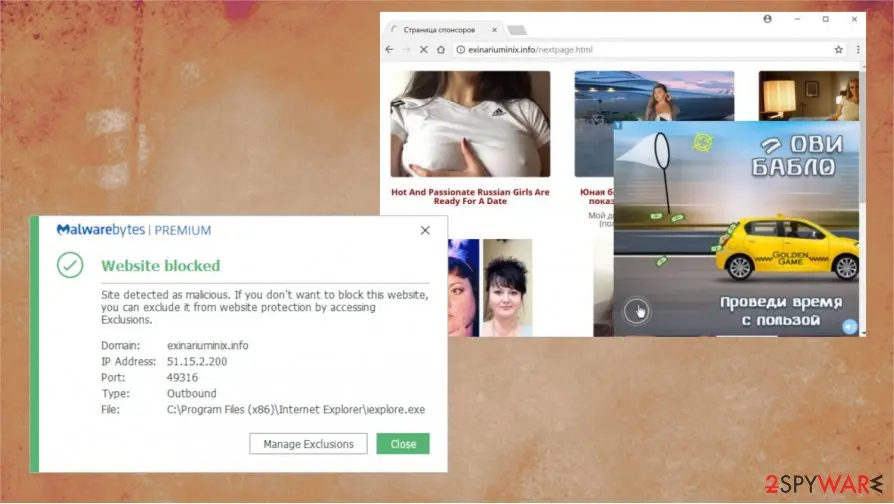
The sponsors page at exinariuminix.info/nextpage.html from our 2020 report, with the Malwarebytes block message in front. 12 August 2026
The registration record changes
The RDAP record for exinariuminix.info was last changed on this date. Nothing in the record says what changed or who controls the name.
6 October 2026
Our new check: a game's landing page
The address now forwards through bulkred.com to the English-language site of a game, with no notification request or pop-up on this one visit. The same kind of forwarding as in 2020, with a different page at the end.
What it means when you see Exinariuminix.info
The address forwards everybody, so even a spotless browser that opens it lands on an offer page. What matters is why your browser opened it, so think back to what you did a moment before.
| What happened | What it means | What to do |
|---|---|---|
| You opened it yourself, or followed a link that spelled it out | The address did what it exists to do. Your device is fine so far. | Shut the tab. Whatever page loaded, leave its Allow, Download and Install buttons alone. |
| It came up right after you pressed an ad, banner or button | The ad was passed through this address on its way to an advertiser, so you landed on a page you never chose. | Leave the page without signing up, paying or installing. |
| Tabs or windows open on their own, on many different sites, with pop-ups and banners | A program, an extension or a changed setting on your device is launching pages. That is how an adware infection usually looks. | Go through extensions, installed programs and scheduled tasks (below). |
| A page says "Click Allow" to prove you are not a robot or to continue | That is a request for permission to show notifications. Allowing it lets the site send ads to your desktop for as long as the permission stands. | Click Block, or close the tab. If you already allowed one, remove the site in your notification settings. |
| It only happens on a single website | That website, or an advert it serves, is to blame, not your computer. | Stop visiting it, or warn its owner if you trust the site. |
| A fake virus warning or a download offer shows up afterwards | Those belong to the page at the end of the chain, not to this address. | Close it. Do not phone any number it shows or open any file it gives you. |
What can go wrong after the redirect
Adware of this kind is far less serious than ransomware: it holds no virus or harmful code of its own, and the address puts nothing on your machine. The cost comes from what you do while it keeps sending you around, since someone else picks the pages and you cannot preview them. Keeping it gives you nothing back.
- High
More unwanted programs or malware
When ads keep appearing, and one can fill half the screen, a mistaken click is easy. Sponsored ads can lead to further unwanted applications or to worse malware. Landing pages also push players, updates and launchers; ours pushed a game launcher, which we left untested. Take software from its maker's own site only.
- High
Loss of money
Destinations behind redirects like this often want your details or a payment, such as dating pages, casino offers and order forms. The 2020 picture holds dating-style adverts. Some of them are traps.
- Medium
Malvertising and unsafe pages
The old guide said the address took part in malvertising campaigns, that is, ads used to carry malicious pages. We could not confirm that. Some of the sites it sends you to may be harmless, as the game site was on our visit, and some may hold malicious code or apps, so keeping this on any device is a risk.
- Medium
Notification permissions
A "Click Allow" page, as in the 2020 picture, asks to send notifications. Once allowed, ads keep arriving after the tab is closed. We saw no request on our visit.
- Low
A layer of extra ads on pages you visit
Ordinary sites can be buried under ads, banners and redirects, so you are interrupted all the time and struggle to find what you came for.
What adware behind such redirects can collect
- IP address
- Geolocation
- Websites visited
- Search queries typed in search bars
- Tracking cookies
- Links and ads clicked
- Browser and device details
Our 2020 guide said this kind of adware stores what you type in search bars, the sites you visit, your IP address and your geolocation, and that the data may be sold to the highest bidder for marketing or malicious uses. We have not seen this address collect anything, and we could not link the list to it with any source. Data like search queries can still contain sensitive details, which is why you should clean up if the redirects return.
How Exinariuminix.info got into your browser
Hardly anyone looks for a forwarding address. It follows an action, often an accidental one. Adware gets on a device without the owner meaning it to, which is why it is called a potentially unwanted program, and it is one cause among several. We found no sign on this one visit of anything more elaborate.
| Route | How it happens | What to check |
|---|---|---|
| Software bundling | The installer of a free program carries extra programs: a package of two or more apps. People download the installer of the program they want and rarely know that other programs install with it. Our 2020 guide said that almost all adware spreads this way; we cannot confirm "almost all", but it is the route it named first. | Was a free program, video tool or download helper installed shortly before it started? |
| Express or Quick setup | In this mode the installer ticks every box for you, so every extra program installs automatically. That is how adware gets on a computer and starts to get in the way of browsing. | Look at which setup type you chose last time. |
| Unsafe ads and hacked sites | An ad or a tampered site can forward the browser on the moment a page loads. Different malware is spread in different ways, and this kind needs no program on your device at all. | Does it happen on one site only? Then the site is the cause. |
| Installed on purpose | Download managers, driver updaters, system optimisers and PDF converters sometimes carry a second job of showing ads and sending you to other sites. The user installed the program but not the ads. | Look at the programs you added recently, and what they are for. |
| Altered settings | A program or extension can change browser settings, and some adware changes the DNS servers of the network connection. | See the DNS check in the steps below. |
How to remove Exinariuminix.info
How to stop the Exinariuminix.info redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Which browser shows the ads?
Remove extensions you do not recognise
Paste
chrome://extensionsinto the address bar and click Remove on anything you did not install yourself, especially anything added shortly before the redirects began.Full procedure with screenshots: Remove a browser extension
Clear the site data
Press Ctrl + Shift + Delete, choose All time, tick Cookies and other site data and Cached images and files, and click Delete data.
Reset Chrome
Open Settings > Reset settings > Restore settings to their original defaults and confirm with Reset settings. This resets the start page, search engine and pinned tabs and turns off extensions; bookmarks and saved passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Remove extensions you do not recognise
Paste
edge://extensionsinto the address bar and click Remove under anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear the site data
Open Settings > Privacy, search, and services > Delete browsing data > Choose what to clear, set All time, tick Cookies and other site data and Cached images and files, and click Clear now.
Reset Edge
Open Settings > Reset settings > Restore settings to their default values and confirm with Reset. Extensions are turned off and the start page goes back to default; favourites, history and saved passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Remove add-ons you do not recognise
Paste
about:addonsinto the address bar, open Extensions, and choose Remove from the three-dot menu of anything you did not install yourself.Full procedure with screenshots: Remove a browser extension
Clear cookies and site data
Open Settings > Privacy & Security > Cookies and Site Data > Clear Data, tick both boxes and click Clear.
Refresh Firefox
Open the menu > Help > More troubleshooting information and click Refresh Firefox. Add-ons and custom settings are removed and the home page goes back to default; bookmarks, history and passwords stay.
Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Remove extensions you do not recognise
In Safari > Settings > Extensions, select anything you did not install yourself and click Uninstall.
Clear the site data
In Safari > Settings > Privacy > Manage Website Data, remove the site's data, or use History > Clear History > all history. To empty the cache as well, turn on Show features for web developers in Settings > Advanced and choose Develop > Empty Caches.
Check the Mac for apps from the ads
Ads also target Mac users with fake players and "cleaners". In Finder > Applications, move anything unknown to the Bin. In System Settings > General > Login Items & Extensions, remove unknown items. Then use Go > Go to Folder to check
/Library/LaunchAgents,~/Library/LaunchAgents,/Library/LaunchDaemonsand/Library/Application Supportfor folders and files with the same unknown names, and empty the Bin.
Then, whichever browser you use
Step 1: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
After removal: keep the ads from coming back
If the redirects keep coming back
Landing on the address once and closing the tab leaves nothing to remove. When it returns again and again, no program named Exinariuminix.info exists in your apps list; the thing opening it sits somewhere else, commonly a browser extension, a changed setting or a scheduled task. Go through the steps in this order.
- 1
Look at your browser extensions first
In every browser you use, open the extensions page and read the list. Anything unfamiliar, especially if it is new, should go. Then watch whether the redirects stop. It takes a minute and comes first because adware often arrives as an extension that the programs list never shows.
- 2
Uninstall suspicious programs
Open Settings > Apps > Installed apps in Windows 11 (Apps & features in Windows 10, or Programs and Features in the Control Panel), sort by install date and uninstall what you do not recognise or what appeared on the day the redirects began (Uninstall a program or app in Windows On uGetFix). On a Mac, move unknown apps from Finder > Applications to the Bin.
- 3
Check the scheduled tasks
The old guide said the adware put itself into the scheduled tasks by editing the registry, so that it starts whenever the browser opens. We could not confirm that this address does so. To look, press Windows + R, type
taskschd.mscand press Enter, open Task Scheduler Library, and look for tasks you did not create that start a browser or a program from the user folders, particularly ones with random names. Right-click such a task and choose Disable or Delete, and note its name first. Leave Microsoft tasks alone. - 4
Check the DNS servers of your connection
A few adware families switch your DNS servers so that names are resolved by someone else. In Windows 11 open Settings > Network & internet > your connection (Wi-Fi or Ethernet) > Hardware properties and read DNS server assignment. If it says Manual with addresses you never typed, change it to Automatic (DHCP). On a Mac go to System Settings > Network > your connection > Details > DNS. We did not test this on a hijacked machine.
- 5
Check the notification permissions
When any page has asked you to press Allow, look through the notification permissions of your browser and delete the sites you cannot place. In Chrome the path is Settings > Privacy and security > Site settings > Notifications.
- 6
Scan, then scan offline
Start a Microsoft Defender Full scan and afterwards the Microsoft Defender Antivirus (offline scan), which catches threats that hide while Windows is running. Nothing has to be bought for this. Should the manual work fail, a full scan by a well-known security product is the next move; remove what it reports. Because adware may have touched system settings, look at the browser and DNS settings once more when the scan ends.
- 7
Clean the browser
Empty the cache and cookies, then reset every browser to its defaults, which switches off extensions and brings back the home page and search engine. Do it once the programs are gone, and in rarely used browsers too, so none of them can open the address again. The tabs above list the steps for Chrome, Edge, Firefox and Safari.
Did you enter a password or card number on a page that an ad opened? Change that password at once, and on every account where you reused it, and ring your bank about the card.
How to keep it from happening again
Installing software carelessly is the most common start, so the habits that help most are the ones used when you set up new programs.
Do
- Never choose Express or Quick installation for free software: it pre-ticks every box and installs whatever comes with it. Choose Custom or Advanced setup instead, read the list of programs and untick the ones you do not want, then continue step by step.
- Take your time with every new installer, watch for buttons placed to mislead, and refuse all extra offers.
- If you arrive at Exinariuminix.info or an address like it, shut the tab straight away and touch nothing on the page.
- Get programs from the maker's website or the Microsoft Store, and read independent reviews of any download manager, driver updater or optimiser first.
- Leave Microsoft Defender running and turn on Potentially unwanted app blocking under Windows Security > App & browser control > Reputation-based protection.
- Back up your files regularly with File History or OneDrive, so that neither an infection nor a dead disk takes your documents.
- On public networks, a VPN hides your IP address from the sites and ad networks you visit; it does not block ads or malware.
Don't
- Press an ad or banner out of curiosity.
- Choose Download, Allow or Install on a page you were sent to.
- Enter a password or card number on a page opened by an ad.
- Rush an installer because a countdown or pop-up urges you.
Questions about Exinariuminix.info
What is Exinariuminix.info?
Exinariuminix.info is a web address that forwards every visitor to other pages; it is not a program and has no content of its own. On 6 October 2026 it answered with an immediate forward to bulkred.com, a click-redirect address, which sent the browser on to the English-language site of the game World of Sea Battle, play.wosb.online.
In 2020 our pictures showed it behind a "Click Allow" page and a sponsors page of adverts. The domain was registered on 1 February 2018. We could not establish who owns it or who pays for the traffic, so we name no owner.
Is Exinariuminix.info a virus?
No, the address is not a virus: it is a website address, and visiting it installs nothing. The phrase Exinariuminix.info virus comes from adware, a browser extension or a changed setting that keeps sending the browser to the address, which is what our 2020 guide described.
Adware is not counted as a severe threat like ransomware, because it carries no virus of its own, but the pages at the end of the chain can lead to unwanted downloads and lost money. Our test was one visit and showed no notification request or pop-up, but one quiet visit does not clear an address that exists to redirect.
Why does Exinariuminix.info keep opening in my browser?
It keeps opening because something sends the browser there. After a click on an ad that is ordinary ad routing. If it appears by itself, in new tabs or on many sites, a browser extension, a program, a scheduled task or an altered setting is opening pages for you.
Our 2020 guide added that constant pop-up ads, banners and redirections usually come with it. Check the extensions of every browser for recent additions, then open Installed apps sorted by date and look at the scheduled tasks. A program called Exinariuminix.info will not be in the list.
How do I remove Exinariuminix.info redirects?
You remove the cause, because the address is only the symptom. If you merely landed on it, close the tab and you are done.
If it keeps opening, remove browser extensions you do not recognise, uninstall programs that appeared when it began, check Task Scheduler for tasks you did not create, check that your DNS servers are set to Automatic, and remove unknown sites from the notification settings.
Then run a Microsoft Defender Full scan and the offline scan, and reset each browser. The steps above give the menu paths for Windows 11 and 10, and the tabs for Chrome, Edge, Firefox and Safari. None of it needs paid software.
Where does Exinariuminix.info redirect to?
It redirects to whatever page a traffic seller sends you to at that moment, and that changes. On 6 October 2026 the chain was exinariuminix.info, then bulkred.com, then play.wosb.online, the site of the game World of Sea Battle, with paid-traffic labels in the final link.
In 2020 our pictures showed a page of sponsors with dating-style adverts and a taxi mini-game advert at exinariuminix.info/nextpage.html. We tested from Lithuania with one desktop browser; other countries, phones or a second visit may get different pages, and we did not test them.
Is it safe to open Exinariuminix.info?
It is not safe to treat it as harmless, though opening it once is unlikely to damage your device by itself. The address forwards you to pages chosen by someone else, and you cannot see them beforehand.
On our one visit the end page was a game site and asked for nothing, but in 2020 the address was shown behind a "Click Allow" prompt and a sponsors page.
If you must look at it, use a separate browser profile, do not click Allow, Download or Install, and close the tab. A quiet visit never proves an address is safe, because redirects can change by country, device and time.
Is the World of Sea Battle site it sends me to a scam?
We found nothing to show that the game site is a scam, and we are not saying it is. It is a real game that the page says is also on Steam, and our visit asked for nothing.
The point is how you got there: you did not choose the page, and it was reached through a paid-traffic forward, so the visit was probably earning someone money.
Be careful with the launcher: if you want the game, get it from the game's own Steam page, not from a link that an unwanted redirect opened. We did not download or run the launcher.
What if I clicked Allow on the page it showed?
Remove the permission, because an allowed notification lets the site keep sending ads after you close the tab. In Chrome open Settings, Privacy and security, Site settings, Notifications, find the site and choose Remove or Block. Edge has the same path under Cookies and site permissions; in Firefox use Settings, Privacy & Security, Permissions, Notifications, Settings.
A prompt that asks you to click Allow to prove you are not a robot is a request for notification permission, not a robot test. We did not see one on our 2026 visit, but our 2020 picture showed such a page.
What should I do if I entered details or ran a file from the page it sent me to?
Act on what you gave away. If you typed a password, change it now and on any other account that used it; if you entered a card number, call your bank. If you downloaded and ran a file, do not run it again, uninstall it in Installed apps and run a Microsoft Defender Full scan and offline scan.
Keep a note of the page, the file name and the time, which helps if you need to report a payment. Our test did not download or run anything, so we cannot say what a file from the chain does. If an employer manages the computer, tell your IT team.
Will Fortect remove Exinariuminix.info?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Exinariuminix.info, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- RDAP record: exinariuminix.info (registration 2018-02-01, changed 2026-08-12, registrar NameCheap, Inc.) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 4, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 4, 2026)