
Extortion Scam: how to spot it and what to do
Extortion Scam is scam email campaign that is used to blackmail victims into paying money. While it is unclear how many separate scammers are involved in the scam, there are hundreds of variants floating around the internet.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Extortion Scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps
Extortion Scam: summary
| Name | Extortion Scam |
|---|---|
| Type | Phishing message |
| Symptoms | A phishing e-mail asking you to sign in |
| Evidence | 7 write-ups by security sites; details still limited |
| Arrives as | |
| Pretends to be | A well-known company |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 4 more facts
| Claim | Your account needs urgent attention |
|---|---|
| Asks for | Your password |
| First seen | 11 September 2020 |
| Facts checked | 7 October 2026 |
What the Extortion Scam message looks like
Of course you can will change your password, or already made it. But it doesn't matter, my rat software update it every time.
How to tell the Extortion Scam message is fake
From our report of Sep 2020 · not reviewed since
Phishing emails have been around for a long time: learn how to recognize them
Cybercriminals often use social engineering to trick their victims, so it comes as no surprise that phishing emails are one of the most widely spread scam methods around.
In most cases, spam and phishing emails are used to deliver malware payloads, such as ransomware or banking trojans. However, some criminals use a more direct approach, trying to lie about the infection itself which does not actually exist.
Unfortunately, not many users are IT savvy and do not know how viruses work, or anything about their infiltration tactics. For such reasons, there are thousands of people who fall for the trick, cleverly engineered by cybercriminals. Here are some tips by experts on how to avoid scams:
If you received a scam email, report it to the appropriate bodies in your area and change your passwords.
- Do not panic when you receive a threatening email;
- Read through it carefully; even if your password or name is mentioned, it does not mean your PC is infected with malware;
- Copy and paste first line of the scam message and search for it online - there will be plenty hints that it is a scam;
From our report of Sep 2020 · not reviewed since
More from our earlier report on Extortion Scam
- Blackmail users into paying money in Bitcoin
- Bad actors try to scare users into believing that their system has been hacked and controversial photos/videos taken
- Ignore the email, report it to the appropriate authorities and change all your passwords
- Scan your machine with security software such as or .
- Different variants of Extortion Scams do not change the primary goal
- But I was struck by the sites of intimate content that you very often visit.
- I am in shock of your reach fantasies!
- I've never seen anything like this!
- I did not even know that SUCH content could be so exciting!
Is Extortion Scam dangerous? What the senders want
From our report of Sep 2020 · not reviewed since
Extortion Scam - a phishing email campaign used for blackmailing users to make them pay ransom in Bitcoin
Extortion Scam is scam email campaign that is used to blackmail victims into paying money.
While it is unclear how many separate scammers are involved in the scam, there are hundreds of variants floating around the internet. While the text of the email might differ slightly, the content remains the same.
Typically, bad actors claim that users' machine has been hacked and the malware has been injected into their system. Allegedly, victims were recorded via the web camera while they were visiting porn sites. Extortion Scam then proceeds with a demand of a ransom to be paid into the specified Bitcoin wallet for the attackers not to reveal the leaked photos/videos to victims' relatives and friends.
What makes these type of scams believable is that they usually include a user's password or/and the name in the Subject line of the email, making users panic and believe that the email is genuine. If you encountered extortion scam yourself, never give in to demands of email authors, as they acquired your personal information through dark web hacking portals, and your computer is most likely malware-free.
The password or other personal information that is included inside the Extortion Scam provides the feeling of it being real, and many people fall for it. How do crooks know this information? It is relatively simple, and they are not sophisticated hackers who create complex malware to do all the things they claim they do.
Extortion Scam authors simply use information that was leaked in data breaches - they happen every day. Whether it is a large organization, a small online shop or e-commerce website, all the information leaked from these sites end up on the Dark Web. Surprisingly, email addresses and names are relatively cheap, so anybody can buy as much data as they need.
The data sold might be old, so that is why users often see an old password in the Extortion Scam emails. However, criminals are quick to elaborate on the issue, claiming that the alleged malware that is installed on the system is capable of reading all passwords, regardless if it has been changed or not. For example:
Another reason why Extortion Scam works is that it affects a sensitive topic - the one that people usually want to keep private, and crooks are threatening to disclose these images to users' relatives, friends and social media platforms. Therefore, many users are simply too ashamed and pay the demanded money which can reach $7,000.
In some cases, Extortion Scam email asks users to transfer the money within a certain amount of time (e.g., two days), or all of the leaked photos will be exposed and device locked. Basically, extortionists are trying to use all possible scare tactics in order to make terrified victims pay.
Extortion Scams (sextortion) have been around for many years, but previously mainly focused on extorting nude videos or pictures and then blackmailing them into disclosing those. However, the model of such blackmailing changed completely, and bad actors now focus on receiving a large amount of money.
The FBI reported that in July 2018 alone, the amount of Extortion Scam reports increased by 13,000 comparing it to previous months. Additionally, there are thousands of unreported occurrences, so the scale of the operation is large, and can involve organized crime members.
You should remove Extortion Scam message from your inbox immediately and ignore everything that is written inside the email. In case an infection was present, eliminate it and then use to fix virus damage and bring your machine to a working state.
From our report of Sep 2020 · not reviewed since
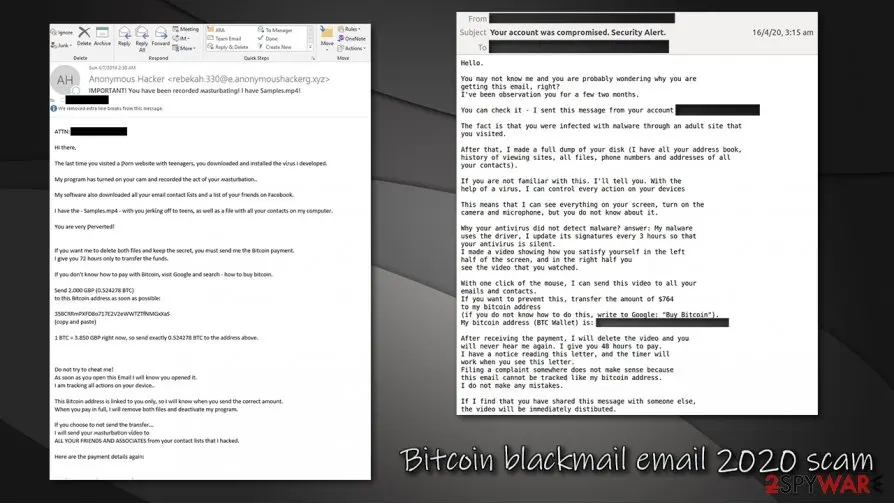
Bitcoin blackmail email 2020 scam
In the wake of the coronavirus epidemic, many people were forced to work from home - they either connect to the management programs or used remote connections (RDP, for example) to perform daily tasks. Students and kids were also forced to stay home due to the pandemic.
Those who usually went out for a coffee on a daily basis or frequently visited the cinema were also forced to seek entertainment at home. As a result, internet traffic increased dramatically, as Netflix, Facebook, and many other websites saw a significant rise in visitors and new subscriptions. Unfortunately, cybercriminals knew such tendencies very well and saw an opportunity to cash up quickly.
In April, the Federal Trade Commission issued another warning about a wave of Bitcoin blackmail email 2020 scam.
Just like with other types of fraud, Bitcoin blackmail email 2020 scam authors attempt to exploit people's minds by using sensitive subjects. The claims of malware infection, hacking, disclosure of the personal password, and sensitive footage leakage are just a few of many traits that might make users give in to the scam and pay up.
You should never pay attention to such unsolicited claims that are stated in the Bitcoin blackmail email 2020 scam, as you will most certainly lose money for nothing. Attackers do not have any information or video footage about you - they got your password from the hacking forums, and this is all just a scheme to extort money from innocent users.
From our report of Sep 2020 · not reviewed since
I have bad news for you email scam
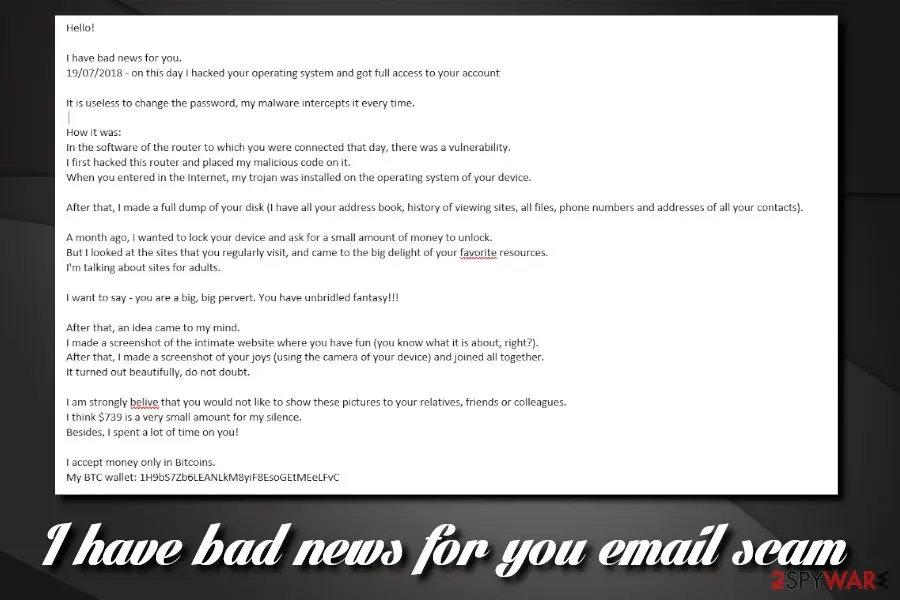
This variant of the extortion scam provides a date when victims' computer was allegedly infected with malware via the vulnerability in the router.
Cybercriminal then proceeds with explaining how the "infection" compromised the whole operating system of the victim.
According to the scam email, the hacker initially wanted to lock up the device in order to ask for a small amount of money. But instead, he or she checked websites that the victim regularly visits and decided to go with the blackmailing tactic instead.
I have bad news for you Email Scam then asks users to pay $813 into a specified Bitcoin wallet to keep the pictures away from relatives, friends, and colleagues. You should under no circumstances try to contact cybercriminals, as you will end up being scammed.
From our report of Sep 2020 · not reviewed since
I am a spyware software developer email scam
As the title says, this scam claims that the originator of the email is a software developer.
He or she claims that the victim visited a dangerous website and disclosed the email password. Hacker then explains that malware has been inserted into the operating system, and changing the password will not help.
Bad actor asks for $900 in order to keep the supposedly taken pictures away from relatives and friends. As usual, human emotions and shame feelings are exploited, ensuring that some users will fall for the trick.
I am a spyware software developer email scam is full of red flags when it comes to its legitimacy. Users who understand how viruses work would know that the scenario explained by the email author is not possible, as even malware cannot be transferred to victims' machine via the email unless they open attachments or click on malicious links.
Thus, I am a spyware software developer email is another hoax, trying to pretend that the threat is real.
From our report of Sep 2020 · not reviewed since
I'm a programmer who cracked your email scam
This fraudulent message is almost identical to I am a spyware software developer email scam with the subject line "Security Alert.
Your account has been hacked" or "Email is compromised. Password must be changed". It also claims that the email author was a skilled programmer who injected a malicious code onto the operating system. Victims are asked to pay $870 into a specified Bitcoin wallet.
Bad actors are trying to shame the victim by stating the following:
The fake email is littered with grammar and spelling mistakes, so it only brings a conclusion that the author is probably not from an English-speaking country. Nevertheless, please remove I'm a programmer who cracked your email scam from your inbox and change all your passwords.
From our report of Sep 2020 · not reviewed since
Porn Blackmail virus
Porn Blackmail virus is one of the Extortion Scam variants.
The purpose of the scam is the same - to make users pay a ransom of up to $7,000 in Bitcoin. Scammers include the password of the target in the Subject line, which might be terrifying to most of the people who receive such an email in their Inbox.
The difference between Porn Blackmail virus and previous versions is that it claims that the user visited a porn website which was infected with malware. Allegedly, using a Remote Desktop, they managed to gain remote access to the PC, hack the camera, and film the controversial video of the victim.
The crooks promise to delete all the videos they obtained if the payment in Bitcoin would be transferred into a specific wallet. Also, they threaten to expose the video if the ransom is not paid within a day and highly discourage users from going to the police.
As usual, ignore cybercriminals and do not get tricked by Porn Blackmail virus.
What to do after the Extortion Scam e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you entered a password after clicking the link in the Extortion Scam message, treat that account as known to the sender.
Open the provider's real site by typing its address yourself, not through any link in the e-mail, and change the password there. Choose a new one you have never used before, and change it on every other account that shared the old one.
Then use the option to sign out of all other sessions or devices, if the provider has one. This works the same in any browser on Windows 11 and Windows 10.
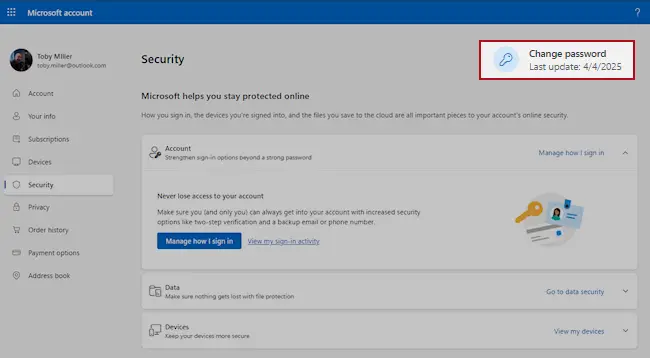
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
Two-step verification asks for a code from your phone or an authenticator app whenever someone signs in from a new device. A stolen password alone is then not enough to open the mailbox.
Turn it on in the security settings of the e-mail account first, then for the bank, shop and social accounts that send their reset links to that address.
While you are there, check the recovery e-mail and phone number and the forwarding rules, which attackers sometimes change to keep access. The settings pages look the same on Windows 11 and Windows 10.
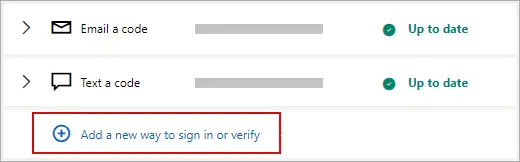
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Report the message instead of only deleting it. In Outlook choose Report > Report phishing, in Gmail the three-dot menu > Report phishing; the provider then blocks the same message for other people.
Do not reply and do not click anything else in it. On a work account, forward it to your IT team as an attachment first. Web mail and the mail apps on Windows 11 and Windows 10 offer the same options.
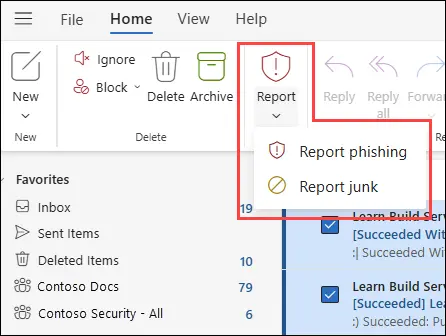
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A page that only asked for a password installs nothing, so most readers can skip this step.
If the Extortion Scam e-mail or the page it opened made you download or open a file, delete it and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
From our report of Sep 2020 · not reviewed since
Get rid of Extortion Scam email without contacting crooks
After receiving a scam message, you should make sure that your system is not compromised.
We suggest using , or (Safe Mode with Networking is the best environment to do so) for Extortion Scam virus removal. If no malware is present on your computer, you should immediately change your passwords on your accounts, and report the incident.
As soon as that is done, you can safely remove Extortion Scam email from your Inbox with no consequences whatsoever. Remember, all the personal information disclosed in the email was acquired from a data breach, so as long as your passwords are updated, you should be safe.
[GI=method-1]If you are unsure whether or not your PC is infected with malware, enter Safe Mode with Networking and perform full system scan:
[GI=method-2]You can also eliminate the virus with the help of System Restore.
Questions about Extortion Scam
Does getting "Of course you can will change your password, or already made it." mean my account was compromised?
Not by itself. Phishing waves are sent to long lists of addresses collected from old breaches, websites and guessing, and the sender does not know whether you even have the account the message mentions. Getting "Of course you can will change your password, or already made it." only means your address is on such a list.
It becomes a problem if you sign in through the link. To be sure, open the real service from a bookmark and check recent activity and security alerts. If you see nothing unusual and you did not type your password into the fake page, your account is fine.
The "Of course you can will change your password, or already made it." page asked for my code too. Is two-step verification enough?
Not when you typed the code yourself. Some phishing pages pass your password and the one-time code to the real site in real time, which lets the attacker sign in once.
Change the password immediately, then sign out of all sessions so the stolen session ends. Check the account's security page for new devices, app passwords and recovery details, and remove anything you did not add.
A passkey or a hardware key is the strongest protection against this trick, because it cannot be typed into a fake page. Keep the e-mail "Of course you can will change your password, or already made it." for your report, then delete it.
Is Extortion Scam really from a well-known company?
No. It is sent by scammers who copy the name and look of a well-known company. The sender address and the links do not belong to it, and the message asks for your password, which a real company does not request through an unexpected message.
If you want to be sure about your account, open the website or app of a well-known company the way you normally do, not through the message, and look for notices there. Then delete the message and report it as phishing. If you already followed its instructions, use the steps in this guide for your case.
Is it true that your account needs urgent attention?
No. The claim that your account needs urgent attention is the hook of Extortion Scam, invented to give you a reason to act quickly. Scammers pick a story that could plausibly apply to many people, so it may feel relevant to you, but nothing in the message is based on your real accounts or devices.
If the claim concerns a service you use, check it there directly, by opening the website or app yourself. You will find no such problem. Then delete the message and report it as phishing.
What happens if I do what Extortion Scam asks?
The scammers get your password, and they use it quickly. Passwords are tried on the real service within minutes, cards are charged or added to phone wallets, remote access is used to open your bank, and crypto is moved on at once.
Documents surface later as accounts in your name. If you already did what the message asked, do not wait to see what happens; follow the steps in this guide for your case today. Speed matters more than anything else here.
Will a well-known company refund me if I fell for Extortion Scam?
A well-known company did not send the message and is not responsible for it, so a refund usually comes from your bank or card issuer, not from the brand. Call the bank first if you paid.
It still helps to tell the real company: they can secure your account, add notes for their fraud team and take down pages that use their name. Contact them through their official website or app only, never through the message or a search ad. Keep the message as evidence.
How do I report Extortion Scam to my mail provider?
Use the built-in button. In Outlook, select the message and choose Report > Report phishing. In Gmail, open the message, click the three-dot menu and choose Report phishing.
Scam text messages can be forwarded to your carrier's spam number, which is 7726 in the US and the UK.
On social networks, use the report option on the message or the profile. Reporting trains the filters that protect you and other users, and it takes a few seconds. Then delete the message.
How quickly do scammers use a phished password?
Often within minutes. Phishing kits send each password to the operators as soon as it is typed, and many test it automatically on the real service. Some kits also pass the two-step code through in real time.
That is why the first hour matters: change the password, end all sessions and check that the recovery details are still yours. If nothing has changed by then, you were probably fast enough, but keep watching for login alerts and password-reset e-mails for a few weeks.
Does receiving Extortion Scam mean I was hacked?
No. A e-mail like this is sent to huge lists at once, and your address or number is on one of them, most likely because it appeared in a data breach or on a public page. Nothing on your PC caused it.
What would matter is whether anyone signed in to your accounts; check recent sign-in activity in your e-mail and bank accounts if you are worried. Turn on two-step verification for the important ones, then delete the message and report it as phishing.
Will Fortect remove Extortion Scam?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Extortion Scam, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- 2-spyware: Magecart strikes again: targets Shopper Approved eCommerce websites (read October 7, 2026)
- Fox News: Paid Content: Here's how much your personal information is selling for on the dark web (read October 7, 2026)
- Talos Intelligence: Anatomy of a sextortion scam (read October 7, 2026)
- FTC: Scam emails demand Bitcoin, threaten blackmail (read October 7, 2026)
- The Conversation: What are software vulnerabilities, and why are there so many of them? (read October 7, 2026)