
Google redirect ads: what it is and how to remove it
"Google redirect virus" is a term used to describe browser hijackers, adware, and other potentially unwanted programs that display intrusive advertisements, change the homepage, alter search results on Chrome web browser. As evident, these infections have nothing to do with the tech giants themselves and are created by third parties that seek to monetize ad revenue.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Not sure what sends your browser to mystartsearch.com? An automatic scan looks at the usual sources for you.
Do it yourself · free Remove Google redirect ads yourself 3 steps, about 9 minutes, no software needed.
Start the steps
Google redirect ads: summary
| Name | Google redirect |
|---|---|
| Type | Adware, browser hijackers and other PUPs |
| Infection means | Third-party websites, bundled software, advertisements, official sites of unwanted programs |
| Symptoms | Symptoms vary depending on type of infection; however, users will notice strange behavior on Google Chrome, such as frequent redirects to suspicious sites, pop-up ads, alternative search results, changed startup page and new tab URL, etc. |
| Risk factors | Malware infection, money loss, sensitive information disclosure to unknown parties, etc. |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Distribution | Not recorded in the old report |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 14 write-ups by security sites; details still limited |
| Domains | mystartsearch.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 25 May 2020 |
| Facts checked | 6 October 2026 |
What the Google redirect ads ads look like
We are not affiliated with or related to Google Lead Services™ in any way. The term "Google" is used as a synonym for "Search"
Is Google redirect ads dangerous?
What readers reported about Google redirect
My browser is causing redirects to Mystartsearch. I can't fix my browser. No matter what site I decide to visit, I am redirected to mystartsearch. Is it safe? Can I use it instead of Google?
Safesurfs.com redirects keep bothering. Solution?. Safesurfs.com has replaced Google search and started redirecting me to unknown online shops and other doubtful sites. It's very annoying since I cannot find relevant information. How can I remove Safesurfs.com hijacker? Please advise.
Redirects to Websearch.the-searcheng.info. My Google search redirects me to Websearch.the-searcheng.info search site all the time. Why? I'm I infected with Google redirect virus or is it something different?
How to get rid of incredibar?. I ve got a problem, everytime i start firefox it redirects me to other search engine 'MyStart' by IncrediBar. mystart.incredibar.com I'm trying to fing the answers in google, on incredibar virus removal, but it seems there is no information.. how do I get rid of it?
From the comments under our earlier guide; names and contact details removed.
From our report of May 2020 · not reviewed since
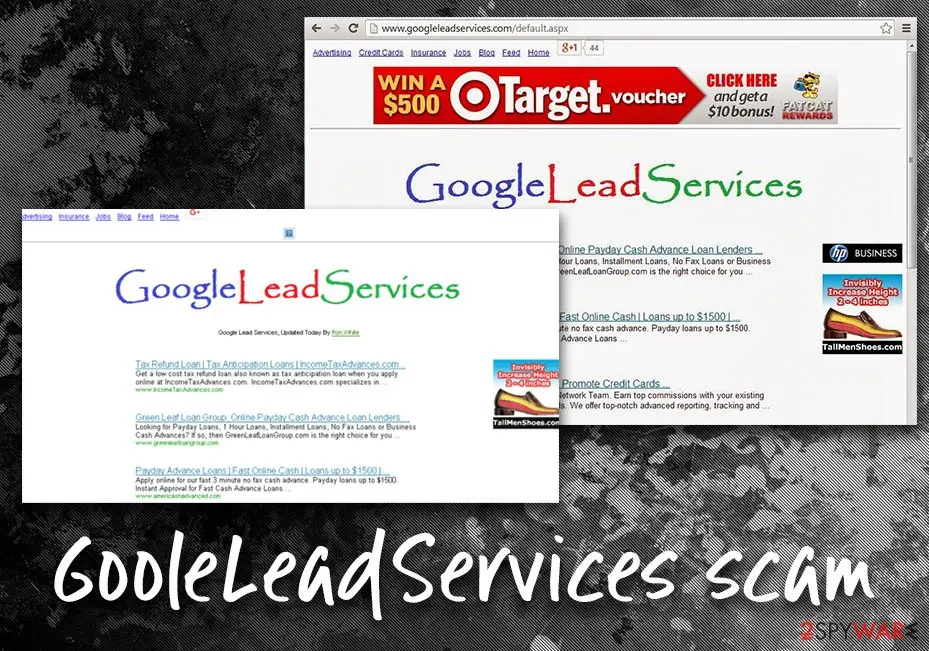
Do not trust Google Lead Services - its is not related to the real tech company
Google Lead Services is a threat to your computer, and it is not related to Ad Services (all the concepts, features, and networks that comprise Google AdWords account).
You should know that redirects through GoogleAdServices.com occur each time you click on an ad in legitimate search results; however, if you happen to be using a fake version of it or a search engine controlled by a browser hijacker, you might experience redirects that go through an alternative domain. If you check the website, it states the following:
It seems that the problem with this domain has been bothering both Windows and Mac users for years. Some people complain about a Cookie that prevents smooth navigation in Safari and other browsers. If you have run into this domain during your browsing session, we highly suggest scanning your computer and removing all files and components associated with it.
In case you experience continuous redirects to the described domain, check if your browser's shortcuts aren't affected. You can find a comprehensive tutorial on how to do it right below the article.
From our report of May 2020 · not reviewed since
The redirect scheme becomes more and more popular
Redirecting users to modified versions of Google, injecting ads and collecting victims' search terms helps companies make money by driving traffic to predetermined sites.
Some of the authors of such redirect viruses join hands with online advertisers or specific third parties. By directing users to certain websites, they get a certain share of the profit from web traffic.
As we have already mentioned, some of these sites can be entirely harmless (Yahoo, Bing, Facebook or Comcast), but it does not apply to all of them. Modified search results can contain links pointing straight to deceptive or malicious Internet sites you definitely do not want to enter.
If you notice something suspicious, or if you feel that you can't trust the search results, check if your system isn't infected with:
Be aware that the matter is extremely dangerous and can compromise your computer by stopping it from functioning normally, locking your files, stealing your credentials or other sensitive data, or even corrupting Windows operating system.
- browser hijacker
- adware app
- other potentially unwanted program
- malware
From our report of May 2020 · not reviewed since
Do not trust apps only because they are on Chrome Web Store
Chrome Web Store as such was launched in 2010.
Since then, millions of Chrome extensions have been downloaded by Chrome users, and, luckily, most of them were lucky to download original variants. Unfortunately, in 2015 complaints started spreading about copycat extensions being spread on the Store infecting users with adware and browser hijacking malware that initiates active these redirect campaigns.
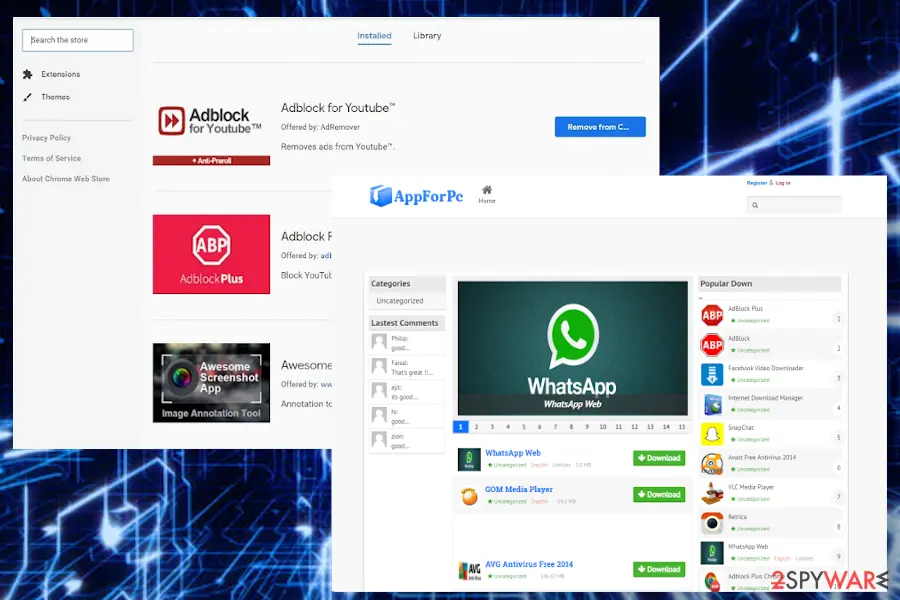
One of the first cases spotted in 2015 on the Chrome Web Store was related to the fake AdBlock Super, AdBlock Plus, and other AdBlock applications. Millions of people installed highly popular AdBlock apps believing that they are genuine. However, these rogue variants not only failed to block intrusive advertising but also redirected to the prodownnet extension download site.
In other words, the Chrome Web Store has become a spamming platform due to a lack of control over the apps that are being offered. According to researchers, the fake AdBlock apps have been downloaded by millions of people who later on started suffering prodownnet redirects to the following domains:
Although the prodownnet virus is not the most suitable term to describe a website that promotes malware, many people on forums expressed their anger about intrusive browser hijacking and unstoppable Google redirects to the mentioned domains. The fact that the mentioned redirect virus is actively promoting other malware is worse than the redirects in general.
Once the fake Adblock app is installed, the browser's settings are altered in a way to redirect people to downnetpro.info/adblock-plus/ and prodownnet.info/adblock-plus/, or another malicious website, where they are asked to download more malicious apps. These are the apps being promoted:
Moreover, such redirects can also lead to a browser hijacking. Upon installation of fake Adblock apps and redirect to prodownnet, Chrome's start page, search provider, new tab URL, and other settings can be aggressively modified. Despite being annoying, such changes pose the risk of redirects to unwanted or potentially dangerous domains, which is why we strongly recommend being very careful with malware and eliminate it asap.
It seems that the prodownnet.info domain has been suspended, as well as the apps that promoted it have been taken from the Chrome Web Store. Nevertheless, people keep looking for answers on how do I get rid of a browser hijacker that redirects to downnetpro.info or related sites, so be careful and do not slip on ad-supported rogue adblockers that can diminish your web browsing experience.
Keep in mind that despite multiple measures that the security expert team at the company takes to protect the Chrome Web Store from malware, hackers seem to be a step forward.
In spring 2020, researchers reported 500 Chrome extensions found on the store that has been freely harvesting browsing data and transmitting it to C2 servers. Besides, they've also been included in the Google redirect scheme and promoting malware like the prodownnet virus.
Therefore, it's important to investigate each extension before downloading it from seemingly trustworthy sources. Read the comments section and check the web for the findings of cybersecurity experts. If you see flags about the extension being ma;ware-related, do not install it under any circumstances.
People who noticed suspicious browser redirect symptoms right after visiting the Chrome Web Store should try to remove prodownnet and related PUPs from the system. The best way to do that is to run an automated scan with or a similar utility.
- downnetpro.info/adblock-plus/
- prodownnet.info/adblock-plus/
- Adguard
- GOM Media Player
- Facebook Video Downloader
- VLC Media Player
- Retrica
- Internet Download Manager
- Adblock Plus Chrome
- Adblock Super
- Adblock Pro
- Adblock Plus Popup
- AdBlock
- AdBlock Plus
- Zenmate
- Periscope
- Scorp
- Shazam, etc.
From our report of May 2020 · not reviewed since
Avoid malware using these easy tips
At first glance, it may seem that installing a free application from trusted sources will exclude you from the burden of PUP and malware.
However, few users realize that even recklessly installing the latest update of Skype or Java might lead them to install unwanted elements, such as adware, browser hijackers , as well.
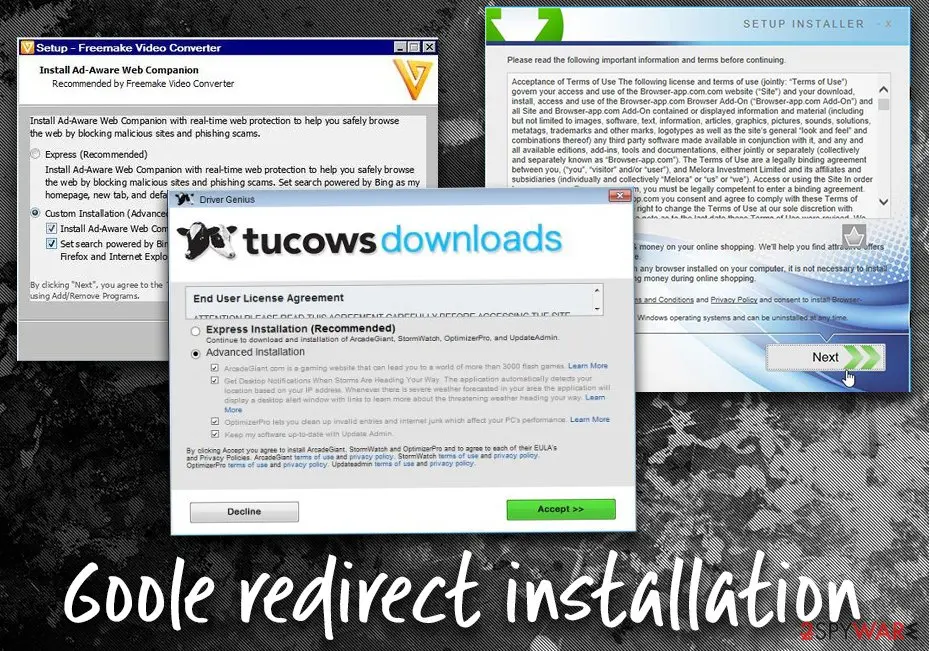
What you have to do when installing freeware and shareware is to monitor its installation process carefully. Choose "Custom" or "Advanced" installation method. It discloses optional download options. Remove the checkmarks from irrelevant add-ons and only then click on the "Install" button.
Quite often, users might be mislead by skipping text in fine print during the installation procedure. It usually states the following:
For that reason, it is extremely important to check all the fine print, otherwise you might agree to things you never would,
Due to the flexible form, the malware might also function via web scripts. In that case, you might not spot any specific changes in the browser. Luckily, even then, there is a solution - check the removal section.
From our report of May 2020 · not reviewed since
More from our earlier report on Google redirect
- Some PUPs might act as malware and alter system settings or infect core files.
- To revert the damage done, use
- By clicking Next, you agree to the Terms and conditions and Privacy Policy and consent to install app.
- Your browser may be restarted
From our report of May 2020 · not reviewed since
Google redirect virus is a set of potentially dangerous computer infections that seek to benefit from ad revenue while exposing users to unsafe content
"Google redirect virus" is a term used to describe browser hijackers, adware, and other potentially unwanted programs that display intrusive advertisements, change the homepage, alter search results on Chrome web browser.
As evident, these infections have nothing to do with the tech giants themselves and are created by third parties that seek to monetize ad revenue. In the meantime, users' web browsing experience suffers as they struggle to find relevant information, battle the annoying pop-ups, and have to deal with the slow operation of the browser.
On the other hand, Google itself has received enough criticism for spying on its users , bypassing phishing links among its search results, and allowing malicious apps into Chrome Web Store or Play Store.
Despite that, the industry giant is trying to reduce the malware inside its own store by tightening its security, improving scanners that block malicious URLs, and providing users with plenty of information on how site admins can protect their visitors from malware.
The majority of complaints reporting URL redirects on Google pages and similar search engines were recorded in 2012. However, the threat is still viable as it surfaces once in a while.
Both Windows 10, Linux, and Mac OS users can be victimized. Note that Google redirect virus iPhone and Android versions also exist. Alternatively, this virus is known as Chrome redirect virus.
There is no wonder why it is so active this year. Browser hijackers causing redirects typically target Chrome users because it is the most popular web browser in the world. Clearly, it means that attacking users of this browser means hitting the right spot with the biggest number of potential victims.
The potentially unwanted program (usually a browser hijacker) meddles with browser settings and worsens the user's browsing and search experience. Typically, such programs are designed to collect victim's search terms and browsing history data and contaminate regular search results with ads.
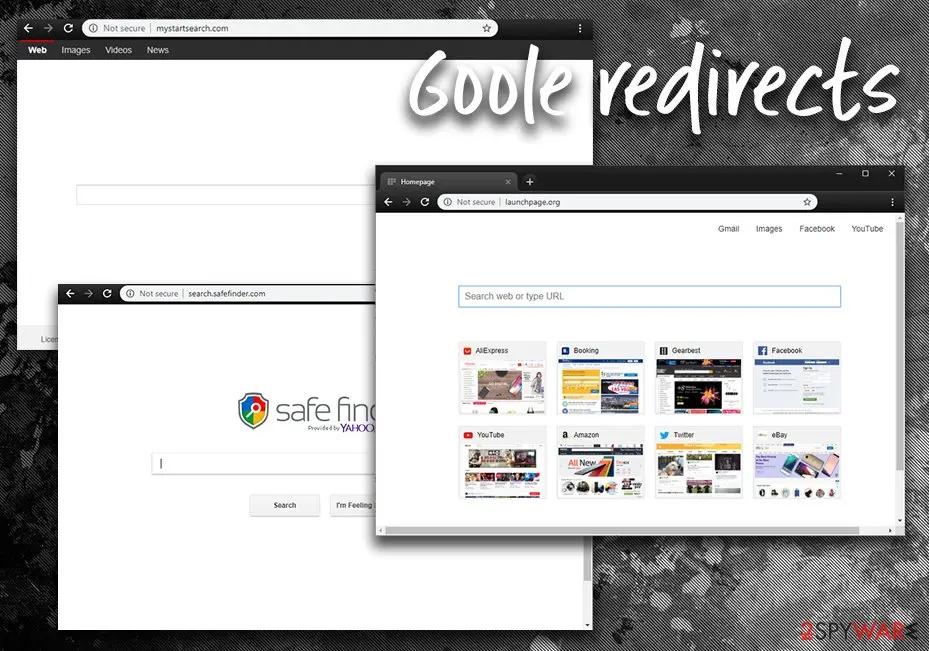
In case you noticed an excessive amount of ads in your search results or if their appearance raises your suspicion, check your system for a browser redirect virus. Some of the programs known to be causing such redirects are:
In case you noticed that Google redirects you to Yahoo or other domains (these sites can be either well-known ones or totally new to you), you should take necessary measures to solve the problem. Just like Yahoo Redirect virus and Bing redirect virus, Safari redirect virus, it functions as a hybrid of a browser hijacker and adware.
The main problem here is its elimination - the infection can hide under any URL domain name, so it might troublesome to eradicate it manually. or speed up the virus removal process. can also save your time by wiping all web scripts and "helper elements." It is of utmost importance to "uninstall" them all in order not to experience this issue again.
Some users start wondering if they're infected with some type of threat after experiencing bookmarks redirecting issue. If your browser unexpectedly initiates a redirect loop once you attempt to open your bookmarks, do not worry.
This issue is common and can be fixed quite easily. Usually, all that it takes to fix the problem is to clear browser cache, cookies, and history, or to sign out of your Google account, close the browser and sign in again.
- Mystartsearch.com
- Launchpage.org
- Weknow.ac
- YesSearches
- Safe Finder, etc.
From our report of May 2020 · not reviewed since
Browser Redirect dangers explained
Browser redirects, while not as dangerous as Petna or Cerber malware, are still a threat to your online safety and computer security.
Besides, such activity can highly tamper with which websites you visit and which ads you click on. Due to the increased number of advertisements, you might struggle to find relevant information online.
Before we discuss the prevention of browser hijackers, let's take a look at the most common symptoms of this infection:
Such phenomena should not be ignored even if excessive advertising does not bother you. This issue has nothing to do with safe browsing and, even if you have a reputable malware elimination tool installed on your computer, remain vigilant while adding a new toolbar or a browser extension.
- Google redirects to Comcast, Bing, Yahoo and similar websites. Naturally, it might trigger the appearance of pop-up alerts. In any case, such behavior indicates that the browser is plagued by a browser infection.
- Altered browser and system settings. Typically, this virus changes the default search engine, new tab, and the homepage. It might also append extra extensions.
- Foisted commercial content in the search results. If the search engine is changed to some fishy Ask or PlusNetwork tool, you might notice more commercial ads beside the search result.
- Tracking your online activities. More aggressive versions of browser redirect viruses might not only compile information about your frequently visited websites and search entries but gather personal details, such as name, email, IP and home addresses and trade this data with business partners.
Check your browser and PC
- Address:
mystartsearch.com
How to remove Google redirect ads
How to stop the Google redirect redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Step 1: Check the browser's extensions
A browser that keeps landing on
mystartsearch.comby itself usually has an add-on doing it. Open the extension list (chrome://extensions, edge://extensions, or Extensions and themes in the Firefox menu) and remove anything you do not remember installing.Coupon, PDF, new tab, search and video downloader add-ons are the usual suspects. Do this in every browser on the Windows 11 or Windows 10 PC.
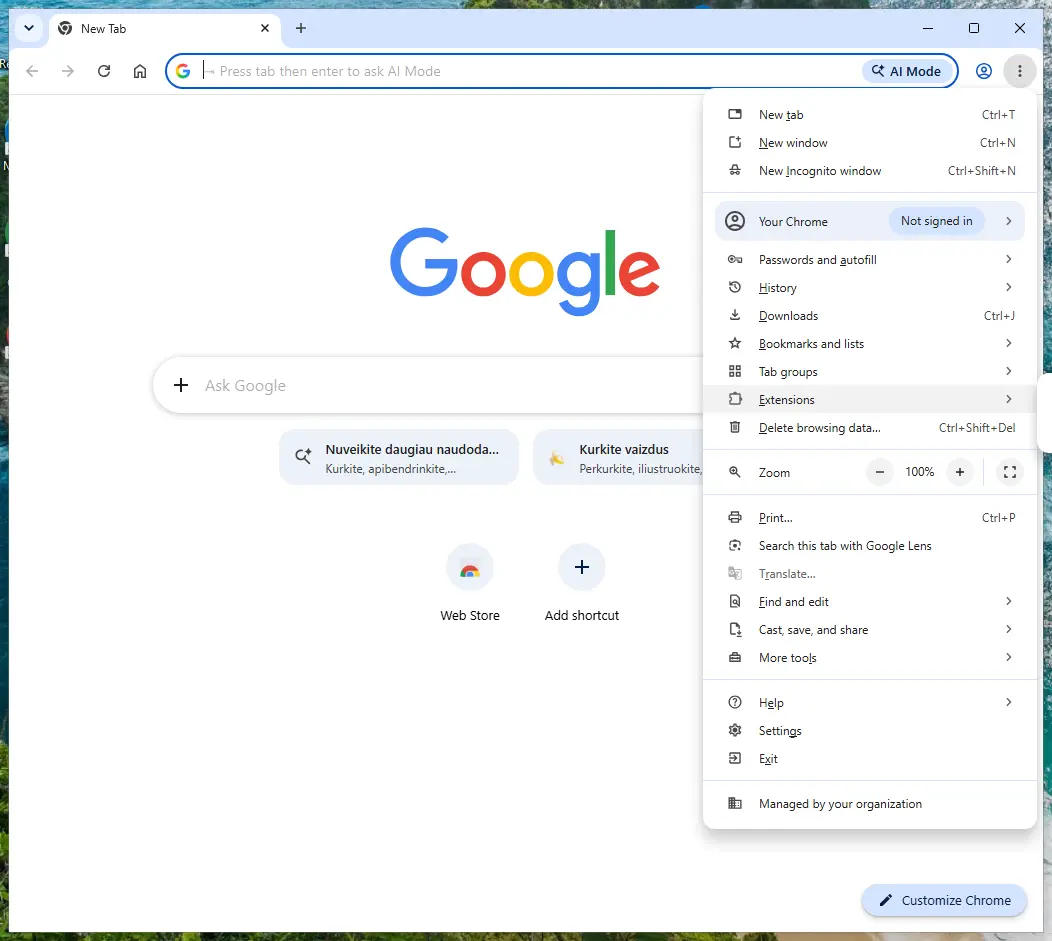
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Reset the browser if the redirects continue
When
mystartsearch.comkeeps opening after the extensions are cleaned, reset the browser to its defaults. Chrome: Settings > Reset settings > Restore settings to their original defaults; Edge: Settings > Reset settings; Firefox: Help > More troubleshooting information > Refresh Firefox.A reset keeps bookmarks and saved passwords but clears site permissions, the start page and the search engine.
If every browser still redirects afterwards, the cause is a program in Windows 11 or Windows 10: check Settings > Apps > Installed apps for anything you did not install.
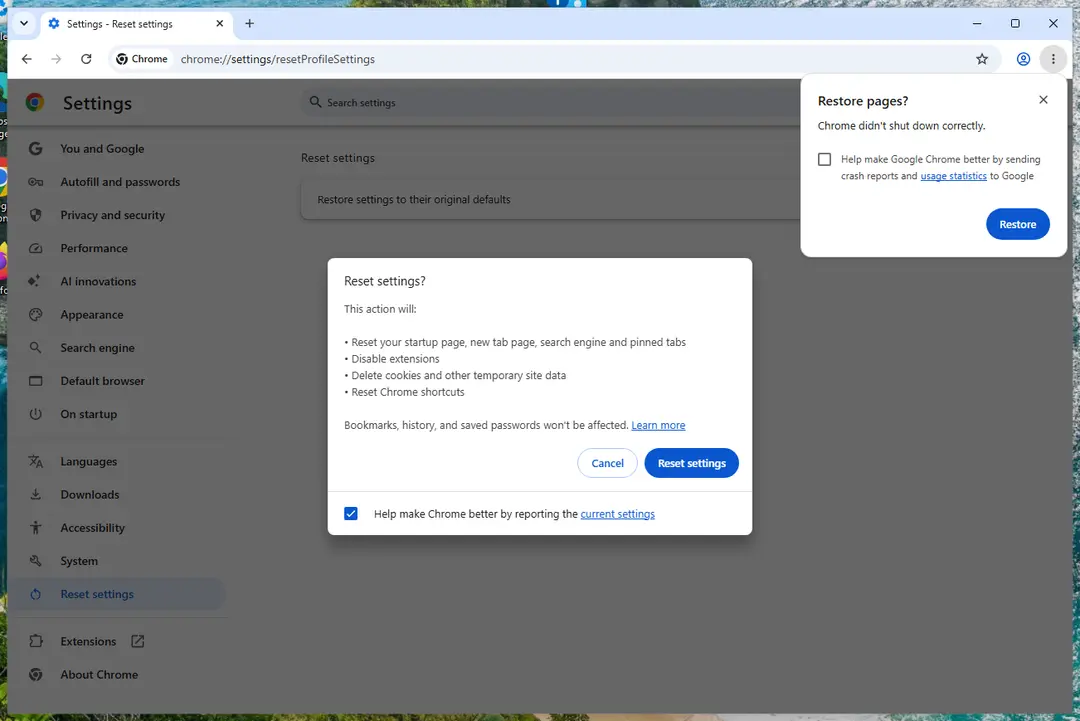
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Scan the PC if you downloaded anything from the ads
Most people who only saw the notifications can skip this step. If a notification or the page it opened made you download or run a file, delete the file and run a full scan, then a Microsoft Defender Offline scan.
In Windows 11 and Windows 10 open Windows Security > Virus & threat protection > Scan options, select Microsoft Defender Antivirus (offline scan) and click Scan now. The PC restarts and the scan takes about 15 minutes, so save your work first.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
To eliminate the browser redirect problem, you need to uninstall all programs/apps that seem suspicious. Also, you should definitely get rid of programs that you can't remember installing on your computer.
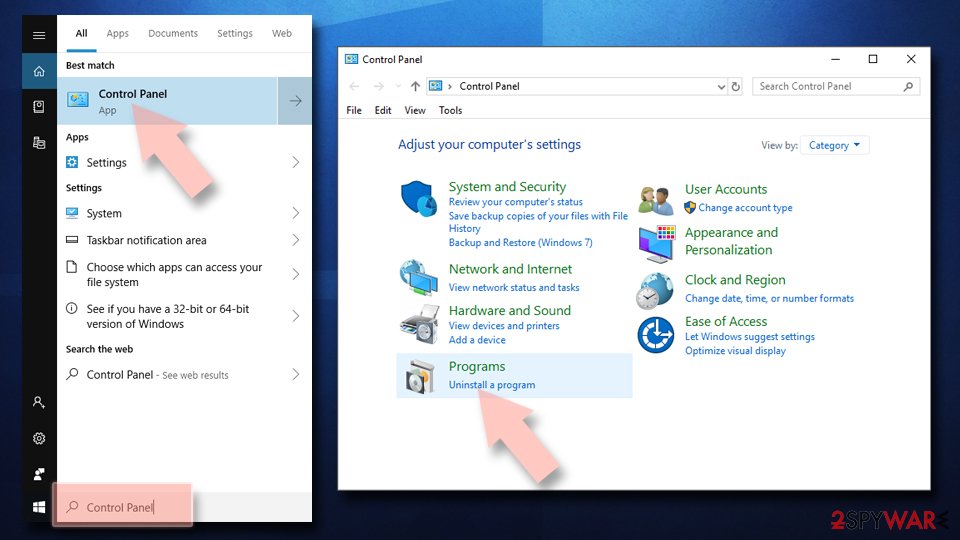
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
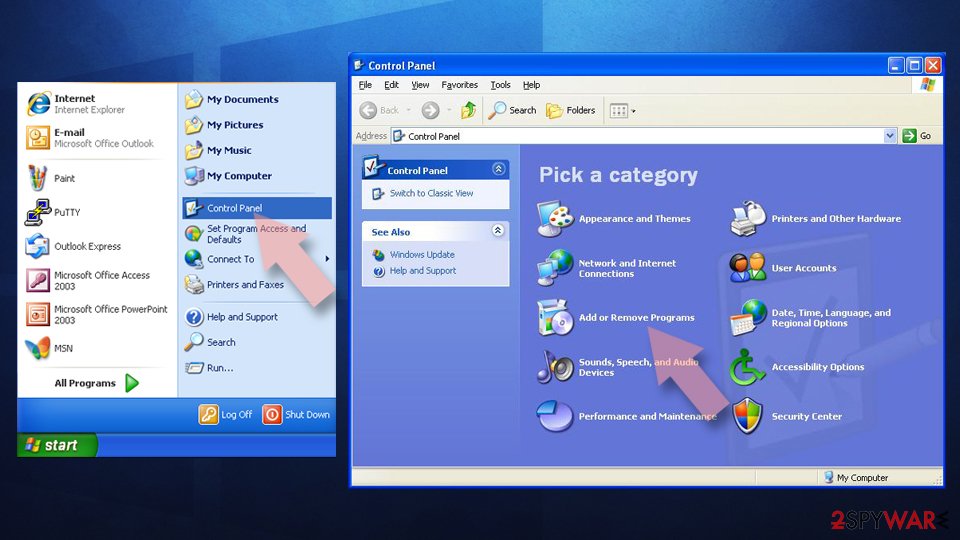
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
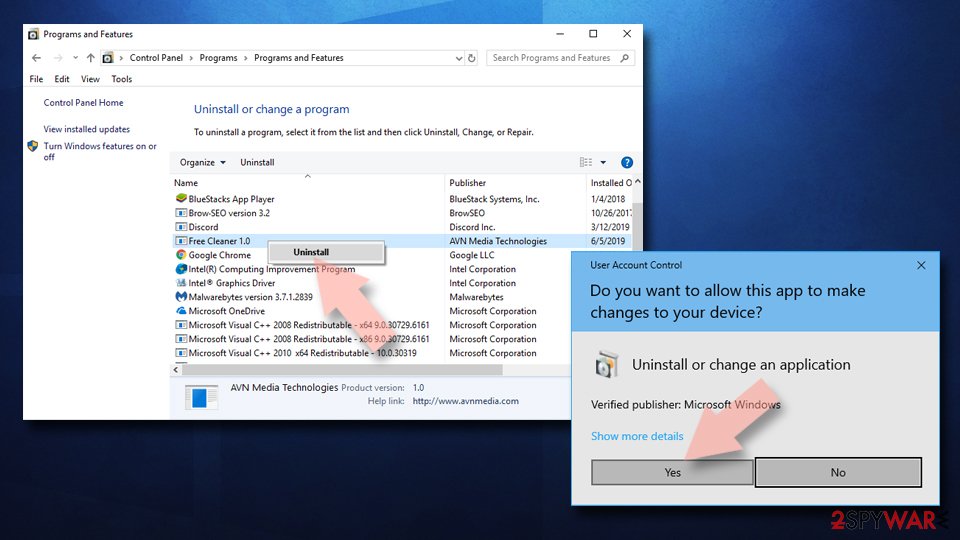
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
To fix Chrome web browser and forget about redirects to unknown websites, you should double-check your extensions. Make sure you remove all entries that look questionable or that you can't even remember installing on your web browser:
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
To remove the virus from Safari, eliminate unwanted extensions and reset the browser.
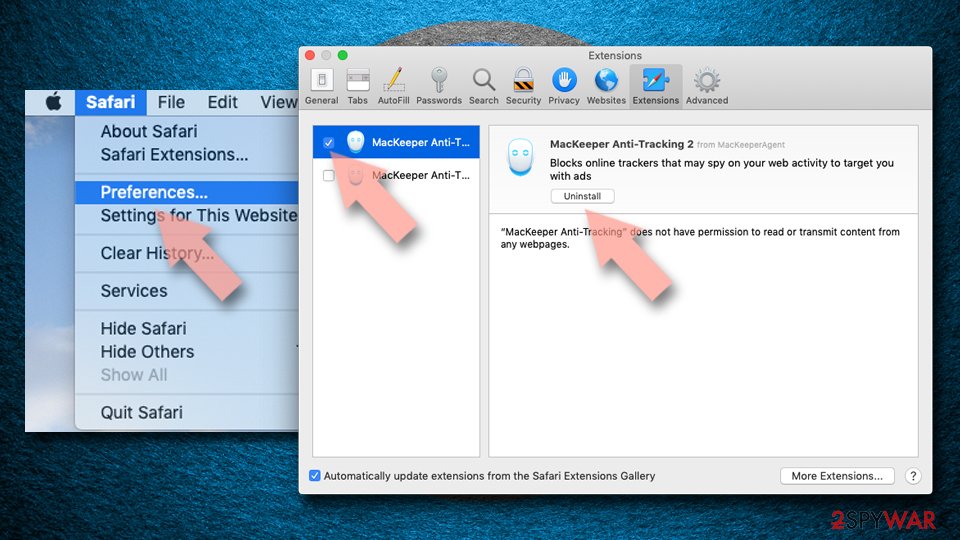
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
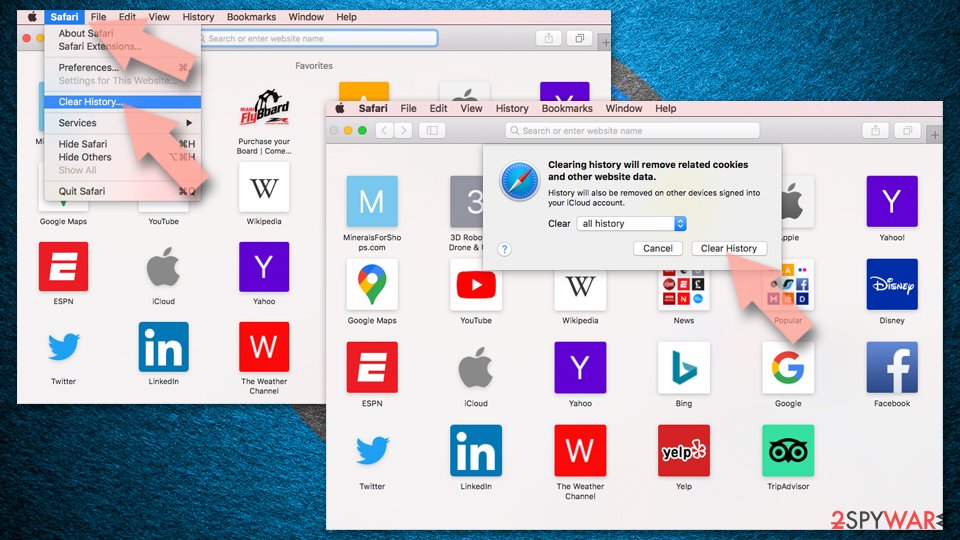
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
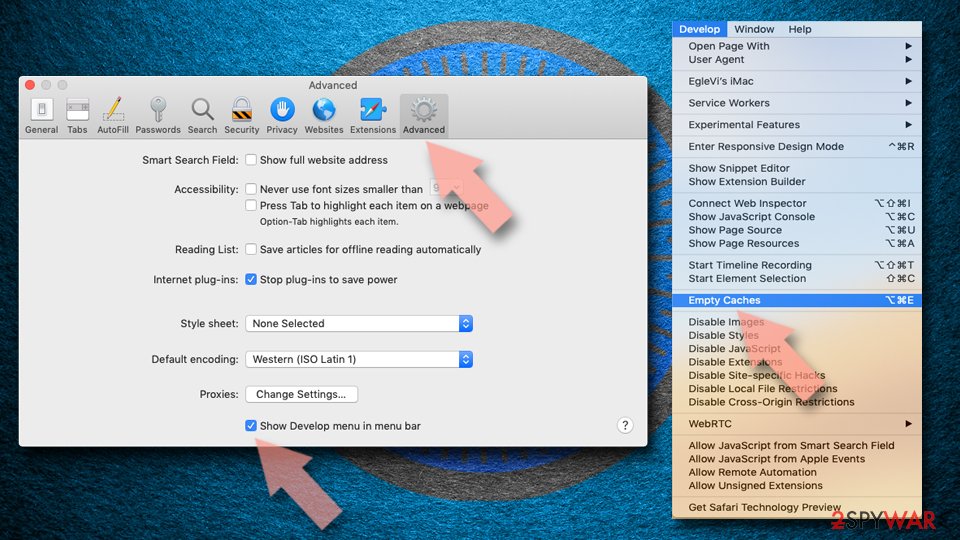
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
To fix your Mac OS X, you should try to find all entries that seem unknown to you. All apps that you can't remember installing on your computer should be eliminated.
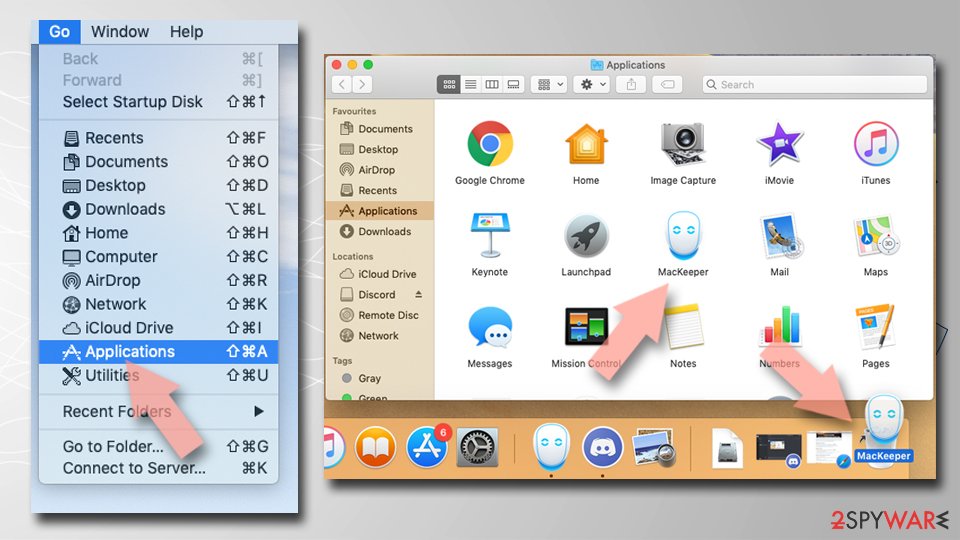
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
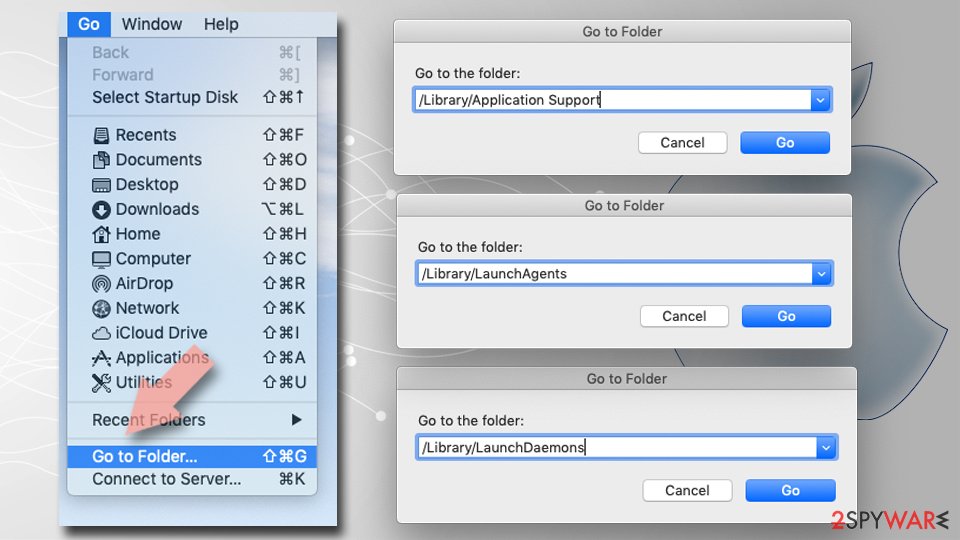
- Finally, empty the Trash to permanently remove the leftovers.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of May 2020 · not reviewed since
Remove Google redirect virus from your PC
Run an anti-spyware tool to start the PUP removal process.
The software will also locate delete the registry keys associated with the threat. After scanning the system, you need to look over detected items and remove them all at once. With the help of an anti-spyware program, this can be done with a single mouse click. They instruct how to get rid of unwanted and dubious browser add-ons.
Full browser reset also facilitates the removal process. If you are still bothered by the occasional redirects, change your proxy settings and host file.
You can find the instructions specific for your browser on the Web. Now proceed to the below guidelines. Safari users will also find the Google redirect scam removal instructions for their browser.
Though the infection is widely spread and operates already for several users, it might take users' liking residing in a specific country, for instance, Germany.
Questions about Google redirect ads
mystartsearch.com opens when I click links. What causes it?
When every click leads to mystartsearch.com first, an extension or a script on the page is rewriting the links. If it happens only on one site, that site uses aggressive ads; close it and use another source. If it happens everywhere, open the browser in a private window, where extensions are normally off, and try again.
No redirect in the private window means one of your extensions is responsible: remove the ones you do not know. A redirect in the private window too means the cause is outside the extensions, such as a notification permission, a changed search setting or a program installed on the PC. The removal steps in this guide cover each of those.
Is it safe that my browser was redirected to mystartsearch.com?
Landing on mystartsearch.com does not infect the PC by itself. A browser does not run programs from a page without your action. The danger is in the pages that come next:
- some ask you to allow notifications
- some show fake virus warnings
- some offer downloads
- ask for card details
If you only saw those pages and closed them, nothing more is needed than removing whatever caused the redirect. If you allowed notifications, remove that permission.
If you downloaded a file, delete it unopened, or uninstall it if you ran it. If you typed a password or card number on one of the pages, change the password and call your bank.
What is Google redirect?
Google redirect is an ad redirect domain, a kind of adware. It earns money by showing redirects through ad pages, and each view, click or redirect pays whoever runs it. It is not something people usually choose; it arrives through a free download, a fake button or a misleading prompt.
Google redirect does not encrypt files or take control of Windows, but its ads are sold to anyone, including scam operators, so they can lead to fake virus warnings and unwanted downloads. The steps in this guide remove it from Windows and from each browser.
Why does mystartsearch.com keep showing up?
There are two possible reasons. If it appears as desktop notifications, a browser on this PC was given permission to receive them from mystartsearch.com, usually through a misleading prompt. That permission stays until you remove it in the browser's site settings.
If it appears as tabs or redirects, an ad on a site you visit is opening it, or an extension or program on the PC is. Test a private window: if mystartsearch.com never appears there, an extension is the likely cause. The plan above covers each case.
Which browsers does Google redirect affect?
In the cases we checked, Google redirect showed up in Chrome, Edge and Firefox. That does not rule out others on your PC, since adware installers often target every browser they find, and permissions and extensions sync across computers signed in to the same browser account.
Open each browser you have, go to its extensions page and its notification settings, and remove anything you do not recognise. Profiles count separately: Chrome and Edge can each hold several, and each one needs checking on its own.
Are the pop-ups I see really from Google redirect?
Compare them with the details in the table above. Google redirect produces redirects through ad pages, and the clearest sign of it is redirects to mystartsearch.com. Other adware looks similar, so check the name of the sending site at the bottom of a notification, the address in the tab that opened, or the newest entries on the extensions page.
If those match, this guide fits. If you see a different name, the same kind of steps apply, but remove the item you actually find rather than guessing.
I let a "support technician" from an ad connect to my PC. What should I do?
Act quickly but calmly. Disconnect the PC from the internet first, so the connection ends. Uninstall the remote access tool they asked you to install and check Installed apps for anything else added during the call.
Run a Microsoft Defender full scan and offline scan. From another device, change your e-mail and banking passwords and sign out of all sessions.
If you paid by card, bank transfer or gift card, contact your bank or the card issuer immediately, and report the scam to the police. Do not answer if they call back.
Can an adware pop-up infect my PC just by appearing?
No. A pop-up, a notification or a new tab is only a web page or a message. It cannot run programs on Windows by itself, provided the browser and Windows are up to date. Infection needs a step from you:
- running a downloaded file
- installing an extension
- giving a stranger remote access
That is why scam pages work so hard to make you click. Close such pages with the tab's X or by closing the browser, not with buttons inside the page, which may start a download.
My scan found nothing, but the ads continue. Why?
Because the source may not be a file a scanner looks for. Browser notifications are a permission stored in the browser, and many adware extensions are not flagged because they come from an official store.
Some ad-supported programs are only reported if you enable detection of potentially unwanted apps. So a clean scan does not mean the job is done. Check each browser's notification permissions and extension list by hand, and turn on Potentially unwanted app blocking in Windows Security before scanning again.
Will Fortect remove Google redirect?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Google redirect, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- SearchSecurity: Browser hijacker (browser hijacking) (read October 6, 2026)
- The Guardian: Google will stop scanning content of personal emails (read October 6, 2026)
- ZDNet: Google let scammers post a perfectly spoofed Amazon ad in its search results (read October 6, 2026)
- The Register: Google Play Store spews malware onto 9 million 'Droids (read October 6, 2026)
- Google Support: Enhance phishing and malware protection (no longer online) (read October 6, 2026)
- Microsoft Community blog: How to remove the Google Redirect Virus? (read October 6, 2026)
- Wikipedia, the free encyclopedia: Potentially unwanted program (read October 6, 2026)
- Google Chrome Help forum: Google search redirects to yahoo (read October 6, 2026)
- Reddit: Fake AdBlock Plus App (read October 6, 2026)
- ThreatPost: 500 Malicious Chrome Extensions Impact Millions of Users (read October 6, 2026)
- 2spyware: What are browser hijackers and how to remove them (read October 6, 2026)
- Dieviren: How to eliminate computer malware (read October 6, 2026)