
LookupShare ads: what it is and how to remove it
LookupShare is an adware program that takes 12 MB of disk space and appears in the Applications folder of macOS machines. User reports claim that some type of Yahoo redirect virus appeared on Safari after the unexpected installation of the adware app.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
Not sure what sends your browser to lesvirus.fr? An automatic scan looks at the usual sources for you.
Do it yourself · free Remove LookupShare ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps
LookupShare ads: summary
| Distribution | Adware apps are promoted via software bundling, unsecured networks, and their hyperlinks/adverts |
|---|---|
| Name | LookupShare |
| Type | Adware application/potentially unwanted program |
| OS and browsers affected | The suspicious product has been created specifically for macOS computer systems and can appear on web browsers such as Google Chrome, Mozilla Firefox, and Safari |
| Goal | Developers who have produced this suspicious application seek to gather income from the cost-per-click method |
| Activities | The main tasks carried out by this adware are intense advertising during browsing sessions, redirecting to affiliate domains, tracking the user's online sessions, etc. LookupShare virus might even tend to bring other PUPs together with itself |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Symptoms | Redirects to an unknown domain |
| Evidence | 4 write-ups by security sites; details still limited |
| Domains | lesvirus.fr |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 24 October 2019 |
| Facts checked | 6 October 2026 |
Is LookupShare ads dangerous?
From our report of Oct 2019 · not reviewed since
LookupShare - adware that might bring other PUPs to macOS
LookupShare is an adware program that takes 12 MB of disk space and appears in the Applications folder of macOS machines.
User reports claim that some type of Yahoo redirect virus appeared on Safari after the unexpected installation of the adware app. Continuously, the adware itself might append major changes to web browsers such as Chrome, Firefox, and Safari. You can expect LookupShare to perform modifications on the homepage and new tab search. Besides, the PUP will supposedly relate to harsh redirecting and advertising activities in the nearest future.
The aim of LookupShare is to collect cost-per-click income from pop-up ads, banner texts, in-text adverts, and other promoted content. Once the affected user clicks on a particular advertisement, money falls straight to the developers' pockets. Nevertheless, third-parties might try to push bogus products through intense advertising. Most commonly, rogue security software is promoted and users are encouraged to buy a useless tool for a high price sometimes.
Additionally, LookupShare virus might attack you with intrusive surveys and questionnaires and ask you to fill some private or technical details. Usually, users are encouraged to reveal personal information if they want to claim a fake prize or reward, for example, an Android/iPhone mobile phone device. We advise not to do that as by revealing sensitive data, you might put yourself in danger of personal information or even identity exposure.
Continuously, adware such as LookupShare is involved in redirecting activities that are supposed to take the user to affiliate sources and provide attractive-looking deals.
However, this process is not that harmless as it might seem from the first view as you might accidentally (or maybe even intentionally) be taken to a malware-laden domain. This is one of the main ways of how users get infected with dangerous viruses such as Trojan horses or ransomware.
Furthermore, LookupShare virus might plant browser helper objects (BHOs) in the infected web browsers. You might spot newly-injected extensions, add-ons, and plug-ins in your browser settings that you did not insert on your own. Also, adware programs can insert tracking objects such as pixels, beacons, and cookies that aim to capture user online activities and browsing history. The captured information usually refers to:
After this information falls in the hands of third-parties, they use it to deliver targeted advertising on the users' computer screens. The developers identify what types of products/services are relevant for the user at the moment and generate adverts regarding the person's needs, however, the offers are often fake and created just for income. You might also see some questionable offers and deals from LookupShare adware.
If you start experiencing unwanted activities and changes after the appearance of this adware, you should remove LookupShare from your macOS machine and web browsers such as Chrome, Firefox, and Safari. To terminate the potentially unwanted program entirely, you have to be sure that no suspicious objects are left lurking on your machine or browser apps, otherwise, the ad-supported application might easily return.
You can perform LookupShare removal in two different techniques - manual/automatical. The first one requires the user's interaction with all infected sources and components. The second one requires only employing reliable software and leaving the job for the program.
Once the adware is no more on your system and browsers, you can try fixing any corrupted places with a tool such as in case the PUP has made more difficult changes than expected.
- IP address.
- Geolocation.
- Search query data.
- Hyperlinks/ads clicked.
- Saved bookmarks.
- Deals/offers searched.
- Commonly visited networks.


From our report of Oct 2019 · not reviewed since
More from our earlier report on LookupShare
- Get rid of the PUP automatically or manually.
- Try using to diminish any changes that were hard to remove at the first place
Check your browser and PC
- Address:
lesvirus.fr
How to remove LookupShare ads
How to remove LookupShare from a Mac
Remove the app and what starts it, then check the browsers.
Step 1: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from LookupShare or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 2: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 3: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 4: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
To eliminate bogus content from Google Chrome and refresh the entire browser, complete these steps
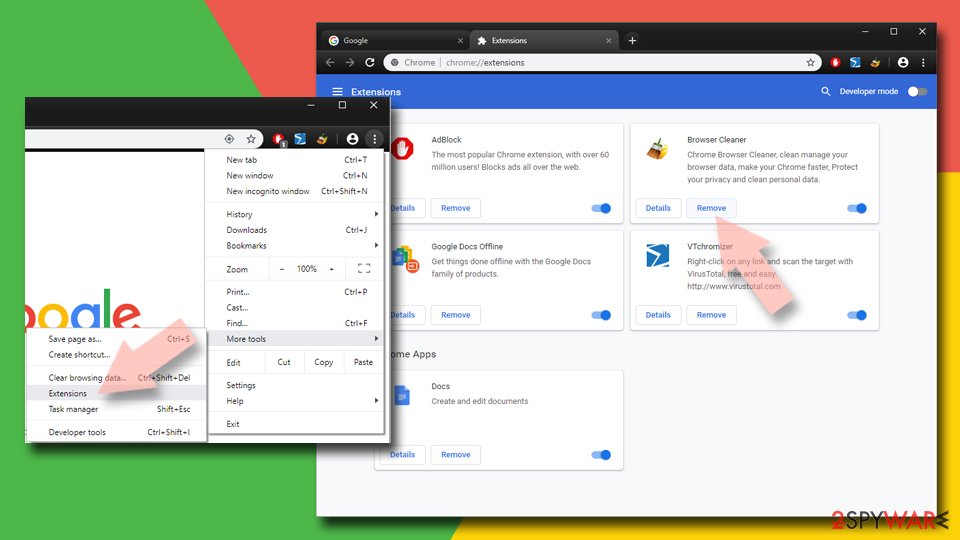
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
Clear cache and web data from Chrome:
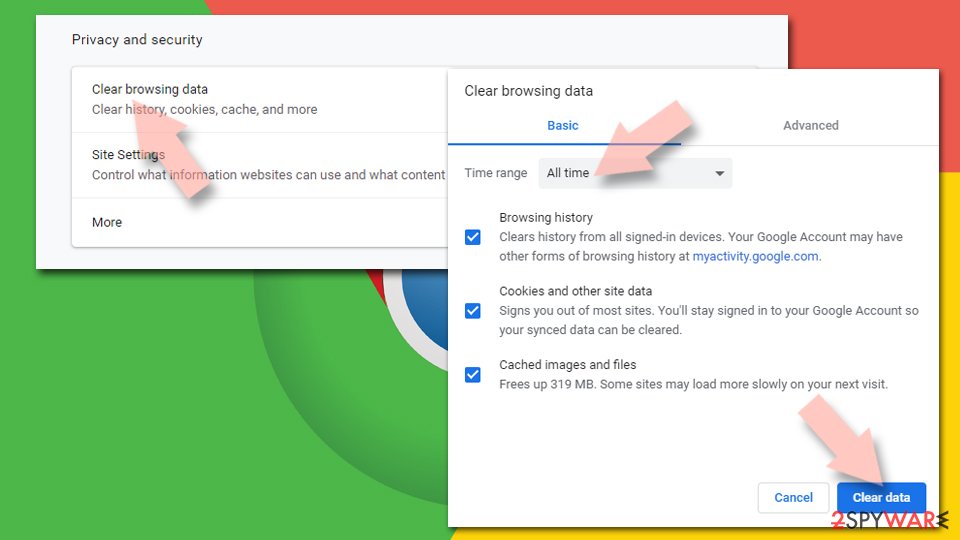
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
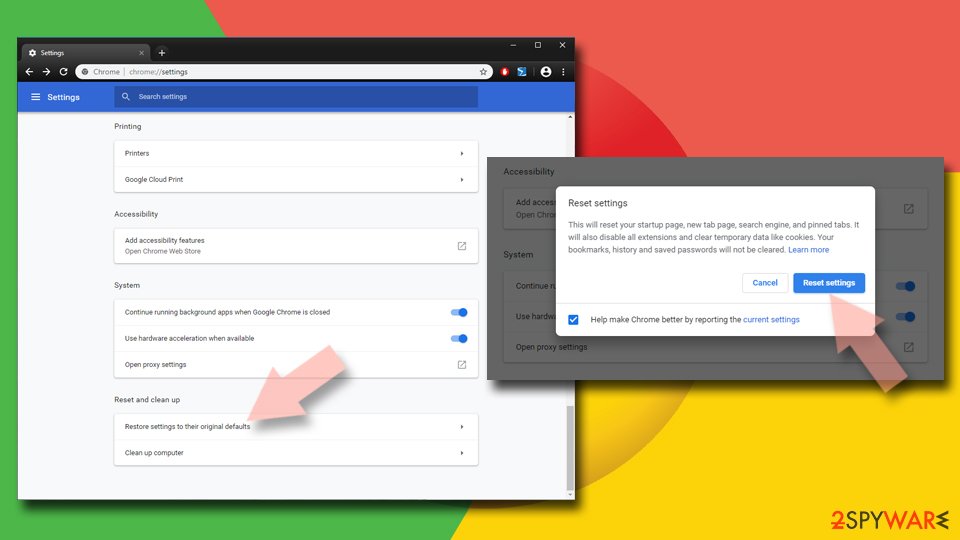
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Mozilla Firefox (FF)
To refresh Mozilla Firefox back to its previous state as it was before the adware attack, you should carry out these following steps
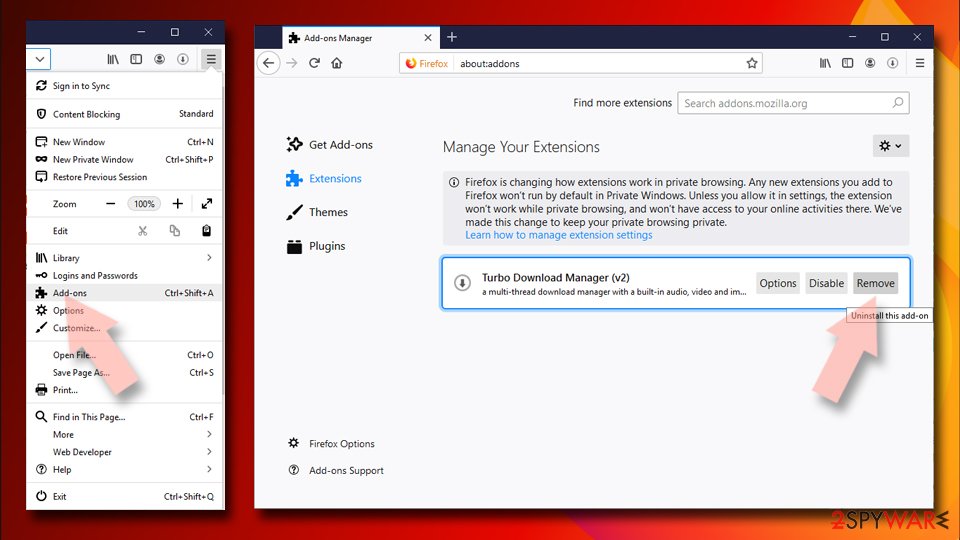
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
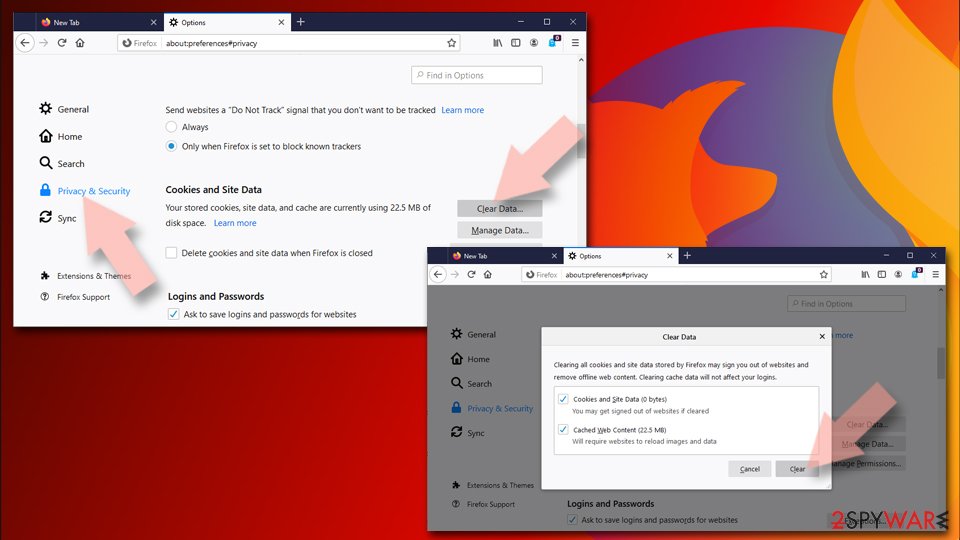
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
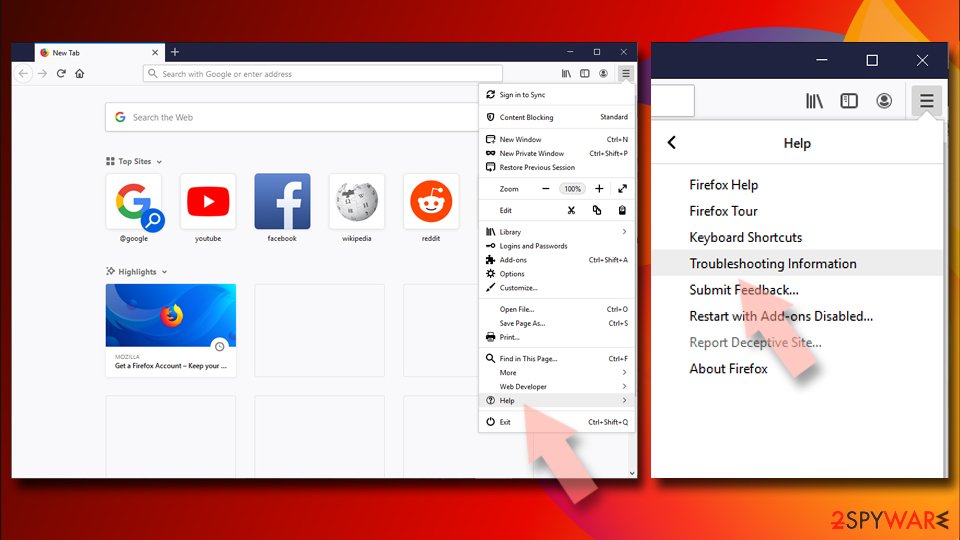
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
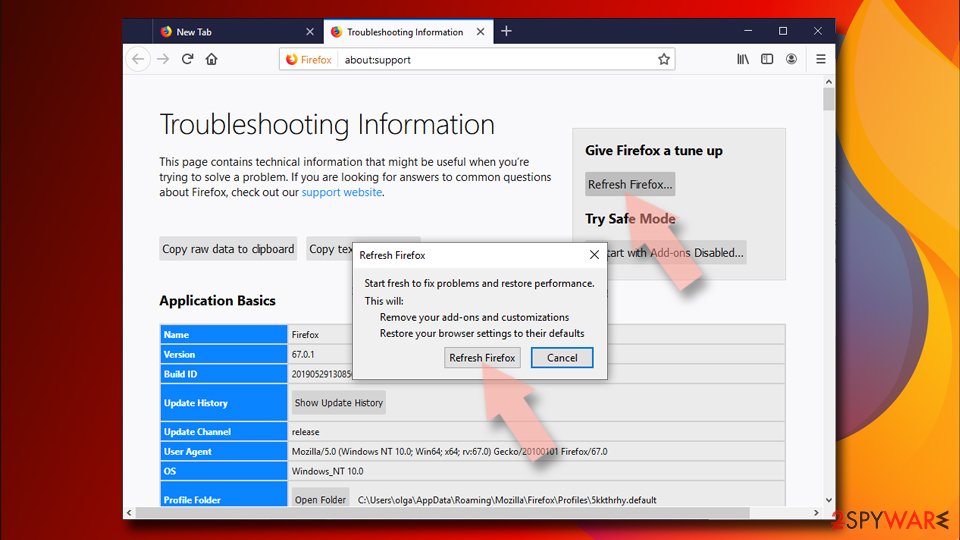
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
To delete questionable products and browser helper objects from the Safari web browser, you should go through these guidelines carefully
Remove dangerous extensions:
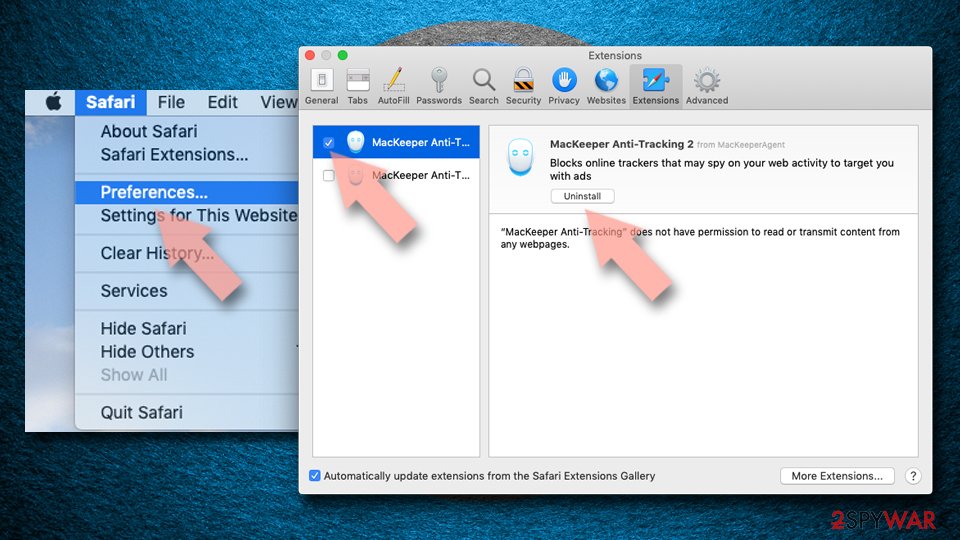
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
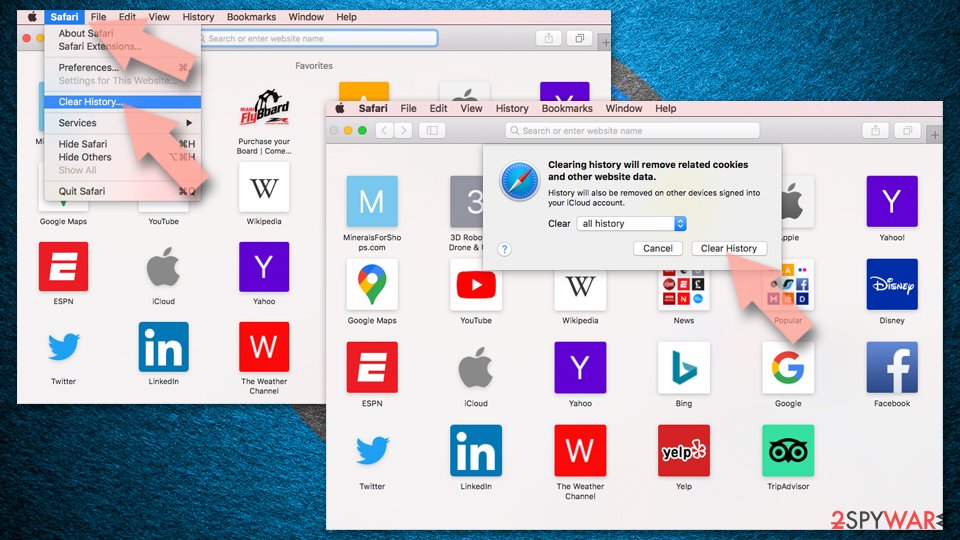
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
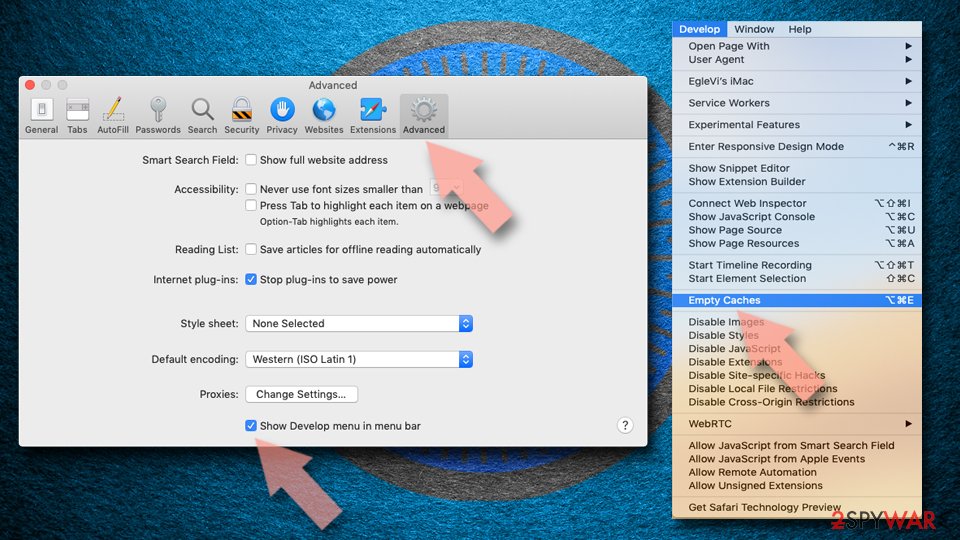
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
To clean your macOS computer from suspicious applications, files, and entries, you should complete the following guiding steps
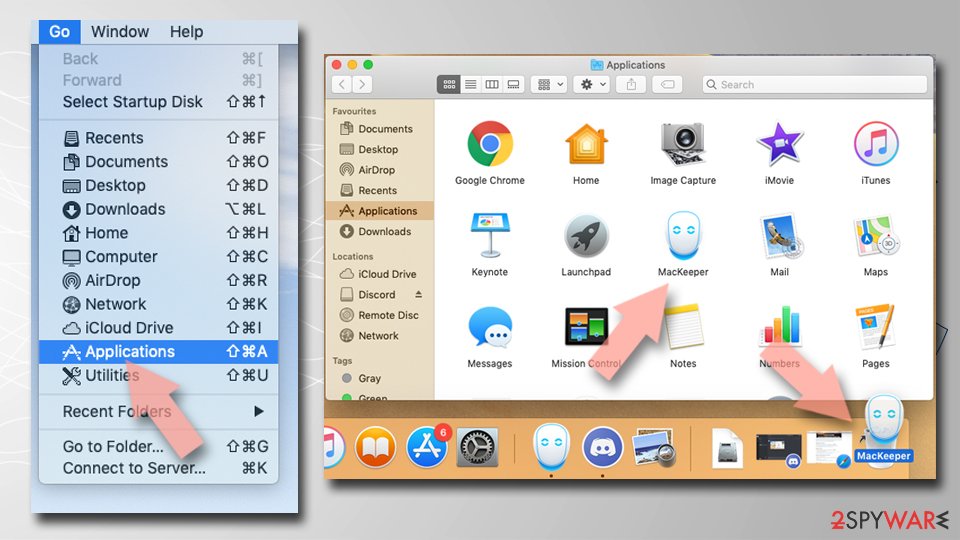
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
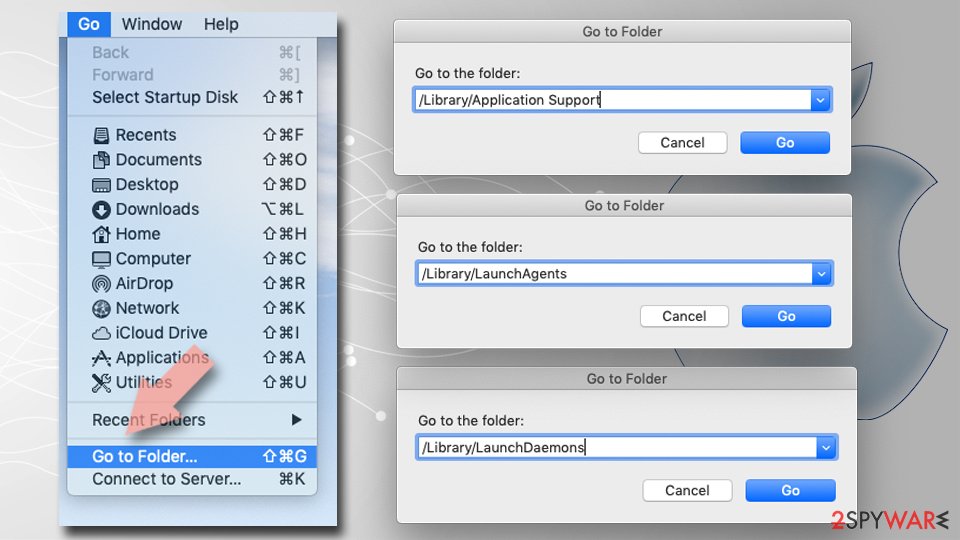
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of Oct 2019 · not reviewed since
Spreading locations of adware apps and how to avoid them
Specialists from LesVirus.fr claim that PUPs such as adware apps are distributed by using various techniques such as bundling, injecting the download of the suspicious program straight into a hyperlink or advertisement that often appear on unsecured networks such as gambling, gaming, and adult-themed pages.
However, we have good news for users that the secret installation of adware programs is easily avoidable if you just put a little bit of effort into it. Of course, automatical computer protection is necessary, so you should place a reliable antivirus tool on your computer. However, do not forget that manual actions are also required here. You can:
- Change the downloading mode into Custom/Advanced. If you have earlier picked the Quick/Recommended configuration, there should be no surprise that suspicious content has invaded your computer system.
- Avoid visiting unsecured online sources. If some type of website that you are tending to enter is marked as unsafe or you start receiving alerts from your antivirus tool, you should not proceed to it anymore.
- Avoid clicking on suspicious advertisements/hyperlinks. You should not click on every notification that appears on your screen while browsing the web as there might be infectious content delivered. However, if ads start bothering you frequently, consider getting AdBlock or Adblock Plus on your browser for further ad prevention.
From our report of Oct 2019 · not reviewed since
LookupShare virus can be eliminated manually or automatically
You can remove LookupShare from your macOS by putting some effort of your own or by employing reliable antimalware software to complete the process for you.
Which method works better for you and the computer is all up to you to decide. However, measure your skills and experience in the virus elimination field first.
If you think that you will be capable to deal with LookupShare removal on your own, go ahead and take a look at the below-provided elimination instructions. Here you will discover how to clean your macOS operating system and reverse browsers such as Google Chrome, Mozilla Firefox, and Safari back to their previous states.
Once LookupShare adware is gone, you should start taking your online and computing security more seriously in order to avoid repeated future incidents. Avoiding adware and similar threats is necessary for maintaining quality-full PC work.
Questions about LookupShare ads
Why does my browser keep going to lesvirus.fr?
Something is sending it there. On one site only, that site's ads are the cause and leaving the site ends it.
On many different sites, the usual causes are an extension you installed with something else, a site you once allowed to send notifications, or an ad-supported program in Windows that changes how the browser behaves. lesvirus.fr itself is only a stop on the way: it records the visit and forwards you to whatever advertiser pays most.
Check the extensions page, then the list of sites allowed to send notifications, then Installed apps sorted by date. Removing the cause stops the redirects; blocking the domain alone usually does not, because the network moves to a new one.
Should I worry about redirects to lesvirus.fr?
Worry less about lesvirus.fr itself and more about what keeps sending you there. A single redirect from a free streaming or download site is normal and harmless once the tab is closed.
Repeated redirects on sites that used to work fine mean something in the browser or in Windows changed, often an extension or program installed alongside other software. It may also collect the pages you visit. Remove the cause with the steps in this guide, and do not act on anything the redirected pages ask:
- no Allow clicks
- no downloads
- no calls
If you already did one of those, the matching section of this guide explains what to do next.
Why does LookupShare show me ads?
Because that is its whole purpose. LookupShare is an adware extension, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Do I have to clean every browser?
Yes, if you use more than one. We saw LookupShare in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from LookupShare?
Look for redirects to lesvirus.fr. That is the trace LookupShare leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
Can adware slow down my PC?
Yes. Adware runs in the background, loads ad scripts, opens extra tabs and contacts its servers, all of which use processor time, memory and bandwidth. Ad-heavy extensions also slow down every page, because they inspect and change it before you see it.
The effect is strongest on older PCs and when several adware programs arrived together. After removal, restart the PC and check Task Manager for anything still using a lot of resources that you do not recognise. Speed usually returns to normal once the ads stop.
Why didn't my antivirus catch LookupShare?
Many security products do not block adware or notification sites by default, because users often agreed to them, even through a misleading prompt. Notification spam installs nothing at all, so there is no file to detect.
In Windows 11 you can make Microsoft Defender block potentially unwanted apps: open Windows Security > App & browser control > Reputation-based protection settings and turn on Potentially unwanted app blocking. If notifications caused the pop-ups, no scanner will report them; the fix is in the browser's site settings.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
Will Fortect remove LookupShare?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For LookupShare, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Apple discussions: lookupshare app ?? Yahoo hijacks Safari (read October 6, 2026)
- LesVirus: LesVirus.fr (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)