
Perlintab.com ads: what it is and how to remove it
Perlin Tab functions as a fake search directory that allows you to customize the new tab and homepage with abstract animation. It also includes a local weather forecast feature to trick users into believing it is actually helpful.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Not sure what sends your browser to perlintab.com? An automatic scan looks at the usual sources for you.
Do it yourself · free Remove Perlintab.com ads yourself 3 steps, about 9 minutes, no software needed.
Start the steps
Perlintab.com ads: summary
| Damage | Non-identifiable information loss, privacy issues, malware infections |
|---|---|
| name | Perlintab.com |
| Type | Redirect virus, browser hijacker |
| Symptoms | Altered browser settings (homepage, default search engine, new tab); redirects to dubious websites |
| extension | Perling Tab |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Distribution | Not recorded in the old report |
|---|---|
| Name | Perlintab.com |
| Evidence | 4 write-ups by security sites; details still limited |
| Domains | perlintab.com |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 24 May 2021 |
| Facts checked | 6 October 2026 |
Is Perlintab.com ads dangerous?
From our report of May 2021 · not reviewed since
Perlintab.com claims to be a helpful search engine, but it's only a PUP
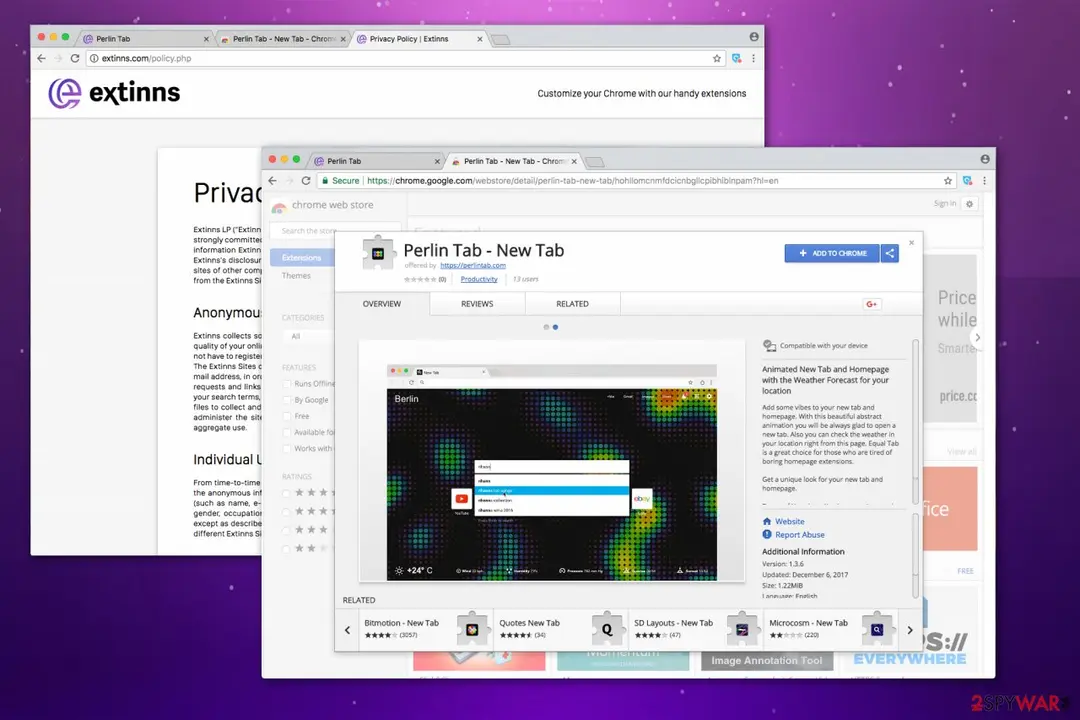
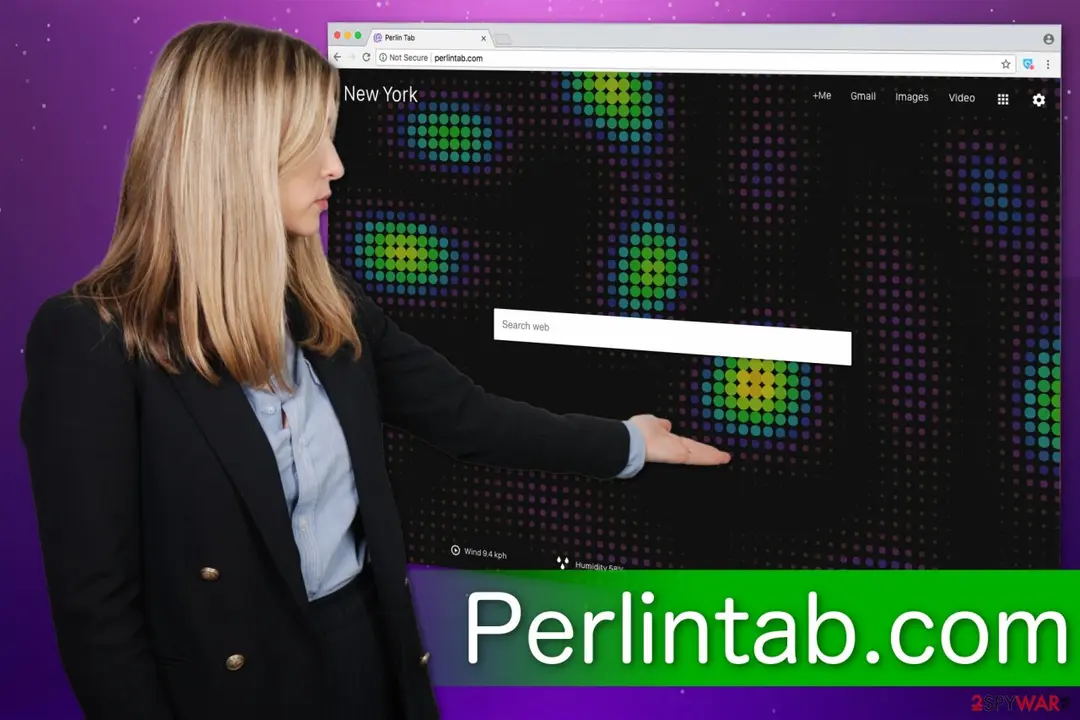
Perlin Tab functions as a fake search directory that allows you to customize the new tab and homepage with abstract animation.
It also includes a local weather forecast feature to trick users into believing it is actually helpful. In reality, this potentially unwanted program hijacks Google Chrome and promotes affiliate websites via intrusive ads.
While you can install this browser hijacker by downloading it from Chrome Web Store, it also spreads inside the packages of free applications. Once it is on the system, you might notice that you are continuously redirected to perlintab.com. We don't advise using this program.
Note that by searching through this unreliable program, you risk your privacy and computer's security. Perlintab.com and its other version, Equaltab.biz, can collect personally identifiable information by tricking you into submitting it via surveys and contests .
It might be dangerous since there are several cases where such actions led to identity theft. Thus, be safe and remove Perlintab.com while you didn't get hurt. Besides, this browser hijacker might prevent you from resetting its modifications. Likewise, we suggest using the elimination guide below.
Additionally, you should be aware that it uses the gathered personally non-identifiable information to deliver various advertisements that are linked to your recent browsing activities. While the extension might seem completely fine, those ads promote ineffective software, poor-quality products, or other useless goods.
Besides, the worst part of Perlin Tab redirect tendency is that some of the generated advertisements might be malicious – they can either lead to suspicious pages where malware is distributed or infiltrate the virus itself . You clicking on the ads is all it requires to sneak the high-risk computer infection on your system.
Therefore, we strongly recommend you to perform a removal while it didn't cause more damage to your computer. You can use or for the safest elimination procedure, which is also the fastest option for the regular PC user. However, you are welcome to employ another antivirus tool as long as it is reliable and expert-tested.
Keeping either of our recommended AV tools up to date would prevent malware and PUPs from infecting your devices. Virus damage is another thing that you'll have to deal with. To repair any system-related irregularities, we advise using the application.
From our report of May 2021 · not reviewed since
PUPs enter your system without asking for a permission
If you tend to rush through the software installation procedure and skip many steps, we have bad news for you.
According to the experts from NoVirus.uk , developers take advantage of such reckless actions and bundle potentially unwanted programs with freeware without disclosure in Quick or Recommended installer settings.
In other words, by choosing the latter ones, you cannot detect the additional programs that will be installed along with the regular application. This distribution technique is called product bundling and widely beloved by many browser hijacker developers. If you want to avoid PUPs, follow these steps when installing software:
- Do not download programs from unauthorized websites;
- Always pick only Advanced or Custom options;
- Uncheck pre-selected marks, which allow installing the PUP.
Check your browser and PC
- Address:
perlintab.com
How to remove Perlintab.com ads
How to stop the Perlintab.com redirects
Work in this order and test a few links after each step, so you know which one was the cause.
Step 1: Check the browser's extensions
Redirects to
perlintab.comon sites that normally behave mean something in the browser is sending you there. In Chrome openchrome://extensions, in Edge edge://extensions, in Firefox the menu > Extensions and themes.Remove every extension you do not remember adding, especially new tab, search, coupon, PDF or video downloader add-ons. The extension pages look the same on Windows 11 and Windows 10.
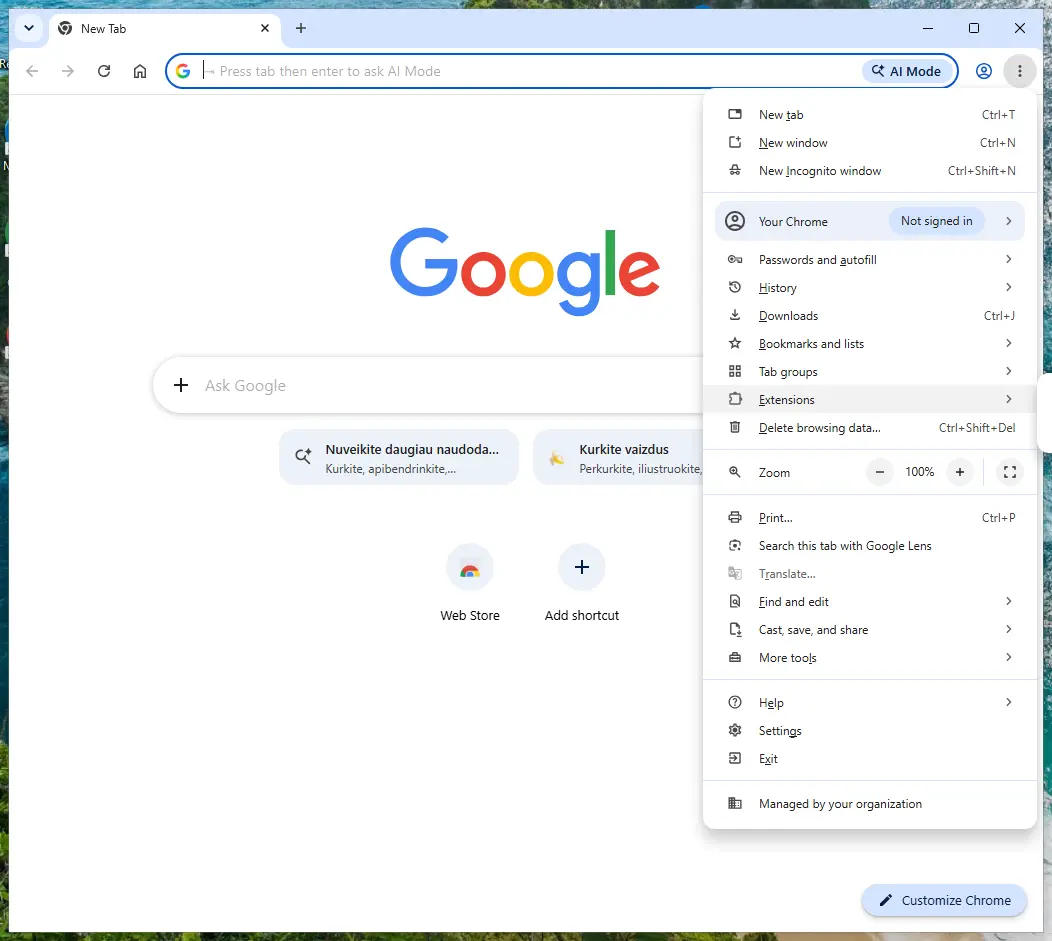
Chrome on Windows 11: More > Extensions > Manage extensions. Full procedure with screenshots: Remove a browser extension
Step 2: Reset the browser if the redirects continue
If
perlintab.comstill opens after the extensions are gone, put the browser's settings back to their defaults. In Chrome open Settings > Reset settings > Restore settings to their original defaults; in Edge Settings > Reset settings; in Firefox Help > More troubleshooting information > Refresh Firefox.Tip: Bookmarks and saved passwords stay, while site permissions, the start page and the search engine are reset.
Redirects that survive a reset in every browser point to a program installed in Windows 11 or Windows 10, so uninstall anything you do not recognise in Settings > Apps > Installed apps.
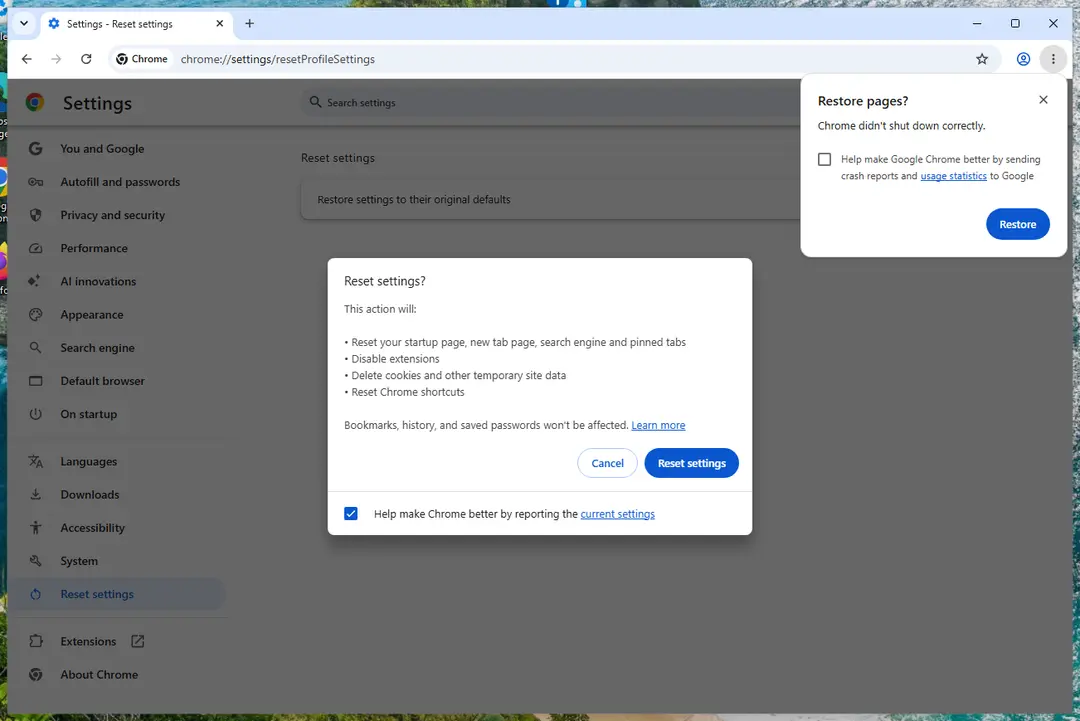
Chrome on Windows 11: Settings > Reset settings. Full procedure with screenshots: Reset a browser and fix a hijacked search engine
Step 3: Scan the PC if you downloaded anything from the ads
If you only saw the notifications and clicked nothing, you can stop before this step. If a notification led you to download or run something, delete that file, then scan Windows.
In Windows Security > Virus & threat protection > Scan options, run a Full scan, then choose Microsoft Defender Antivirus (offline scan) and Scan now. The offline scan restarts the PC and takes about 15 minutes on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Uninstall from Windows
You can clean your Windows system by uninstalling any unwanted apps like this:
Uninstall from Windows 10/8:
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
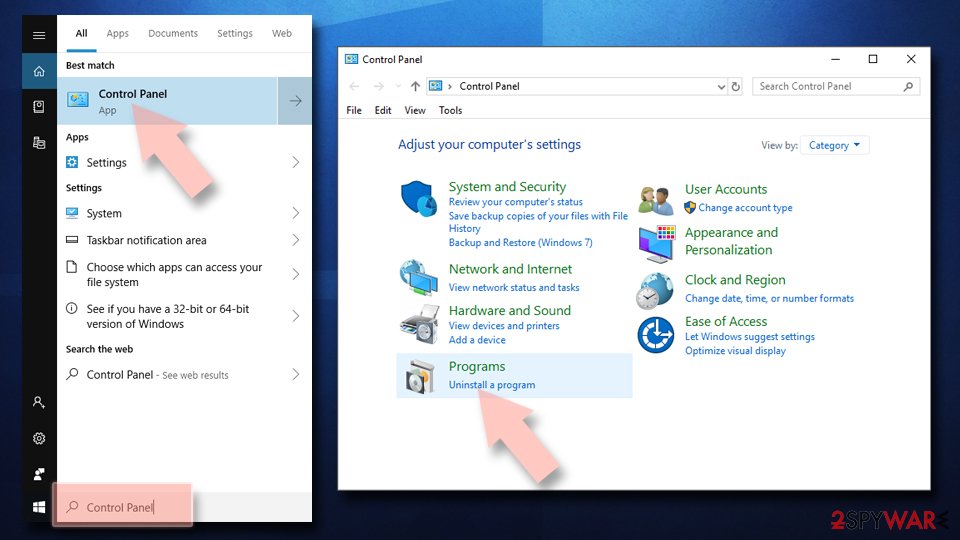
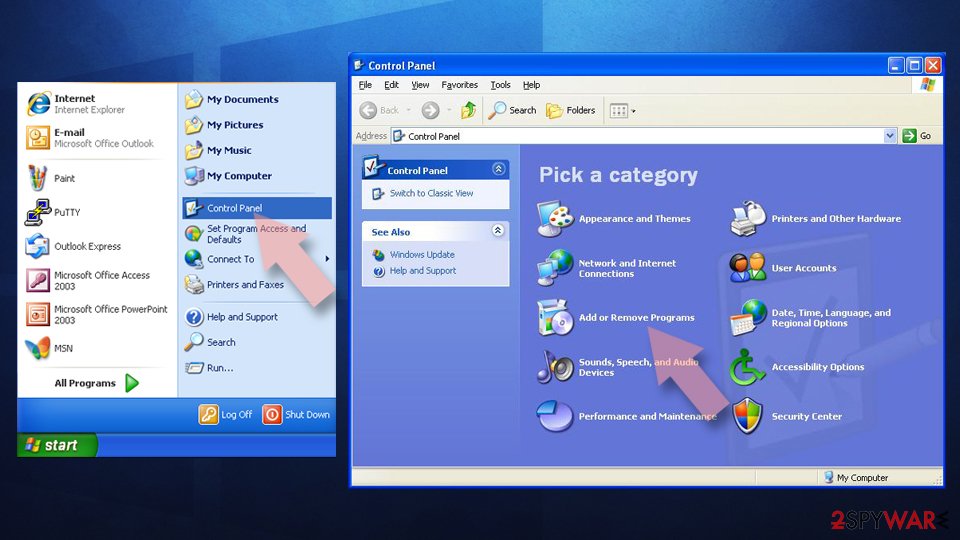
Uninstall from Windows 7/XP:
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
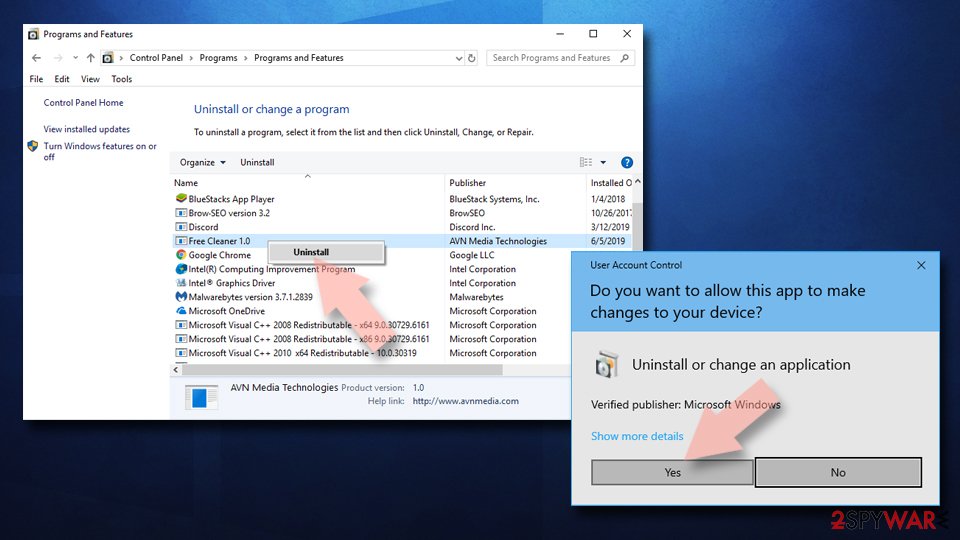
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Remove from Google Chrome
Instructions for resetting Chrome browser:
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
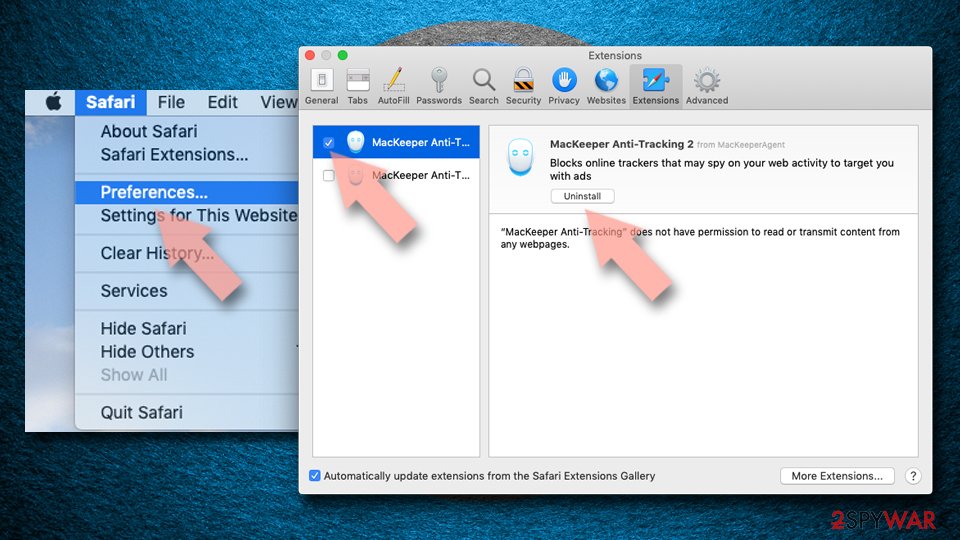
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
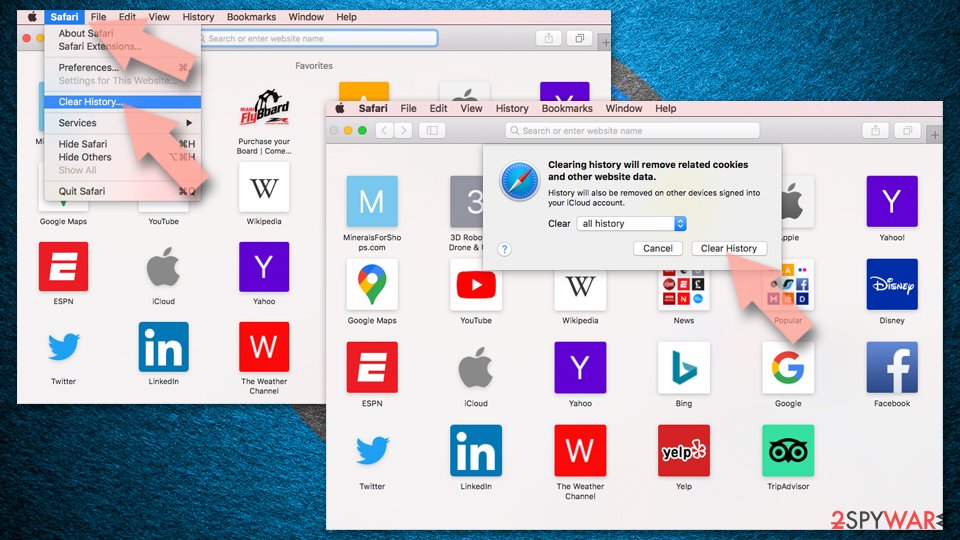
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
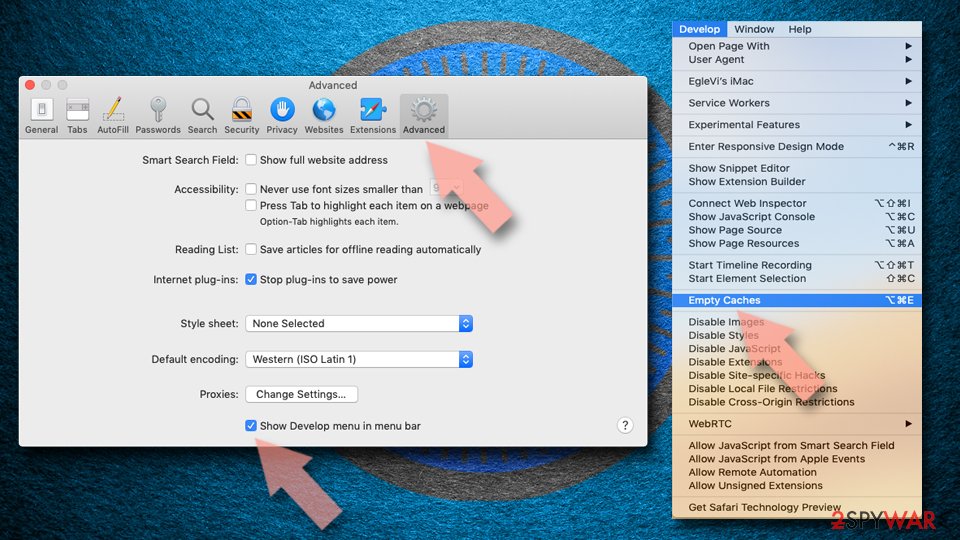
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
Guide to delete suspicious entries from Macs:
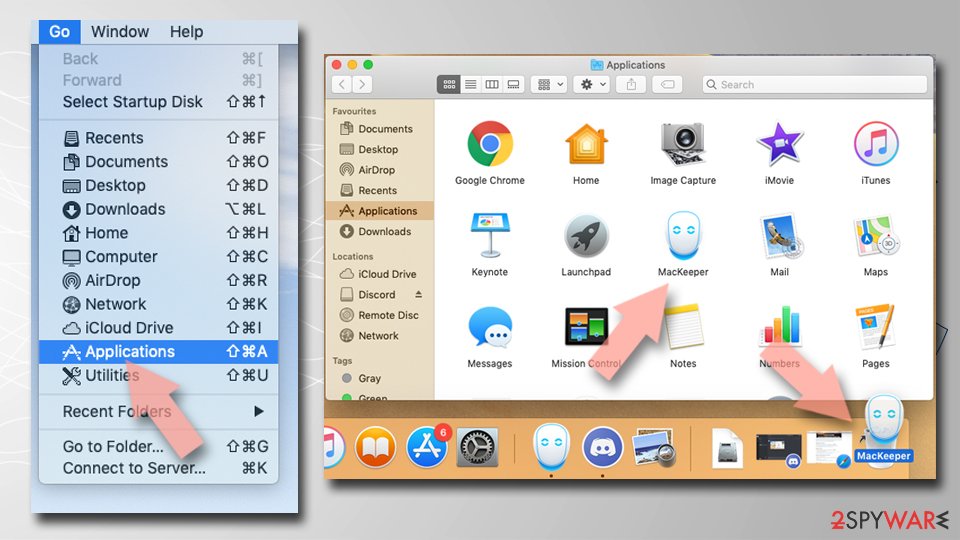
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
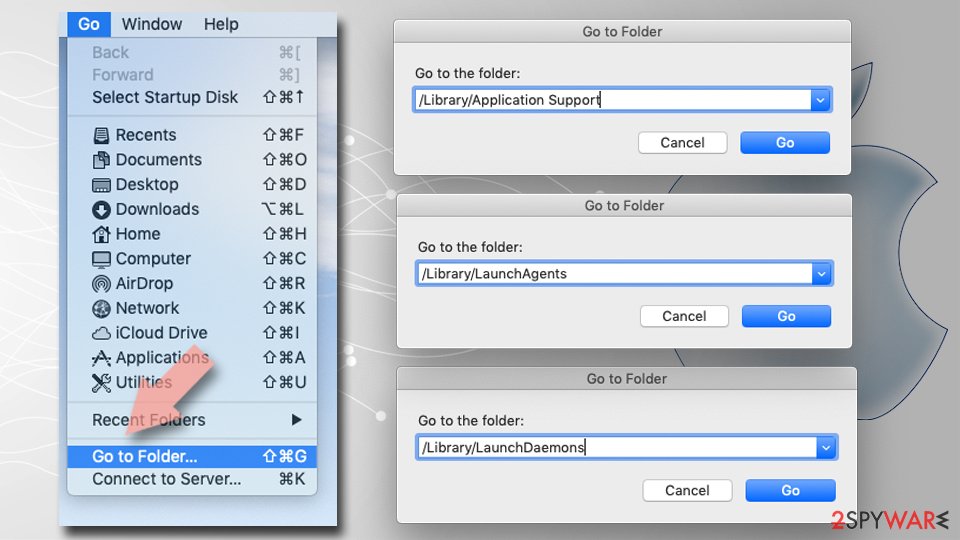
- Finally, empty the Trash to permanently remove the leftovers.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of May 2021 · not reviewed since
Perlintab.com virus removal can be easy
After that and resetting your browsers, you will be able to enjoy your browsing sessions once again.
However, if you are interested in manual removal, you can always use our guide below. It is designed to be easily understood. But be aware that you should not make any interpretations during the procedure and follow it strictly, or the browser hijacker could reappear with the next reboot.
Questions about Perlintab.com ads
perlintab.com opens when I click links. What causes it?
When every click leads to perlintab.com first, an extension or a script on the page is rewriting the links. If it happens only on one site, that site uses aggressive ads; close it and use another source. If it happens everywhere, open the browser in a private window, where extensions are normally off, and try again.
No redirect in the private window means one of your extensions is responsible: remove the ones you do not know. A redirect in the private window too means the cause is outside the extensions, such as a notification permission, a changed search setting or a program installed on the PC. The removal steps in this guide cover each of those.
Did perlintab.com install a virus on my PC?
Very unlikely, unless you downloaded and opened something from the pages it led to. Redirect domains such as perlintab.com sell your visit to advertisers; they do not need to install anything to make money.
What can be installed is the thing that causes the redirects in the first place, such as an extension or an ad-supported program that came with free software. That is why the checks in this guide look at extensions, notification permissions and Installed apps.
A full scan with Microsoft Defender afterwards gives you a clear answer about the rest of the PC. If the scan is clean and the redirects stop after removing the cause, you are done.
Why does Perlintab.com show me ads?
Because that is its whole purpose. Perlintab.com is an ad redirect domain, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Is perlintab.com safe to visit?
No. The site perlintab.com exists to push visitors towards ads, and the pages it leads to include fake virus warnings, fake updates, prize scams and notification prompts. Visiting it once does not infect an up-to-date PC, but anything you click or download there is a gamble.
Do not enter personal details, do not allow notifications and do not call phone numbers it shows. If it opens by itself, close the tab and check the browser's extensions and notification permissions. Blocking the single domain helps little, because the operators register new names regularly.
Do I have to clean every browser?
Yes, if you use more than one. We saw Perlintab.com in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from Perlintab.com?
Look for redirects to perlintab.com. That is the trace Perlintab.com leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
Does adware steal passwords?
Ordinary adware is built to show ads, not to steal logins, and most of it never touches saved passwords. The line is blurry, though. Extensions that can read every page could capture what you type, and adware ads sometimes lead to phishing pages that ask for passwords directly.
If you entered credentials on a page reached through an ad, change that password from a clean device and turn on two-step verification. Otherwise, removing ad redirect domain and clearing cookies is usually enough.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
Will Fortect remove Perlintab.com?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Perlintab.com, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Engadget: You say advertising, I say block that malware (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)