
Protectwatcher.xyz e-mail scam: how to spot it and what to do
Protectwatcher.xyz is a fraudulent website created by cybercriminals to display false information to visitors in order to get them to download potentially unwanted software. The primary objective here is monetization through various illicit means, including showing fake virus alerts so that users would purchase software licenses, making money from push notification spam, and redirecting users to other dangerous websites that could jeopardize their privacy and computer security.
Facts checked October 7, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Protectwatcher.xyz e-mail scam yourself 4 steps, about 12 minutes, no software needed.
Start the steps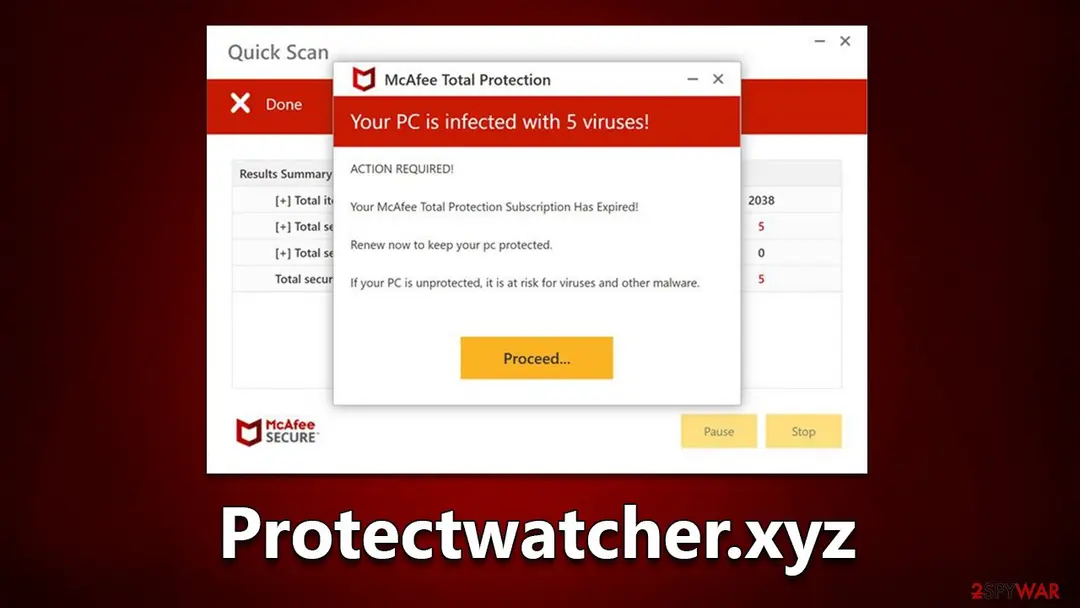
Protectwatcher.xyz e-mail scam: summary
| Distribution | Redirects from other malicious websites, adware |
|---|---|
| Damage | Loss of finances due to fake subscriptions; redirects to other malware-laden, scam websites; installation of potentially unwanted or malicious software |
| Name | Protectwatcher.xyz |
| Type | Scam, fraud, phishing, redirect |
| Operation | The scam is based on scaring users into believing that their systems are infected and that they need to remove the allegedly found malware with promoted software |
| Symptoms | A phishing e-mail asking you to sign in |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Evidence | 4 write-ups by security sites; details still limited |
|---|---|
| Arrives as | |
| Pretends to be | A well-known company |
| Claim | Your account needs urgent attention |
| Asks for | Your password |
| First seen | 10 November 2022 |
| Facts checked | 7 October 2026 |
What the Protectwatcher.xyz e-mail scam e-mail looks like
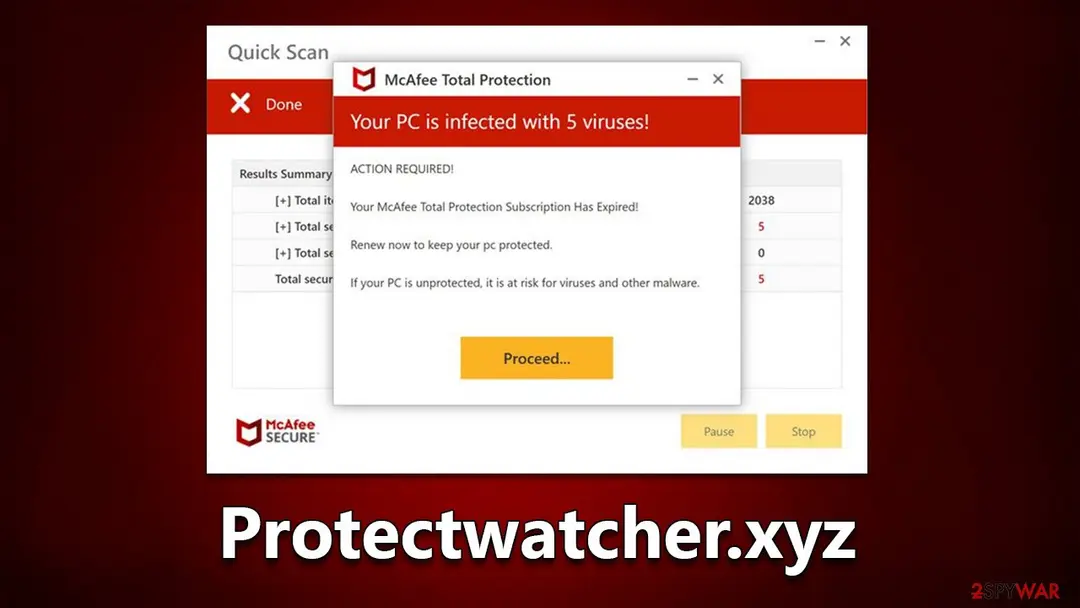
Your PC is infected with 5 viruses!
ACTION REQUIRED
Your McAfee Subscription Has Expired!
Renew now to keep your PC protected.
If your PC is unprotected, it is at risk for viruses and other malware.
How to tell the Protectwatcher.xyz e-mail scam e-mail is fake
From our report of Nov 2022 · not reviewed since
- In reality, McAfee did not initiate any scans on your system - it is the work of scammers.
- You should not interact with any links or ads shown on the scam page and shut it down immediately.
- Then, perform a full scan with security software as a precautionary measure
- Cleaning web browsers is one of the secondary things you should do after PUP/malware removal to secure your privacy.
Is Protectwatcher.xyz e-mail scam dangerous? What the senders want
From our report of Nov 2022 · not reviewed since
Protectwatcher.xyz is a fake website that tricks users into buying a subscription
Protectwatcher.xyz is a fraudulent website created by cybercriminals to display false information to visitors in order to get them to download potentially unwanted software.
The primary objective here is monetization through various illicit means, including showing fake virus alerts so that users would purchase software licenses, making money from push notification spam, and redirecting users to other dangerous websites that could jeopardize their privacy and computer security.
While Protectwatcher.xyz ads are not directly linked to some type of a virus infection, this possibility should not be excluded - adware is one of the most common potentially unwanted applications that could have been installed on your system unintentionally, so it's important to check it thoroughly.
From our report of Nov 2022 · not reviewed since
How scammers achieve their goals
Many cybercriminals use the element of surprise to commit online fraud, as it is very effective in eliciting an emotional response from victims.
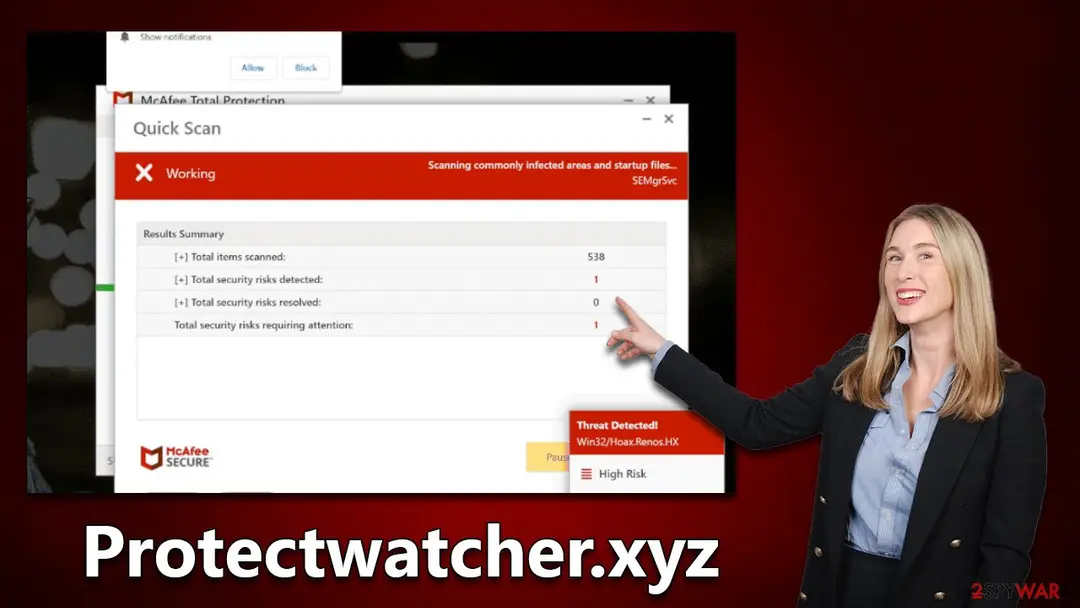
The goal is to scare users into making hasty decisions before they realize they are being scammed. Protectwatch.xyz uses this tactic by impersonating a system scan with several pop-up messages and what seems to be a progress bar. A short while later, users are presented with the following alarming results:
In fact, it is virtually impossible for any website to diagnose your computer regarding its security, as only robust anti-malware software installed on the device can do so. Websites can, however, record general information about any user, including their operating system, IP address, web browser and its version, and similar details, which are also often abused in phishing campaigns.
The fake results are shown to everybody who enters the scam page - they are simply a replica of the security vendor's anti-malware software. There are thousands of other websites that use reputable vendors' names in this scheme, and the fake scanning performed is identical to that of Protectwatcher.xyz (Alltimesecuritysystem.live, Haloweenpromob2.click, and Asxerk.click are just a few examples).
What to do after the Protectwatcher.xyz e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you typed a password on the page the Protectwatcher.xyz message opened, assume the sender has it. Go to the real site by typing its address yourself and change the password there, choosing one you have never used.
Change it anywhere else the same password was used, and sign out all other sessions if the service offers it. Any browser on Windows 11 or Windows 10 will do, as long as you do not follow the e-mail's link.
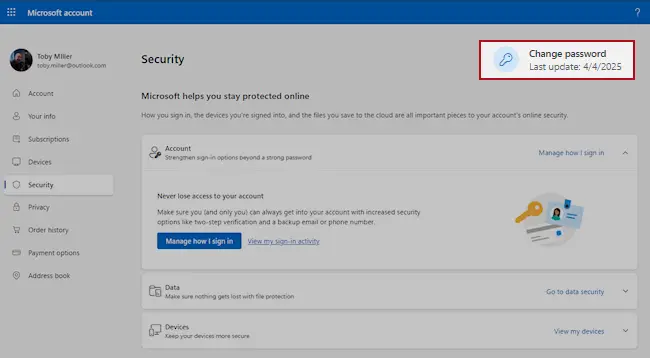
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
With two-step verification on, a stolen password alone no longer opens the account, because a sign-in from a new device also needs a code from your phone.
Switch it on for the e-mail account first, then for banking, shopping and social accounts that use that address.
Check the recovery phone, the recovery e-mail and any forwarding rules while you are in the settings, since attackers change them to come back. The pages are the same on Windows 11 and Windows 10.
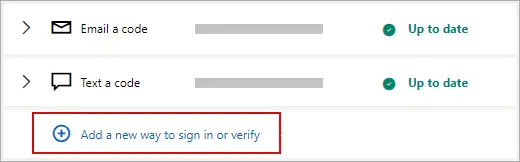
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Do not reply and do not click anything else in the message. In Outlook select the e-mail and choose Report > Report phishing; in Gmail open the three-dot menu next to Reply and pick Report phishing.
That trains the filter for everyone on the service, and the message goes to the junk folder. If the e-mail came to a work address, forward it to your IT team as an attachment first.
The steps are the same in the web mail and the mail apps on Windows 11 and Windows 10.
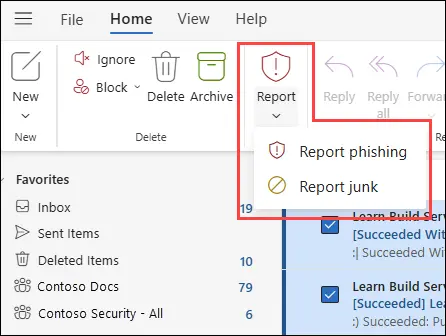
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A fake sign-in page only steals what you type, so most readers can skip this step. If the Protectwatcher.xyz e-mail made you download or open a file, delete it and scan the PC.
In Windows Security > Virus & threat protection > Scan options, run a Full scan and then Microsoft Defender Antivirus (offline scan) > Scan now. The offline scan restarts Windows 11 or Windows 10 and takes about 15 minutes.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of Nov 2022 · not reviewed since
What to do if you have enabled push notifications
First off, you should check whether you enabled push notifications from Protectwatcher.xyz, as it delivers the request as soon as one enters the website.
If you have clicked the "Allow" button either intentionally or not, you might start receiving suspicious pop-ups with various dubious content in them - you might be exposed to more fake virus infection alerts, bogus lottery winnings, get-rich-quick schemes, and similar.
Push notifications are not a direct result of virus infection and would show up as long as the website is permitted to do so. In other to stop the intrusive activity, you have to access browser settings and block the relevant URL as follows:
MS Edge (Chromium):
- Open the Google Chrome browser and go to Menu > Settings.
- Locate the Privacy and security section and pick Site Settings > Notifications.
- Look at the Allow section and look for a suspicious URL.
- Click the three vertical dots next to it and pick Block. This should remove unwanted notifications from Google Chrome.
- Open Mozilla Firefox and go to Menu > Options.
- Click on Privacy & Security section.
- Under Permissions, you should be able to see Notifications. Click the Settings button next to it.
- In the Settings – Notification Permissions window, click on the drop-down menu by the URL in question.
- Select Block and then click on Save Changes. This should remove unwanted notifications from Mozilla Firefox.
- Open Microsoft Edge, and go to Settings.
- Select Site permissions.
- Go to Notifications on the right.
- Under Allow, you will find the unwanted entry.
- Click on More actions and select Block.
- Click on Safari > Preferences...
- Go to the Websites tab and, under General, select Notifications.
- Select the web address in question, click the drop-down menu and select Deny.
From our report of Nov 2022 · not reviewed since
Removal of all unwanted and malicious software
Most people who land on a scam website have caused it themselves by clicking on a malicious link from another site.
It's recommended to stay away from places like gambling, X-rated, torrent, and similar sites that often host these links and scripts. Not only can these places redirect you to phishing websites, but you may also be tricked into executing a malicious EXE file on your system, resulting in ransomware or other malware infections, which can be devastating.
Browser redirects and an increased number of ads can also be caused by adware. So, if you're constantly being redirected to Protectwatcher.xyz or other strange websites, there's a decent chance that your device has some sort of unwanted software installed. A good place to start would be checking for programs on the system level:
Besides moving the unwanted app into Trash, removing adware might require a few more steps.
To fully remove an unwanted app, you need to access Application Support, LaunchAgents, and LaunchDaemons folders and delete relevant files:
Browser extensions are also known to cause unwanted redirects and ads, so make sure you check whether all your extensions are trustworthy - remove everything you don't recognize or find suspicious.
If you're unsure when apps should or shouldn't be present, you can rely on or to handle the adware removal process. This way, you won't have to worry about some of the components being left behind. We also recommend clearing browser caches to prevent data tracking with .
- Enter Control Panel into the Windows search box and hit Enter or click on the search result.
- Under Programs, select Uninstall a program.
- From the list, find the entry of the suspicious program.
- Right-click on the application and select Uninstall.
- If User Account Control shows up, click Yes.
- Wait till the uninstallation process is complete and click OK.
- From the menu bar, select Go > Applications.
- In the Applications folder, look for all related entries.
- Click on the app and drag it to Trash (or right-click and pick Move to Trash)
- Select Go > Go to Folder.
- Enter /Library/Application Support and click Go or press Enter.
- Look for any dubious entries in the Application Support folder and then delete them.
- Now enter /Library/LaunchAgents and /Library/LaunchDaemons folders the same way and terminate all the related .plist files.
Questions about Protectwatcher.xyz e-mail scam
Can reading "Your PC is infected with 5 viruses!" infect my computer?
Reading it cannot. An e-mail is text and pictures, and current versions of Outlook, Gmail and other web mail services do not run code from a message just because you opened it. What can cause harm is an action:
- signing in on the page the link opens
- opening an attachment
- enabling macros in a document
The message "Your PC is infected with 5 viruses!" was built to lead you to one of those steps. If you stopped at reading, delete it and use the report button so the provider can block the same wave for others. Nothing needs to be removed from Windows.
How fast do I need to react after signing in on the "Your PC is infected with 5 viruses!" page?
As fast as you can. Stolen passwords are often tried within minutes, and the first thing an attacker usually changes is the recovery e-mail or phone, which locks you out. Change the password from a clean device first, then sign out everywhere and review the recovery settings.
If you are already locked out, use the provider's account recovery form straight away and mention that the page behind "Your PC is infected with 5 viruses!" took your password. Warn your contacts, since a taken-over mailbox is often used to send the same phishing to them.
Could Protectwatcher.xyz be a genuine message?
We checked it, and it is not. A well-known company is only the costume. The message exists to get your password, and real companies handle that inside your account, after you sign in normally, not through links, attachments or phone numbers in a message you did not expect.
Scammers copy logos and footers perfectly, so the design proves nothing. The sender address, the link target and the request are the reliable signs, and all three point to a scam here. Delete it, and if you are worried, check your account directly.
Why does Protectwatcher.xyz say that your account needs urgent attention?
Because that story works. A problem that needs fixing, a deadline and a simple solution make people act before they check.
The claim that your account needs urgent attention is the same for everyone who received Protectwatcher.xyz; it was written once and sent in bulk. Nothing about your own situation triggered it.
If you are unsure, look at the real account or service the normal way, without using the message. The claim will not be there, which settles the question. Then report the message.
What does Protectwatcher.xyz want from me?
In the end, your password. Everything else in Protectwatcher.xyz, from the logo to the deadline, is there to get you to that point without stopping to think. Knowing the goal helps you judge your risk.
If you did not give it, you lost nothing and can delete the message. If you did, the steps in this guide are ordered by what you handed over:
- passwords first
- then card and bank details
- then documents and anything you installed
- ran
Act on the highest item on that list first.
How do I contact the real a well-known company?
Not through anything in Protectwatcher.xyz. Type the official website address into the browser yourself, use the app you already have, or use the phone number printed on your card, contract or a previous genuine invoice. Search results can be risky too, because scammers buy ads for support numbers.
Once you reach the real a well-known company, you can ask whether there is any problem with your account and report the scam message; many companies have a dedicated address for phishing reports on their security page.
How urgent is Protectwatcher.xyz?
Urgent enough to act today, not urgent enough to panic. The sign reported, an e-mail with the subject "Your PC is infected with 5 viruses!", means someone is using or testing your details. Changing the password and turning on two-step verification takes ten minutes and usually locks them out.
If a payment is involved, the sooner the bank knows, the better the chance of getting it back. Do not respond to calls or messages that arrive right after the incident, even if they claim to be from your bank: call the bank yourself.
I entered my password on the fake page. What should I do?
Change the password on the real site right away, through its own website or app, and sign out of all sessions.
If you use the same password anywhere else, change it there too. Turn on two-step verification with an authenticator app or a passkey. Check the account for changes:
- recovery e-mail
- phone number
- forwarding rules
- recently sent messages
If you can no longer sign in, use the provider's account recovery page. Tell your contacts if the account sent messages in your name.
What is the single best habit against scams like this?
Never act on a message through the message itself. If something claims to be from a well-known company and asks you to sign in, pay, call or open a file, close it and go to the service the way you always do:
- a bookmark
- the app
- the number on your card
Real problems will be visible there. This one habit defeats almost every phishing, invoice, delivery and account-suspension scam, regardless of how convincing the design is, because the scammers can copy the look but not the real account.
Will Fortect remove Protectwatcher.xyz?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Protectwatcher.xyz, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Imperva: Phishing attacks (read October 7, 2026)
- Wikipedia: Ransomware (read October 7, 2026)
- FTC: How to recognize and avoid phishing scams (read October 7, 2026)
- CISA: Recognize and report phishing (read October 7, 2026)
- Microsoft Support: Protect yourself from phishing (read October 7, 2026)