
Ursnif, Gozi, ISFB, Dreambot: what it is and how to remove it
Ursnif (also known as Gozi, ISFB, or Dreambot) is a virus that specializes in banking credentials and other information-stealing by using a variety of methods. Released in 2006, malware has seen a fair share of updates and is constantly returning with new campaigns that typically utilize malvertising (fake Adobe Flash updates) and malspam (Word or Excel documents embedded in phishing emails) for the propagation.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If svchost.exe returns after removal, a full scan can find the entry that brings it back.
Do it yourself · free Remove Ursnif, Gozi, ISFB, Dreambot yourself 3 steps, about 9 minutes, no software needed.
Start the steps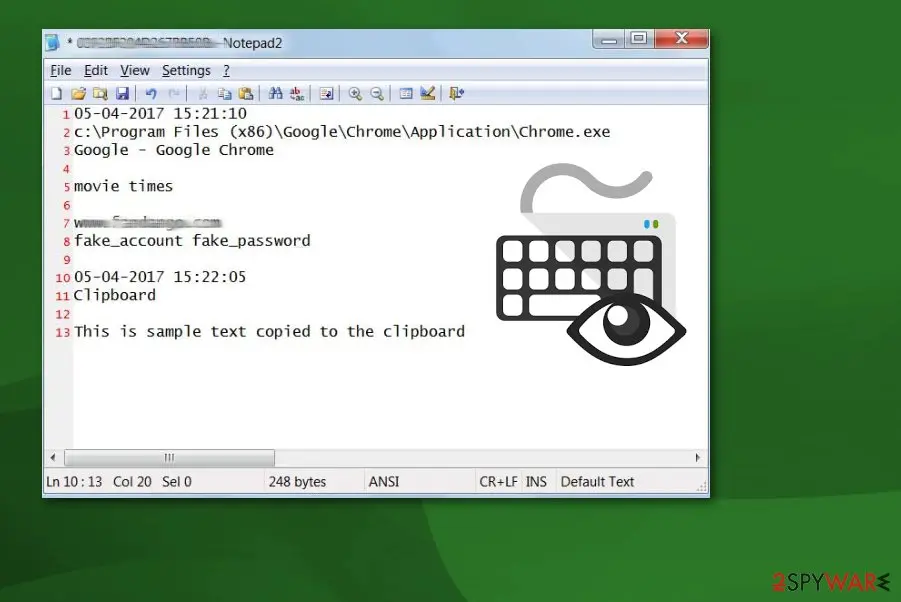
Ursnif, Gozi, ISFB, Dreambot: summary
| Distribution | The main distribution method is spam emails boobytrapped with malicious attachments. In most cases, MS Office documents are used, although other file types were also spotted in the wild |
|---|---|
| Name | Ursnif, Gozi, ISFB, Dreambot |
| Type | Trojan, Data-stealer |
| Associated process | Explorer.exe, iexplorer.exe, svhost.exe, click.exe |
| Symptoms | Information stealing malware rarely emits any symptoms, as it is designed to operate using stealth techniques. Nonetheless, some victims might notice suspicious computer behavior, such as inability to access particular sites via the web browser, system slowdowns, application/system crashes, errors, etc. |
| Danger level | High. Malware uses several evasion techniques, so it may remain on the system for months before it is detected, gathering sensitive information, such as financial details, account credentials, Social Security Numbers, and much more |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Evidence | 7 write-ups by security sites; details still limited |
| File name | svchost.exe |
| First seen | 21 May 2020 |
| Facts checked | 6 October 2026 |
What Ursnif, Gozi, ISFB, Dreambot does
From our report of May 2020 · not reviewed since
Trojan:W32/Ursnif virus termination is not easy, but achievable
When dealing with any silent intruder, anti-malware tools are the best option in virus elimination.
However, trojans are one of the most dangerous cyber infections that can additionally install malware on the system. To remove Ursnif virus and all related programs from the system, run a full system scan with updated anti-spyware.
If you are blocked, check two methods given below that are supposed to help you disable the virus before a scan. You can get rid of the Trojan:W32/Ursnif infection by relying on proper anti-malware tools that possibly find and delete this threat and any other threats related to issues with your machine.
Update these programs to their latest versions and run a full system scan to check your device thoroughly and get rid of any malware hiding on your system.
You can also use the anti-virus software of your choice, just make sure that it is a reputable and well-known tool. As for the Gozi virus damage, you need to think about PC repair or optimization tools like that can fix affected files and functions for you.
From our report of May 2020 · not reviewed since
More from our earlier report on Ursnif, Gozi, ISFB, Dreambot
- If your computer is connected to a network, disconnect it and then perform a full system scan with anti-malware software and remove the malicious virus
- In some cases, malware can infect and damage Windows system files.
- As a result, users might experience stability issues, such as lag, crashes, BSODs, and errors.
- <...>you may notice the C&C host list includes "microsoft.com", "update.microsoft.com", "avast.com", "cdevinoucathrine.info", "zcei60houston.club" and "kenovella.club".
- Why are the hosts of "microsoft" and "avast" listed here?
- In fact, this is a way to deceive researchers who capture and analyze the traffic.
What Ursnif, Gozi, ISFB, Dreambot collects and where it sends it
From our report of May 2020 · not reviewed since
This trojan is designed to record various sensitive information about the user, including banking data, logins or passwords, web browsing activity, information about the victim's OS and device.
All this recorded information is additionally shared with virus developers. Ursnif keylogger can also delete itself from the system once it receives such a command.
Gozi is constantly evolving, and several cybercriminal groups are working on its improvements. It started targeting various financial institutions from the beginning and recently expanded to more prominent organizations and changed distribution techniques and types of information to steal.
Trojan:W32/Ursnif is known to use different techniques as web injecting, man-in-the-browser, or keylogging functionality. The latest attacks were based on spear-phishing emails and the fact that malware deleted copies of itself after the initial process. These facts make this banking trojan more dangerous and difficult to detect or analyze.
Malware steals various data about the user personally, the device, and other account information like:
Ursnif virus changes various registry keys to keep affecting the system. People behind this threat are focusing on getting revenue from various background activities on your system or even stealing your banking credentials so get your money directly out of your bank accounts.
While there is no way to spot the infiltration of this trojan, you should note that the main way used by this malware to get into the system is spam. Gozi has been using intelligent tactics that rely on infected Word documents that are filled with malicious macros.
If you have recently been asked to enable macros to check the content of the email's attachment, we highly recommend making sure that you are not infected and that there is nothing related to Trojan:W32/Ursnif/ Gozi virus. The easiest way to do that is to scan the system with updated anti-spyware.
If you have any doubts either you have this malware on the device or not, check your system with updated anti-spyware, and perform the virus removal to save your personal information. To get rid of any viruses, use reputable anti-malware/anti-virus software.
We do not recommend performing the Trojan:W32/Ursnif removal manually as this is a dangerous cyber threat that can be related to numerous different components hidden on your computer. If you are blocked, reboot your PC to Safe Mode with networking first to disable the virus.
In most of cases, antivirus programs detect the Gozi Trojan horse as:
Virus activity may lead you to serious privacy issues or money loss, so you need to remove Ursnif virus as soon as possible. This type of cyber intruder can download and install other malware, including ransomware-type viruses, which could lead you to data loss.
There is no need to keep yourself at such a risk. However, we should say one more time that you shouldn't try to delete the trojan manually as you can lead your system to serious trouble by removing needed system components.
- information from your email accounts;
- various information from your browsers;
- logins and passwords of your social media accounts;
- banking website logins and passwords.
- TR/Crypt.XPACK.Gen
- Trojan:W32/Ursnif
- Virus/Win32.PolyRansom.c
- HEUR/Fakon.mwf
- Win32.Doboc.Gen.1
- Troj.Heur.LP.mE18
- etc.
How Ursnif, Gozi, ISFB, Dreambot got on your PC
From our report of May 2020 · not reviewed since
Ursnif is the info-stealing threat distributed in various online scam campaigns
Ursnif (also known as Gozi, ISFB, or Dreambot) is a virus that specializes in banking credentials and other information-stealing by using a variety of methods.
Released in 2006, malware has seen a fair share of updates and is constantly returning with new campaigns that typically utilize malvertising (fake Adobe Flash updates) and malspam (Word or Excel documents embedded in phishing emails) for the propagation.
Once inside the system, the Ursnif virus launches the malicious svchost.exe and explorer.exe processes, which are used to hide its presence on the host machine. Additionally, this modular malware starts numerous activities behind victims' backs, including the distribution of other malware.
However, the main Gozi virus activity is related to data tracking - it employs keylogging and other techniques in order to harvest information from browsers, email accounts, user configurations, as well as digital wallets. Ursnif later sends these details to the Command & Control that is accessible to the attackers only.
The threat is known for spreading during scam campaigns and using other techniques. The more recent fake keyboard verification scam - "B, S, Tab, A, F, Enter" CAPTCHA, during which the payload gets loaded without users' knowledge due to the keyboard inputs that people get tricked into doing themselves.
In 2015, the source-code of Trojan:W32/Ursnif was leaked online and placed on the GitHub platform, which allowed several cybercriminal groups to modify malware in a way that would increase its capabilities. As a result, the Trojan is now widely used and is highly evasive, making it a prevalent choice within the illegal data-stealing business.
In one of the latest Gozi campaigns, threat actors were spotted delivering the payload within MS Word documents, titled as "info_ .doc," that are embedded with malicious macros. As soon as users press "Enable Content," a Visual Basic code is executed, beginning the infection routine.
This variant of Ursnif was also using anti-detection techniques by injecting its Command & Control servers with a reference list of trusted companies, such as Microsoft:
In January 2020, security researchers from FireEye have discovered a variant of Ursnif, which was dubbed SaiGon. While this version still focuses on data stealing, its capabilities include backdoor functionality (which allows it to push other malware), process injection, and various evasion techniques.
From our report of May 2020 · not reviewed since
Spam email and online scam campaigns spread the trojan accross devices
Researchers have always been warning people that they shouldn't believe anything on the internet that looks too good to be true.
That includes banner ads, in-text links, and spam emails as well.
Spam has also been a commonly used technique for trojan distribution. However, when discussing a trojan horse, note that it relies on a slightly different distribution method. The main way used by its developers to deliver this malicious threat relies on Word documents filled with malicious macros. Once downloaded, such an attachment asks you to enable macros and launches the virus in this way.
Other unique features about the distribution technique used by this banking trojan:
You can avoid getting these intruders if you delete spam emails that are not from companies you know or services you do not use. Make sure to clean those suspicious emails from the email box more frequently and try to scan files before downloading them on the device. Pay more attention to these processes and do not open an email if you were not expecting that.
- Compromised email accounts are used to reply to emails. The content of an email looks convincing;
- The malicious payload is released when the user downloads the macro-filled documents. However, the Trojan waits until the attachment is closed to launch the process;
- The safe-looking Word attachment also executes the PowerShell code. After this process, malware connects to URL and delivers the payload directly on the system;
- The whole campaign is based on the fact that emails are sent from familiar services what increases the chances of people opening the infected file;
- The most common pattern used to name these files is "the name of a local business or service_Statement"
How to check the PC for Ursnif, Gozi, ISFB, Dreambot
- File:
svchost.exe
How to remove Ursnif, Gozi, ISFB, Dreambot
A stealer usually takes what it wants within minutes and may already be gone.
The scan comes first, then the accounts.
Step 1: Scan the PC, then run the offline scan
A scan finds the parts of Ursnif, Gozi, ISFB, Dreambot that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 2: Change passwords from another device and sign out other sessions
Ursnif, Gozi, ISFB, Dreambot can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after Ursnif, Gozi, ISFB, Dreambot, its publisher or created on the day the problem started.Delete those folders, and check
C:\Program FilesandC:\Program Files (x86)too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Protect your privacy - employ a VPN
There are several ways how to make your online time more private - you can access an incognito tab.
However, there is no secret that even in this mode, you are tracked for advertising purposes. There is a way to add an extra layer of protection and create a completely anonymous web browsing practice with the help of VPN. This software reroutes traffic through different servers, thus leaving your IP address and geolocation in disguise.
Besides, it is based on a strict no-log policy, meaning that no data will be recorded, leaked, and available for both first and third parties. The combination of a secure web browser and VPN will let you browse the Internet without a feeling of being spied or targeted by criminals.
No backups? No problem. Use a data recovery tool
If you wonder how data loss can occur, you should not look any further for answers - human errors, malware attacks, hardware failures, power cuts, natural disasters, or even simple negligence.
In some cases, lost files are extremely important, and many straight out panic when such an unfortunate course of events happen. Due to this, you should always ensure that you prepare proper data backups on a regular basis.
If you were caught by surprise and did not have any backups to restore your files from, not everything is lost. is one of the leading file recovery solutions you can find on the market - it is likely to restore even lost emails or data located on an external device.
Questions about Ursnif, Gozi, ISFB, Dreambot
What is svchost.exe and why is it running?
Every process is started by something:
- a program you installed
- a Windows service
- a scheduled task
- a startup entry
To learn why svchost.exe runs, find its file with Open file location in Task Manager, then look for an entry pointing to that file in Settings > Apps > Startup and in Task Scheduler.
Sort Installed apps by date to see what arrived when the process first appeared. Once you know the owner, you can decide whether to keep it, switch it off at startup or uninstall it completely.
Can I end svchost.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending svchost.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
I deleted svchost.exe. Am I safe now?
Your PC may be, but your accounts are not yet. Deleting svchost.exe stops Ursnif, Gozi, ISFB, Dreambot from running again, if nothing else on the PC restarts it, yet it does nothing about data that was already collected and sent.
Run the offline scan to make sure no other component or second payload remains. Then change passwords from a clean device, sign out of all sessions, move crypto and turn on two-step verification. Those steps, not the deletion, are what protect you from the stolen data.
Is Ursnif, Gozi, ISFB, Dreambot a known stealer?
Not as a named family yet. The sign, an unfamiliar process called svchost.exe in Task Manager, is typical of information stealers, keyloggers or clippers, but no analysis links Ursnif, Gozi, ISFB, Dreambot to a specific one. That is common:
- victims notice the effects
- such as lost accounts or swapped addresses
- before anyone sees the file
You do not need the family name to act. Change passwords from a clean device, sign out of all sessions, move crypto to a new wallet and run a Microsoft Defender offline scan on the PC. If a scan gives a detection name, note it for the report.
Is Ursnif, Gozi, ISFB, Dreambot still on my computer?
Possibly, possibly not. Some stealers stay and keep collecting; others delete themselves after one run. The sign you saw, an unfamiliar process called svchost.exe in Task Manager, only shows that data was used, not where the program is now.
A Microsoft Defender offline scan answers the first question; checking Startup apps, Task Scheduler and the Downloads folder for files from the days before helps too. Either way, the account steps are needed, because stolen passwords and cookies keep working after the program is gone, sometimes for weeks.
Should I report Ursnif, Gozi, ISFB, Dreambot to the police?
Yes, if money was lost or accounts were misused. A police report gives you a reference number that banks, exchanges and insurers often ask for. Include when you first saw an unfamiliar process called svchost.exe in Task Manager, the accounts and amounts involved, any wallet addresses or messages, and what you downloaded before it started.
In the US, use the FBI's IC3; in the UK, Report Fraud; in other countries, the national police cybercrime unit. Reporting rarely brings money back quickly, but it helps link cases and is often required for refunds.
Can I change my passwords on the infected PC?
Not while the spyware may still be running. A keylogger or stealer would capture the new passwords too. Use a phone or another computer that was never infected, or wait until the Microsoft Defender offline scan on this PC comes back clean.
Start with your main e-mail account, because it can reset every other password, then banking and payment accounts. When you return to this PC, sign in to the browser again only after the scans are clean and you have ended old sessions.
Who should I tell about Ursnif, Gozi, ISFB, Dreambot?
Start with the companies that can act quickly:
- your bank
- card issuer and payment services if money is involved
- crypto exchanges if coins were moved
- the providers of any account that was taken over
Each has a fraud or account-recovery process. Then file a police or national cybercrime report if you lost money or your identity was misused. If the PC is used for work, tell your employer's IT team, because work accounts and data may be affected as well.
Nothing has happened yet. Do I still need to change passwords?
Yes. Stolen logs are often sorted and sold before anyone uses them, so the quiet period can last weeks.
The criminals look for the most valuable accounts first, usually crypto, banking and e-mail, and may only reach yours later. Changing passwords and ending sessions now makes the copy worthless whenever it is used.
It takes an evening. Start with e-mail, then money, then everything else saved in the browser, and turn on two-step verification as you go. Watch for login alerts over the following months.
Will Fortect remove Ursnif, Gozi, ISFB, Dreambot?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Ursnif, Gozi, ISFB, Dreambot, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Biztech: Trojan malware on the rise in the banking sector (read October 6, 2026)
- Wikipedia: TOR (read October 6, 2026)
- Fortinet: New Ursnif Variant Spreading by Word Document (read October 6, 2026)
- FireEye: SAIGON, the Mysterious Ursnif Fork (read October 6, 2026)
- Virustotal: Trojan analysis (read October 6, 2026)
- Semvirus: Semvirus (read October 6, 2026)