
VBS:Malware: what it is and how to remove it
VBS:Malware-gen is a generic trojan detection name covering various malicious programs that steal data and compromise system security. These trojans enter silently through exploits, weak passwords, and phishing emails, making antivirus protection essential.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like VBS:Malware usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove VBS:Malware yourself 5 steps, about 15 minutes, no software needed.
Start the steps
VBS:Malware: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Name | VBS:Malware |
| Type | Loader |
| Symptoms | An unknown program in Installed apps |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 3 more facts
| Evidence | 5 write-ups by security sites; details still limited |
|---|---|
| First seen | 2 January 2021 |
| Facts checked | 5 October 2026 |
What VBS:Malware does on an infected PC
From our report of Jan 2021 · not reviewed since
VBS:Malware-gen is a virus that is capable of modifying targeted system settings for malicious purposes
VBS:Malware-gen is a generic name used for various trojan horses.
The threat can range from harmless ads display to straight out data-stealing, remote computer access, and other malicious activities. Additionally, malware can serve as a backdoor to other malware, such as self-propagating worms.
VBS:Malware-gen trojan usually enters computers without users noticing, and hackers use such distribution techniques as exploit kits, weak passwords, open RDP, spam emails, and other tricks, often including social engineering techniques. While most detections like idp.generic or idp.alexa.51 are legit, users have reported that certain anti-virus tools detected regular system files as false positive.
Since VBS:Malware-gen represents a variety of different computer viruses, it is hard to speak about its traits. Nevertheless, we will try to describe the typical behavior of a trojan horse, which would help you detect and remove VBS:Malware-gen from your machine.
Once VBS:Malware-gen enters the targeted computer, it performs a series of changes, which can range from:
Malware performs these changes to accomplish the goal it is set to do:
- steal data
- turn the computer into a spam machine
- redirect to sponsored websites
- similar
Crooks behind malware always seek for personal gain, and they do not care what the user have to through. VBS:Malware-gen can result in permanent data loss if it lets in ransomware virus in.
Additionally, stolen personal information such as banking details and other credentials can be sold in the black market for profit. It goes without saying that the presence of VBS:Malware-gen can significantly compromise your online safety, as well as computer security.
Unfortunately, trojan horses rarely produce any symptoms. This complicates VBS:Malware-gen removal procedure, especially for those who do not use comprehensive security software. Thus, experts highly recommend downloading and installing anti-malware software, such as or , which would prevent most of the malicious applications from entering the PC.
As we already mentioned, security software forums are filled with reports of AV engines recognizing several legitimate processes as VBS:Malware-gen. In such a case, it is a false positive and should be ignored. If users proceed with certain file removal, they can damage the system or prevent it from functioning correctly.
- Changes to browser settings
- Scheduling of new tasks
- Shutting down and spawning Windows processes
- Modifying Windows Registry
- Installing additional applications without consent, etc.
From our report of Jan 2021 · not reviewed since
Trojans should be avoided at all costs
While no method would protect your machine from infection completely, there are several things you can do to improve its security and reduce the chance of virus infiltration.
If you think that you are immune to infections, you are wrong, and even those who never been affected by malware usually face their first time at some point.
Thus, we suggest you follow these security tips:
- Pay attention to spam emails. Phishing emails are a well-known technique used by cybercriminals to install malware. Therefore, do not open attachments or click on hyperlinks embedded inside the email from an unknown source. Scan the URL or the file with tools like Virus Total before opening;
- Use secure passwords. Predictable passwords are one of the main reasons for malware infiltration. For example, Remote Desktop Protocol should be not only protected by a strong password, but should only be used with a VPN on;
- Update installed programs on time. Software vulnerabilities are discovered frequently and patched very soon after that. It is essential patching software immediately, as JavaScript can inject malware without you noticing;
- Beware of unsafe websites. Hackers often host malware on compromised sites. Additionally, they can create their own ones, which usually share files like cracks, keygens, and other illegal software.
From our report of Jan 2021 · not reviewed since
More from our earlier report on VBS:Malware
- Unsafe websites, unprotected RDP, exploits, spam emails, etc.
- Use reputable security software like to get rid of threats.
- will be helpful in case you notice some virus leftovers, that are disturbing your work.
How to remove VBS:Malware
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Programs like VBS:Malware add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 2: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
Uninstalling often leaves the program's folders, and some threats reinstall themselves from them.
Press Windows + R, type
%LocalAppData%and press Enter, then do the same for%AppData%and %ProgramData%, and look for folders named after VBS:Malware, its publisher or created on the day the problem started. Delete those folders, and check C:\Program Files and C:\Program Files (x86) too.If Windows says a file is in use, end it in Task Manager or delete the folder after a restart in Safe Mode. The folders are the same in Windows 11 and Windows 10.
Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of VBS:Malware that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
VBS:Malware can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
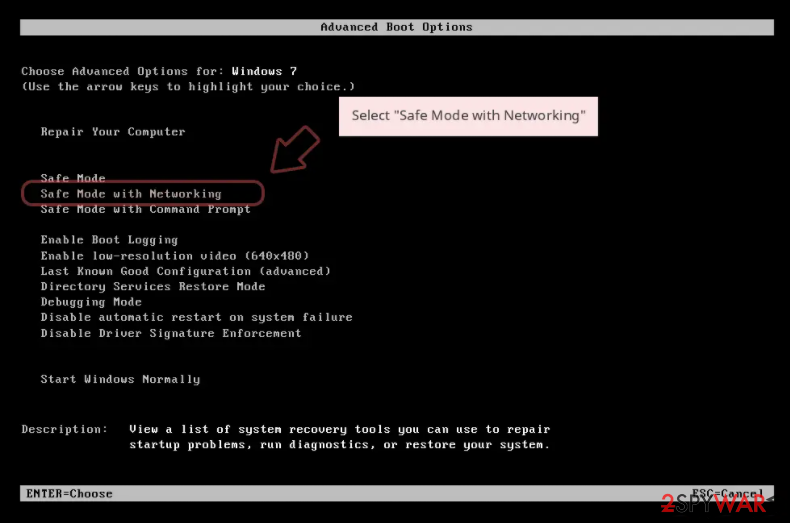
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
Windows 10 / Windows 8
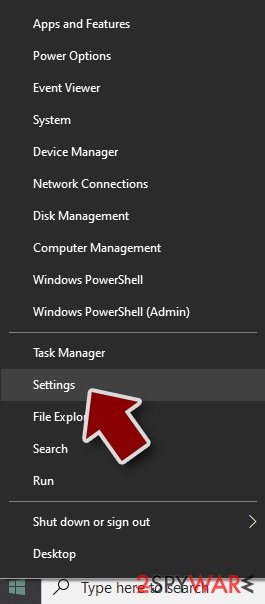
- Right-click on Start button and select Settings.
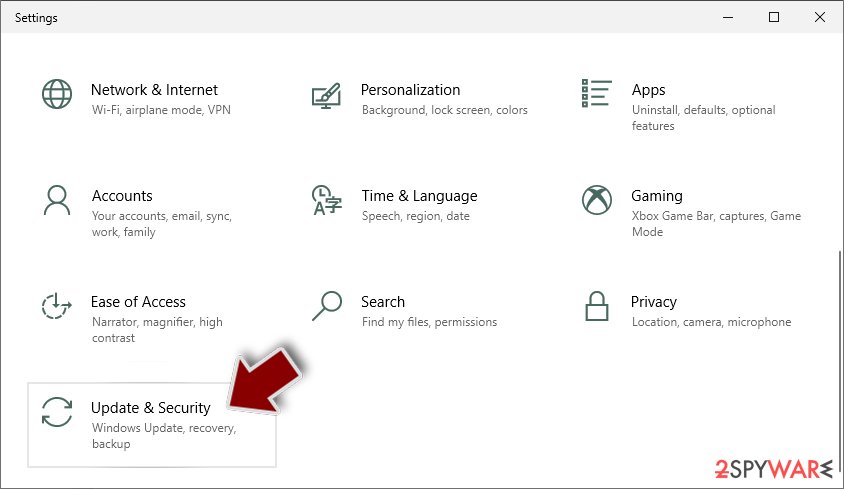
- Scroll down to pick Update & Security.
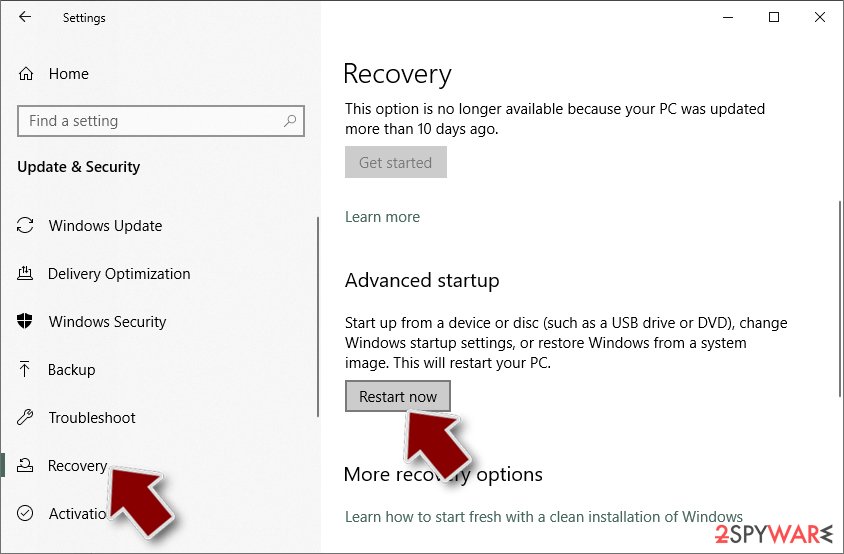
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
- Select Troubleshoot.
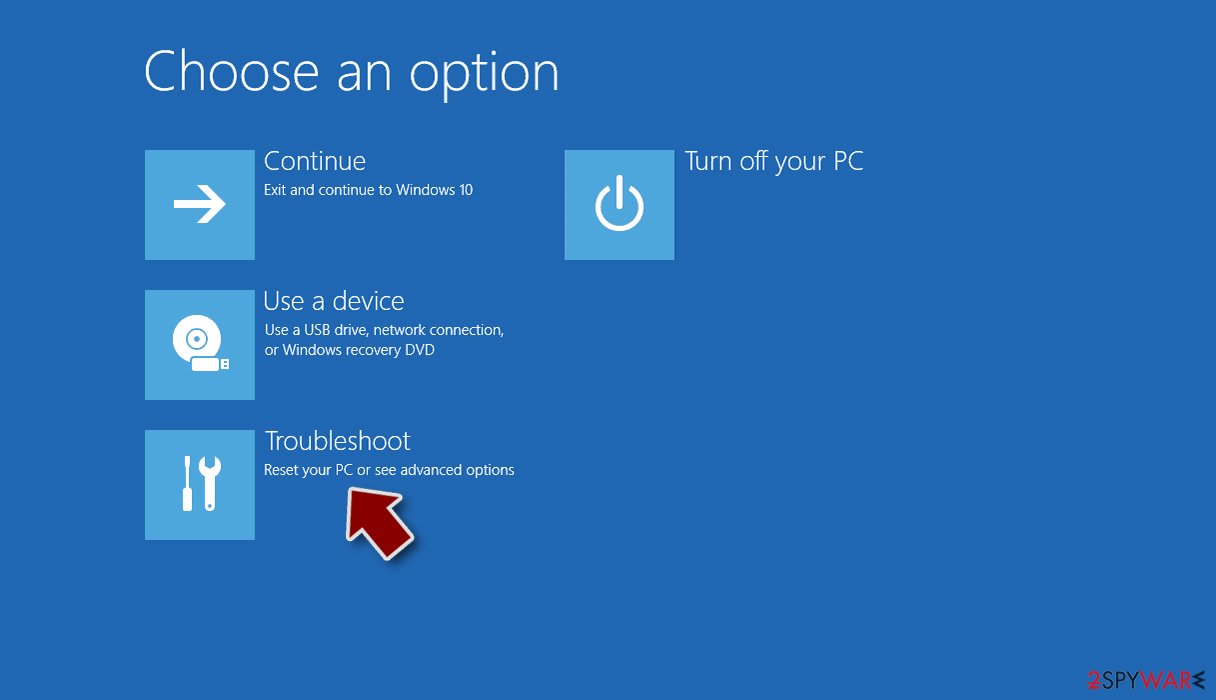
- Go to Advanced options.
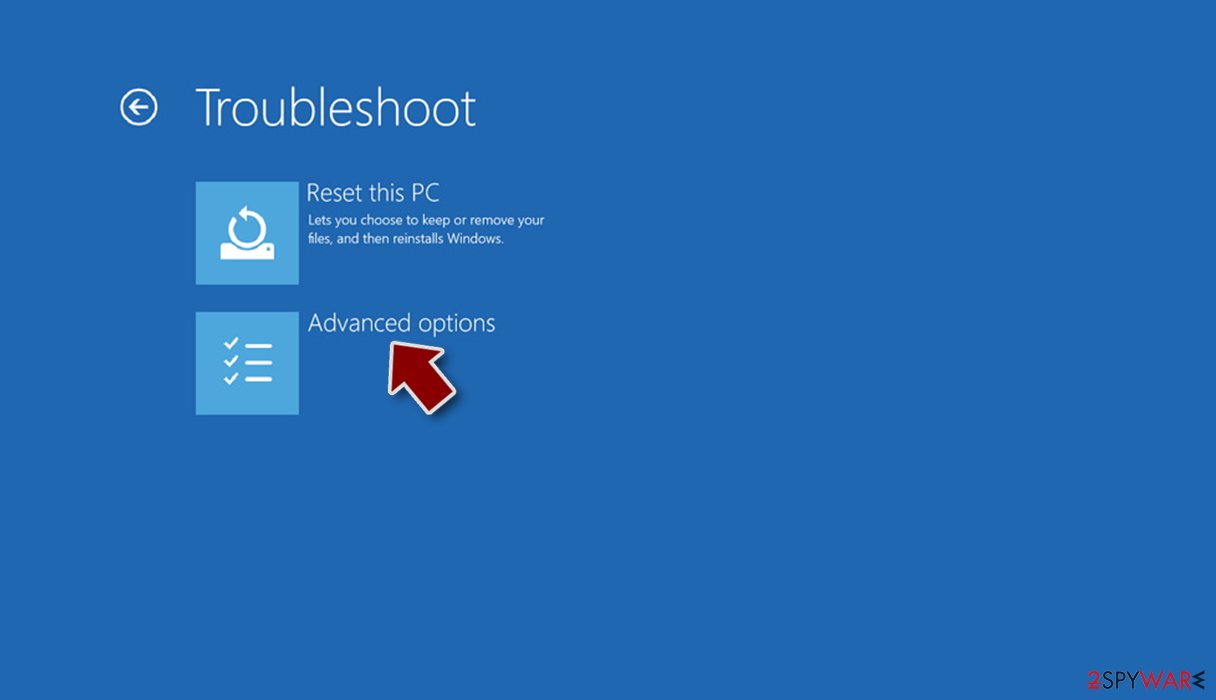
- Select Startup Settings.
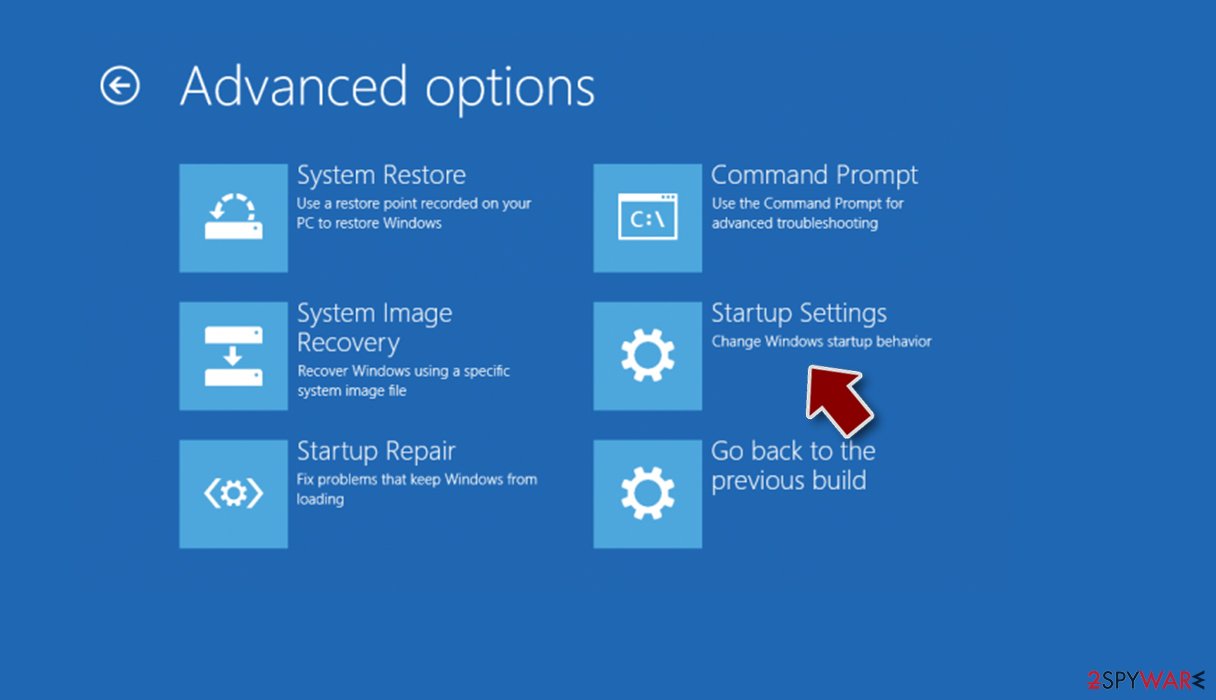
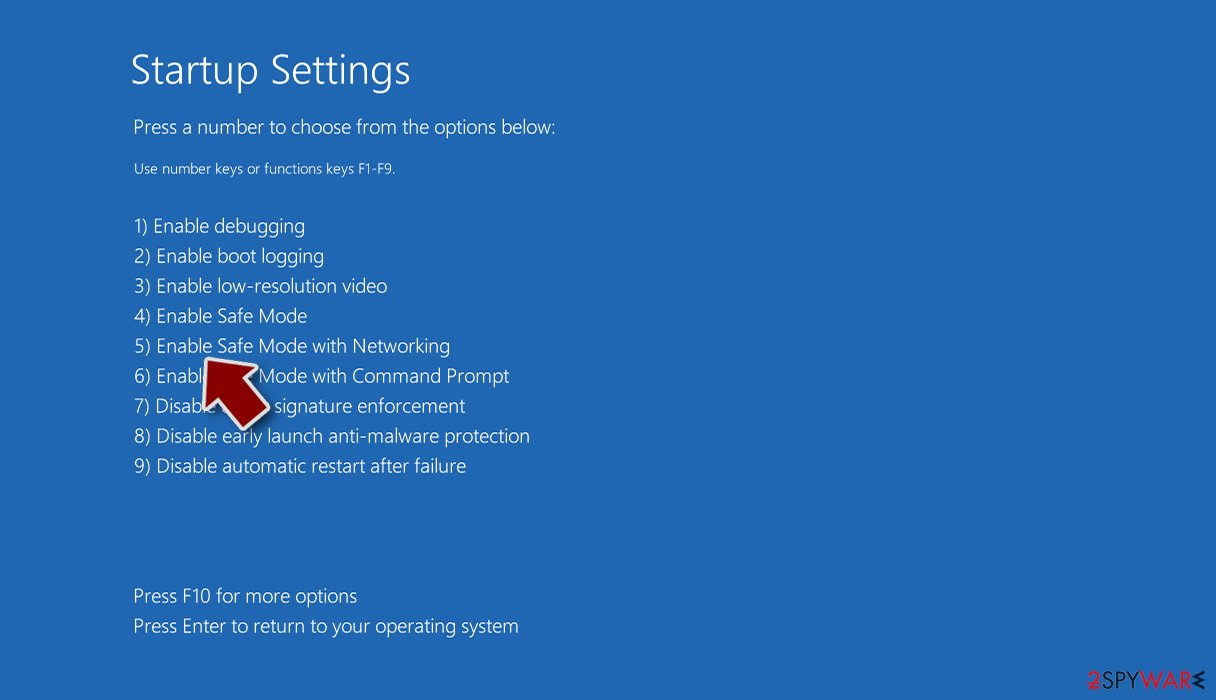
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
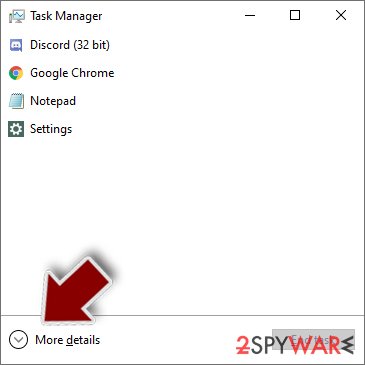
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
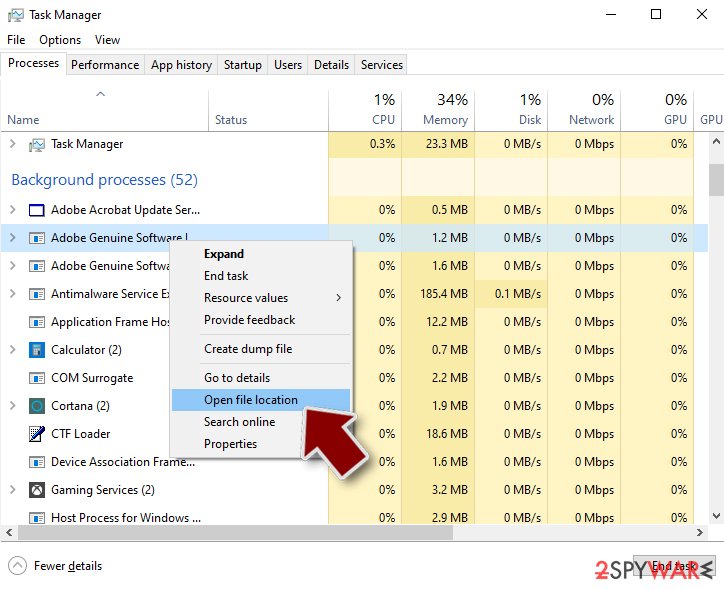
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
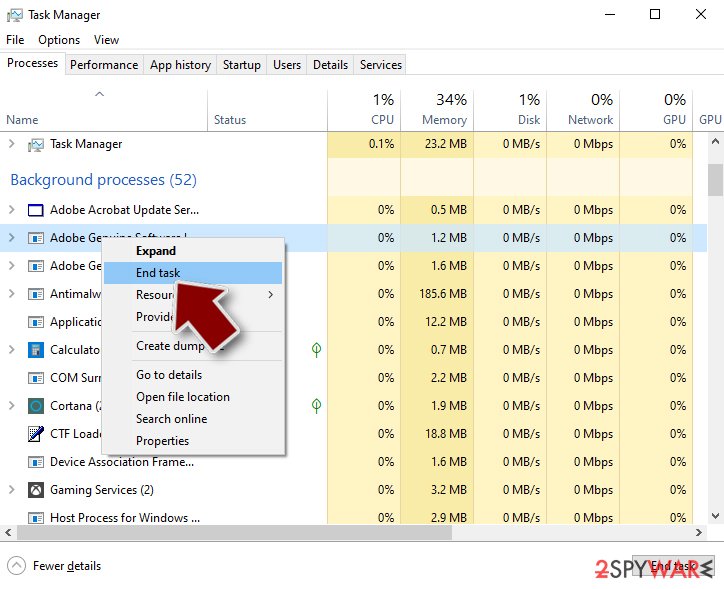
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
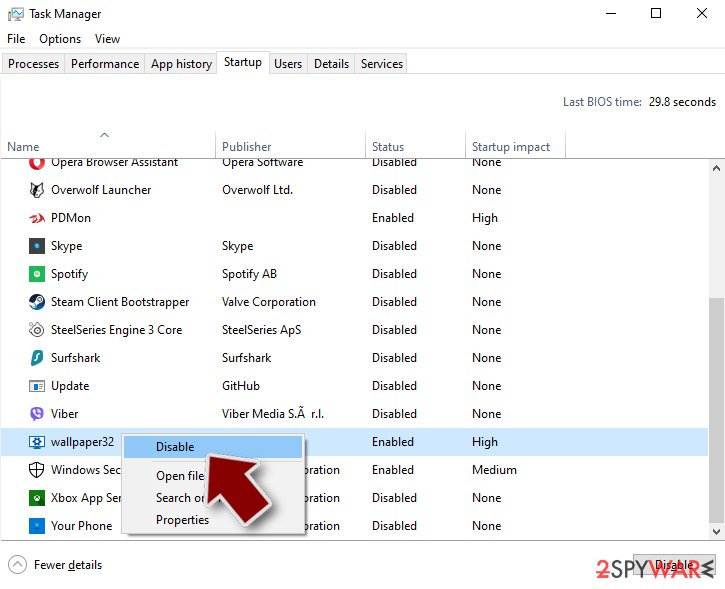
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
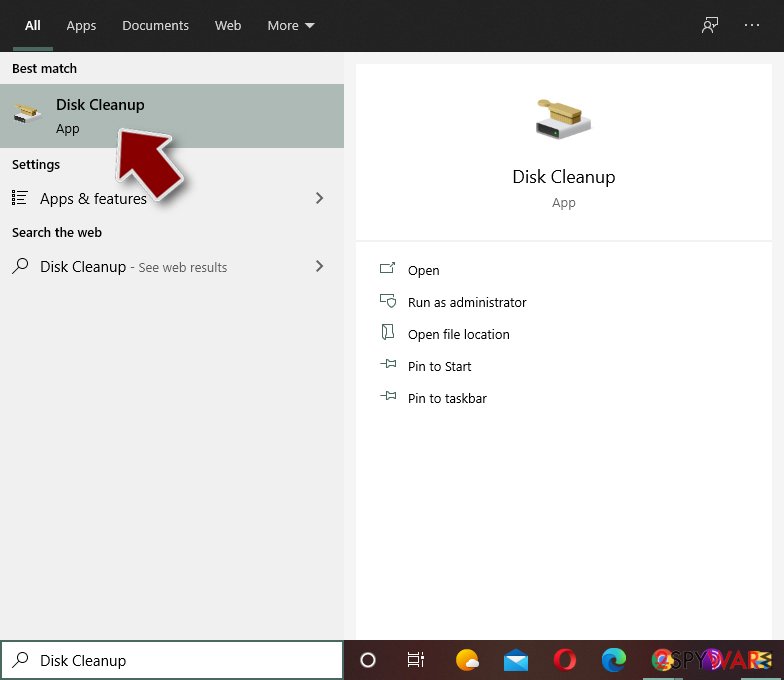
- Type in Disk Cleanup in Windows search and press Enter.
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
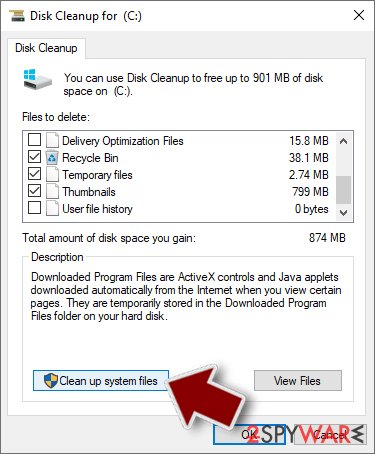
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Jan 2021 · not reviewed since
Eliminate VBS:Malware-gen virus using trustworthy security software
Trojan infection is a severe risk, and it should be taken care of as soon as possible.
Of course, to remove VBS:Malware-gen virus, you will have to employ reputable security software. Beware that some malware might hinder the proper operation of security software. In such a case reboot your PC and enter Safe Mode with networking - it will temporarily disable the virus. Virus damage is easily removed with if needed.
Do not even try manual VBS:Malware-gen removal. Malicious software is embedded deep within the system, and restoring the machine to its previous state is a mission impossible for a regular user. Therefore, merely trust security software to do the job for you instead.
After removal: passwords, accounts and prevention
Your passwords after VBS:Malware
Removing VBS:Malware does not undo what it may already have sent out while the PC showed VBS:Malware in the list of installed apps.
Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
Questions about VBS:Malware
What is VBS:Malware-gen?
VBS:Malware-gen is a generic detection name used by antivirus software for various trojan horses. The threat can range from harmless ad displays to serious data-stealing, remote computer access, and other malicious activities. It serves as a backdoor allowing other malware, such as self-propagating worms, to enter systems.
The virus typically enters computers without user awareness through exploit kits, weak passwords, open RDP connections, spam emails, and social engineering techniques. Because this is a generic detection name, actual infected files can vary significantly in their specific behavior and capabilities.
Is VBS:Malware-gen a real virus or a false positive?
VBS:Malware-gen is a real generic detection category, but antivirus tools sometimes flag legitimate system files as false positives. Users have reported that certain antivirus products misidentified regular Windows processes as VBS:Malware-gen or similar generic detections like idp.generic or idp.alexa.51.
If your antivirus reports this detection and the file appears to be a standard Windows system file, it may be a false positive. However, if the detection occurs for unknown files or suspicious processes, it warrants investigation. Verify suspicious detections by scanning with alternative antivirus software or checking the file properties and location before removing anything.
How does VBS:Malware-gen infect computers?
VBS:Malware-gen trojans typically enter computers through multiple distribution methods without user awareness. Common infection vectors include exploit kits that attack software vulnerabilities, weak passwords allowing unauthorized access, unprotected RDP (Remote Desktop Protocol) connections, spam emails containing malicious attachments, and social engineering techniques. Once inside, the malware performs a series of system changes to accomplish its goal:
- stealing data
- turning the computer into a spam machine
- redirecting to sponsored websites
- installing additional applications without consent
Users who don't practice good security hygiene face elevated infection risk from these distribution methods.
What damage can VBS:Malware-gen cause?
VBS:Malware-gen can cause significant damage by acting as a vector for ransomware infections, leading to permanent data loss. Stolen personal information such as banking details and credentials can be sold in the black market for profit. The trojan may modify targeted system settings, disable security software, redirect internet traffic, or install additional malicious programs.
It compromises both online safety and computer security. While trojan horses rarely produce visible symptoms, their silent operation makes detection difficult. VBS:Malware-gen infections should be treated as serious threats requiring immediate professional antivirus intervention.
How do I remove VBS:Malware-gen?
Removal requires reputable security software capable of detecting and eliminating the threat. Popular options include established antivirus programs that perform comprehensive full system scans. Some malware might hinder proper security software operation, requiring you to reboot your PC and enter Safe Mode with networking to temporarily disable the virus.
If security software leaves traces causing problems, repair tools can help restore system stability. Manual removal is not recommended, as trojan horses are embedded deep within system files making them nearly impossible for regular users to remove correctly. Trust reputable security software to handle the complete elimination process.
What symptoms indicate a VBS:Malware-gen infection?
Unfortunately, trojan horses like VBS:Malware-gen rarely produce visible symptoms, which complicates detection and removal. Users might experience increased CPU usage, crashing programs, error messages, and similar unexpected computer events, but these symptoms vary. Most infections occur silently in the background without user awareness.
The lack of obvious signs means victims often remain unaware until significant damage occurs or security software alerts them. This is why experts highly recommend downloading and installing comprehensive antivirus software to prevent most malicious applications from entering your PC. Regular scanning with reputable security tools provides the best protection.
How can I protect my computer from VBS:Malware-gen?
Protection involves multiple security practices to reduce infection chances. First, install and maintain reputable security software like Microsoft Defender or other established antivirus programs. Keep your operating system and all installed programs updated immediately, as software vulnerabilities are frequently discovered and patched quickly.
Avoid opening attachments or clicking hyperlinks in emails from unknown senders; scan suspicious files with Virus Total before opening. Use strong, unpredictable passwords, especially for Remote Desktop Protocol which should only be used with VPN enabled. Don't download illegal content or visit malicious sites hosting cracks, keygens, and illegal software.
Do I need to reinstall Windows if infected with VBS:Malware-gen?
Complete Windows reinstallation is typically unnecessary if you use reputable security software for removal. Established antivirus programs can detect and eliminate VBS:Malware-gen from your system in most cases. After removal, any damage to system files and settings can usually be automatically repaired using PC repair tools.
However, in severe cases where malware deeply compromises critical system files or creates persistent infections resistant to standard removal, reinstalling Windows might be necessary as a last resort. Always attempt professional antivirus removal first before considering reinstallation. Keep backups of important files before undertaking any major system repairs.
Will Fortect remove VBS:Malware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For VBS:Malware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Trend Micro: Exploit kit (read October 5, 2026)
- Avast: [FIXED] [VBS: Malware Gen] False positives Vir. def: 170221-1 22.2.2017 0:08:41 (read October 5, 2026)
- FTC: How to recognize, remove and avoid malware (read October 5, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 5, 2026)
- Microsoft Learn: How Microsoft names malware (read October 5, 2026)