
WannaLocker ransomware: what it is and how to remove it
WannaLocker is Android ransomware from 2017 that copies the screen of WannaCry, spreads as a fake King of Glory plugin and encrypts files on the phone's shared storage. Remove the app in Safe mode, do not pay the 40 yuan, and check for a free decryptor before you give up on the files.
Facts checked October 5, 2026. Steps checked against Apple's and Google's current documentation and the reports we cite. We have not run the app or the link on a phone ourselves.
Do it yourself · free Remove WannaLocker ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps
WannaLocker ransomware: summary
| Type | Android ransomware: encrypts shared storage and shows a WannaCry lookalike window |
|---|---|
| Risk | Medium for the 2017 ransomware, high for the 2019 version with spyware and a banking Trojan |
| Symptoms | App icon gone, anime wallpaper, photos that will not open, a Chinese ransom window with two timers |
| How to get rid of it | Restart in Safe mode, uninstall the app, scan with Google Play Protect; see the steps |
| Our check | Source check on 5 October 2026 (Avast, Trend Micro, CERT-In); we did not run the malware |
| First seen | Early June 2017 (Qihoo 360, Avast 7 June 2017); our first guide 2 July 2019 |
Show 12 more facts
| Contact | A QQ account named in the window and in the file names; no e-mail or wallet address |
|---|---|
| Detection names | No Microsoft detection name is known. Trend Micro: ANDROIDOS_SLOCKER.OPST; Avast: WannaLocker, WannaHydra (2019) |
| Sample hashes | SHA-256 200d8f98c326fc65f3a11dc5ff1951051c12991cc0996273eeb9b71b27bc294d and 36f40d5a11d886a2280c57859cd5f22de2d78c87dcdb52ea601089745eeee494 (2017) |
| Name | WannaLocker ransomware |
| Files and processes | com.android.tencent.zdevs.bah |
| Evidence | 0 write-ups by security sites; no sample analysed yet |
| Ransom note | none, the note is a window |
| Free decryptor | No free decryptor is known (checked 5 October 2026) |
| Distribution | Typically cracked programs, keygens and game cheats, fake installers, e-mail attachments, and Remote Desktop with weak passwords in small offices |
| Damage | Files on the PC and connected drives encrypted, restore points often deleted, sometimes a password stealer installed as well |
| Encrypted file extension | Not confirmed yet: look at the ending added to the encrypted files' names |
| Facts checked | 5 October 2026 |
Facts checked on 5 October 2026 against Avast's posts of June 2017 and July 2019, Trend Micro's analysis, the CERT-In alert and our own 2019 screenshots. We did not run the malware.
What WannaLocker is
WannaLocker is Android ransomware from June 2017 that copies the screen of WannaCry: a fake King of Glory plugin that encrypts files on the phone's shared storage with AES and asks for 40 yuan, not Bitcoin.
It is not the Windows worm WannaCry, and no source we read shows it running on a PC.
- Platform
- Android phones and tablets
- Family
- A variant of SLocker (Trend Micro:
ANDROIDOS_SLOCKER.OPST); the 2019 banking version is WannaHydra - Package name
com.android.tencent.zdevs.bah- Price
- 40 yuan (about 5 to 6 US dollars) through QQ, Alipay or WeChat
How the WannaLocker story went
June 2017
First reports
Qihoo 360 reported it first. Avast named it WannaLocker on 7 June. Trend Micro says decrypt tools followed within days and a suspect was reportedly arrested (it cites a Tencent news item we could not read).
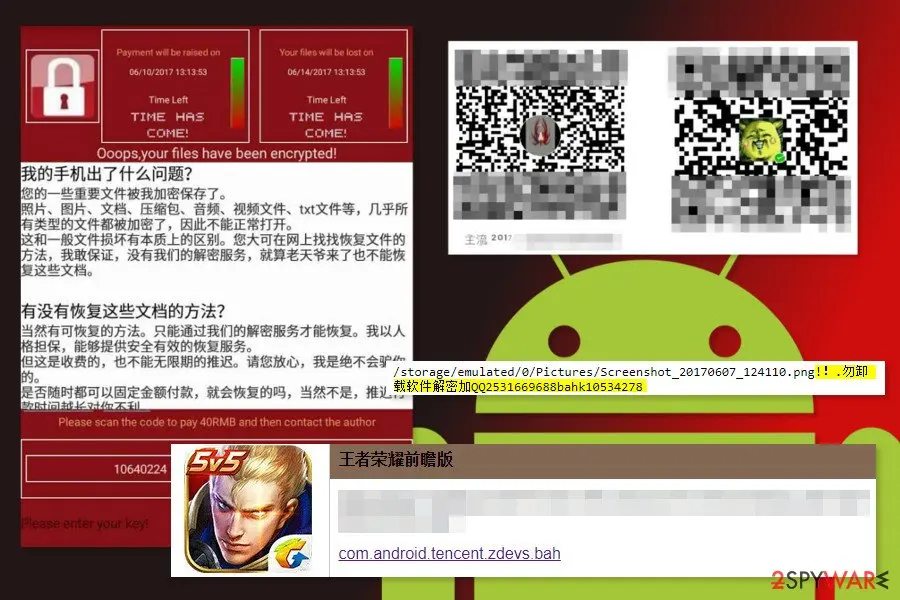
Our 2019 collage: the ransom screen, a file name with Chinese text appended, and the app entry 王者荣耀前瞻版 with its package name (the Android robot is report artwork). 1 July 2019
A banking version in Brazil
Avast reports a version with spyware, remote access and banking code aimed at four Brazilian banks. Dark Reading calls it WannaHydra.
11 July 2019
CERT-In alert
India's CERT-In rated the threat High and named the AhMyth remote access tool.
What we checked and what we did not
We did not run this malware and no website is involved, so this is a check of sources.
WannaLocker ransomware · source check · 5 October 2026
- Ransom windowRead from our 2019 screenshots; English lines verbatim, Chinese lines our translation.
- GapsThe vendors disagree about the DCIM and download folders, we did not check a current decryptor list, and the Android steps from Google's help were not tested on an infected phone.
Old, but the 2019 version is the risk The 2017 ransomware spread mostly on Chinese forums.
- Note file:
none, the note is a window - File:
com.android.tencent.zdevs.bah
How WannaLocker ransomware behaves
What it does on the phone, step by step
The order comes from Avast's and Trend Micro's 2017 analyses of the first samples; later variants changed details.
- 1
You install a fake game plugin
Trend Micro's first sample was called 王者荣耀辅助 (King of Glory Auxiliary); others posed as game guides or video players.
- 2
The icon and name change
On the first run it disables its launcher entry and enables a second one, so the icon and name change. Avast adds that it hides its icon from the app drawer.
- 3
The wallpaper becomes an anime picture
The anime wallpaper is the first sign the owner sees.
- 4
It encrypts the shared storage
It makes a random number, builds an AES key from its MD5 hash and encrypts matching files. Each file name gets a suffix that holds a QQ number and the random number (Trend Micro).
- 5
The ransom window opens
A full-screen Chinese window modelled on WannaCry's shows two timers, payment QR codes and a box for the key.
Which files it encrypts and which it skips
Personal files in shared storage are the target, and the two vendors disagree about the Pictures and Downloads folders, so check every folder.
| Rule | Avast, June 2017 | Trend Micro, July 2017 |
|---|---|---|
| Names | Skips names starting with a dot | Skips paths with /.; the name must contain a dot |
| Folders | Skips paths with "DCIM", "download", "miad", "android", "com." | Skips "android", "com.", "miad"; targets "download" and "dcim" paths and folders under three levels deep |
| Size | Skips files under 10 KB | Only files from 10 KB to 50 MB |
Our 2019 guide said files "bigger than 10 KB" are skipped and wrote "DCMI". Both are wrong: small files are skipped and the folder is DCIM.
What the window demands
The price is small and paid in everyday Chinese payment apps, not cryptocurrency.
| Item | What we know | What it means |
|---|---|---|
| Price | 40 yuan (Avast) | Far below other mobile ransomware. |
| Payment | QQ, Alipay, WeChat; two QR codes (Avast). All three options in Trend Micro's sample led to one QQ code | Easy to trace, as Avast notes. |
| Timers | "Payment will be raised on" 10 June and "Your files will be lost on" 14 June 2017 in our screenshot; Trend Micro: after three days and a week | Pressure. We found no report of files really being deleted. |
| Key | A box for a key sent after payment | In the first sample it was the stored number plus 520 (Trend Micro). |
How it reaches phones
Only one route is documented.
The routes in our 2019 guide are possibilities, not findings.
- High
A fake game plugin
Avast and Trend Micro describe a King of Glory helper posted on Chinese game forums, QQ groups and bulletin boards.
- Medium
Third-party stores and links
Avast and CERT-In suspect them for the 2019 version.
- Low
Spam, malvertising, fake updates
Listed in 2019 for ransomware in general; no source ties them to WannaLocker.
WannaHydra: spyware and a banking Trojan
The 2019 version steals far more than files: Avast lists messages, call log, contacts, camera photos, location, microphone audio and what you type into a fake bank screen.
- High
Fake bank sign-in
Owners of four targeted bank apps see a message about an account problem and are asked to sign in (Avast).
- High
Spyware and remote access
CERT-In names the AhMyth remote access tool and the WannaHydra banking component.
- Medium
Ransomware as a fallback
Avast saw the encryption part unfinished. A Dark Reading commentator guesses it runs when no targeted bank app is installed.
Our 2019 guide said it "attacked four banks"; Avast reports it targets customers of four Brazilian banks. If you use a bank app on a phone that had it, treat the bank password as stolen.
What to do in the first hour
Do not pay and do not uninstall yet: first save what decides how files can be restored.
- 1
Photograph the window
Include the number in the key box and the timers. Do not scan the QR codes.
- 2
Go offline
Turn on airplane mode, so the app cannot send data out.
- 3
Pause backup and sync
If sync replaces good copies with encrypted ones the cloud copy is lost; sources do not document it for this family.
- 4
Copy a few encrypted files to a computer
Use a cable, copy two or three files and the photo, then disconnect.
The WannaLocker ransomware note
Ooops, your files have been encrypted!
Payment will be raised on / Your files will be lost on (two countdown timers)
What happened to my phone? Some of your important files were encrypted. Photos, pictures, documents, archives, audio, video and txt files, almost every type of file, cannot be opened normally. I guarantee that without our decryption service they cannot be restored.
Is there a way to recover them? Only through our decryption service. It costs money and cannot be put off forever.
Please scan the code to pay 40RMB and then contact the author
Please enter your key!
Can WannaLocker ransomware files be decrypted?
Can the encrypted files be restored?
Possibly, and not by paying: Trend Micro found the first sample's key was a stored number plus 520, and says free decrypt tools came out in 2017.
Our 2019 guide said no decryptor existed; that is out of date for the first samples. Later variants changed the formula.
- 1
Look for a free tool
Keep the encrypted copies, whose file-name suffix holds the number analysts used. Search for WannaLocker and SLocker on the official lists of No More Ransom, Kaspersky and Emsisoft. We did not confirm an entry.
- 2
Try your own copies
Cloud photo backup, a computer, a memory card and chat history often hold the same pictures. Open the cloud on a computer and choose a version before the attack.
Do
- Remove the app before any decrypting, so it cannot encrypt again
Don't
- Do not enter keys from forums
- Do not download a "decryptor" from an ad: fake ones spread malware
Should you pay the 40 yuan?
No. The small amount is the bait: nothing obliges the seller to reply, and QQ, Alipay and WeChat payments are easy to trace (Avast), as our 2019 guide said.
- High
You may get nothing
The timers are pressure; we found no report of files being deleted.
- Medium
Payment does not remove the app
It stays on the phone, and the 2019 version also contains spyware.
How to remove WannaLocker ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove WannaLocker ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
WannaLocker ransomware encrypts everything it can reach, including drives and shares you connect later. Cut the network first: cable out, or Wi-Fi off from the taskbar.
Then unplug every USB stick and backup disk and pause cloud sync, so the encrypted versions do not replace your online copies. Do not reconnect any of them until the ransomware is removed from the Windows 11 or Windows 10 PC.
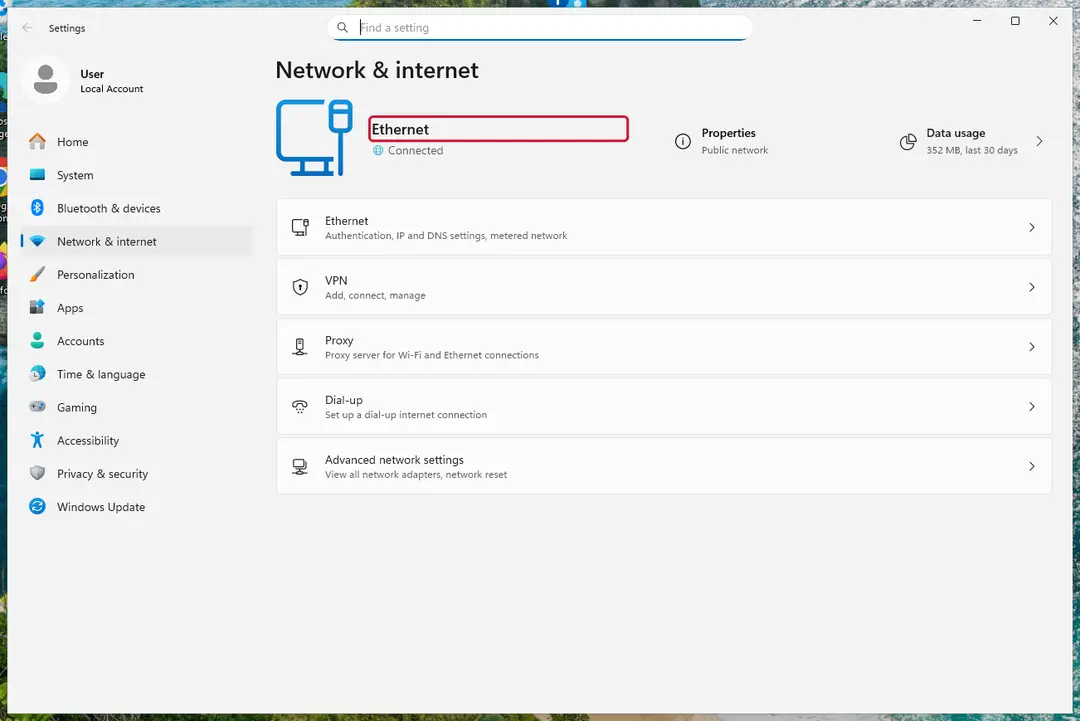
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and identify the family
Find the ransom note, usually a
.txt,.htmlor .hta file in every folder or on the desktop, and copy it with one or two encrypted files to a USB stick.From another device, upload them to ID Ransomware or No More Ransom's Crypto Sheriff, which name the family from the note and the file extension. Write down the contact address and your personal ID from the note for the report.
Warning: Never contact the attackers from the infected Windows 11 or Windows 10 PC.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
For WannaLocker ransomware, no free decryptor is known (checked 5 October 2026). Search the family name in the No More Ransom decryption tools list and in the free decryptors of Emsisoft, Avast and Kaspersky, because new tools appear years after an attack.
Important: Keep the encrypted files even if nothing works today, and do not pay before every free option is ruled out: payment does not guarantee a working key.
Decryptors run on Windows 11 and Windows 10, but only after the ransomware itself is removed.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Restoring or decrypting files while WannaLocker ransomware still runs lets it encrypt them again. Run a Full scan in Windows Security > Virus & threat protection > Scan options, then the Microsoft Defender Antivirus (offline scan).
If the ransomware blocks Windows Security, start Safe Mode with Networking and scan from there. Some families install a password stealer as well, so let both scans finish on Windows 11 or Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Open Command Prompt as administrator and run
vssadmin list shadows. If it lists copies dated before the attack, right-click a folder with encrypted files in File Explorer, choose Properties > Previous Versions, and open or restore a version from before that date.ShadowExplorer, a free tool, shows the same copies when the tab is empty or hidden. Most current families delete shadow copies, so an empty list is normal, but the check takes two minutes on Windows 11 or Windows 10.
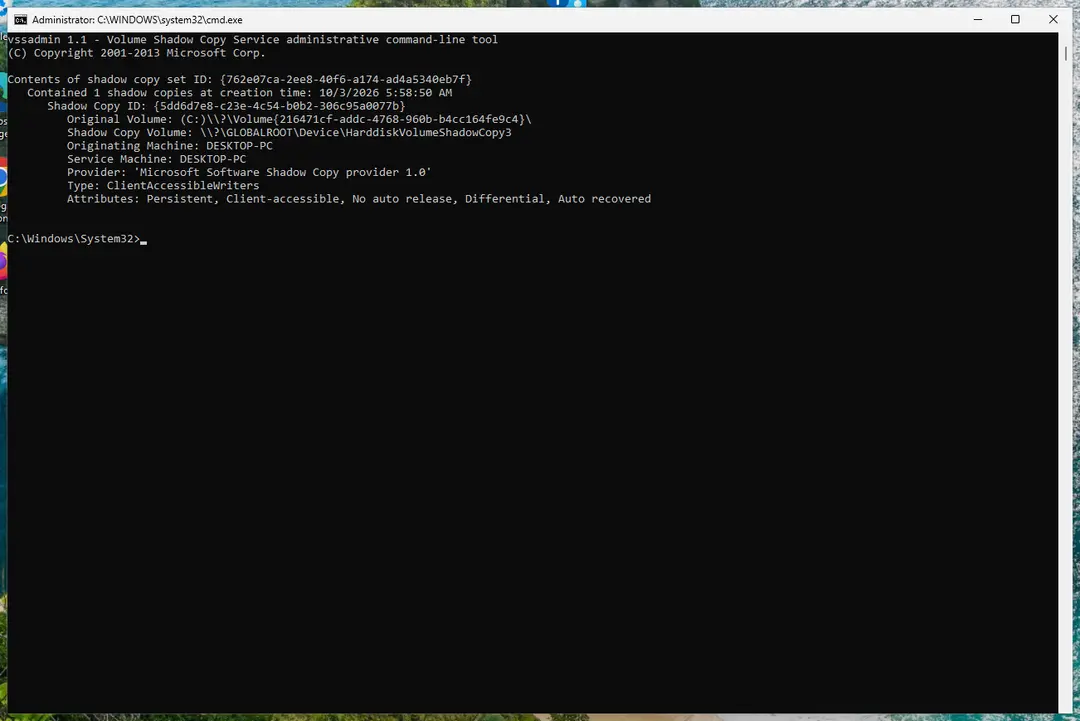
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
Restore from an external backup, File History or OneDrive's version history, choosing a date before the attack. Connect the backup drive only after the scans are clean, or the ransomware encrypts it too.
If there is no backup, file recovery software can sometimes find the deleted originals, because some ransomware writes an encrypted copy and deletes the original file.
Stop writing to the drive and try recovery on Windows 11 or Windows 10 before new files overwrite the space.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Removing WannaLocker from an Android phone
Start in Safe mode, uninstall the app, then scan with Google Play Protect. These steps follow Google's malware help, not the old guide's antivirus-only advice; menu names differ by maker, and we did not test them on an infected phone.
- 1
Restart in Safe mode
Hold the power button, touch and hold Power off, and confirm Safe mode. Safe mode turns off third-party apps until you restart. Some phones use a different key combination.
- 2
Find and uninstall the app
Open Settings > Apps > See all apps (older Android: Apps & notifications). Tap the unfamiliar game helper, or
com.android.tencent.zdevs.bah, then Uninstall. If Uninstall is greyed out, check the device administrator apps list under Security & privacy; we could not confirm that for this family. - 3
Restart normally and scan
In Google Play Store tap your profile picture, then Play Protect > Settings, and turn on Scan apps with Play Protect. If you installed from outside the Play Store, also turn on Improve harmful app detection.
- 4
Update and check your account
Install updates under Settings > System > Software updates, then open
myaccount.google.com/security-checkupon another device. After the 2019 version, change the bank password from a clean device. - 5
Reset only as a last resort
Google says you may need to reset the phone if signs of malware remain. A reset erases the phone, so copy the encrypted files to a computer first.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Back up with the 3-2-1 rule
Our 2019 guide advised backing up the phone and the computer; the 3-2-1 rule from CISA's ransomware guidance makes it a plan.
| Number | Rule | Example |
|---|---|---|
| 3 | Three copies | The phone plus two backups |
| 2 | Two kinds of storage | Cloud photos and a computer |
| 1 | One copy out of the phone's reach | A disk you connect only to copy |
How to prevent WannaLocker ransomware and the next attack
Do
- Install apps only from Google Play and read the downloads, reviews and permissions first
- Keep Install unknown apps off, Play Protect on and Android updated
- Use the official bank app with two-step sign-in
Don't
- Do not install game cheats or helpers from forums and chat groups
- Do not follow links in messages that ask you to install something
Questions about WannaLocker ransomware
What is WannaLocker?
WannaLocker is Android ransomware first reported in June 2017 that copies the screen of the Windows worm WannaCry. It spread as a fake plugin for the game King of Glory on Chinese forums and encrypted files in the phone's shared storage with AES.
Its window asked for 40 yuan, about 5 to 6 US dollars, paid through QQ, Alipay or WeChat. In July 2019 Avast reported a version that added spyware, remote access and a banking Trojan aimed at four Brazilian banks.
Can I open my encrypted .jpg and .docx files?
Not while they are encrypted, but you may be able to restore them. WannaLocker encrypts photos, documents, archives, audio and video in the phone's shared storage and adds a suffix with a QQ number and a random number to each file name.
It skips names starting with a dot and files under 10 KB. Renaming a file back does not help. Copy a few encrypted files to a computer, remove the app, and then look for a free decryptor or your own backup.
How do I remove WannaLocker from my Android phone?
Restart in Safe mode, uninstall the app, restart normally and scan with Google Play Protect. Hold the power button, touch and hold Power off and confirm Safe mode. Then open Settings, Apps, See all apps, find the unfamiliar game helper or the package com.android.tencent.zdevs.bah, and tap Uninstall.
These steps follow Google's malware help, and we did not test them on an infected phone. Before you uninstall, photograph the ransom window and copy a few encrypted files to a computer.
Is there a WannaLocker decryptor?
Possibly, for the 2017 samples, though our 2019 guide said none existed. Trend Micro reported that decrypt tools were published within days and that the first sample accepted a key equal to a stored random number plus 520.
We could not confirm a current tool and did not check the No More Ransom list for it, so look for a WannaLocker or SLocker entry on the official lists of No More Ransom, Kaspersky and Emsisoft. Never download a decryptor from an ad or a forum.
Should I pay the WannaLocker ransom?
No. The window asks for 40 yuan, paid through QQ, Alipay or WeChat, and then for you to contact the author. In the first sample the key could be worked out from a number stored on the phone, so payment was never needed.
The timers that raise the price after three days and threaten deletion after a week are pressure; we found no report of files really being deleted. Payment also does not remove the app, which can contain spyware.
Do paid decryption services or recovery companies work for WannaLocker?
We found no evidence that one is needed. A recovery company can do nothing with Android shared storage that a free tool or a backup cannot, and some resell a ransom payment at a markup.
For the first samples, Trend Micro showed that the key was a stored number plus 520, so analysts and free tools solved it without payment. Try the official free lists and your own backups first, and never pay a company in advance.
Is WannaLocker the same as WannaCry?
No. WannaCry is a Windows worm that spread in May 2017 through a Windows file-sharing flaw and encrypted PCs, according to Cisco Talos. WannaLocker is an Android app that copied WannaCry's ransom screen a few weeks later.
The two share nothing else in the sources we read, so Windows tools and updates for WannaCry do not help a phone, and the removal steps differ. We found no WannaLocker sample for Windows or iPhone.
What did the 2019 WannaLocker version steal?
Avast reported that the 2019 version collects text messages, call logs, the phone number, contacts, GPS location, photos from both cameras, microphone audio and manufacturer details. It also shows a fake sign-in screen over four Brazilian banking apps and collects what the owner types.
CERT-In names the AhMyth remote access tool and the WannaHydra banking component. If you suspect this version, change the bank password from another device, tell the bank, watch the account and turn on two-step sign-in.
How did WannaLocker get on my phone?
The documented route is a fake plugin or helper app for the game King of Glory, downloaded from Chinese game forums, QQ groups and bulletin boards. For the 2019 version Avast does not know the route and suspects malicious links or third-party app stores.
Spam and fake updates, listed in our 2019 guide, are not tied to this family by any source. Installing apps only from Google Play and keeping unknown sources off blocks the known route.
Will Fortect remove WannaLocker ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For WannaLocker ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Avast: WannaCry WannaBe targeting Android smartphones (7 June 2017) (read October 5, 2026)
- Avast: WannaLocker targets banks in Brazil (1 July 2019) (read October 5, 2026)
- Trend Micro: SLocker Mobile Ransomware Starts Mimicking WannaCry (read October 5, 2026)
- CERT-In Cyber Swachhta Kendra: WannaLocker/Slocker Android Ransomware (read October 5, 2026)
- Tripwire: The WannaCry Copycat Targeting Android Users in China (read October 5, 2026)
- Dark Reading: New WannaHydra Malware a Triple Threat to Android (read October 5, 2026)
- Google Account Help: Remove malware or unsafe software (Android) (no longer online) (read October 5, 2026)
- Cisco Talos: Player 3 Has Entered the Game, Say Hello to WannaCry (read October 5, 2026)
- CISA: StopRansomware (read October 5, 2026)