
CrescentCore, OSX/CrescentCore: what it is and how to remove it
CrescentCore, also known as OSX/CrescentCore is a Trojan horse designed to infect Mac computers by avoiding antivirus detection. This dangerous threat is capable of secretly hiding inside a .dmg disk image and pretends to be a fake update of the Adobe Flash Player tool.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with CrescentCore, OSX/CrescentCore.
Do it yourself · free Remove CrescentCore, OSX/CrescentCore yourself 7 steps, about 21 minutes, no software needed.
Start the steps
CrescentCore, OSX/CrescentCore: summary
| Distribution | Malicious websites, infected hyperlinks, fake Adobe Flash Player updates |
|---|---|
| Name | CrescentCore, OSX/CrescentCore |
| Type | Trojan horse/Mac malware |
| Appears as | Fake Adobe Flash Player update |
| Target | Mac systems that are not running on virtual machines and have no strong security |
| Related objects | LaunchAgent |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 6 more facts
| Detection names | No Microsoft detection name is known |
|---|---|
| Damage | Not recorded in the old report |
| Symptoms | An unknown program in Installed apps |
| Evidence | 6 write-ups by security sites; details still limited |
| First seen | 13 August 2021 |
| Facts checked | 6 October 2026 |
What CrescentCore, OSX/CrescentCore does on an infected Mac
From our report of Aug 2021 · not reviewed since
CrescentCore is the malware that can significantly damage the machine and evade detection
CrescentCore, also known as OSX/CrescentCore is a Trojan horse designed to infect Mac computers by avoiding antivirus detection.
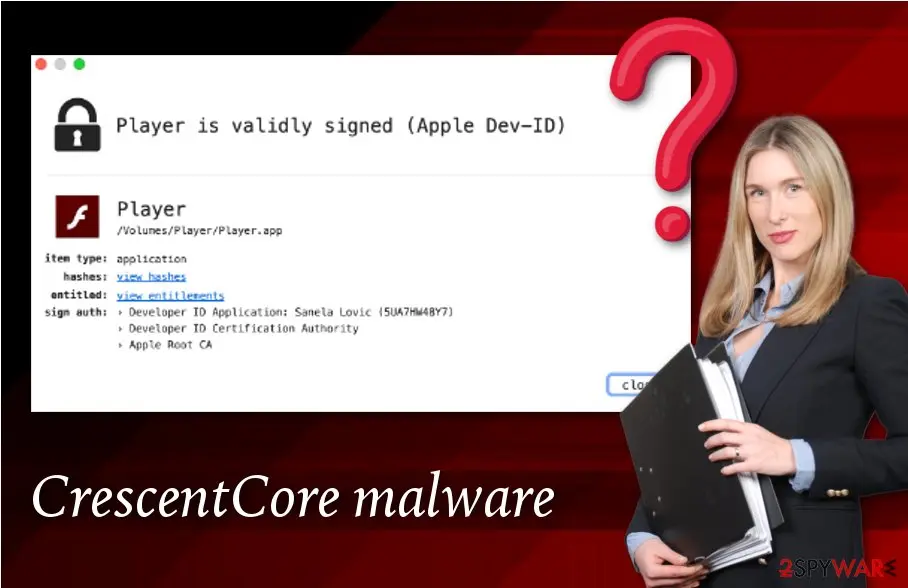
This dangerous threat is capable of secretly hiding inside a .dmg disk image and pretends to be a fake update of the Adobe Flash Player tool. Nevertheless, this type of malware aims to inject other programs into the system if the infected OS is not activated on a virtual machine and if no third-party security tools are enabled.
The infection process of any Mac malware, similar to OSX/Shlayer, begins when the victim clicks on the disk image icon and enters the fake Flash Player application. However, the threat takes some certain precautionary measures and identifies if it is not a virtual machine that it is running on. If not, malicious activities successfully continue.
Such a precaution step is taken by CrescentCore to ensure that the cybercriminals do not damage their own systems during the infective period.
Nevertheless, the Trojan virus needs to ensure that no antivirus protection is running on the infected system and if the malware finds out that it is working on a virtual machine or there is anti-malware on the system, it immediately stops the infections process and deletes itself from the computer/laptop.
If you are a Mac user who has always been concerned about automatic system protection, we can congratulate you as OSX.CrescentCore should not appear on your computer. However, if your machine lacks the required security, the risk of getting infected with this Trojan horse might not be that small as you expect it to be.
If CrescentCore finds all conditions satisfying, it continues malicious actions by installing another component known as LaunchAgent. Talking about what it does after such installation, cybersecurity researchers do not have one true answer. However, the Trojan horse might relate in the injection of suspicious security tools such as Advanced Mac Cleaner, Mac Tonic, Mac Mechanic, Auto Mac Speedup, and similar.
Besides, security experts think that the new malware strain might be capable of injecting a malicious "helper object" (e.g. extension) into the Safari web browser application. This type of activity can lead anywhere. CrescentCore and LaunchAgent might start spying on your personal information or credentials for misusing them in the future.
If you have discovered this notorious malware on your Mac computer system, you should be careful with it and opt for malware removal right away. Note that trojan infections might relate to high CPU work, injection of other malicious programs, corruption of software or files, collection of personal data/credentials.
You should not try to remove CrescentCore by yourself as manual activities might relate to more damage than you think it could. Our suggestion would be to scan the entire system with a strong antivirus program such as , to identify all malware strains. Once you find their directories, clean these locations with reputable software entirely.
From our report of Aug 2021 · not reviewed since
More from our earlier report on CrescentCore, OSX/CrescentCore
- Use anti-malware tools to perform a full system scan and find malware
- In addition to virus removal, you should take care of the virus damage to, so run to fix possible
How CrescentCore, OSX/CrescentCore got on your Mac
From our report of Aug 2021 · not reviewed since
Security experts from NoVirus.uk claim that dangerous infections often choose unprotected sources to be placed in.
These pages are easy to enter and due to the lack of protection they provide, potential victims are also very easy to catch here. If you like entering third-party video-watching, gambling, adult-themed, or piracy websites, you have a big risk of ending with notorious malware on your computer system.
The second way of distributing notorious viruses is by using fake Adobe Flash Player updates. Messages which claim that updates are needed for the Player app often appear to be very legitimate-looking and aim to trick a big number of users.
However, we want to warn users not to fall for such tricks, especially, if they are using Google Chrome. This browser updates its in-built Player automatically and no manual updates are ever needed.
Malware might also be pushed through email spam campaigns and come injected into normally-looking attachments which are the main carriers of the malicious payload. Be aware of messages that include numerous grammar mistakes, come from an unrecognizable sender. All attachments (even legitimate-looking ones) need to be put under a scan of anti-malware software for full identification.
How to remove CrescentCore, OSX/CrescentCore
How to remove CrescentCore, OSX/CrescentCore from a Mac
Start with the passwords and crypto, from another device: a stealer copies them in seconds.
Then clean the Mac, or erase it.
Step 1: Change passwords from another device first
If you pasted a command into Terminal or opened a downloaded file from CrescentCore, OSX/CrescentCore, assume the passwords saved in the browsers and in Keychain on this Mac are known to the attacker.
From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and work accounts, and sign out of all other sessions on each one.
Move any cryptocurrency to a new wallet created on a clean device, because a seed phrase that was stored on this Mac is compromised. Do this before cleaning the Mac: cleaning does not undo the theft.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Step 3: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 4: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from CrescentCore, OSX/CrescentCore or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 5: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 6: If it was an infostealer, erase and reinstall macOS
Stealers copy data and often leave persistence you cannot be sure you found.
The only complete fix is to back up your personal files only (documents, photos, not apps or settings), then open System Settings > General > Transfer or Reset > Erase All Content and Settings, or use macOS Recovery to erase the disk and reinstall macOS, as Apple describes in its support articles.
Restore only your files afterwards, and install apps again from their official sources.
Step 7: Report it and watch your accounts
Report the site and the command to the authorities in your country, and tell your bank if any card was saved in a browser or in Keychain.
Over the next weeks watch your e-mail, bank and exchange accounts for sign-ins and transfers you did not make. Keep the notes you made, such as the process names and the file dates, in case a bank or the police ask for them.
Full procedure with screenshots: Report a cyber attack or scam to the authorities
From our report of Aug 2021 · not reviewed since
Elimination of the CrescentCore virus
CrescentCore removal process is not a thing you should postpone or not pay attention to.
Most important, DO NOT try to get rid of this malware by yourself if you lack skills in this field. However, if you believe that you are a well-experienced user and have found some signs of infection on your computer, what you can do by yourself is disabling malicious processes if some are found in your Mac machine:
Once you have done this, you can also search for malicious strings related to the malware in your Mac login items. If you have found some, you can delete them with the help of these guiding steps:
However, our suggestion would still be to use reputable anti-malware programs such as , , for detecting all components related to this Trojan virus. Also, you can keep the antivirus protection on your computer/laptop for future safety purposes.
- Go to Launchpad and type in "Activity Monitor".
- Open the application and go to the Processes tab.
- Find all suspicious processes and press the X button to quit them.
- Locate the Apple menu and continue with System Preferences.
- Press on the Users & Groups sector.
- Ensure that your username is picked in the left side.
- After that, find all suspicious login components in the Login Items tab.
- Use the minus (-) sign to eliminate them.
After removal: passwords, accounts and prevention
Secure your accounts after the clean-up
Assume that whatever was saved in the browsers on this PC while the PC showed crescentCore, OSX/CrescentCore in the list of installed apps has been copied:
- passwords
- cookies
- autofill data
Work from a clean device, or from this PC once the offline scan finds nothing.
Start with your main e-mail account, because it can reset everything else, then banking and payment, then social and gaming accounts. Change each password, sign out of all sessions and turn on two-step verification: Turn on two-step verification / secure a hacked account.
The full order, including crypto wallets and card replacement, is in securing your accounts after malware.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about CrescentCore, OSX/CrescentCore
What is CrescentCore, OSX/CrescentCore and why is it on my PC?
CrescentCore, OSX/CrescentCore is a program that was installed on the PC, most likely together with something else you downloaded. Free software sites and many installers add extra programs on setup pages with pre-ticked boxes, so the extra install looks like your choice even though nobody read the page.
Check the install date in Settings, Apps, Installed apps: the program you installed that day is the probable carrier. If you do not need CrescentCore, OSX/CrescentCore, uninstall it. If it belongs to your hardware or to a program you use, search its exact name and publisher first, because drivers and their tools can have unfamiliar names.
How do I stop programs like CrescentCore, OSX/CrescentCore from being installed again?
Most unwanted programs arrive through installers, so the fix is in how you install software. Download programs from their official sites or the Microsoft Store, not from download portals or ads above search results. During setup, choose Custom or Advanced installation and untick every extra offer, including browsers, toolbars and optimizers.
Decline update prompts that appear inside other programs unless you know them. In Windows Security, turn on reputation-based protection and potentially unwanted app blocking. These steps would most likely have stopped CrescentCore, OSX/CrescentCore before it reached the app list.
Can a normal remote support program be a backdoor?
Yes. Tools such as AnyDesk, TeamViewer and ScreenConnect are legitimate, but whoever controls the account behind them controls the PC. Scammers install them during fake support calls, and some trojan campaigns install them silently because antivirus programs do not flag a genuine, signed product.
If you find one you did not set up, uninstall it, check Startup apps for related entries and change passwords from another device. If money or accounts were involved, call your bank and report the incident.
How dangerous is CrescentCore, OSX/CrescentCore?
Treat it as serious until proven otherwise. The visible sign is crescentCore, OSX/CrescentCore in the list of installed apps, and programs that behave this way often have more abilities than they show:
- copying passwords
- downloading other malware
- giving remote access
Its family is not known yet, so nobody can say which of these it uses. The good news is that the response is the same in every case and takes about an hour:
- cut the network
- remove the startup entry
- run an offline scan
- change passwords from a clean device
If someone had remote control, a full reset is safer.
Is a trojan infection worth reporting to the police?
If there was harm, yes. Unauthorised payments, accounts used for fraud, blackmail or a remote session during a scam call all belong in a report, and banks often ask for its reference number before they refund anything.
If antivirus caught CrescentCore, OSX/CrescentCore before it ran and nothing was misused, there is nothing to report. Keep the evidence anyway:
- protection history
- the original download
- the dates
Businesses may also have to notify a data protection authority if personal data could have been accessed.
What are the signs of a trojan infection?
Most trojans try to leave no visible signs, so look for side effects. Common ones:
- Windows Security turned off or unable to update
- new entries in Startup apps or Task Scheduler
- programs in Installed apps you did not install
- browser settings that changed by themselves
- unusual network activity while the PC is idle
- password-reset or login-alert e-mails you did not trigger
None of these proves an infection on its own. Together with an antivirus alert naming CrescentCore, OSX/CrescentCore, they are a strong reason to follow the full plan.
Which malware family is CrescentCore, OSX/CrescentCore?
That is not known yet. CrescentCore, OSX/CrescentCore has been reported by people who saw crescentCore, OSX/CrescentCore in the list of installed apps, but no sample has been analysed publicly, so security companies have not assigned it to a family. The name you see may be a file or program name chosen by the authors, not a family name.
This does not stop you from removing it: the startup points, the offline scan and the account steps are the same for most families of this type. If Microsoft Defender or another scanner gives the file a detection name, write it down; that name is the best clue to the family and is useful when you report the incident.
Should I reset my PC because of CrescentCore, OSX/CrescentCore?
Only if the signs point to deeper access. Reset when you see crescentCore, OSX/CrescentCore in the list of installed apps again after removal, when Windows Security cannot start or update, when remote access tools you did not install keep appearing, or when you simply cannot trust the PC any more.
Otherwise, the plan in this guide plus an offline scan is enough. If you do reset, choose Remove everything and Cloud download for a fresh copy of Windows, restore only documents and photos, and reinstall programs from their official sites. Change important passwords from the clean system afterwards.
Why didn't my antivirus stop CrescentCore, OSX/CrescentCore?
New trojan builds are packed and changed often so that signatures do not match, and some are signed with stolen or bought certificates. Many arrive inside password-protected archives, which scanners cannot open until you extract them.
Some downloads also tell the user to turn off the antivirus "because it gives false alarms", a common line in cracked software instructions. Keep real-time protection on, never disable it for an installer, and run the offline scan whenever you suspect something slipped through.
Will Fortect remove CrescentCore, OSX/CrescentCore?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For CrescentCore, OSX/CrescentCore, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Threat Post: Mac Malware Pushed via Google Search Results, Masquerades as Flash Installer (read October 6, 2026)
- Apple Insider: Latest Mac malware in the wild evades security software, researchers (read October 6, 2026)
- Comodo: What Trojan Horse Virus Do? (read October 6, 2026)
- The Economic Times: Definition of 'Piracy' (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)