
Nols ransomware: what it is and how to remove it
Nols ransomware, found and announced by Michael Gillespie on Twitter, is a ransom-demanding malware that is included as the 173d version of the Djvu ransomware family. The acting principle of this malware is the exact same one as used by its previous siblings: infecting > encrypting > ransom-demanding.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Before you restore backups, a full scan can confirm the program that added .nols is gone.
Do it yourself · free Remove Nols ransomware yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Nols ransomware: summary
| Name | Nols ransomware |
|---|---|
| Type | Ransomware virus |
| Family | This notorious cyber threat is the 173d version of the Djvu ransomware family that has been releasing new versions in a very fast speed |
| Appendix | Once files and documents on the victim's computer system are locked by this malware strain, the filenames end up with the .nols appendix added |
| Encryption | Hackers use unique encryption algorithms such as AES, SHA, or RSA to lock up files that are found on the infected computer system |
| Ransom note | The dangerous malware places the _readme.txt ransom message on the Windows computer desktop and also adds the message to every folder that includes encrypted files and documents |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 16 more facts
| Money demands | Criminals demand $490 as the starter price if the money is transferred in a 3-day time limit. However, if users fail to follow this condition, they will have to pay a doubled price to receive the decryption key |
|---|---|
| Altered locations | Malicious payload can be found in the Windows Task Manager and Registry sections. Besides, the ransomware virus can damage the Windows hosts file to prevent users from accessing security-based forums |
| Additional features | .nols file virus might be capable of eliminating Shadow Volume Copies of encrypted data. Also, the malware can carry AZORult trojan as an additional malicious payload |
| Detection names | No Microsoft detection name is known |
| Contact | gorentos@bitmessage.ch, gorentos2@firemail.cc, @datarestore |
| Encrypted file extension | .nols |
| Decryptor | No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates |
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Symptoms | Files renamed with a new extension and a ransom note left in folders |
| Evidence | 5 write-ups by security sites; no sample analysed yet |
| Encrypted files | .nols |
| Attacker contacts | gorentos@bitmessage.ch |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| First seen | 22 October 2019 |
| Facts checked | 6 October 2026 |
What to search your PC and browser for
- File extension:
.nols - Note file:
_readme.txt - Contact:
gorentos@bitmessage.ch
How Nols ransomware behaves
From our report of Oct 2019 · not reviewed since
Nols ransomware - a recently-discovered file-encrypting threat that appears to be the 173d Djvu ransomware variant
Nols ransomware, found and announced by Michael Gillespie on Twitter, is a ransom-demanding malware that is included as the 173d version of the Djvu ransomware family.
The acting principle of this malware is the exact same one as used by its previous siblings: infecting > encrypting > ransom-demanding. Once Nols ransomware infects a particular Windows-based computer, all files, and documents that have been placed on the machine are locked by using unique algorithms such as AES, RSA, or SHA.
Afterward, every component ends up with the .nols appendix near to its filename and the _readme.txt ransom message shows up and urges users to transfer a price of $490-$980. If the victim fails to pay the $490 ransom in 72 hours, the price doubles up and people have to empty their pockets even more.
The creators of Nols virus claim that purchasing the decryption tool from them is the only way to properly recover files and any other options are not available and these people even offer to send them 1 small file for free decryption as evidence that the decryption software truly exists. For this purpose, the victims can make contact via gorentos@bitmessage.ch, gorentos2@firemail.cc, or @datarestore Telegram account.
Nols ransomware can carry a complex module in order to succeed in its tasks at the highest level possible. The malware supposedly damages the Windows hosts file to prevent victims from accessing security-related networks where they might discover handy tips of the malware elimination process or even data recovery.
Note that once you have completed the Nols ransomware removal, ensure that you delete the hosts file too or the access will remain blocked.
Continuously, Nols ransomware possibly alters the Windows Registry and Task Manager and fills these locations with bogus files, keys, and processes. Some of them allow the malware to boot itself automatically within each computer startup process, other entries execute the encryption module, and some might allow the ransomware virus to run suspicious processes in the background, e.g. inject other malicious threats.
It is known that STOP/Djvu ransomware viruses carry the AZORult trojan virus. The same thing is valid for Nols ransomware. Be extremely careful while dealing with this threat and do not postpone its removal process as you might end up with additional malware on your computer system. Trojan horses are capable of stealing credentials, private data, corrupting software, and damaging the entire machine and its components.
Remove Nols ransomware as soon as possible once this malware has been spotted operating on your Windows computer system. software should help you to detect all malware-laden strings on your machine. If you want to search for infection signs on your own, they are very accurate.
All of your filenames will be slightly modified and the components will remain properly inaccessible. Additionally, you will definitely see this ransom note on your computer screen and also placed in every folder that holds encrypted data:
Nols ransomware is a very dangerous malware to deal with and needs to be removed instantly. Afterward, you can start thinking about possible data recovery options.
Even though no official decryption key has been yet released, you can try purchasing DrWeb's Rescue Pack that offers a decryptor and two years of computer protection. Try out the free decryption tool offered by DrWeb experts and if it works for you, you can buy the whole package for $150.
Warning: Do not pay the Nols ransomware developers as you take a big risk of getting scammed.
These people urge for huge prices even up to $1000 for the decryption software that you might lose for absolutely nothing. Nevertheless, the malware might delete Shadow Volume Copies of encrypted files by executing Power Shell commands and hardening the data recovery process for victims themselves.
Besides, if you want to prevent possible future attacks from malware such as Nols ransomware, you should take a look at the below-provided paragraphs on malware distribution and prevention. Besides, thinking of ways to secure valuable files also is a necessity here. You can purchase a portable drive such as USB and store copies of important data there. You can also use services that are provided by iCloud or Dropbox.


From our report of Oct 2019 · not reviewed since
Protection possibilities from ransomware viruses
Due to the increasing number of ransomware infections worldwide, it is very important to know how to protect yourself, your computer system and valuable documents from these dangerous malware attacks.
So, let's get started.
First of all, ensure that you always have a reliable antimalware product installed on your computer system. Purchase only a reliable tool that includes multiple protective features and will ensure your safety 24/7. Additionally, do not forget to update this program when new upgrades are released or the AV tool might not operate properly without proper updating.
Second, manage all of your emails carefully. Delete everything that falls in the spam section and even erase messages from the inbox place if you were not respecting to receive anything similar recently. Besides, do not open any attached files/documents without scanning them with reputable antimalware software.
Furthermore, avoid visiting unprotected sources that might contain malicious data. If you are ever ready to proceed to some type of third-party page but it gives you a concerning feeling, better close the window and never try it again. The same goes for clicking on ads and links - if they look questionable to you, do not enter them.
Last but not least, you should always keep your software and services updated. Hackers aim to release fake product updates and trick users by pushing upgrades through various third-party sources. If you are ever provided with a program update that you were expecting to receive, look it up on the Web and find some user reviews.
From our report of Oct 2019 · not reviewed since
Ransomware payload can be spread via multiple sources
Malicious payload mostly comes camouflaged, however, in different types of ways regarding the situation and technique promoted to infect potential victims.
According to research, cybercriminals usually use these types of methods to infect random people with malware:
- Hacked RDPs. Ransomware developers are known for their ability to hack vulnerable RDP and forcibly enter the administrative password into the computer system. Also, TCP Port 3389 is known as one of the most vulnerable ports.
- Phishing emails. Hackers often pretend to be from reliable shipping companies such as FedEx or DHL and send users messages that include "order confirmation" in the form of a link or attachment but truly is the malicious payload.
- Infected files. Criminals usually use executables, word documents, or similar files to hide the malware in. These components can end up placed on p2p networks, gambling websites, online dating, porn sources, etc. For example, The Pirate Bay that includes proxies worldwide often has the chance of being hacked and filled with malware.
- Other ransomware distribution sources include exploit kits, outdated software, or just fake program updates. The name of Adobe Flash Player is often used for creating fake software updates and tends to trick a big number of users.
The Nols ransomware note
ATTENTION!
Don't worry, you can return all your files!
All your files like photos, databases, documents and other important are encrypted with strongest encryption and unique key.
The only method of recovering files is to purchase decrypt tool and unique key for you.
This software will decrypt all your encrypted files.
What guarantees you have?
You can send one of your encrypted file from your PC and we decrypt it for free.
But we can decrypt only 1 file for free. File must not contain valuable information.
You can get and look video overview decrypt tool:
https://we.tl/t-514KtsAKtH
Price of private key and decrypt software is $980.
Discount 50% available if you contact us first 72 hours, that's price for you is $490.
Please note that you'll never restore your data without payment.
Check your e-mail "Spam" or "Junk" folder if you don't get answer more than 6 hours.
To get this software you need write on our e-mail:
gorentos@bitmessage.ch
Reserve e-mail address to contact us:
gorentos2@firemail.cc
Our Telegram account:
@datarestore
Your personal ID:
How to remove Nols ransomware
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove Nols ransomware and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so Nols ransomware cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
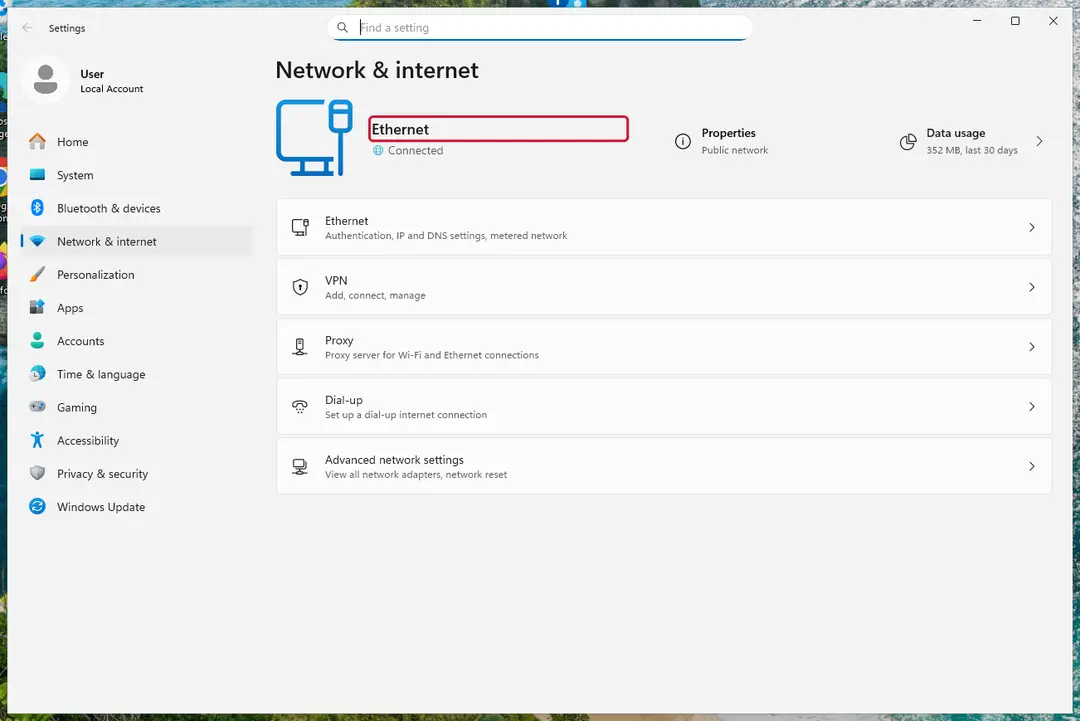
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and confirm the family
Your files now end in
.nolsand the instructions are in_readme.txt. Save both to a USB stick, a copy of the note and two small encrypted files, before anything else.On another device, check them with ID Ransomware or Crypto Sheriff: the family name decides which decryptor, if any, can help. Keep the note's ID and contact line for your report.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for Nols ransomware, no free decryptor is known (checked 6 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing Nols ransomware does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
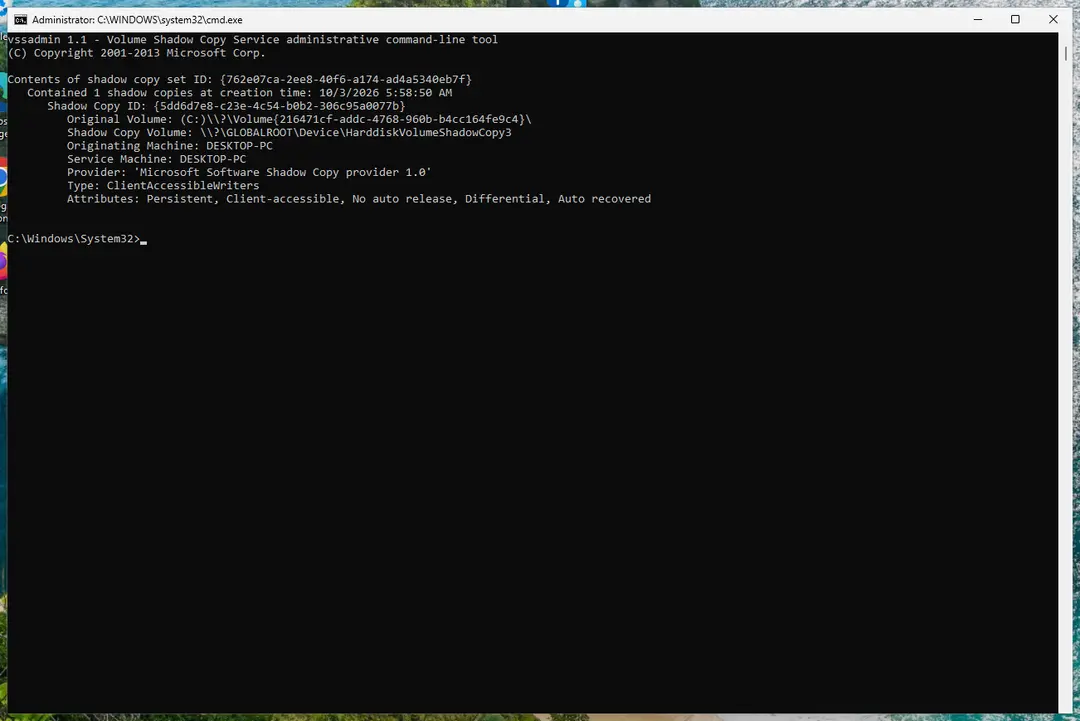
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that Nols ransomware deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Oct 2019 · not reviewed since
Removal instructions for Nols ransomware + file decryption possibilities
Nols ransomware removal can be performed only by employing automatical software.
In addition, you can use the help of , , or for completing a thorough system scan and identifying all malicious strains and activities. After you receive the malware checkup results, you will get a view on what type of locations need ultimate cleaning.
Do not try to remove Nols ransomware on your own as you might miss some crucial objects. According to experts from NoVirus.uk, if you skip any malicious file or process, the ransomware virus might easily renew itself within the next computer boot process. Complete the elimination before you try to restore data, otherwise, files might get repeatedly encrypted.
Even though .nols files virus is currently undecryptable with official software, there are other alternatives that you can try. For example, the DrWeb Rescue Pack that includes file decryption software and two years of antimalware protection. Continuously, below you will also find a few methods that might appear handy to you.
[GI=method-1]Turn on Safe Mode with Networking and disable all malicious modifications that have been brought by the file-encrypting malware to your Windows computer system.
[GI=method-2]Activate System Restore to reverse suspicious changes that have been done by the ransomware virus. Learn how to achieve such a task by completing the following steps.
If you have spotted encrypted, damaged, or just inaccessible files, you can try to recover them by launching this tool.
Using Windows Previous Versions feature might allow you to bring back some individual files.
Make sure that you have enabled System Restore in the past, otherwise, this feature might not be helpful.
Try Shadow Explorer for data recovery.
Employ this software if you want to restore some of your individual data. Note that this method might not work if the virus has eliminated Shadow Volume Copies of your encrypted files.
Currently, no official decryption key has been released for files locked by Nora ransomware. As an alternative, you can try DrWeb's rescue pack that might be capable of decrypting some Djvu ransomware versions.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Make the next attack harmless
Nols ransomware could only hurt the files that had no second copy, and the signs (files that end in .nols and no longer open) showed exactly which ones those were.
The 3-2-1 rule fixes that:
- three copies
- two media
- one disconnected
A practical version for a home PC: OneDrive or another cloud backup with version history, plus an external disk that you plug in once a week for File History and then unplug. Test a restore now and then by opening a few files from the backup on another device.
Details, schedules and what not to back up are in our 3-2-1 backup guide for Windows.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about Nols ransomware
Is there a decryptor for .nols files?
That depends on the family behind the .nols extension, which this guide cannot confirm yet from the reports alone. Check No More Ransom and ID Ransomware with your ransom note and one encrypted file; they list families with free tools.
If none exists today, keep the encrypted files and a copy of the note on a separate drive, because decryptors are sometimes published months later after flaws are found or servers are seized. Never buy a decryptor from a website that is not the security company that made it.
How do I open .nols files?
You cannot open them by renaming or by choosing another program. The .nols ending shows that Nols ransomware encrypted the content, and only the matching key can reverse it. Renaming a file back to .docx or .jpg changes nothing except the icon, and it can confuse a future decryptor, so leave the names as they are.
To get the content back, use a backup, an unencrypted copy elsewhere, or a decryptor listed on No More Ransom if one exists for Nols ransomware. Store the encrypted files on an external disk until then.
How did Nols ransomware get on my computer?
The way Nols ransomware spreads has not been documented yet, so look at your own recent activity. On home PCs, ransomware most often comes with cracked programs, game cheats, key generators and fake updates, or with an e-mail attachment that was opened. On business networks, attackers usually log in through Remote Desktop with a stolen or guessed password.
Think back to what was downloaded or installed in the days before files that end in .nols and no longer open, and check the Downloads folder and Installed apps sorted by date. Keep anything suspicious for your report, but do not run it again.
Should I pay the ransom?
We advise against it, and so do the FBI, Europol and national cyber agencies. Payment does not guarantee a working tool: some attackers never reply, some tools damage files, and some variants have no decryptor at all. Paying also funds further attacks and can make you a target again.
Before considering payment, try every recovery option in this guide and report the attack. Companies must involve their legal adviser and insurer, because payments to sanctioned groups can be illegal. If files are truly irreplaceable, store the encrypted copies and wait; decryptors sometimes appear later.
Can a data-recovery company decrypt my files for a fee?
Only if a decryptor already exists or the company pays the attackers for you. Some "ransomware recovery" services advertise that they can decrypt families with no known flaw; in practice they negotiate with the attackers and add their own fee. Others use the same free tools listed on No More Ransom.
Before you hire anyone, ask in writing how they will recover the files, whether they will contact the attackers and what happens if they fail. A legitimate service answers clearly. If a free decryptor exists for your family, you can run it yourself.
Did Nols ransomware steal my files or passwords?
We do not know yet. Nothing published so far shows data theft by Nols ransomware, but the only confirmed sign is files that end in .nols and no longer open, which says nothing about what happened before. Many current ransomware attacks copy files or run a password stealer first, so it is wise to act as if they did.
From a clean device, change the passwords that were saved in the browsers on this PC, starting with e-mail and banking, sign out of all sessions and turn on two-step verification. Watch bank statements and account activity for the next few weeks.
Is Nols ransomware the same as other ransomware with a similar name?
Not necessarily. Ransomware names come from the file extension, the note or a word in the code, so unrelated families often end up with similar names, and one family can appear under several names. The difference matters: a decryptor or advice for one family does not fit another and can damage files.
Compare the ending added to your files and the exact name of the note with the summary table at the top of this guide, then upload the note and one encrypted file to ID Ransomware from a clean device. If the result names another family, follow the guide for that family instead.
What does _readme.txt tell me about the ransomware?
Quite a lot. The file name _readme.txt, the wording, the contact addresses and the format of the personal ID are typical for each family. Uploading the note together with one encrypted file to ID Ransomware or No More Ransom's Crypto Sheriff usually names the family within seconds.
That name decides your options: some families have free decryptors, some can be partially recovered, and some cannot be decrypted at all. The note's claims about stolen data should be taken seriously but not at face value.
My files got .nols overnight. What happened?
Ransomware often runs at night or when the PC is idle, so the encryption finishes before anyone notices. It usually entered earlier through a cracked program, a fake installer, an e-mail attachment or remote desktop with a weak password.
The .nols extension marks every file it reached. Start by disconnecting the PC from the network, then identify the family from the ransom note and one encrypted file, check for a decryptor, and look for copies in backups and OneDrive before you consider anything else.
Will Fortect remove Nols ransomware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Nols ransomware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Twitter: #STOP #Djvu #Ransomware (read October 6, 2026)
- Wikipedia: Secure Hash Algorithms (read October 6, 2026)
- CISA: StopRansomware (read October 6, 2026)
- No More Ransom (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)