
SettingsModifier:Win32/HostsFileHijack: what the alert means and how to remove it
SettingsModifier:Win32/HostsFileHijack is the name Microsoft Defender gives to suspicious changes in the Windows hosts file, and it is not a program you can uninstall. Read the file's entries to see whether malware or your own blocklist made the change, then let Defender reset it or allow it.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like a Windows Security alert for SettingsModifier:Win32/HostsFileHijack that names the hosts file usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove SettingsModifier:Win32/HostsFileHijack yourself 5 steps, about 15 minutes, no software needed.
Start the steps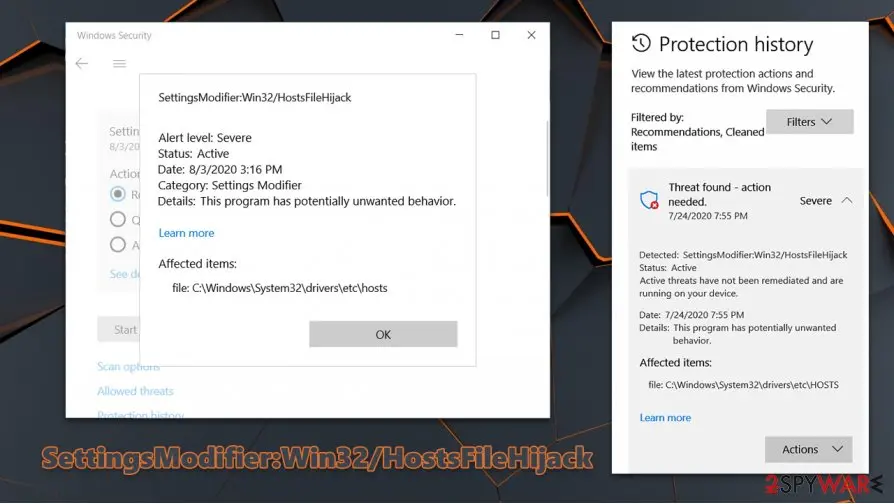
SettingsModifier:Win32/HostsFileHijack: summary
| Type | A Microsoft Defender detection for changed entries in the Windows hosts file; not a program you can uninstall |
|---|---|
| Risk | Medium until you have read the file: malware can use it to block updates or redirect you, but the same alert appears for your own edits |
| Symptoms | The alert, changed entries in the hosts file, and sometimes a failed save with "contains a virus or potentially unwanted software" |
| How to get rid of it | Check the entries, let Defender reset the file, full scan and Defender Offline, Windows Update; allow it only if you made the change |
| Our check (6 October 2026) | Reading Microsoft, BleepingComputer and a forum thread; no sample to run. Not a clearance of any PC |
| First seen | Microsoft entry published 14 January 2020, updated 7 August 2020; alerts widespread from late July 2020 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Detection | Microsoft: SettingsModifier:Win32/HostsFileHijack, no aliases; a settings-change name, not a Trojan:Win32/ program name |
|---|---|
| Not to be confused with | SettingsModifier:Win32/PossibleHostsFileHijack, the Windows 8 era name in Microsoft Support article 2764944 |
| Name | SettingsModifier:Win32/HostsFileHijack |
| Evidence | 0 write-ups by security sites; details still limited |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against the Microsoft Security Intelligence entry, Microsoft Support articles 2764944 and 972034, the Windows Security and startup settings pages, BleepingComputer (3 August 2020) and a Malwarebytes forum thread. We ran no sample and tested no PC; the removal steps follow Microsoft's pages and were not tried on a live infection.
What SettingsModifier:Win32/HostsFileHijack is, and what it is not
SettingsModifier:Win32/HostsFileHijack is not a program and not one virus. It is the name Microsoft Defender Antivirus gives to a change in the Windows hosts file, and the same alert appears when malware makes the change and when you or a privacy tool make it.
- 1
What Microsoft says it flags
Microsoft's entry says the detection "flags suspicious modifications to the Windows hosts file, specifically entries for certain domains used by the operating system and critical services". It lists no aliases, and no file or process name, because the thing detected is a change to one file.
- 2
Why the hosts file matters
Windows uses the hosts file to turn a domain name into an IP address before it asks DNS. Microsoft says a malicious change can "prevent legitimate network connections, such as updates and certificate checks", or send you to a destination an attacker controls, which can end in more malware being downloaded.
- 3
Who may have made the change
Microsoft's advice splits in two. If the change was made without your or your organisation's knowledge, "the entry was likely set by a malware or an attacker". If you meant to make it, Microsoft says the hosts file is not a supported way to manage network connections to Windows devices.
- 4
What our 2020 guide got wrong
It called the name a heuristic and the cause "a computer infection", and said Microsoft treats every hosts file change as severe since July 2020. Microsoft's entry describes entries for certain Microsoft and critical-service domains, not every change. The next chapters correct the rest.
- Shown by
- Microsoft Defender Antivirus, in Windows Security under Virus & threat protection and Protection history
- What it is
- A detection of changed entries in one text file, C:\Windows\System32\drivers\etc\hosts, not a program you can uninstall
- Microsoft entry
- Published 14 January 2020, updated 7 August 2020; no associated aliases
- What Defender does
- Removes the threat, blocks attempts to insert entries for protected domains, and resets the hosts file to default, which deletes every entry in it
- Platform
- Windows. The file and the detection are Windows-only; a Mac or Android phone has a different hosts file and a different alert
- Not the same as
- SettingsModifier:Win32/PossibleHostsFileHijack, the older Windows 8 era detection for the same file (Microsoft Support article 2764944)
What SettingsModifier:Win32/HostsFileHijack does on an infected PC
What we checked on 6 October 2026, and what we could not
There is no site to visit and no sample to run: this is a detection name. We read what Microsoft, BleepingComputer and a Malwarebytes forum thread publish about it, and we ran nothing on a PC.
Our reading of the sources, 6 October 2026
- The detection is realMicrosoft Security Intelligence has an entry for SettingsModifier:Win32/HostsFileHijack, detected by Microsoft Defender Antivirus. A pop-up that shows this name with a phone number or a payment page is a scam, not Defender.
- It is about one fileThe entry names the hosts file at %windir%\system32\drivers\etc\hosts as the only symptom: "Modifications to the hosts file".
- Which domains trigger itMicrosoft names none. BleepingComputer tested on 3 August 2020 and saw it fire on entries for 15 Microsoft names such as telemetry.microsoft.com and watson.microsoft.com; that list may have changed since.
- Whether your alert is malwareThe name cannot tell you. The same text appears for a privacy tool's blocklist and for an attacker's entry; the contents of your own hosts file decide.
- Why it comes backNot documented by Microsoft. A forum thread of 15 August 2020 describes the alert returning after a privacy tool's settings were undone, and the helper advised removing the tool.
- A clean second scanDoes not clear a PC. Defender's reset deletes the entries, so a later scan finds nothing even if a program is still writing them back.
Read your hosts file before you decide Treat the alert as real until you have looked at the entries. This test was reading, not running, so it cannot say your PC is clean, and nothing we read tells how often the alert means malware today.
From the January 2020 entry to Windows 10 support ending
Our guide dates from 28 October 2020. The three pictures are from it and are dated by what they show; the other entries are dated pages.
14 January 2020
Microsoft publishes the entry
Microsoft Security Intelligence first lists SettingsModifier:Win32/HostsFileHijack on 14 January 2020. Windows 8 had an older name for the same check, PossibleHostsFileHijack, which Microsoft Support article 2764944 says could flag a hosts file that users had edited themselves.
24 July 2020
First alert dated in our pictures
A Protection history entry in our report reads "Threat found - action needed", Severe, status Active, affected item C:\Windows\System32\drivers\etc\hosts. BleepingComputer says users began reporting the detection from the end of July.
3 August 2020
BleepingComputer finds the trigger
Adding a blocklist of Microsoft telemetry names to the hosts file made Windows refuse the save with "contains a virus or potentially unwanted software" and raised the alert. Blocking other sites alone did not, in the author's tests. Detections of hosts file hijacks were not new, but this trigger was.
4 August 2020
Allowed and quarantined
Two alerts from our report: an English one dated 8/4/2020 saying the threat was allowed and will not be remediated in the future, and a Spanish one dated 3 August 2020 marked Grave, the Spanish word for Severe.
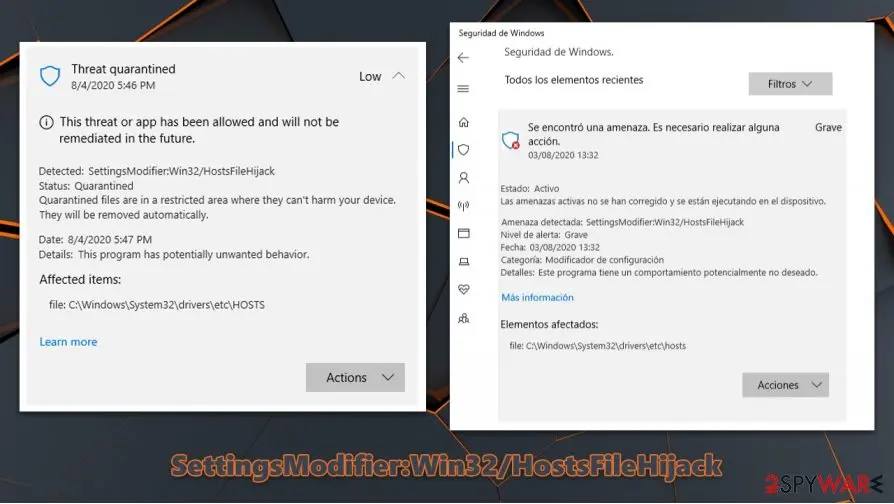
Two alerts from our 2020 report, English on the left and Spanish on the right. The left one shows severity Low because the threat was allowed; the right one shows Grave, which is Severe. Both name the hosts file. 7 August 2020
Microsoft updates its entry
The entry carries this update date. Its current text says Defender resets the hosts file to default when it removes the threat, and that the hosts file is not a supported way to manage Windows connections.
15 August 2020
A forum report of an alert that stays
A Malwarebytes forum user reported repeated Defender alerts. A helper pointed to the privacy tool Spybot Anti-Beacon and said the detection was new but bypassing the hosts file had been discussed since 2006. The thread closed on 31 August 2020 with no result posted.
24 August 2020
Notepad refuses to save
A picture in our report shows Notepad failing with "Operation did not complete successfully because the file contains a virus or potentially unwanted software" after a line mapping www.microsoft.com to 0.0.0.0 was added, next to a Threat removed or restored notification.
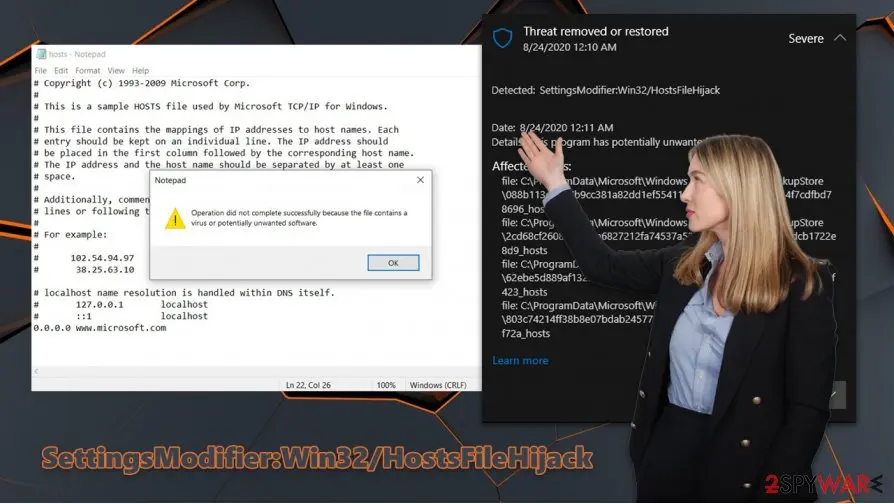
The hosts file open in Notepad with one added line, and the error Windows shows when it is saved. The notification on the right lists copies of the hosts file kept by Windows Security. The woman is a stock-photo model, not a user. 28 October 2020
Our first guide
The 2020 guide called the alert a virus, and told readers to remove it, whitelist it or switch off Windows Defender. Its advice for the false positive was right; its description of the cause was not.
14 October 2025
Windows 10 support ends
Microsoft Support says free updates and security fixes for Windows 10 ended on 14 October 2025. The alert in our pictures is the Windows 10 look; Windows 11 uses the same Windows Security app and the same menus.
Our 2020 claims, checked
The 2020 guide mixed true statements with ones Microsoft's entry does not support. Here is each one against what we read.
| What the 2020 guide said | What the sources say |
|---|---|
| The name is a heuristic detection name | Microsoft calls it a detection that flags suspicious modifications to the hosts file, for entries for certain domains. It does not use the word heuristic and lists no aliases |
| Microsoft treats all modifications as a severe threat since July 2020, whoever makes them | Partly. The alert is Severe in our pictures, and it appeared in late July 2020, but the trigger is entries for protected Microsoft and critical-service domains. BleepingComputer's blocking of other sites did not raise it |
| Telemetry domains named include www.microsoft.com and us.vortex-win.data.microsoft.com | Correct. BleepingComputer's list from 3 August 2020 includes www.microsoft.com, microsoft.com, telemetry.microsoft.com and us.vortex-win.data.microsoft.com among 15 names |
| The malware can prevent connections to Windows update servers | Microsoft says modifications can prevent "legitimate network connections, such as updates and certificate checks" |
| Moss, Lyli and Copa use the hosts file to keep you off security sites | We could not confirm these three. We read no Microsoft or other page about them, so it stays as an old claim, not a finding |
| Defender's Actions > Remove deletes the malware and the modified file and creates a new one | Close. Microsoft says that when it remediates this threat it resets the hosts file to default, removing existing entries |
| If you edited the hosts file yourself, the alert is a false positive | Microsoft says the change is a threat unless you or your organisation made it, and that the hosts file is not a supported way to manage connections. The alert is accurate, even when the cause is harmless |
| Switch off Windows Defender and use other security tools | Not advised. Microsoft says Defender turns itself off when a compatible non-Microsoft antivirus is installed, and that turning real-time protection off leaves downloads unscanned |
What SettingsModifier:Win32/HostsFileHijack can steal or download
What a hijacked hosts file can cost you
Microsoft's entry names the mechanism and not a payload. The consequences below are the ones it describes, plus the ones our 2020 guide listed.
- High
Diverted traffic
Microsoft says an attacker can modify the file "to divert network traffic to a destination controlled by the attacker, resulting in the download of additional malware or other malicious activity". Your bank's or mail provider's name could lead to a look-alike.
- High
Windows cannot update
Microsoft says malicious changes can block updates and certificate checks. The 2020 guide listed the same: stopping Windows Update and certificate checks. A PC that cannot update falls behind on fixes.
- High
Further infections
The 2020 guide said such changes "might be devastating and result in further malware infections". The entry says the redirect can lead to more malware being downloaded.
- Medium
Security sites blocked
The 2020 guide said some malware uses the file to keep you off security sites and make removal harder. We confirmed the general method in Microsoft's entry, not the three families the guide named.
- Medium
Stability problems
The 2020 guide said malware can leave errors, crashes and lag after it is gone. We found no source for this on this detection, so treat it as general.
- Low
Nothing, if it was your own edit
If you added the names yourself, the main loss is that Defender resets the file and removes them. Your blocklist goes with it.
What you may notice, and what the sources say
Microsoft lists one symptom. The 2020 guide listed more, and they are separated here.
| Sign | What we found |
|---|---|
| The alert in Windows Security | The usual sign. Pictures in our report show it as Threat found, Threat quarantined or Threat removed or restored |
| Changed entries in the hosts file | The only symptom Microsoft's entry lists: modifications to the file at %windir%\system32\drivers\etc\hosts |
| A save in Notepad that fails | Seen in BleepingComputer's test and in our 24 August 2020 picture, with the message that the file contains a virus or potentially unwanted software |
| Sites in Chrome, Firefox, Safari or Edge will not open | From the 2020 guide. A blocked name fails in every browser on the PC; Safari does not run on Windows, so that part of the old line cannot apply here |
| Connectivity problems | From the 2020 guide, and the same effect Microsoft describes for blocked connections. They also have many other causes |
How to check the PC for SettingsModifier:Win32/HostsFileHijack
The hosts file in plain words
A short course, because the alert only makes sense once you know what a line in this file does.
- 1
What it is
Microsoft describes the hosts file as a plain-text system file that maps host names such as contoso.com to IP addresses, a standard part of an operating system's IP implementation. Each entry sits on its own line: an IP address, then one or more names, separated by spaces or tabs. Lines that start with # are comments.
- 2
Where it is
At C:\Windows\System32\drivers\etc\hosts, which Microsoft writes as %WinDir%\System32\Drivers\Etc. The file has no extension. BleepingComputer says only a program with administrator rights can edit it.
- 3
What the default holds
Microsoft's default file is only comment lines. Even the localhost lines in it start with #, because localhost is handled inside DNS itself. Any line that does not start with # was added by someone or something.
- 4
Why it still exists
The 2020 guide said the file dates from before DNS was widespread, and that Microsoft keeps it because it still has uses. Microsoft's reset page, updated in 2026, still treats it as a normal part of Windows.
- 5
What a line can do
A line that maps a name to 127.0.0.1 or 0.0.0.0 blocks it, because the PC then asks itself. A line that maps a name to another address sends you there instead. Microsoft names both outcomes as the danger: blocked updates and certificate checks, or traffic diverted to an attacker.
| A line like | What it does | Alert? |
|---|---|---|
| 0.0.0.0 www.microsoft.com | Blocks the name | Yes, on a protected domain (picture of 24 August 2020) |
| 127.0.0.1 ads.example.net | Blocks an ad server | BleepingComputer's tests of other blocked sites did not raise it; ad blocklists use this form |
| 203.0.113.5 yourbank.example | Sends the name to another address | This is the attack Microsoft describes; the address here is a documentation example |
| # any text | A comment, no effect | No |
Your own edit, a tool's, or malware: how to tell
Look at the entries, not at the alert. Open the file read-only first, and write down what is in it before Defender resets it.
- 1
Copy the alert
Open Windows Security > Virus & threat protection > Protection history and take a screenshot of the entry. Note the date and what it says happened: Quarantined, Removed, Allowed or Needs action.
- 2
Open the file as a reader
Press the Windows key, type Notepad, right-click it and choose Run as administrator. In Notepad choose File > Open, paste C:\Windows\System32\drivers\etc\hosts in the box, set the file type to All files and open it. Do not save.
- 3
Copy the entries
Select all, copy, and paste the text into a new document you keep outside the Windows folder. If the Defender reset has already run, the file will show only comment lines and your copy will be of the default, so check Protection history for where the old copy went.
- 4
Read every line that does not start with #
Mark each as one you or a tool added, or one you do not recognise.
| Points to your own edit or a tool | Points to malware |
|---|---|
| Many lines mapping known ad, tracker or Microsoft telemetry names to 0.0.0.0 or 127.0.0.1 | Lines that map banks, shops, search engines, security sites or Windows Update to an address you do not know |
| A privacy or debloat tool is installed and ran recently | You never opened the file and never ran such a tool |
| The alert started in the minutes after you saved the file or applied the tool's setting | The alert began after an attachment, a crack or a bundled installer |
| The same entries return only when the tool runs | Entries return after a reboot with no tool installed, or other symptoms appear |
| Security sites open normally | Security sites will not open, or Windows Update fails |
How the file gets changed
The sources agree that a program with administrator rights has to write to it. They do not agree, because they cannot, on which program.
- 1
You, in Notepad
Adding blocklist lines by hand needs Notepad run as administrator. BleepingComputer reproduced the alert this way.
- 2
A privacy or anti-telemetry tool
The Malwarebytes forum thread of 15 August 2020 points to Spybot Anti-Beacon, and says tools of this kind can trigger the alert by blocking Microsoft telemetry.
- 3
Malware
Microsoft says hosts file tampering is a common malware or attacker technique. The 2020 guide listed spam emails, adware bundles, drive-by downloads, vulnerabilities and cracks or keygens as the ways malware arrives; none of the pages we read ties this detection to one of them.
- 4
An email attachment or a fake update
The 2020 summary row listed spam emails, exploits, vulnerabilities, malicious websites, fake updates and drive-by downloads. They are ways malware arrives, not ways the hosts file is changed, so use them to ask what you opened before the alert.
How to remove SettingsModifier:Win32/HostsFileHijack
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to SettingsModifier:Win32/HostsFileHijack or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever SettingsModifier:Win32/HostsFileHijack installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Deal with the alert on Windows 11 and Windows 10
Do the steps in order and stop when the hosts file holds only what you expect and a scan is clean. We did not run these steps on an infection; they follow Microsoft's pages.
- 1
Finish the check first
Do the steps in the previous chapter before you clean anything: the screenshot and the copy of the entries. The reset cannot be undone from Defender.
- 2
Let Defender clean it
In Windows Security > Virus & threat protection > Protection history open the entry, choose Actions and then the option to remove or clean it. Microsoft says that removing the threat resets the hosts file to default, and that updating definitions and running a full scan may help address remnant artefacts.
- 3
Run a full scan
In Virus & threat protection > Scan options choose Full scan and Scan now.
- 4
Run a Microsoft Defender Offline scan
In Scan options choose Microsoft Defender Antivirus (offline scan) and Scan now. Microsoft says it restarts the PC and scans in the Windows Recovery Environment without loading Windows, so persistent malware has a harder time hiding.
- 5
If Defender cannot finish, use Safe Mode
The 2020 guide advised Safe Mode with Networking when the threat interferes with the security software. Open Settings > System > Recovery, choose Restart now next to Advanced startup, then Troubleshoot > Advanced options > Startup Settings > Restart and press 5. Microsoft says Safe Mode starts Windows with a limited set of files and drivers, and that Safe Mode with Networking adds the network drivers.
- 6
Install Windows updates
Open Settings > Windows Update. A hijacked file may have kept Windows from updating, so check that updates can run now.
- 7
Ask a second scanner
The 2020 guide told readers to check the PC with other security software if malware is suspected, and noted that no security app catches everything, so repeated scans with different tools can help. Keep one product's real-time protection on and run the other on demand.
- 8
Put back what is yours
If you edited the file yourself, read the chapter on editing the file yourself before you paste anything back.
- 9
Reset the file by hand only if needed
Microsoft's reset steps for Windows 11 and 10: save the default text as a file called hosts with no extension, rename the existing file to Hosts.old in %WinDir%\System32\Drivers\Etc, and copy the new file in. Approve the administrator prompt.
Never download a removal program because a pop-up or a stranger tells you to. A real Defender alert does not show a phone number or a payment page.
If you edited the hosts file yourself
The 2020 guide called this case a false positive and gave three ways out. They are kept here, with what each costs.
| Option | What it does | What it costs |
|---|---|---|
| Let Defender reset the file | Deletes your entries and leaves Microsoft's default | You lose the list. The 2020 guide noted that many readers were unhappy because their blocklists for ad-filled sites were deleted, and that the alert came back when the tool rewrote them |
| Allow the threat | Windows Security takes no action on threats you have allowed, and your entries stay | BleepingComputer warns this may allow every hosts modification from now on, including a malicious one. Allow only if you fully understand the risk |
| Add the hosts file as an exclusion | Microsoft's article 2764944 uses this for the older PossibleHostsFileHijack on Windows 8 | Microsoft says exclusions apply to real-time scanning only, so scheduled scans may still flag the file |
| Stop using the hosts file for this | Microsoft says it is not a supported way to manage connections to Windows devices and points to its documentation of supported methods | Telemetry settings in Windows may be less complete than a blocklist |
| Turn off Defender and use other security tools | Our 2020 guide listed this | Not advised: unscanned downloads while it is off. Defender turns itself off anyway when a compatible non-Microsoft antivirus is installed |
- 1
To allow it
In Protection history open the entry, choose Actions and then the option to allow it on the device (menu wording differs between Windows builds). Allowed items are listed under Virus & threat protection > Allowed threats.
- 2
To undo it
In Allowed threats select the item and choose Don't allow. Microsoft says Windows Security will act on it again the next time it sees it.
- 3
If you are sure it is a false positive
The 2020 guide said that when you are sure, allowing the detection lets the entries stay and stops the file being deleted. That is accurate, and it also leaves the file open to a real attack, so keep a copy of the entries you trust.
Names BleepingComputer saw flagged on 3 August 2020 (15 of them)
- www.microsoft.com
- microsoft.com
- telemetry.microsoft.com
- wns.notify.windows.com.akadns.net
- v10-win.vortex.data.microsoft.com.akadns.net
- us.vortex-win.data.microsoft.com
- us-v10.events.data.microsoft.com
- urs.microsoft.com.nsatc.net
- watson.telemetry.microsoft.com
- watson.ppe.telemetry.microsoft.com
- vsgallery.com
- watson.live.com
- watson.microsoft.com
- telemetry.remoteapp.windowsazure.com
- telemetry.urs.microsoft.com
From BleepingComputer's test of 3 August 2020. Microsoft publishes no list, so entries for other names may also trigger the alert.
After removal: passwords, accounts and prevention
Your passwords after SettingsModifier:Win32/HostsFileHijack
Removing SettingsModifier:Win32/HostsFileHijack does not undo what it may already have sent out while the PC showed A Windows Security alert for SettingsModifier:Win32/HostsFileHijack that names the hosts file in the list of installed apps. Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
If it was malware: what to do about your accounts
The scans deal with the PC. These steps deal with what a redirect could have seen while the file was changed.
- 1
Change passwords from another device
Email first, then banking, then everything else. Turn on two-step sign-in. A hosts file that sends a bank name to another address can feed a fake login page.
- 2
Sign out everywhere
Use the sign out of all sessions option in your Google, Microsoft and social accounts.
- 3
Check your money
Look at card statements and wallets for payments you did not make.
- 4
Look for programs you did not install
Open Settings > Apps > Installed apps and uninstall programs you do not know.
- 5
Scan again in a week
Run another full scan and a Defender Offline scan a week later and keep the first alert's screenshot.
Keep the hosts file and the PC safe
The 2020 tips, with what changed since.
Do
- Keep Microsoft Defender or another single security product updated, with real-time protection on.
- Install Windows updates and updates for your apps when they are offered.
- Use strong passwords, a different one for every account, and two-step sign-in where it exists.
- Use a standard Windows account for daily work. BleepingComputer says only a program with administrator rights can edit the hosts file, so a silent change then needs your approval.
- Be careful with email: addresses can be spoofed, so handle links and attachments with caution.
- Choose Advanced or Custom install in a program's installer and untick what you did not ask for.
- Keep a backup on a disk you unplug, such as File History or OneDrive, so that one infection cannot take the only copy.
Don't
- Do not open an attachment that asks you to enable macros.
- Do not run cracks, keygens or pirated installers; the 2020 guide named them as a route for malware.
- Do not add Microsoft telemetry names to the hosts file; Microsoft says it is not a supported way to manage connections.
- Do not allow the alert if you do not know who changed the file.
- Do not run two antivirus programs with live protection at once.
- Do not call a number shown in an alert.
Questions about SettingsModifier:Win32/HostsFileHijack
What is SettingsModifier:Win32/HostsFileHijack?
It is the name Microsoft Defender Antivirus gives to suspicious changes in the Windows hosts file, not a program. Microsoft's entry says the detection flags modifications to entries for certain domains used by the operating system and critical services. It lists no aliases and no file or process, because the thing detected is a change to one file at C:\Windows\System32\drivers\etc\hosts.
The same alert appears when malware edits the file and when you or a privacy tool add blocklist lines. So the name alone does not say whether you have an infection; the lines in your hosts file do. Open it read-only before you let Defender clean it.
Is SettingsModifier:Win32/HostsFileHijack a virus?
Not by itself. Microsoft says that if the change was made without your or your organisation's knowledge, the entry was likely set by malware or an attacker, so the alert can point to a real infection. If you or a tool added the lines, the detection is accurate but the cause is harmless.
Our 2020 guide called it a computer infection, and this page corrects that. Decide by reading the file: lines that send banks, security sites or Windows Update elsewhere are a warning sign; blocklists of ad or telemetry names that you installed are not. A quiet scan afterwards does not settle it, because the reset removes the entries.
Why did Windows Defender suddenly detect my hosts file?
Because Microsoft began flagging entries for its own domains in late July 2020. BleepingComputer reported on 3 August 2020 that adding a blocklist of Microsoft telemetry names to the hosts file raised the alert at once, and that Windows refused to save the file. Blocking other sites in its tests did not.
Detection of hosts file hijacks was not new, but entries for Microsoft's servers were. If your alert began after you or a tool such as a privacy or debloat program edited the file, that edit is the likely cause. If you never touched it, treat it as malware and follow the removal steps.
How do I remove SettingsModifier:Win32/HostsFileHijack?
Let Defender remove it, then scan. Open Windows Security, go to Virus and threat protection, then Protection history, open the entry, choose Actions and the option to remove it. Microsoft says this resets the hosts file to default, so copy any entries you want to keep first.
Then run a Full scan and a Microsoft Defender Offline scan, and install Windows updates. If Defender cannot finish, start Windows in Safe Mode with Networking, as our 2020 guide advised, and scan from there. Do not install a cleaner because a pop-up says so; Defender and Windows' own tools are enough for this alert.
Is it a false positive if I edited the hosts file myself?
Microsoft treats it as a threat anyway. Its entry says that if the change was intended, the hosts file is not a supported method for managing network connections to Windows devices. Our 2020 guide called it a false positive, and it is one in the sense that no malware is involved.
To keep your entries you can allow the threat in Protection history, but BleepingComputer warns that this may allow every later hosts file change, including a malicious one. Exclusions help less than they seem: Microsoft says they apply to real-time scanning only, so scheduled scans may still flag the file.
How do I stop Defender deleting my hosts file entries?
You can allow the detection, but it has a cost. In Protection history open the alert, choose Actions and Allow on device, and Windows Security will take no action on it, so your lines stay.
The cost, as BleepingComputer says, is that it may let all later hosts file changes through, even malicious ones, so keep a copy of the entries you trust and read the file now and then.
To undo it open Allowed threats and choose Don't allow. A different route is to stop using the hosts file for Microsoft names, since Microsoft says it is not a supported method.
Why does the detection keep coming back after I remove it?
Something is writing the entries again. Defender's reset only deletes what is in the file; it does not stop a program from adding the lines at its next run. A Malwarebytes forum thread of 15 August 2020 describes this: the alert continued after the user undid a privacy tool's settings, and the helper advised removing the tool for good.
Check what is installed and what runs at startup, including Task Manager's Startup apps and Task Scheduler. If you have no such tool and the entries return after a restart, scan with Defender Offline and a second scanner and treat it as malware.
Can I fix it without Windows Defender?
Yes, you can reset the file by hand, but scanning still needs a security product.
Microsoft's steps for Windows 11 and 10 are to open Notepad, paste the default text, which is only comment lines, save it as a file named hosts with no extension, rename the existing file to Hosts.old in the Etc folder and copy the new one in, approving the administrator prompt.
Our 2020 guide suggested turning Defender off and using other tools; Microsoft says Defender switches itself off when a compatible non-Microsoft antivirus is installed. Switching it off by hand leaves downloads unscanned.
Does this mean my PC was hacked?
Not necessarily. Microsoft says a change made without your knowledge was likely set by malware, but it publishes no figures for how often that is the case, and we found none. Many 2020 reports came from people who added Microsoft telemetry names to the file.
Check the entries first. If you find lines you do not recognise, pointing banks, security sites or Windows Update to an address you do not know, run the full scan and the Offline scan, change your passwords from another device and watch your statements.
If you find only lines you or a tool added, the PC was not hijacked by this alert.
Will Fortect remove SettingsModifier:Win32/HostsFileHijack?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For SettingsModifier:Win32/HostsFileHijack, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft Security Intelligence: SettingsModifier:Win32/HostsFileHijack (published 14 Jan 2020, updated 7 Aug 2020) (read October 6, 2026)
- Microsoft Support: Hosts file is detected as malware in Windows Defender (2764944) (read October 6, 2026)
- Microsoft Support: How to reset the Hosts file back to the default (972034) (read October 6, 2026)
- Microsoft Support: Virus and threat protection in the Windows Security app (read October 6, 2026)
- Microsoft Support: Windows startup settings (Safe Mode, Windows 10 support end) (read October 6, 2026)
- BleepingComputer: Windows 10: HOSTS file blocking telemetry is now flagged as a risk (3 Aug 2020) (read October 6, 2026)
- Malwarebytes Forums: Defender HostFileHijack notifications (15 Aug 2020) (read October 6, 2026)