
.Shit ransomware virus: what it is and how to remove it
PC security experts have been widely discussing the popularity of Locky virus. According to them, this ransomware has just switched to .Shit file extension that has been used to block victims' files.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
A free scan checks for the encryptor still on the PC; it does not decrypt .shit files.
Do it yourself · free Remove .Shit ransomware virus yourself 6 steps, about 18 minutes, no software needed.
Start the steps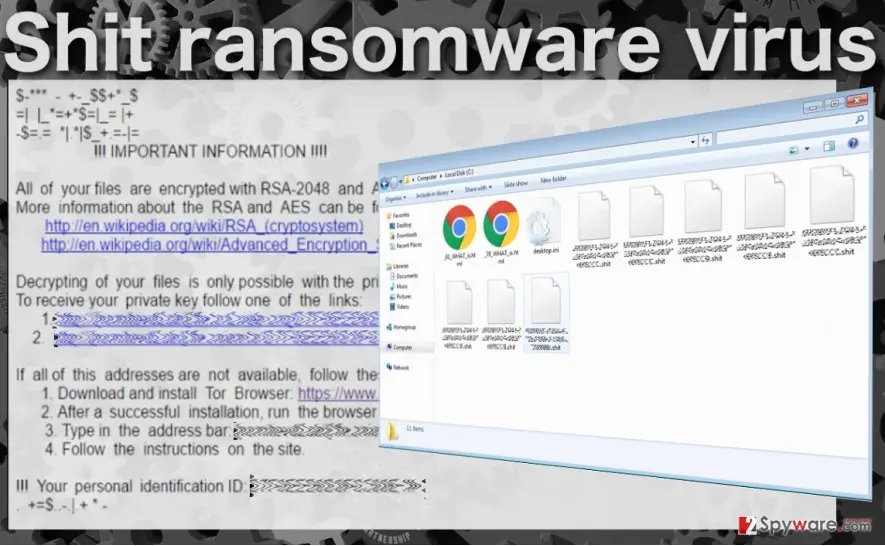
.Shit ransomware virus: summary
| Detection names | No Microsoft detection name is known |
|---|---|
| Ransom note | Not recorded in our earlier report |
| Contact | Not recorded in our earlier report |
| Encrypted file extension | .shit |
| Decryptor | No free decryptor is known for this variant; check No More Ransom (nomoreransom.org) for updates |
| Distribution | Not recorded in the old report |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Damage | Not recorded in the old report |
|---|---|
| Name | .Shit ransomware virus |
| Type | File-encrypting ransomware |
| Symptoms | Files renamed with a new extension |
| Evidence | One write-up by a security site; details still limited |
| Encrypted files | .shit |
| Free decryptor | No free decryptor is known (checked 6 October 2026) |
| First seen | 2 November 2016 |
| Facts checked | 6 October 2026 |
Traces of .Shit ransomware virus you can check
- File extension:
.shit
How .Shit ransomware virus behaves
From our report of Nov 2016 · not reviewed since
.Shit file extension virus - new ransomware hailing from the family of Locky virus
PC security experts have been widely discussing the popularity of Locky virus.
According to them, this ransomware has just switched to .Shit file extension that has been used to block victims' files. Additional steps used by Shit ransomware are still the same - victim is informed about the encryption of the most valuable files and then asked to pay the ransom in exchange for the special decryption key.
There is no doubt that this virus is just another extension of the notorious ransomware which has already released ODIN and Zepto versions before. Shit virus has been first spotted in France where it was spreading via spam emails as an attachment file labeled Receipt.
Nevertheless, if you live in some other country, we do not advise letting your guard down either. Due to its active distribution, .Shit malware is very likely to spread to other parts of Europe and, eventually, the rest of the world.
Although the .Shit virus does not sound like an especially sophisticated cyber infection, trust us -- it is not a work of amateurs. This parasite is well capable of inflicting serious damage on the PC, similarly to Locky and other ransomware viruses.
In fact, its creators seem to have taken the best they could from the category of these particular infections: they have implemented the malware with a military grade AES CBC 256-bit encryption capability which allows locking the infected computer files without leaving their owners any chance of recovery. The same cipher has been used by Locky, ODIN and a bunch of other advanced ransomware before.
Besides, following their lead, this virus also changes the located file names to a random row of characters and pins the controversial .Shit extension to all of the encrypted files. This extension is exactly what earned the virus its nasty name. Though it is practically impossible to restore personal documents after the attack of this malware, by no means should you simply leave it be.
If you want to continue using your computer safely in the future, you must remove SHIT ransomware virus from the system completely. You can use professional antivirus utilities like to do that. When the removal is done, you may still have a chance to recover at least a small portion of your files.
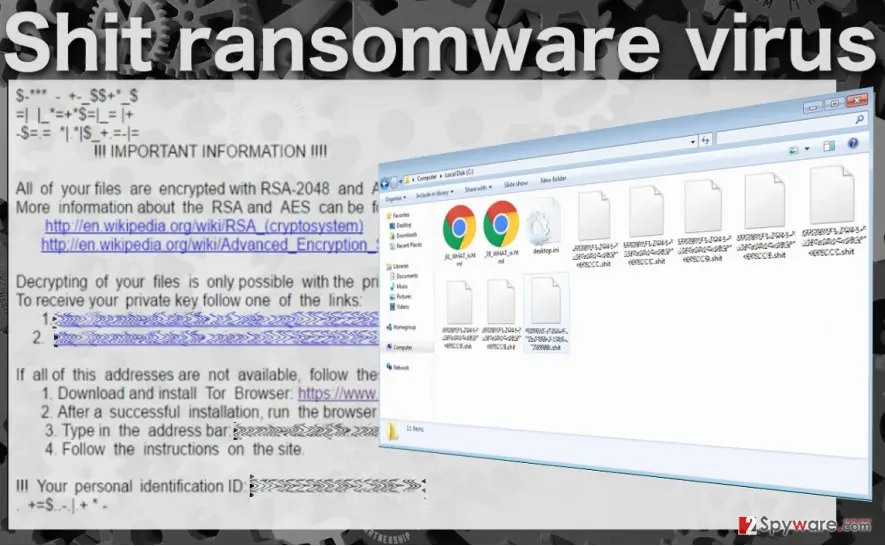
There are plenty of features of this ransomware that help classify it as a member of the Locky family. Not only does it offer to decrypt your files using the notorious Locky Decrypter, but it also drops three types of files on the infected computer:
- _WHAT_is.html
- _[2_random_numbers]_WHAT_is.html
- _WHAT_is.bmp
Similar variants of these files can be found in other virus versions as well. Though the file titles may differ, they usually feature the same ransom note and instructions for the data retrieval. Of course, details such as links to the payment sites, identification numbers or the amount of ransom usually vary with each individual version.
Shit ransomware currently demands 0,5 Bitcoin (around 326 USD) for the data decryption, but you should not even consider paying up. This virus is relatively new, so there is no way of knowing whether its creators are really willing to decrypt your files, or will they simply disappear as soon as your money is in their pockets.
A safer option is to head straight to the Shit virus removal when you first notice the warning signs suggesting it might have infected your PC. After you can check our recommendations for data recovery provided below the article.
From our report of Nov 2016 · not reviewed since
Distribution methods used by this ransomware
Just like Locky and its versions, .Shit ransomware virus is mostly distributed via malicious spam campaigns, possibly the ones that distribute the original infection.
The virus usually comes into their potential victim's inboxes as JavaScript or WS attachments which the users unknowingly download believing that they contain invoice information, speeding ticket, online shopping confirmations or official letters. Opening such emails activate the malicious script which downloads the virus on the computer and it can start encrypting files.
You should also make sure you update your software via reputable sources and avoid downloading software updated from unsafe pages or pop-ups that might randomly emerge while browsing the web. It is likely that you will find .Shit ransomware in a few of these.
How to remove .Shit ransomware virus
Tools you'll need
All of these are free except where noted. Download them on a clean device if the infected PC is offline.
- A USB stick: to keep the ransom note, two or three encrypted files and screenshots off the infected PC.
- Microsoft Defender Offline: built into Windows 11 and Windows 10; scans before Windows starts, so running malware cannot hide.
- Microsoft Safety Scanner: a second, portable scanner with current signatures; each download works for 10 days.
- ID Ransomware: identifies the family from the note and one encrypted file and says whether a decryptor exists.
- No More Ransom: the free decryptors from police and security companies; check it again every few months.
- Fortect (optional): scans Windows for malware and repairs the system files and settings it damaged. The free scan is in the box above.
How to remove .Shit ransomware virus and get your files back
Work in this order.
Disconnecting comes first, removal comes before any restore, and nothing here asks you to contact the attackers.
Step 1: Disconnect the PC and unplug backup drives
Unplug the network cable or turn off Wi-Fi, and disconnect USB drives, external disks and network shares, so .Shit ransomware virus cannot reach more files. Pause OneDrive, Google Drive or Dropbox sync, because synced folders upload the encrypted copies over the good ones.
Leave the PC on but offline while you read the next steps, since a restart can let the ransomware run again. This applies to Windows 11 and Windows 10 alike.
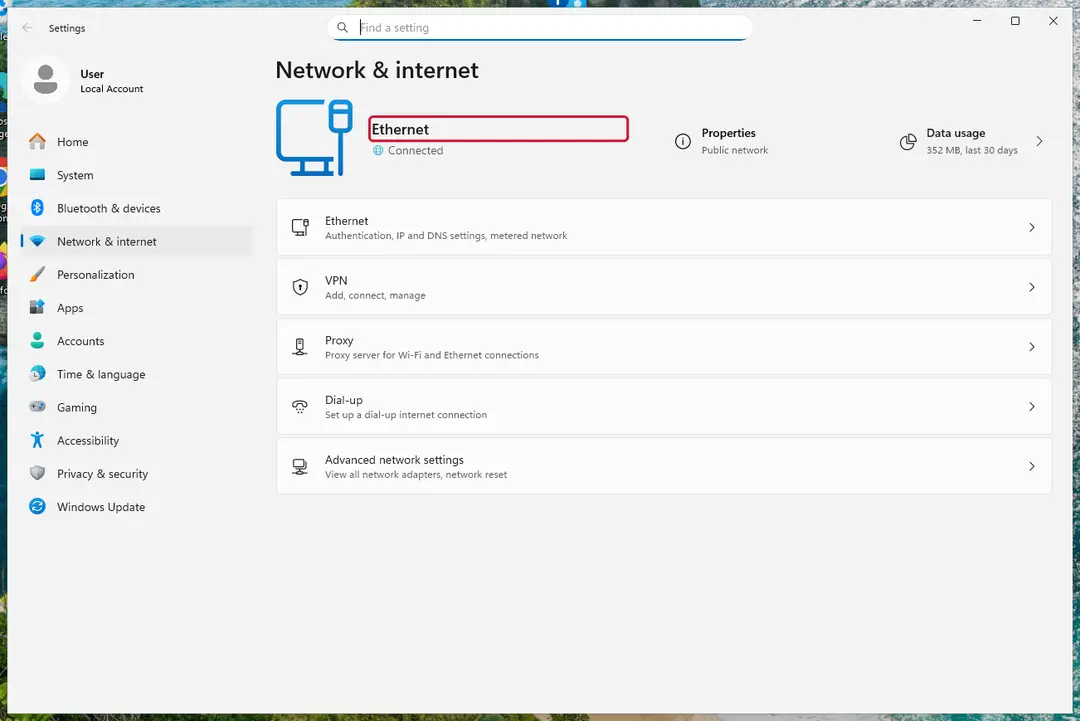
Windows 11: turn off Wi-Fi to take the PC offline. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 2: Save the ransom note and identify the family
The name of the family decides whether a free decryptor can help. Copy the ransom note and two small encrypted files to a USB stick, and check them on another device with ID Ransomware or Crypto Sheriff.
Note the extension added to the files, the contact address and the victim ID shown in the note. Keep the originals on the Windows 11 or Windows 10 PC untouched.
Windows 11: the ransom note and encrypted files to copy for identification. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 3: Check for a free decryptor
Our last check found that for .Shit ransomware virus, no free decryptor is known (checked 6 October 2026). Look again yourself in the No More Ransom list and the free decryptor pages of Emsisoft, Avast and Kaspersky, which add new families every year.
A decryptor needs the ransomware gone first, or it encrypts the files again. Keep at least one copy of the encrypted files on an external drive, even if no tool works yet.
Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 4: Remove the ransomware before you restore or decrypt
Removing .Shit ransomware virus does not bring the files back, but it has to come first. Start with Defender's Full scan, then the offline scan from the same Scan options page, which checks the disk before Windows loads.
If the scan cannot start, use Safe Mode with Networking. Delete the ransom notes only after you have saved a copy, because removal tools sometimes leave them behind on Windows 11 and Windows 10.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Look for shadow copies of the files
Windows keeps shadow copies for restore points and backups, and some ransomware fails to delete them.
vssadmin list shadowsin an administrator Command Prompt tells you at once whether any exist.If they do, right-click the folder that held your files, open Properties > Previous Versions, select a version from before the attack, and click Open to check it before you Restore or copy the files out. Windows 11 and Windows 10 both have the tab.
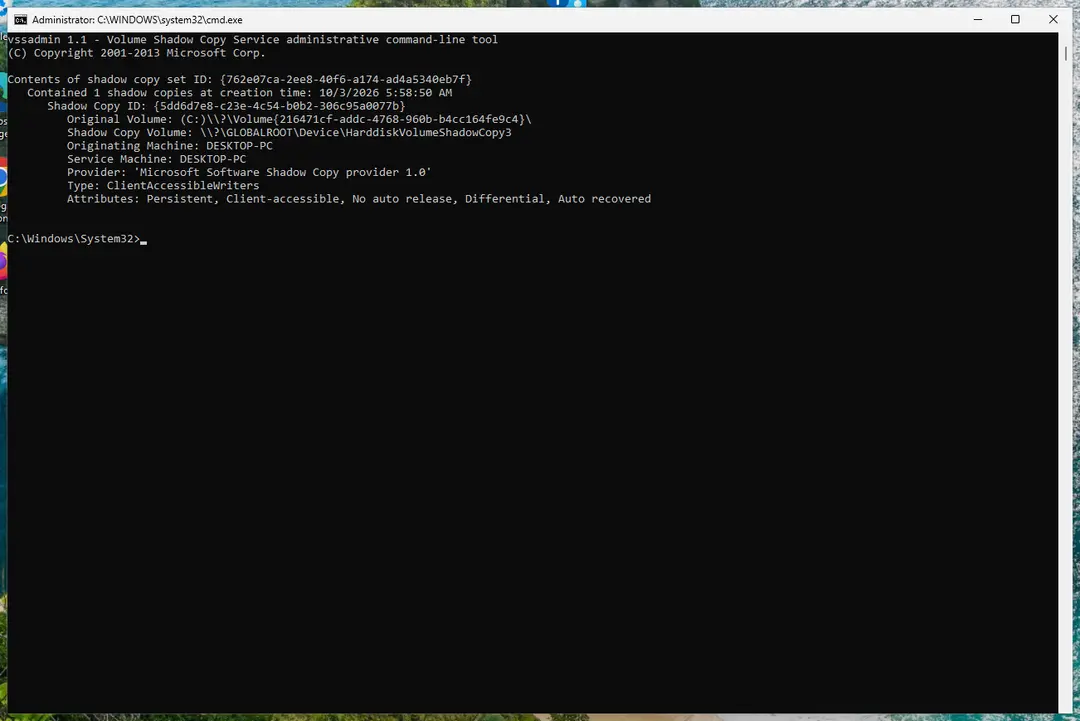
Windows 11: vssadmin list shadows shows whether shadow copies exist. Full procedure with screenshots: Ransomware: first steps, finding a decryptor and recovering files
Step 6: Restore the files from a backup or recover deleted originals
A backup made before the attack is the surest way back. Connect it only once the PC is clean, then restore from File History, Windows Backup, OneDrive's Restore your OneDrive or your own external copies.
Without a backup, try file recovery: the originals that .Shit ransomware virus deleted may still be on the disk until something overwrites them. Install nothing new on the drive you want to recover from on the Windows 11 or Windows 10 PC.
Full procedure with screenshots: Recover deleted files (Recycle Bin, backups, OneDrive) On uGetFix
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.
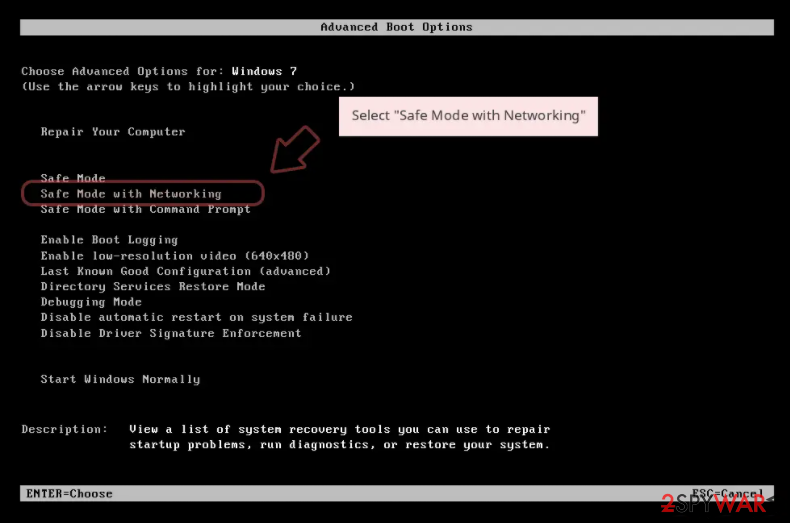
Windows 10 / Windows 8
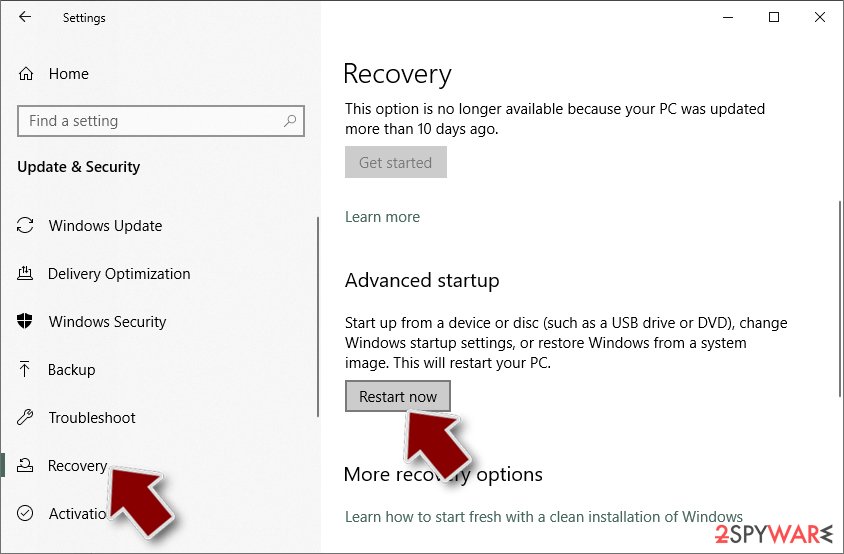
- Right-click on Start button and select Settings.
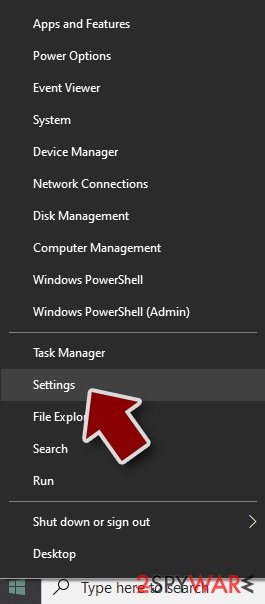
- Scroll down to pick Update & Security.
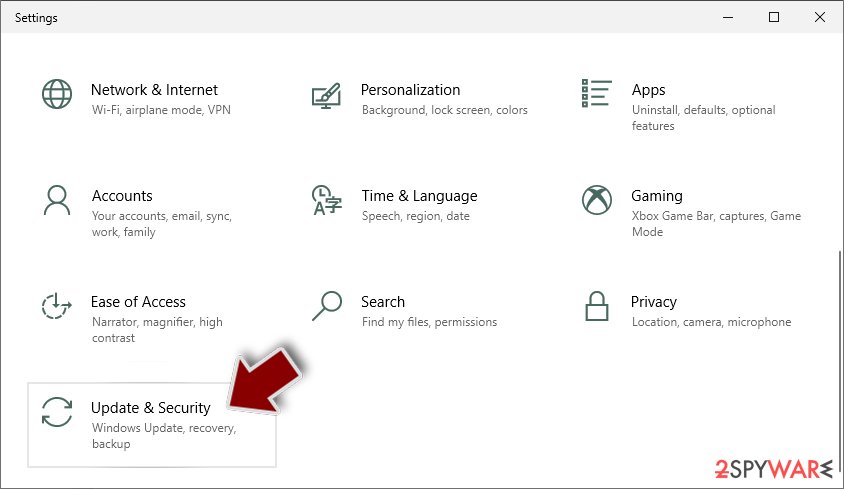
- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.
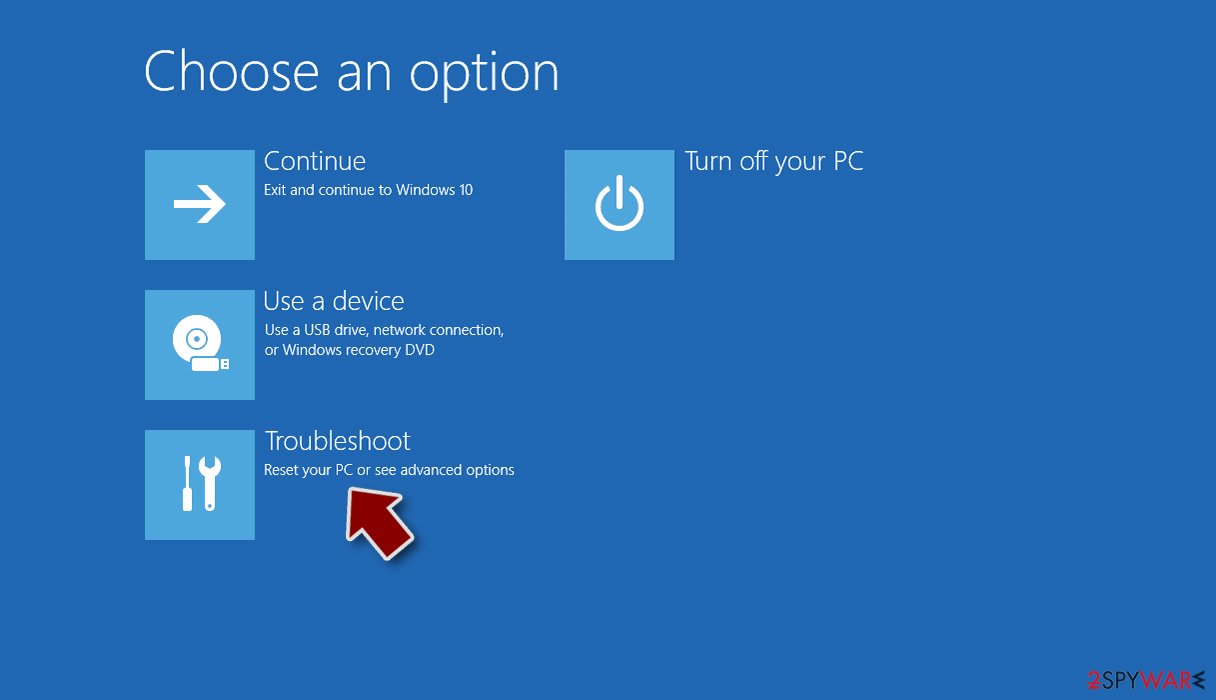
- Select Troubleshoot.
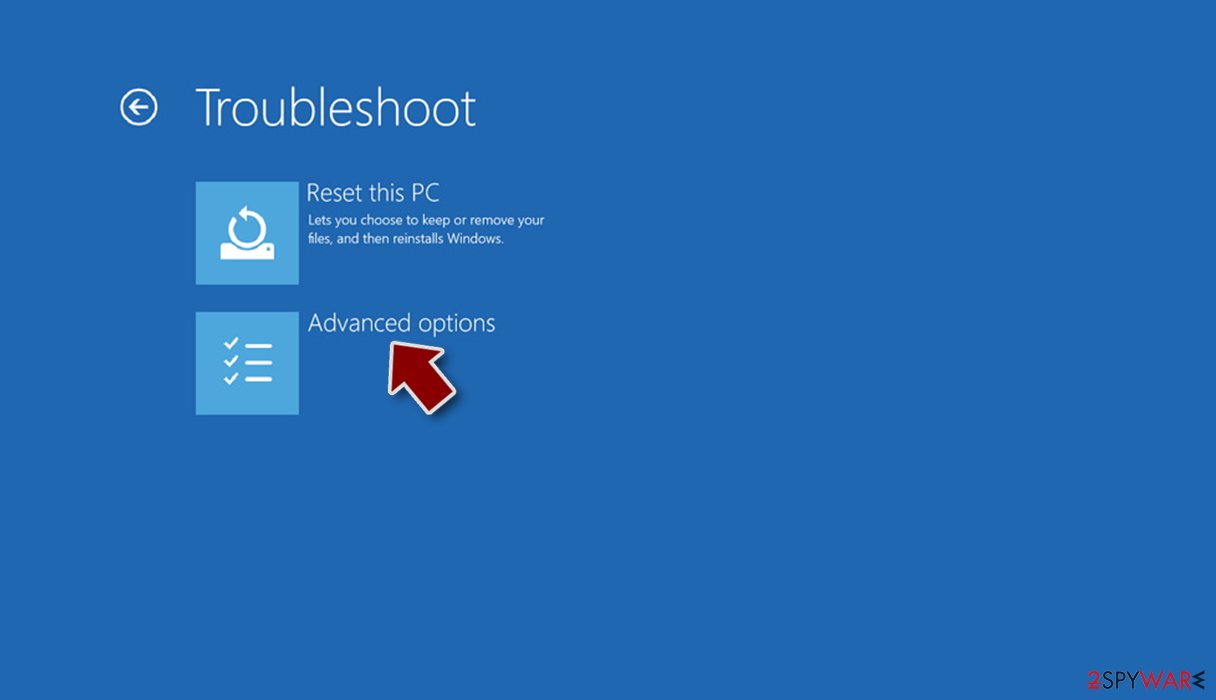
- Go to Advanced options.
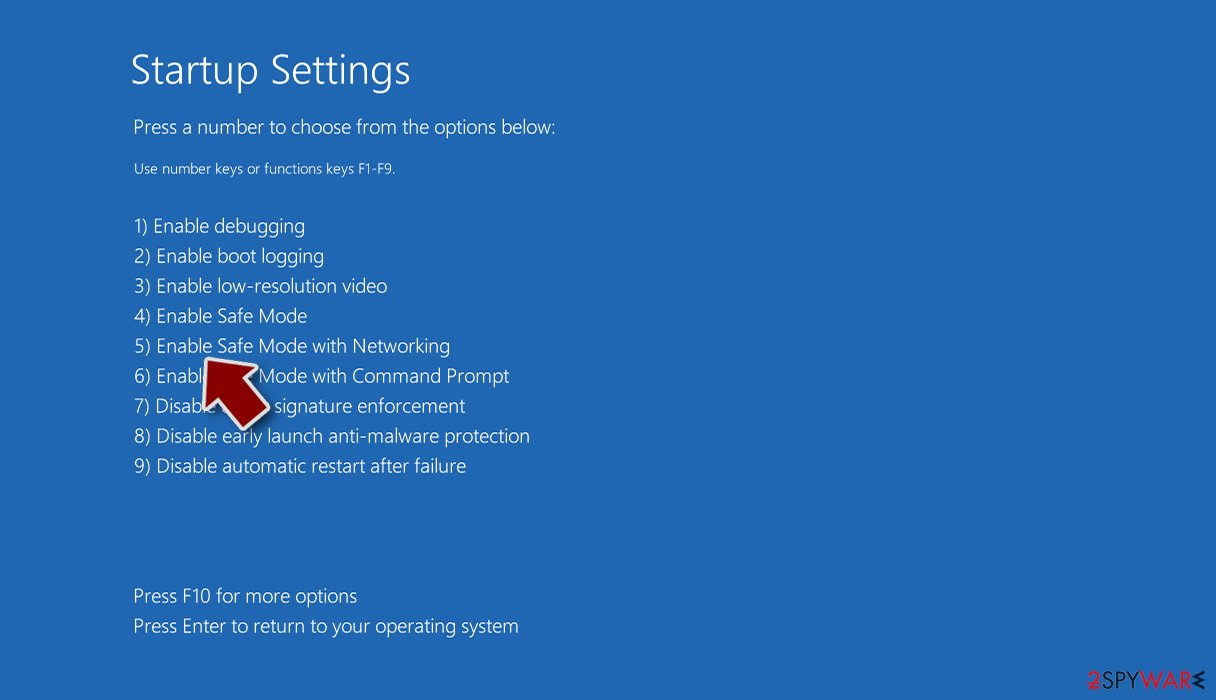
- Select Startup Settings.
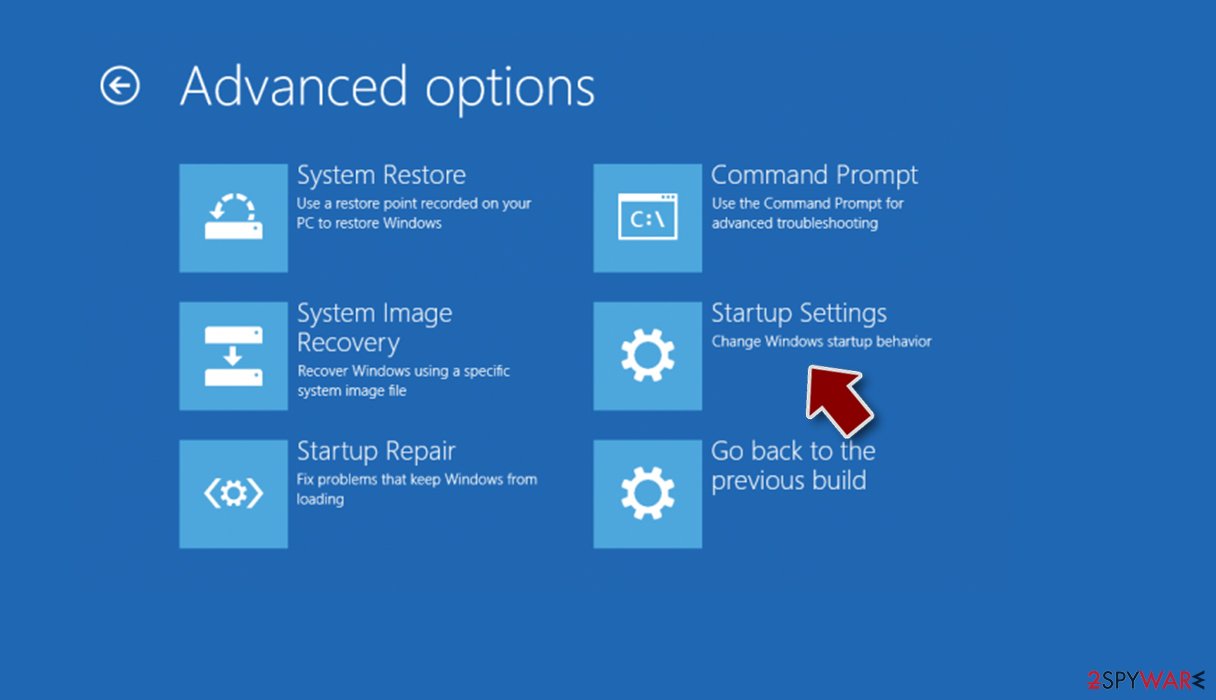
- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.
Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
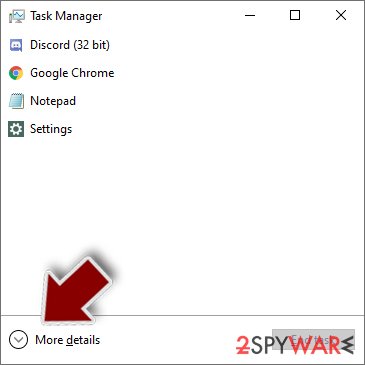
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.
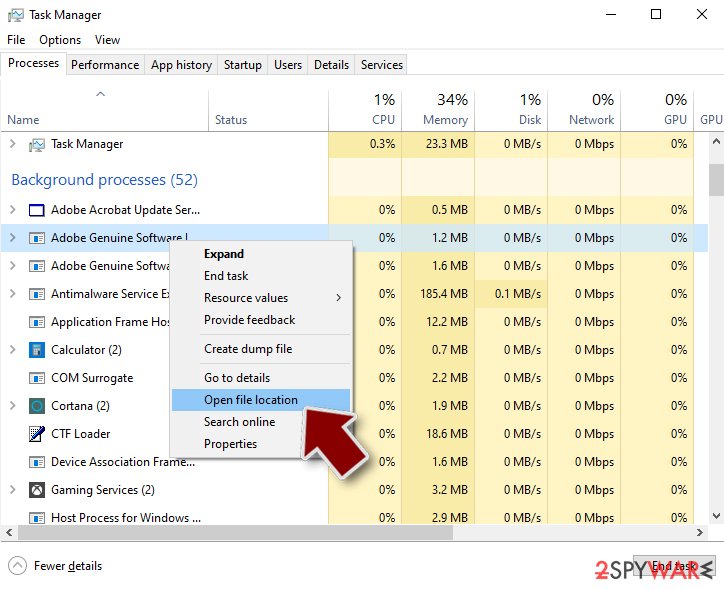
- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.
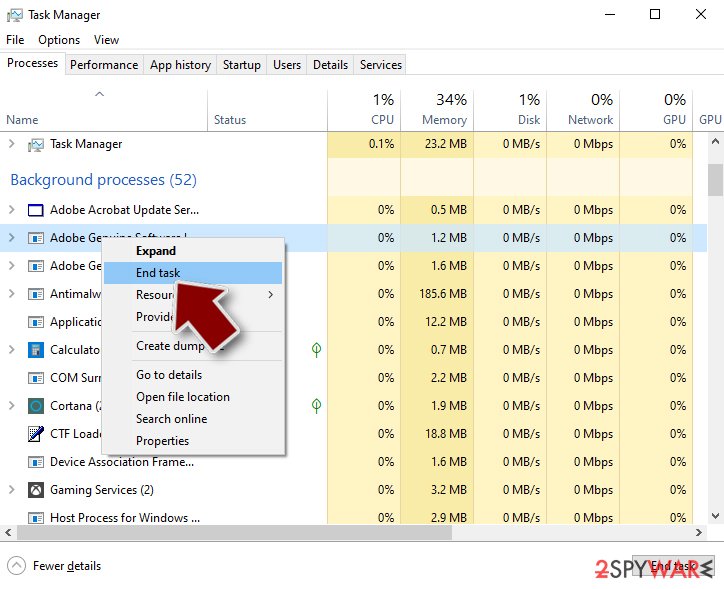
- Go back to the process, right-click and pick End Task.
- Delete the contents of the malicious folder.
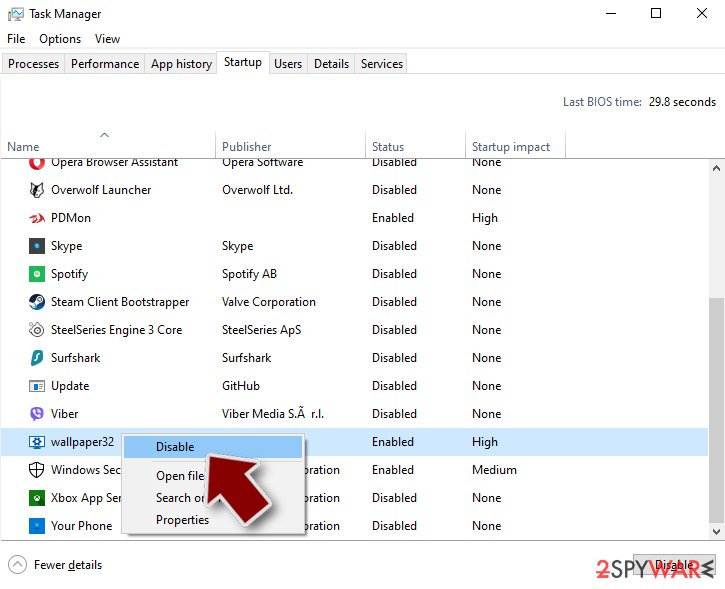
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.
Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.
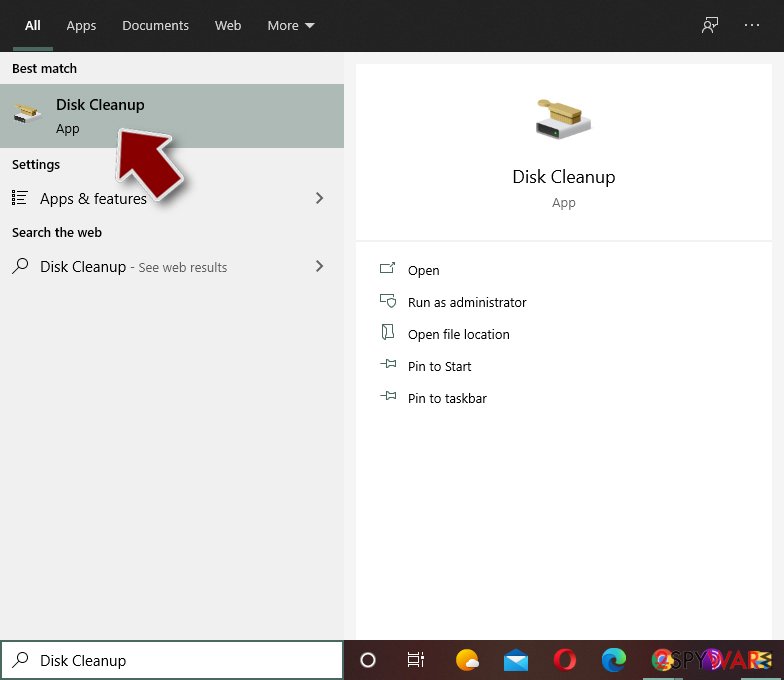
- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
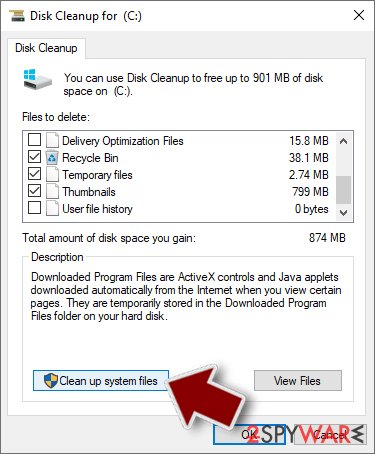
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.
- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
From our report of Nov 2016 · not reviewed since
Tips on .Shit ransomware removal
If you are worrying that you might not be able to remove .Shit ransomware from your computer yourself, we have some good news for you.
We have prepared instructions that will gradually lead you from the initial steps of the .Shit virus removal to the data recovery. The first thing you need to do is test your antivirus, whether the virus does not block its processes. If it doesn't -- just run a full system scan and remove Shit virus from your PC.
Below, you will also find a couple of file recovery tips you can use to try retrieving your data after the virus elimination. Though it will probably won't help you get all of the lost data back, you might still be able to recover at least some of the documents.
Data recovery using Windows Previous Versions feature
This method is not an answer to all of your problems, but it may help you recover important files in case of emergency. What you should note is that you should have the System Restore feature enabled pre-attack; otherwise, this method will prove useless.
Data recovery using ShadowExplorer feature
Finally, you may try to extract your files from the Volume Shadow Copies that are normally stored on your computer. Malicious viruses like .Shit ransomware can, of course, delete these files, but ShadowExplorer feature is still worth giving a try.
Report it and recover your files
Report it
Report the attack even if you do not expect the files back: insurers and banks ask for the report number, and police use the contacts in the note to link cases.
- United States
- FBI IC3 · FTC ReportFraud
- United Kingdom
- Report Fraud (formerly Action Fraud) · NCSC
- Australia
- ReportCyber (ASD)
- EU countries
- Europol: national reporting sites
Give the victim ID, the note and the date the files were encrypted. A business that holds personal data may also have to notify its data protection authority, in the EU within 72 hours.
Make the next attack harmless
.Shit ransomware virus could only hurt the files that had no second copy, and the signs (files that end in .shit and no longer open) showed exactly which ones those were. The 3-2-1 rule fixes that:
- three copies
- two media
- one disconnected
A practical version for a home PC: OneDrive or another cloud backup with version history, plus an external disk that you plug in once a week for File History and then unplug. Test a restore now and then by opening a few files from the backup on another device.
Details, schedules and what not to back up are in our 3-2-1 backup guide for Windows.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
Questions about .Shit ransomware virus
Is there a decryptor for .shit files?
That depends on the family behind the .shit extension, which this guide cannot confirm yet from the reports alone. Check No More Ransom and ID Ransomware with your ransom note and one encrypted file; they list families with free tools.
If none exists today, keep the encrypted files and a copy of the note on a separate drive, because decryptors are sometimes published months later after flaws are found or servers are seized. Never buy a decryptor from a website that is not the security company that made it.
How do I open .shit files?
You cannot open them by renaming or by choosing another program. The .shit ending shows that .Shit ransomware virus encrypted the content, and only the matching key can reverse it. Renaming a file back to .docx or .jpg changes nothing except the icon, and it can confuse a future decryptor, so leave the names as they are.
To get the content back, use a backup, an unencrypted copy elsewhere, or a decryptor listed on No More Ransom if one exists for .Shit ransomware virus. Store the encrypted files on an external disk until then.
How did .Shit ransomware virus get on my computer?
The way .Shit ransomware virus spreads has not been documented yet, so look at your own recent activity. On home PCs, ransomware most often comes with cracked programs, game cheats, key generators and fake updates, or with an e-mail attachment that was opened. On business networks, attackers usually log in through Remote Desktop with a stolen or guessed password.
Think back to what was downloaded or installed in the days before files that end in .shit and no longer open, and check the Downloads folder and Installed apps sorted by date. Keep anything suspicious for your report, but do not run it again.
Did .Shit ransomware virus steal my files or passwords?
We do not know yet. Nothing published so far shows data theft by .Shit ransomware virus, but the only confirmed sign is files that end in .shit and no longer open, which says nothing about what happened before. Many current ransomware attacks copy files or run a password stealer first, so it is wise to act as if they did.
From a clean device, change the passwords that were saved in the browsers on this PC, starting with e-mail and banking, sign out of all sessions and turn on two-step verification. Watch bank statements and account activity for the next few weeks.
Should I pay the ransom?
We advise against it, and so do the FBI, Europol and national cyber agencies. Payment does not guarantee a working tool: some attackers never reply, some tools damage files, and some variants have no decryptor at all. Paying also funds further attacks and can make you a target again.
Before considering payment, try every recovery option in this guide and report the attack. Companies must involve their legal adviser and insurer, because payments to sanctioned groups can be illegal. If files are truly irreplaceable, store the encrypted copies and wait; decryptors sometimes appear later.
Can a data-recovery company decrypt my files for a fee?
Only if a decryptor already exists or the company pays the attackers for you. Some "ransomware recovery" services advertise that they can decrypt families with no known flaw; in practice they negotiate with the attackers and add their own fee. Others use the same free tools listed on No More Ransom.
Before you hire anyone, ask in writing how they will recover the files, whether they will contact the attackers and what happens if they fail. A legitimate service answers clearly. If a free decryptor exists for your family, you can run it yourself.
Is .Shit ransomware virus the same as other ransomware with a similar name?
Not necessarily. Ransomware names come from the file extension, the note or a word in the code, so unrelated families often end up with similar names, and one family can appear under several names. The difference matters: a decryptor or advice for one family does not fit another and can damage files.
Compare the ending added to your files and the exact name of the note with the summary table at the top of this guide, then upload the note and one encrypted file to ID Ransomware from a clean device. If the result names another family, follow the guide for that family instead.
Should I reinstall Windows after the .shit attack?
Reinstalling removes the ransomware but not the encryption: your files ending in .shit stay encrypted afterwards. So first copy the encrypted files and the ransom note to a separate drive, in case a decryptor appears later. Then decide:
- a clean-up with an offline scan is often enough for home PCs
- while a full reset is safer if remote access was involved
- scans keep finding new items
Restore your backups only after the PC is clean, and change passwords from another device.
Will removing .Shit ransomware virus unlock my .shit files?
No. Removing .Shit ransomware virus stops it from encrypting more files and from starting again, but it does not decrypt the files that already end in .shit. The scanner does not have the attackers' key.
Files come back only from a backup, from copies the ransomware did not reach, such as OneDrive version history, Previous Versions, e-mail attachments or a phone, or with a working decryptor if one exists.
Remove the ransomware first anyway: if you restore files while it is still active, it can encrypt them again. Keep the encrypted files; a decryptor may be published later.
Will Fortect remove .Shit ransomware virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For .Shit ransomware virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- CISA: StopRansomware (read October 6, 2026)
- No More Ransom (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)