
Trojan.MalPack: what the Malwarebytes alert means and how to clear it
Trojan.MalPack is the name Malwarebytes gives to a file packed the way malware is packed, and it is not a program you can uninstall. Check the path and origin of the file, then follow the scan and removal steps.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
An automatic scan checks installed programs, startup items and browser extensions for anything that came with a Malwarebytes alert for Trojan.MalPack on a packed file.
Do it yourself · free Remove Trojan.MalPack yourself 5 steps, about 15 minutes, no software needed.
Start the steps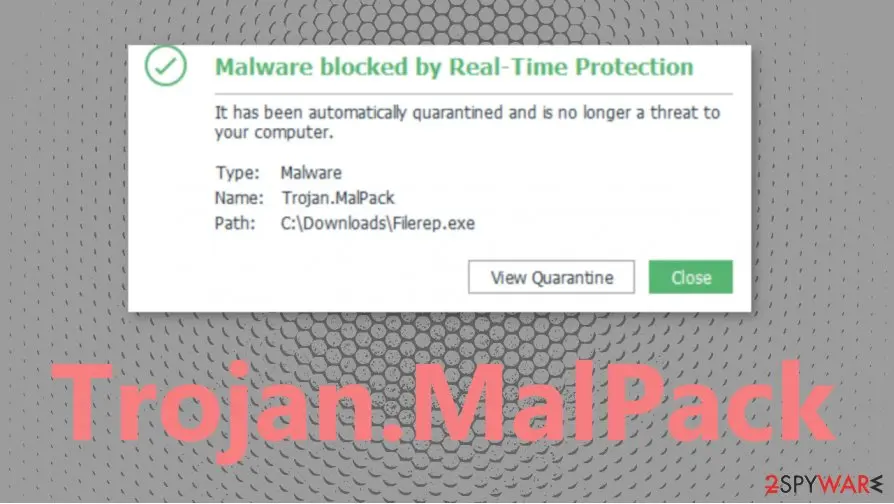
Trojan.MalPack: summary
| Type | A Malwarebytes detection name for trojans that use custom packers; not a program name |
|---|---|
| Risk | Unknown for the plain name: the payload is not documented. The .GS suffix is tied to Ransom.GandCrab. Treat as medium until the path and origin are checked |
| Symptoms | A Malwarebytes alert naming a file path, sometimes repeating; no other sign in most cases we read |
| How to get rid of it | Safe Mode, Threat Scan and Quarantine, Windows Security full scan, Microsoft Defender Offline, Windows updates, System Restore; ask a helper if it repeats |
| Our check (6 October 2026) | No PC test: we read the vendor's threat pages and four forum threads; no sample was run |
| Running since / first seen | No vendor date; Malwarebytes explained packers in March 2017; our first guide 9 November 2020 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Detection | Malwarebytes: Trojan.MalPack, .GS, .VB.Generic, .Generic. No Microsoft detection name is known for this label; Microsoft names threats in its own Trojan:Win32/ scheme and none of the reports we read shows one |
|---|---|
| Shown by | Malwarebytes products; no report of this exact name from another vendor found |
| Not to be confused with | Trojan.Win32.Generic and other vendors' generic labels, which are other detections |
| Name | Trojan.MalPack |
| Evidence | 0 write-ups by security sites; details still limited |
| First seen | 9 November 2020 |
| Distribution | Typically fake installers, cracked programs, e-mail attachments, fake "verify you are human" pages and ads for popular apps |
| Damage | Installs other malware, often several programs at once |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Malwarebytes' threat pages for the family, its 2017 explanation of packers, four Malwarebytes forum threads from 2018 to 2024 and Microsoft Support pages.
We ran no sample and tested no PC; the removal steps follow the vendor page, Microsoft and forum helpers and were not tried on a live infection. Not confirmed: any link to Djvu ransomware, and any payload for the plain name.
What Trojan.MalPack is, and what it is not
Trojan.MalPack is a name Malwarebytes gives to a file, not the name of a program you can look up and uninstall. Malwarebytes calls it a generic detection for trojans that use custom packers, and says the detection rests purely on the way the file is packed, so the payload could be anything.
- 1
What Malwarebytes says
Its threat page says Trojan.Malpack is its generic detection name for trojans that use custom packers to obfuscate their code. It adds that these are packers not normally used for legitimate purposes, and that the detection is based on the way the file is packed. The payload inside could be anything.
- 2
What a packer is
A runtime packer wraps a program so that it unpacks itself in memory when it is run. Malwarebytes' researcher wrote in 2017 that packers were invented to make files smaller, that this matters little today, and that most packers seen now are used for malicious purposes, to make reverse engineering harder and hide the payload from security software.
- 3
What a forum helper added in 2018
A Malwarebytes forum reply from 11 September 2018 called it a generic or heuristic signature that targets files compressed with a tool known to be used by the people who make infections. The reply said it does not necessarily mean the file was an infection, because legitimate software makers sometimes use the same kind of compression.
- 4
What our 2020 guide got wrong
It called Trojan.MalPack a malware packer that spreads various threats, and it described the name as a sign of a threat that infects the machine further. The name labels a packed file; it is not a program that spreads other programs. Whether a given file is harmful depends on what is inside it, and the name does not tell you that.
- Shown by
- Malwarebytes products; we found no report of this exact name from another vendor
- Usual form
- Trojan.MalPack, sometimes with a suffix such as .GS, .VB.Generic or .Generic
- Platform
- Windows; the reports we read are all about Windows files (.exe and .dll)
- Is it a file?
- Yes: unlike a memory detection, the alert names a path, for example a file in AppData, Downloads or a program folder
- Not the same as
- Trojan.Win32.Generic or Microsoft's own Trojan:Win32/ names, which are other labels from other vendors
The label tells you how the file is built, not what it does. The next chapters help you decide, from the path and where the file came from, whether it was real.
What Trojan.MalPack does on an infected PC
The name and its suffixes, one by one
Malwarebytes uses one base name and adds a suffix for each packer or engine behind a detection. These are the ones we found described.
| Name | What the vendor says | What it means for you |
|---|---|---|
| Trojan.MalPack | Generic name for trojans that use custom packers; the detection is based on the packing, and the payload could be anything | Look at the path and where the file came from before you decide |
| Trojan.MalPack.GS | The packed payload delivered by the Grandsoft Exploit Kit, which has delivered Ransom.GandCrab among others | The most serious variant on record; see the chapter on it below |
| Trojan.MalPack.VB.Generic | Not described on a Malwarebytes threat page that we found. In June 2019 it flagged a file manager, xyplorer.exe v20.20, and staff said a fix would come in the next update | In that case a false positive; the name shows the packer family, not guilt |
| Trojan.Malpack.Generic | Not described on a threat page that we found. A reader in March 2024 saw it repeating every few seconds after running a program from an untrusted source | Can be real; that reader needed a helper to clean the PC |
| Generic.Trojan.Malpack.DDS | Trojans that use custom packers, as found by the vendor's Katana engine (its page, as listed in search results) | A detection by behaviour rules, not by an exact signature |
| Trojan.MalPack.VAK | Trojans packed with a specific packer that uses modified API names to avoid generic detection (vendor page, as listed in search results) | Names the packer, not the payload |
What we checked on 6 October 2026, and what we could not
There is no website to test here and we did not run a sample. We read Malwarebytes' pages for the family and four forum threads from 2018 to 2024, and we ran nothing on a PC.
Our reading of the sources, 6 October 2026
- The detection existsMalwarebytes lists Trojan.Malpack and Trojan.MalPack.GS on its own threat pages, so the name is not made up and the alert is not from a web page.
- The alert is a real product messageThe forum cases show it coming from Malwarebytes' own scanner and real-time protection, with a file path and a Quarantine choice.
- What the file isNot known from the name. The vendor says the payload could be anything; its page names no single program.
- Real infection or false positiveNot settled by the name. In 2018 and 2019 the same name flagged Spotify's libegl.dll and XYplorer, and Malwarebytes fixed it in an update; in 2024 a reader's case was real.
- What it doesDocumented for one variant only: Trojan.MalPack.GS delivered Ransom.GandCrab through the Grandsoft Exploit Kit. For the plain name, no payload is documented.
- A clean second scanDoes not clear it. A packed file can be quarantined before it runs, and a clean rescan only says that nothing else matched at that moment.
Check where the file came from before you decide One detection of a packed file can be a false alarm, a blocked download or a leftover of an infection. Write down the path, check where the file came from, then follow the check and removal chapters. We tested nothing on a live PC, so treat the nothing-found of one scan as one data point only.
How readers met it from 2017 to 2026
Our guide dates from 9 November 2020. The picture below is from it, and the other entries are Malwarebytes' own pages and reader reports in its forum.
2017
Malwarebytes explains packers
In March 2017 its researcher published an explanation of packers, crypters and protectors. A block screenshot on the Trojan.Malpack page was uploaded in April 2017. The vendor gives no first-detection date for the name.
2018
Grandsoft delivers GandCrab
Malwarebytes' blog covered GandCrab ransomware distributed by the RIG and GrandSoft exploit kits in early 2018, and the Trojan.MalPack.GS page names the packed payload of the latter.
11 September 2018
Spotify file flagged, then cleared by an update
Readers saw Trojan.MalPack on libegl.dll in the Spotify folder under AppData. A forum reply said a rule had been removed to resolve a false positive that day, and advised updating the database. One reader who had quarantined a file in AppData the same day was told one detection alone made an installed infection unlikely.
June 2019
A file manager flagged as Trojan.MalPack.VB.Generic
A reader found xyplorer.exe v20.20 flagged. The developer said the program was clean, staff said the fix would come in the next update, and the next day the reader scanned again and the alert had gone.
9 November 2020
Our first guide
The 2020 guide treated the name as a packer that spreads threats and showed an alert window naming Filerep.exe.
From our 2020 guide: a Real-Time Protection alert window naming Trojan.MalPack and the path C:\Downloads\Filerep.exe. The window does not show which product made it, and it is not a screenshot we took. March 2024
After a program from an untrusted source
A reader who had run an untrusted program first saw a coin-miner detection from other tools, then Malwarebytes repeating Trojan.Malpack.Generic every few seconds and a slow PC. A helper had the reader run support-tool logs and a fix script, and the reader reported the alert gone afterwards.
August 2026
An uninstaller flagged
A thread title in Malwarebytes' File Detections forum, dated August 2026, reports Trojan.MalPack on the uninstaller of a build of RStudio. We saw only the title, so we do not know the outcome.
Why a detection that rests on packing behaves differently
A scan that matches a file's wrapping can be right, early or wrong. These are the situations the reports show and what to do in each.
| What you see | What is going on, from the reports | What to do |
|---|---|---|
| One alert, one file, no other detection | A forum reply in 2018 said an active trojan would have created a loading point and been caught in at least two items, so one alert alone makes an installed infection unlikely | Note the path, check the file's origin, then run one more full scan |
| The path is a well-known program (Spotify, a file manager, an uninstaller) | Legitimate makers sometimes use the same compression, and the same name flagged a well-known file in 2018 and 2019 | Update Malwarebytes, scan again, and report the file to the vendor if it is flagged again |
| The path is Downloads, Temp or AppData and you do not know the file | This is where the Grandsoft payload shape and untrusted installers sit; the 2018 reply noted AppData needs no administrator rights | Leave it in quarantine and follow the removal chapter |
| It repeats every few seconds | In March 2024 the alert repeated while something kept writing the file again | Something is running and recreating it: find it from Safe Mode or ask a helper |
| You deleted it from quarantine and a scan finds nothing | A removed file does not show what ran before it was blocked | Check passwords if you ran the file before the alert |
Trojan.MalPack.GS: the Grandsoft and GandCrab link
The one suffix with a documented payload is .GS. Malwarebytes says it is the packed payload delivered by the Grandsoft Exploit Kit and that it has delivered Ransom.GandCrab, among others.
- 1
How the kit reaches a PC
An exploit kit is a web page that tries known flaws in a browser or its plug-ins, and drops a file when one works. The Malwarebytes blog described GandCrab being distributed by the RIG and GrandSoft kits in early 2018.
- 2
What the name means for you
If the alert says Trojan.MalPack.GS, think of a file that came from a web page you visited or an unsafe download, and check for ransomware signs (renamed files, a note file) before anything else.
- 3
Other families
Our 2020 guide also said the detection often comes up with versions of the Djvu ransomware. We found no source for that, so we mark it as not confirmed. If your files have a new extension or a note was left, identify the family with ID Ransomware before you pay or reinstall anything.
- 4
What the vendor lists
The page for Trojan.MalPack.GS lists indicators for this payload, including the file name hdgdihijeavhj.exe, and describes a Threat Scan and Quarantine with Malwarebytes for Windows.
What Trojan.MalPack can steal or download
What a hidden trojan can cost you
The one documented payload is the GandCrab ransomware behind Trojan.MalPack.GS. The other risks are those of trojans in general, from our old guide, and they are possibilities, not findings about every alert.
- High
Ransomware
Malwarebytes says Trojan.MalPack.GS delivered Ransom.GandCrab. Our old guide also said the packer may be built to deliver ransomware and other infections; for the plain name no source confirms it.
- High
Data theft or damage
The old guide said an infection like this can trigger data exfiltration or damage. Any trojan that gets to run can, so treat passwords and bank sessions on that PC as at risk until it is cleaned.
- Medium
Other malware on the same PC
The payload can be anything, and a packer can carry several threats. A clean-up of one detection can leave another, which is why a full scan and a second tool matter.
- Medium
A slower PC, damaged programs and altered files
The old guide listed slowness and altered programs. The March 2024 reader reported a slow PC with plenty of memory, but a helper did not tie that to the detection alone.
- Medium
Spreading by e-mail attachments or links
The old guide said spam campaigns can distribute such files as attachments or links. We found no source tying Trojan.MalPack to e-mail, and the reports we read involve downloads.
- Low
Nothing at all
A false positive does no harm, and Malwarebytes has fixed such cases in an update. The danger is the case you cannot tell apart yet.
What you may notice, and what the reports show
Our 2020 guide said the infection can run quietly and affect performance, programs and functions. Here is what the reports we read actually show.
| Sign | What we found |
|---|---|
| The alert itself | Reported in every case: a Malwarebytes scan or real-time block that names a path and offers Quarantine |
| The alert repeating | One reader in March 2024 saw it repeating every few seconds, which means something kept putting the file back |
| A slow PC | The same reader said the PC became sluggish despite 32 GB of memory; the cause was not stated |
| Missing or changed files | Not reported with the plain name. Files encrypted on disk point to ransomware, which Malwarebytes ties to the .GS suffix only |
| Crashes or odd programs | Not reported in any thread we read; a reason to scan, not proof of this detection |
| Nothing | The 2018 reader saw only the one alert after a scan and no other change |
How to check the PC for Trojan.MalPack
How a packed trojan gets onto a PC
No source we read says how plain Trojan.MalPack arrives. These are the routes our old guide gave, the one the Malwarebytes page documents and the one a reader named.
- 1
An unsafe download
The old guide said you most likely got it when you started a download from an unsafe site. The March 2024 reader had run a not-so-trusted program in an emergency, and the alert began after that.
- 2
An exploit kit
The .GS suffix is the payload of the Grandsoft kit, which tries flaws in an outdated browser when you visit a booby-trapped page.
- 3
An e-mail attachment
The old guide said a spam e-mail attachment, or a link inside the e-mail, can carry such a file. It is a general route for trojans, not documented for this name.
- 4
A file you allowed
The old guide put it plainly: you only need to let the file onto the machine and the payload is launched. Opening an attachment from a sender you do not trust, or running a file from a link you do not trust, is how it happens.
- 5
A legitimate program that is flagged
Not an entry route but a possibility: the 2018 and 2019 cases involved genuine programs flagged by mistake.
Whichever the route, the first sign is often only the antivirus alert, because the file may have been stopped before it ran.
Check your PC before you delete anything
Write down exactly what the alert says before you click Quarantine or Delete: the detection name, the path and the time. A forum helper will ask for them.
- 1
Copy the alert
Take a screenshot. Note the full name (the suffix matters), the file path and whether it says it was blocked or found by a scan.
- 2
Open the report
In Malwarebytes open Detection History (the history tab), then the latest scan, and note which items were quarantined. Our 2018 and 2024 readers both learned more from the path than from the name.
- 3
Ask where the file came from
A file in Downloads, Temp or AppData that you did not knowingly save is more worrying than one inside a program you installed on purpose. A path inside a program from a known maker points to a false positive.
- 4
Look for a second antivirus
Open Settings > Apps > Installed apps and look for another security product with live protection. Two of them can interfere with each other.
- 5
Look at what starts with Windows
Press Ctrl + Shift + Esc, open Startup apps, and note names you do not know. If the alert repeats, something is starting the file again.
- 6
Ask whether you ran something new
A file from a download or an e-mail attachment just before the first alert is the most likely route. If you ran it, treat the PC as possibly infected and use the account steps below.
How to remove Trojan.MalPack
A loader's job is to install other malware, so treat the PC as infected with more than one program until the scans are clean.
Step 1: Delete scheduled tasks that bring it back
Open Task Scheduler from the Start menu and click Task Scheduler Library. Select each task you do not recognise and read the Actions tab:
- a task that starts a file in
%AppData%or%Temp% - runs
powershellwith a long encoded line - opens a web address belongs to Trojan.MalPack or a similar program
Right-click such a task and choose Delete, and check the subfolders too. Leave tasks from Microsoft, your PC's maker and programs you use. Task Scheduler is the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
- a task that starts a file in
Step 2: Remove it from startup
Whatever Trojan.MalPack installed usually starts with Windows. Open Task Manager with Ctrl + Shift + Esc, go to Startup apps in Windows 11 or the Startup tab in Windows 10, and disable what you do not know, starting with entries that have an empty Publisher column.
Open file location on the right-click menu shows the file, which helps you decide and tells you what to delete later. Disabling is safe: if something you need stops working, switch it back on.
Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 3: Delete the folders left behind
What the uninstaller leaves behind is usually in the user folders. Open File Explorer, switch on View > Show > Hidden items (in Windows 10 View > Hidden items), and go through
%LocalAppData%,%AppData%, %ProgramData% and the two Program Files folders.Sort by Date modified and delete folders that appeared together with the problem and belong to no program you use. Folders with random names that hold
.exe,.dll, .js or .ps1 files are the strongest sign.Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Scan the PC, then run the offline scan
Open Windows Security > Virus & threat protection > Scan options, run a Full scan and remove everything it finds. Then select Microsoft Defender Antivirus (offline scan) and click Scan now: the PC restarts and scans before Windows loads, which finds files that hide while Windows runs.
Save your work first, because the offline scan takes about 15 minutes. Both scans are built into Windows 11 and Windows 10, and a second scanner from another vendor is a useful extra opinion.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Assume that the passwords saved in this PC's browsers, and the accounts that were open in them, are known to the attacker. From a phone or a clean computer, change the e-mail password first, then banking, shopping, social and gaming accounts.
Use each service's option to sign out of all other sessions, because stolen cookies keep a session open even after a password change. Turn on two-step verification on each account. Wait with the infected Windows 11 or Windows 10 PC until the scans are clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Remove it from Windows 11 and Windows 10
Do the steps in order and stop when a full scan is clean and the alert has not returned. We did not run these steps against a live infection; they follow the Malwarebytes threat page, Microsoft's pages and the advice given in the Malwarebytes forum.
- 1
Disconnect, then back up documents
Turn off Wi-Fi or unplug the cable. Copy documents and photos, not programs, to an external drive that you unplug afterwards.
- 2
Start in Safe Mode with Networking
Open Settings > System > Recovery, click Restart now beside Advanced startup, then choose Troubleshoot > Advanced options > Startup Settings > Restart and press 5 for Safe Mode with Networking. Microsoft says Safe Mode loads only the essential drivers and services, so a program that starts with Windows may not run there. Our old guide told readers to enter Safe Mode before running the scan.
- 3
Scan with Malwarebytes and quarantine
The vendor's page for this detection lists these steps: install Malwarebytes for Windows, click Get started, click Scan to start a Threat Scan, click Quarantine to remove the found threats, and reboot if asked. That is what the vendor describes; we did not run it ourselves.
- 4
Run a full scan with Windows Security
Open Windows Security > Virus & threat protection > Scan options, choose Full scan and Scan now. A second product catches what the first does not, as the old guide advised when it said to double-check with an AV tool.
- 5
Run Microsoft Defender Offline
In the same Scan options choose Microsoft Defender Offline scan and Scan now. Microsoft says it restarts the PC and scans before Windows loads, so malware that hides in Windows has a harder time. Review the result under Protection history.
- 6
If the alert repeats, ask a helper
Download the Malwarebytes Support Tool, choose Advanced, Gather Logs, and post the zip file in the Malwarebytes malware-removal forum. The March 2024 reader was cleaned that way. Do not run a fix script from anyone who has not seen your logs, and never pay for help.
- 7
Update Windows and change passwords
Open Settings > Windows Update and install everything offered. If you ran the file before the alert, change your passwords from a different device.
- 8
Try System Restore
If the alert began after a recent install, open Run with Windows logo + R, type
rstrui.exeand choose a restore point from before it. Microsoft says System Restore reverts system files, registry settings and installed programs, and leaves personal files alone. It will not help if no restore point exists. - 9
Last resort: reset Windows
Back up documents, then use Settings > System > Recovery > Reset this PC and choose Remove everything. Restore documents only, no programs and no full system image.
Never download a removal program because a pop-up or a stranger tells you to. A real threat does not need a phone number or a payment page to fix.
Could it be a false alarm?
Possibly. The same name flagged Spotify's libegl.dll in 2018 and XYplorer in 2019, and Malwarebytes fixed both in a database update. Only the vendor can confirm a false positive.
| Points to a real infection | Points to a false positive |
|---|---|
| The path is in Downloads, Temp or AppData and you do not know the file | The path is inside a program you installed from its maker |
| The alert repeats within seconds or minutes | The alert came once and was quarantined |
| The name ends in .GS, or other tools find something too | Only one product flags it, and a database update stops it |
| A new program, download or attachment came first | No new program, file or download beforehand |
| Files were renamed or a note file appeared | The PC works normally and only the alert is odd |
If you think it is false, update Malwarebytes, scan again and report the file in the vendor's False Positives forum with the scan log. Staff told 2019 readers they could add an exclusion and restore the file, but do that only after the vendor or the program's maker has said the file is clean.
After removal: passwords, accounts and prevention
Accounts come next
Because the PC showed A Malwarebytes alert for Trojan.MalPack on a packed file in the list of installed apps, a sign of a program that could read browser data, the clean-up is only half of the work. The other half happens in your online accounts.
Change passwords from a clean device, beginning with e-mail; sign out of all sessions; check forwarding rules and recovery phone numbers; and turn on two-step verification with an authenticator app or a passkey. Ask your bank to replace cards saved in the browser.
Why the order matters and what to check in each account: secure your accounts after malware.
If it was real: what to do about your accounts
The scans above deal with the PC. These steps deal with what the trojan could have seen, and they matter most if you ran the file before the alert.
- 1
Change passwords from another device
Email first, then banking, then everything else. Turn on two-step sign-in. Do this before you use banking on the infected PC.
- 2
Sign out everywhere
Use the sign out of all sessions option in your Google, Microsoft and social accounts so stolen cookies stop working.
- 3
Check your money
Look at card statements and any wallets for payments you did not make.
- 4
Look for ransomware signs
Check whether documents were renamed or a note file appeared. If so, do not pay and do not reinstall yet; identify the family first.
- 5
Scan again in a week
A clean scan today does not clear everything. Run another full scan and a Defender Offline scan a week later, and keep the alert screenshot.
Keep packed trojans off your PC
The 2020 advice was to be suspicious of unknown senders and links. It still holds; here it is with current details.
Do
- Keep one security product with Real-time protection on. Microsoft Defender is built into Windows 11 and 10.
- Install Windows Update monthly, and update browsers and PDF readers, so exploit kits find no flaw.
- Open attachments only when you expected them and the sender's address matches. Delete the rest.
- Download programs from their makers' sites or the Microsoft Store.
- Keep a backup of documents on a disk you unplug (File History or OneDrive).
- Use a password manager and two-step sign-in so one stolen password does not open every account.
Don't
- Do not run programs from sites you do not trust, even in an emergency.
- Do not open a file from a link or an e-mail whose sender you do not trust.
- Do not run two antivirus programs with live protection at once.
- Do not restore a quarantined file or add an exclusion until the vendor says it is clean.
- Do not call a number shown in an alert.
Questions about Trojan.MalPack
What is Trojan.MalPack?
It is a Malwarebytes detection name for a file that has been wrapped with a custom packer of the kind used for malware. Malwarebytes says the detection rests purely on the way the file is packed, and that the payload inside could be anything.
The name does not tell you which program is behind it, and it is not something you can find in the Apps list and uninstall. A suffix such as .GS names a specific case: the packed payload of the Grandsoft Exploit Kit, which has delivered Ransom.GandCrab. Treat the alert as a prompt to check the file's path and origin.
Is Trojan.MalPack a virus or a false positive?
It can be either, and the name alone cannot tell you which. Malwarebytes flagged Spotify's libegl.dll in September 2018 and XYplorer in June 2019 under this family, and fixed both in a database update. A March 2024 reader, however, had run an untrusted program and saw the alert repeat every few seconds.
Check the path first: a file inside a program from its maker points to a false positive, while a file in Downloads, Temp or AppData that you do not know points to a real one. Update the scanner and scan again to see if the alert stays.
How do I remove Trojan.MalPack from Windows 11 or 10?
Disconnect and back up documents, start in Safe Mode with Networking, then run a Threat Scan in Malwarebytes and quarantine what it finds, as the vendor's page describes. Follow with a full scan in Windows Security and a Microsoft Defender Offline scan, and install all Windows updates.
If you ran the file, change your passwords from another device. If the alert returns within minutes, gather logs with the Malwarebytes Support Tool and ask in its removal forum. We did not test these steps on a live infection.
What is the difference between Trojan.MalPack, .GS, .VB.Generic and .Generic?
The suffix names the case or the engine behind the detection. Plain Trojan.MalPack is the generic name for custom-packed trojans. The .GS suffix is the packed payload of the Grandsoft Exploit Kit and is tied to Ransom.GandCrab.
The .VB.Generic and .Generic forms appear in forum reports, from a false positive on a file manager in 2019 to a repeating alert in 2024, but we found no vendor page describing them. The DDS and VAK suffixes mark a behaviour engine and a specific packer. The .GS case is the one to take most seriously.
Does Trojan.MalPack mean I have ransomware?
No, not by itself, but the .GS suffix is linked to it. Malwarebytes says Trojan.MalPack.GS has delivered Ransom.GandCrab, among others, through the Grandsoft kit.
Our old guide also said the detection often appears with Djvu ransomware; we found no source for that and mark it as not confirmed. Check for signs:
- documents renamed with a new extension
- a note file in folders
- a message asking for payment
If none appear, the detection was probably a blocked file. If they do, do not pay, and identify the family with ID Ransomware first.
Why does Malwarebytes keep detecting Trojan.MalPack again and again?
Because something keeps putting the file back. One reader in March 2024 saw the alert repeat every few seconds, and a helper cleaned it with logs and a fix script. A quarantined file only removes the packed file, not the process or startup entry that writes it.
Restart in Safe Mode, check the Startup apps list, run a Defender Offline scan, and gather logs with the Malwarebytes Support Tool for a helper. Do not run a fix script from someone who has not read your logs.
Should I restore a Trojan.MalPack file from quarantine or add an exclusion?
Only if the vendor or the program's maker has said the file is clean. In June 2019 staff told XYplorer users they could add an exclusion and restore the file while waiting for the update, and the maker said the program was clean.
That was a known program with a known source. If you do not know the file, leave it in quarantine. When in doubt, report it to the vendor's False Positives forum with the scan log and wait for the answer.
Does Trojan.MalPack steal my passwords?
The name does not say so, and no source we read ties the plain name to password theft. The payload could be anything, and a trojan that runs can in general record what you type or send files out. Our old guide listed data exfiltration as a possibility.
If you ran the file before the alert, change your passwords from another device, turn on two-step sign-in and check your statements. If the file was only blocked in quarantine, the risk is low, but a week of caution costs little.
Can another antivirus show Trojan.MalPack?
We found no report of this exact name from another vendor. It is Malwarebytes' label, and other products name the same kind of file in their own schemes, such as Microsoft's Trojan:Win32/ names, so a different name does not mean a different file.
If a second scanner says the file is clean, that is one more data point, not a clearance, because packed files can hide from some engines. Compare the path, the file's origin and the Detection History of each product.
Will Fortect remove Trojan.MalPack?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Trojan.MalPack, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Malwarebytes: Trojan.Malpack threat alert (read October 6, 2026)
- Malwarebytes: Trojan.MalPack.GS threat alert (read October 6, 2026)
- Malwarebytes: Generic.Trojan.Malpack.DDS threat alert (search-result description) (read October 6, 2026)
- Malwarebytes: Trojan.MalPack.VAK threat alert (search-result description) (read October 6, 2026)
- ThreatDown (Malwarebytes): Explained: Packer, Crypter, and Protector (26 March 2017) (read October 6, 2026)
- Malwarebytes Forums: Trojan.malpack Please help very anxious (11 September 2018) (read October 6, 2026)
- Malwarebytes Forums: XYplorer.exe False Positive (June 2019) (read October 6, 2026)
- Malwarebytes Forums: Trojan.Malpack.Generic keep reproducing every 3 seconds (March 2024) (read October 6, 2026)
- Malwarebytes Forums: File Detections, page 4 (thread title, August 2026) (read October 6, 2026)
- Microsoft Support: Windows startup settings (Safe Mode) (read October 6, 2026)
- Microsoft Support: System Restore (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (read October 6, 2026)
- Microsoft Support: Virus and threat protection in the Windows Security app (read October 6, 2026)