
Mokes malware: what it is and how to remove it
Malware targets Windows, macOS/Mac OS X, as well as Linux users and is packed of various capabilities, including data theft, keystroke capture, screenshot making, audio/video footage recording, and much more.
While over the years, the developers used different tactics to distribute the malware, most recently Mokes virus was spotted being delivered with the help of online scams, which shows users that the security certificate has expired as soon as they land on a malicious website.
Facts checked October 6, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If 2020.exe returns after removal, a full scan can find the entry that brings it back.
Do it yourself · free Remove Mokes malware yourself 6 steps, about 18 minutes, no software needed.
Start the steps
Mokes malware: summary
| Distribution | The malware is delivered with the help of various methods, including spam emails, exploits, file sharing sites, hacked sites, and, most recently, fake security certificate alerts |
|---|---|
| Name | Mokes malware |
| Type | Backdoor |
| Platform | The malware is cross-platform – it targets Windows (Backdoor.Win32.Mokes.imv), macOS (OSX.Mokes), and Linux (Backdoor.Linux.Mokes.a) users |
| Capabilities | Creates a backdoor that allows propagation of other malware Connects to a remote Command & Control server to receive and execute commands Steals banking login details and financial information Logs keystrokes Takes screenshots and records video Monitors USB storage, etc. |
| Dangers | Infection of another malware, such as ransomware, financial losses, identity theft |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 7 more facts
| Symptoms | Rarely any, although more advanced users can spot new folders and other entries created by Mokes |
|---|---|
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| File names | 2020.exe |
| First seen | 18 March 2020 |
| Facts checked | 6 October 2026 |
What Mokes malware does on an infected PC
From our report of Mar 2020 · not reviewed since
Mokes malware - malicious software that targets users' banking credentials
Malware targets Windows, macOS/Mac OS X, as well as Linux users and is packed of various capabilities, including data theft, keystroke capture, screenshot making, audio/video footage recording, and much more.
While over the years, the developers used different tactics to distribute the malware, most recently Mokes virus was spotted being delivered with the help of online scams, which shows users that the security certificate has expired as soon as they land on a malicious website.
Mokes malware removal is crucial to every computer owner who was infected with it. In case it is allowed to run for a prolonged time, it can steal and deliver the most sensitive data to malicious actors behind it. As a result, victims might suffer from monetary losses, installation of other malware, or even identity theft.
Mokes malware is a sophisticated backdoor that can steal information without victims noticing its presence on the device.
As a result, they might suffer from significant monetary losses due to banking credential theft and also be exposed to the Dark Web, which means that the stolen data can be used to purchase goods online in victims' names, take out loans, etc. In other words, Mokes virus can result in identity theft, which can be disastrous to any individual.
Over time, Mokes malware developers used a variety of distribution techniques, including:
Once executed, Mokes virus will begin the infection of the system, which also differs, depending on the platform that is used. After the infiltration, malware will drop a variety of malicious files on the infected device and also connect to a remote C&C server, which is used to deliver stolen information, as well as receive commands from malicious actors.
Mokes malware will begin to steal valuable data from the infected individual, including keystrokes, which means that everything that is typed on online banking, social media, and other websites can be retrieved by cybercriminals.
Additionally, it may take screenshots every 30 seconds and also record audio. Unfortunately, because Mokes is a silent virus, most users will be unaware that it is operating in the background and stealing an excessive amount of information about them.
Therefore, the only way to detect and remove Mokes malware is by employing anti-virus software that can scan the machine thoroughly and eliminate all the malicious files and traces. Additionally, to fix virus damage, users are recommended using .
- spam email attachments
- targeted phishing attacks
- (zero-day) exploits
- repacked software installers
- fake updates, etc.
From our report of Mar 2020 · not reviewed since
Mokes malware recreates its nine times in different locations on Windows
When the Windows version of the malware was initially noticed, it also came with a valid certificate - it meant that users were not asked whether they want to execute the malicious file on their computers.
Upon infiltration on Windows machines, Mokes malware chooses nine random locations on Windows' %AppData% folder and then copies itself there. Additionally, the virus creates a folder called "version," which holds information about a version of the installed malicious software.
For persistence, Mokes virus will create the registry keys under the following entry (this ensures that malware launches with every Windows boot - typical behavior of most malicious programs):
Later, Mokes malware uses a built-in Windows API in order to enable the keylogger functionality on the computer, as well as record the mouse inputs of the victim. As a final step, it contacts its C&C server, which it can receive commands from every 60 seconds. All the communications are encrypted with a secure AES encryption algorithm, along with all the stolen data from the victim's machine.
From our report of Mar 2020 · not reviewed since
Mokes for Mac creates a folder that may seem legitimate to regular users
On macOS, Mokes malware is known as OSX.Mokes or Backdoor.OSX.Mokes.a, and is written in C++ by utilizing the Qt framework.
Initially, Apple patched the vulnerability that was used to proliferate the infection, but new variants of Mokes virus soon showed up, and these could bypass the newly implemented security measures.
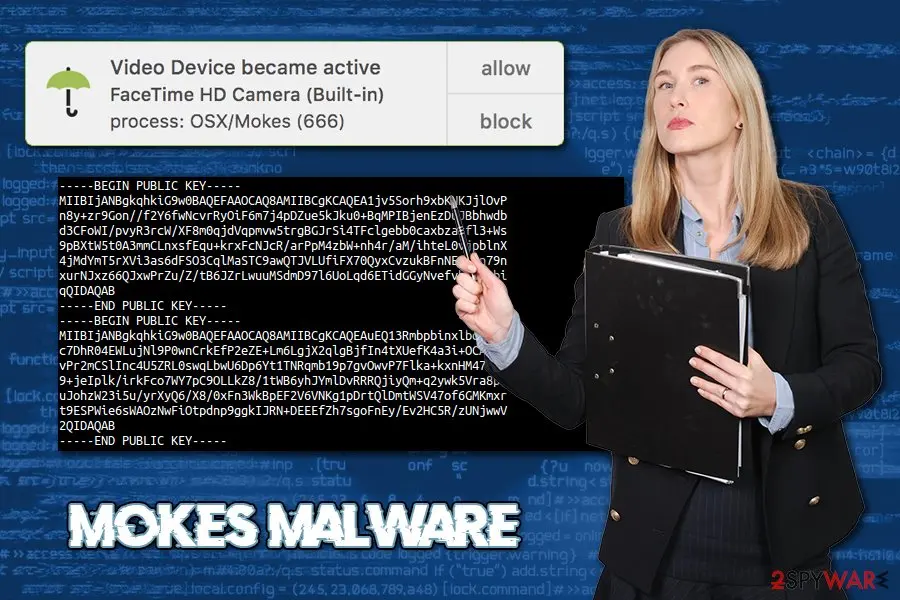
Just like on Windows, Mokes malware typically operates silently in the background, without showing any signs or symptoms to regular users. Nevertheless, some might notice suspicious or erratic Mac behavior when the infection is present. For example, if you notice pop-ups like "Install.app wants access to control" should never be ignored, as it is an unusual behavior of the computer.
After gaining access to a Mac, Mokes will create a new folder labeled as "App Store" in the Home Library folder. This folder typically does not exist on macOS systems, but the name is used to deliberately mislead users if they happen to encounter it on their devices. Inside, it will create a service "storeuserd," which is used to hide Mokes from being detected.
As evident, some macOS users still claim that malware is not an issue to this platform - malware strains like Mokes, Shlayer Trojan, CrescentCore, and many others prove that Macs need extra protection.
From our report of Mar 2020 · not reviewed since
Terminate Mokes malware
As previously mentioned, Mokes virus is a stealthy backdoor that typically does not emit any symptoms.
Therefore, unless you are an advanced user who knows about which files belong to the OS and which are imported by malware, you most likely never know that it is running on the background of your Windows, macOS, or Linux computer.
Thus, you should employ anti-malware software to remove Mokes malware from your system at once. If you keep up-to-date security software on your computer, you can avoid most of the malicious intrusions in the future.
Note that Mokes malware removal might get interrupted due to its functionality. In such a case, you can access Safe Mode with Networking, as explained below, and perform a full system scan from there.
Additionally, we highly advise you to monitor your online banking activities for unauthorized transactions, as these can often be reverted after contacting the bank. In case you find your credit card compromised, contact your bank and close it down immediately.
[GI=method-1]Access Safe Mode with Networking by performing the following steps:
From our report of Mar 2020 · not reviewed since
More from our earlier report on Mokes malware
- Mokes is a cross-platform backdoor that was first discovered in 2016 by Kaspersky security researchers.
- In case your Windows system is malfunctioning after you get rid of the infection (lag, crashes, errors), you can repair virus damage with the help of
- Besides, the 2019 malware report, delivered by Malwarebytes researchers, claimed that Mac malware is outpacing even Windows machines.
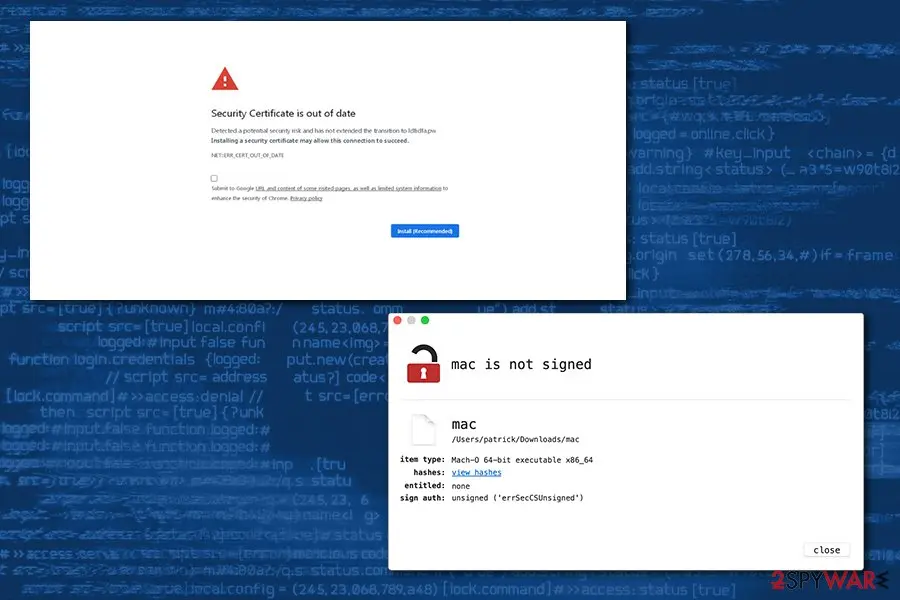
- Security Certificate is out of date Detected a potential security risk and has not extended the transition of Idfidfa.pw Installing a security certificate may allow this connection to succeed.
- NET::ERR_CERT_OUT_OF_DATE Submit to to Google URL and content of some visited pages as well as limited system information to enhance the security of Chrome.
How Mokes malware got on your PC
From our report of Mar 2020 · not reviewed since
Malicious actors behind the campaign used a variety of techniques to distribute the malicious program.
Security researchers spotted it abusing the zero-day vulnerability within the Mozilla Firefox web browser - once users land on a specially crafted site (via the redirects or adware), a weak spot within the software is abused to insert malware automatically.
Thus, users are injected with malicious payload without performing any actions at all. Hence, it is vital to patch all the installed software with security updates as soon as possible (this includes the operating system as well).
Another popular technique used by attackers is spam email attachments. These typically include various attributes of legitimate and well-known companies like UPS or Amazon. Using social engineering, malicious actors pretend to be representatives of these corporations and urge users to open the attached file. Thus, make sure you never open an executable file clipped to the mail, or never allow MS Office files to run macro function.
In mid- January 2020, Mokes malware was spotted in a phishing campaign abuse the trusted certificate feature on various websites, including zoo and e-commerce sites. Upon entering the page, users were met with the following message:
Because the alert uses formatting and attributes that are typical to Google Chrome's warning alerts, many users might not suspect a thing and proceed with the installation process of the "Certificate_Update_v02.2020.exe," which is actually Mokes malware payload. To avoid the deception, you should use sophisticated anti-malware tools along with web protection shields on your machine.
How to check the PC for Mokes malware
- File:
2020.exe
How to remove Mokes malware
Someone may have had remote control of the PC.
Cut the connection first, then remove the trojan and secure your accounts.
Step 1: Remove remote access tools and lock the attacker out
Attackers keep access through remote control tools and extra user accounts. Disconnect the PC from the internet, then remove every remote access program you did not install yourself from the installed apps list in Windows 11 or Windows 10.
Look for a user account you do not know and delete it, and switch off Remote Desktop in Settings > System. Reconnect only for the scan.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Check where 2020.exe runs from and stop it
In Task Manager (Ctrl + Shift + Esc) find
2020.exeon Processes, right-click it and choose Open file location before ending anything.Windows' own files live in
C:\Windows\System32; the same name in%AppData%, %Temp% or C:\Users\Public is an impostor. If the folder is wrong, right-click the process again, choose End task and delete the file.If it starts again within seconds, a task or another process restarts it, so run the scan step in Safe Mode. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Delete scheduled tasks that bring it back
Programs like Mokes malware add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 4: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 5: Scan the PC, then run the offline scan
A scan finds the parts of Mokes malware that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 6: Change passwords from another device and sign out other sessions
Mokes malware can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
After removal: passwords, accounts and prevention
Your passwords after Mokes malware
Removing Mokes malware does not undo what it may already have sent out while the PC showed an unfamiliar process called 2020.exe in Task Manager.
Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
Access your website securely from any location
When you work on the domain, site, blog, or different project that requires constant management, content creation, or coding, you may need to connect to the server and content management service more often. The best solution for creating a tighter network could be a dedicated/fixed IP address.
If you make your IP address static and set to your device, you can connect to the CMS from any location and do not create any additional issues for the server or network manager that needs to monitor connections and activities. VPN software providers like can help you with such settings and offer the option to control the online reputation and manage projects easily from any part of the world.
Recover files after data-affecting malware attacks
While much of the data can be accidentally deleted due to various reasons, malware is one of the main culprits that can cause loss of pictures, documents, videos, and other important files.
More serious malware infections lead to significant data loss when your documents, system files, and images get encrypted. In particular, ransomware is is a type of malware that focuses on such functions, so your files become useless without an ability to access them.
Even though there is little to no possibility to recover after file-locking threats, some applications have features for data recovery in the system. In some cases, can also help to recover at least some portion of your data after data-locking virus infection or general cyber infection.
Questions about Mokes malware
Is 2020.exe safe?
It depends on where the file is and who signed it, not on the name. Open Task Manager, go to the Details tab, right-click 2020.exe and choose Open file location. A file inside Program Files or System32 with a valid digital signature from a known company is usually part of a legitimate program.
A file in AppData, Temp or ProgramData with no signature, especially one that restarts itself after you end it, is suspicious. If you cannot tie the process to anything you installed, uninstall recent unfamiliar programs and run a Microsoft Defender Offline scan.
Can I end 2020.exe in Task Manager?
Ending an unknown process is safe in the sense that Windows will warn you before you close anything critical, and a restart brings back whatever Windows needs. Ending 2020.exe will not remove it, though: if a task or startup entry launches it, it returns at the next sign-in.
Use ending the process as a test. If something important stops working, it belonged to a program you use. If nothing changes and it comes back by itself, find and disable its starter, delete the file and scan the PC.
Is 2020.exe a virus?
If it sits outside the Windows and Program Files folders and your antivirus links it to Mokes malware, yes. 2020.exe is the file name used by this trojan. Some trojans borrow the names of real Windows components, so the name alone does not decide it:
- right-click the process in Task Manager
- choose Open file location
- look at the folder and the publisher under Properties > Details
A file in a user folder with no publisher is the trojan. Do not delete it by hand while it runs; use the offline scan in the plan above.
How do I know if my PC has Mokes malware?
Often you do not, which is the point of a trojan. Possible signs are an antivirus alert naming Mokes malware or a generic trojan detection, unknown programs or scheduled tasks, processes with random names in Task Manager, browser extensions you did not add, security settings turned off, slower performance, or account alerts about logins from unknown places.
The reliable check is a full scan followed by Microsoft Defender's offline scan. If you recently ran a crack, a fake installer or a command a website told you to paste, scan even without symptoms.
Is Mokes malware a known trojan?
Not as a documented family, at least not yet. What is known is the visible sign, an unfamiliar process called 2020.exe in Task Manager, which matches a hidden program working for someone else.
New threats are often seen by victims weeks before researchers publish anything about them. Treat Mokes malware as you would any trojan:
- remove what starts it
- run an offline scan
- change passwords from another device
If a scan reports a detection name, keep it; it usually reveals the family and whether it is known to download other malware. We update this guide when an analysis appears.
I found AnyDesk or ScreenConnect that I did not install. Is that Mokes malware?
Not necessarily Mokes malware, but it is a warning sign. These are legitimate remote support tools, and criminals use them as ready-made backdoors, especially after tech support scams or fake invoice calls.
If you did not install it and no one you trust set it up, uninstall it, change passwords from a clean device and check your bank account. If someone connected to your PC through it, follow the steps for remote access trojans and consider a Windows reset. Installed apps sorted by date shows when it appeared.
Is it safe to do online banking after seeing an unfamiliar process called 2020.exe in Task Manager?
Not on that PC until it is clean. A program that produces an unfamiliar process called 2020.exe in Task Manager runs with your rights and could read what you type or what the browser shows. Use a phone or another computer for banking and for changing passwords.
When the offline scan of the affected PC is clean and nothing suspicious starts with Windows any more, you can go back to using it. Check your bank statements for the past weeks either way, and call the bank if anything looks unfamiliar; banks can block cards and reset access quickly.
Do I need to reinstall Windows to get rid of Mokes malware?
Usually not. A thorough clean-up is enough when the offline scan finds nothing afterwards and you do not see an unfamiliar process called 2020.exe in Task Manager again. A reset is the safer choice if an attacker had remote control, if security tools were switched off, or if detections come back after every clean-up.
Windows 11 can reset itself without a USB stick under Settings > System > Recovery > Reset this PC. Copy documents and photos out first and scan the copies. A reset does not change passwords or undo stolen data, so the account steps still apply.
Should I check my other computers too?
Yes, it takes little time and removes doubt. Mokes malware itself usually stays on one PC, but the download that carried it may have been copied to other computers, shared drives may hold the same installer, and an attacker who had access could have tried saved passwords on other devices.
Run a full scan on every Windows PC in the home or office, check shared folders for the original download, and change Wi-Fi and router passwords if they were stored on the infected machine.
Will Fortect remove Mokes malware?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Mokes malware, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- SecureList: From Linux to Windows – New Family of Cross-Platform Desktop Backdoors Discovered (read October 6, 2026)
- ZDNet: Backdoor malware is being spread through fake security certificate alerts (read October 6, 2026)
- SentinelOne: How Two Firefox Zero Days Led to Two macOS Backdoors (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)