
Mughthesec ads: what it is and how to remove it
Mughthesec is a type of malware that usually attaches itself to Safari, Google Chrome, or another browser as an extension, although it also drops files on the system. Designed strictly for Macs, this malicious program gains access to the device behind users' backs, namely, fake Flash Player installers that could be encountered on malicious websites around the internet.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
If redirects to a.akamaihd.net keep coming back, a free scan can check extensions, programs and browser settings in one pass.
Do it yourself · free Remove Mughthesec ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps
Mughthesec ads: summary
| Distribution | This malware is typically installed via fake Flash Player updates |
|---|---|
| Name | Mughthesec |
| Type | Mac virus, adware |
| Dangers | Malicious actors could download additional payloads on the infected machine, steal information, and perform other nefarious actions while controlling the device remotely |
| Related files | Installer.app, Player.dmg, FlashPlayerInstaller |
| Detection names | No Microsoft detection name is known |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Damage | Not recorded in the old report |
|---|---|
| Symptoms | Redirects to an unknown domain |
| Evidence | 4 write-ups by security sites; details still limited |
| Domains | a.akamaihd.net |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 14 January 2021 |
| Facts checked | 6 October 2026 |
What the Mughthesec ads ads look like
<...>it turns out that the installer actually doesn't do anything malicious, (besides actually installing a legit copy of Flash), if it detects it running in VM.
Is Mughthesec ads dangerous?
From our report of Jan 2021 · not reviewed since
Mughthesec - Mac virus that might remain undetected due to its effective evasion techniques
Mughthesec is a type of malware that usually attaches itself to Safari, Google Chrome, or another browser as an extension, although it also drops files on the system.
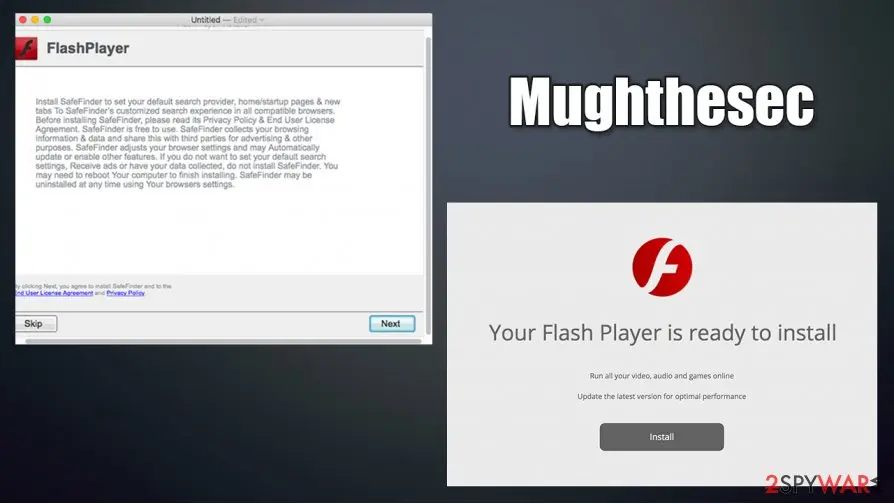
Designed strictly for Macs, this malicious program gains access to the device behind users' backs, namely, fake Flash Player installers that could be encountered on malicious websites around the internet. These might be titled Player.dmg, while, during the installation, users might only see an Installer.app shown to them.
Once installed, the Mughthesec virus drops multiple malicious .plist files and establishes persistence by evading security software. It also installs several malicious apps designed for Macs, including the notorious scarware Advanced Mac Cleaner.
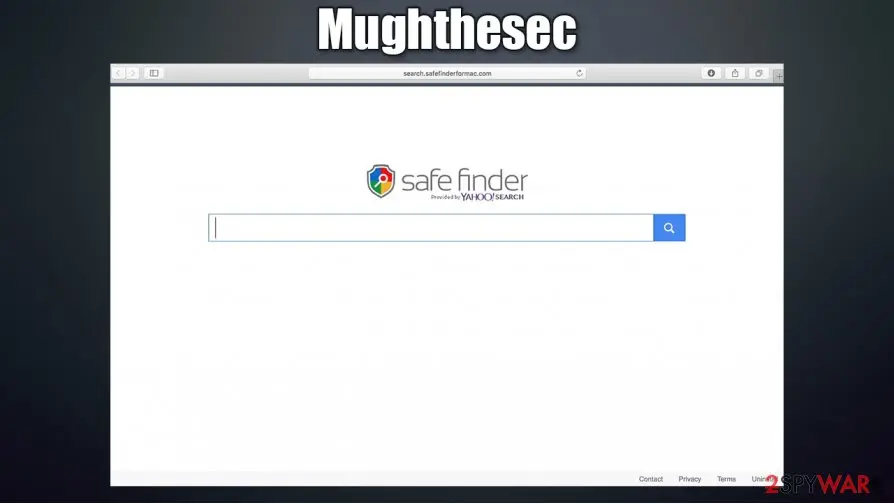
It also hijacks users' web browsers, sets the homepage to a.akamaihd.net, and delivers intrusive advertisements and sponsored links on a regular basis. Hence, its main goal is to gain revenue from ads and remain undetected on the infected machine for as long as possible.
Fake Flash Player updates have been used to spread malware around for ages now, and Mac users are pretty much accustomed to this type of online scams. Upon accessing a malicious website, visitors are presented with a fake version of the plugin, with the claim that it is needed in order to display website contents or play multimedia.
Unfortunately, to this day, users are still getting deceived by this old trick and end up installing potentially unwanted programs or malware on their systems.
There could be many apps that would be disguised as the Mughthesec virus, thus making it virtually impossible to detect if the user is unaware that it is installed in the first place. For example, UniversalWebResults or AnySearch were found to be one of the main culprits of the infection.
Once installed, malware would deliver a pop-up, asking users to install the following applications:
These apps are very typical adware designed to use scam techniques to make users buy stuff online. Do not allow these to be installed on your system, as you will only infect your device further! After that, users will see their browsers completely messed up, as their homepage settings would be altered, and results redirected to Yahoo.
What is particularly interesting about this malware is its ability to avoid detection by most security software due to its effective evasion technique. Once launched, it deploys a binary that includes the names of the most common security applications used on Mac devices. However, updated versions of security software should be able to detect and stop the infiltration of the virus.
Due to malware's nature, one of the main ways to detect it on a Mac is by using a powerful Firewall. It can blog the insecure connection when the installed tries to establish it to download its malicious files onto a computer.
Another interesting feature of Mughthesec malware is that it tries to avoid analysis completely when it detects that a virtual machine is used. According to researchers:
Nonetheless, it is important to clean the system properly when trying to remove Mughthesec virus from your system fully, and you might have to employ several tools for that, combining it with the manual instructions we provide below. can also be used as a tool to clean the leftovers of the virus if such need arises.
- Advanced Mac Cleaner
- Safe Finder
- Booking.com.
From our report of Jan 2021 · not reviewed since
Fake Flash Player installers are prevalent on Macs - learn to avoid them
Flash Player has been terminated fully by Adobe in January 2021 and is no longer supported.
From a security standpoint, it is definitely good riddance, as this plugin has been possibly the most exploited tool by cybercriminals. There are two ways threat actors employ it for malicious deeds:
Therefore, without exceptions, you should simply not use Flash - even the legitimate version. There is simply no need for it, as it has long been replaced with new technologies such as HTML 5. All the claims that it needs to be updated in order to view some online content are fake and a scam, so you should never listen to these requests.
While some fake installers may be signed with a valid certificate (making the infiltration of malware a much easier process, as signed files bypass the built-in Gatekeeper protection), most are not, so security software should be able to detect malicious versions of such files easily.
- Use fake installers to trick users into installing PUPs or malware;
- Exploit numerous software vulnerabilities found within the plugin.
From our report of Jan 2021 · not reviewed since
More from our earlier report on Mughthesec
- However, the best results can only be achieved by using reputable security software, such as
- After you eliminate the threat from your machine, you should change all your passwords and then perform repeated scan with to clean malware leftovers
Check your browser and PC
- Address:
a.akamaihd.net
How to remove Mughthesec ads
How to remove Mughthesec from a Mac
Remove the app and what starts it, then check the browsers.
Step 1: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from Mughthesec or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 2: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 3: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 4: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
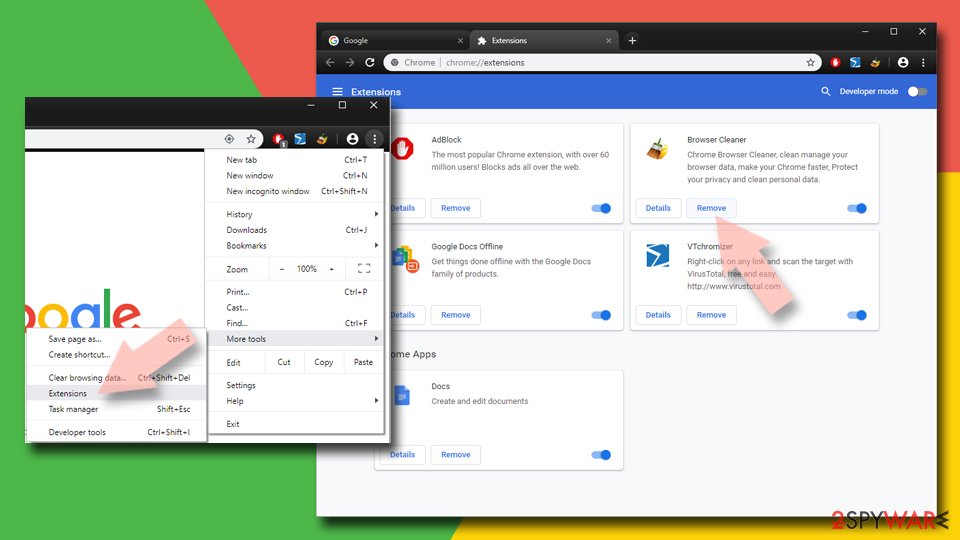
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
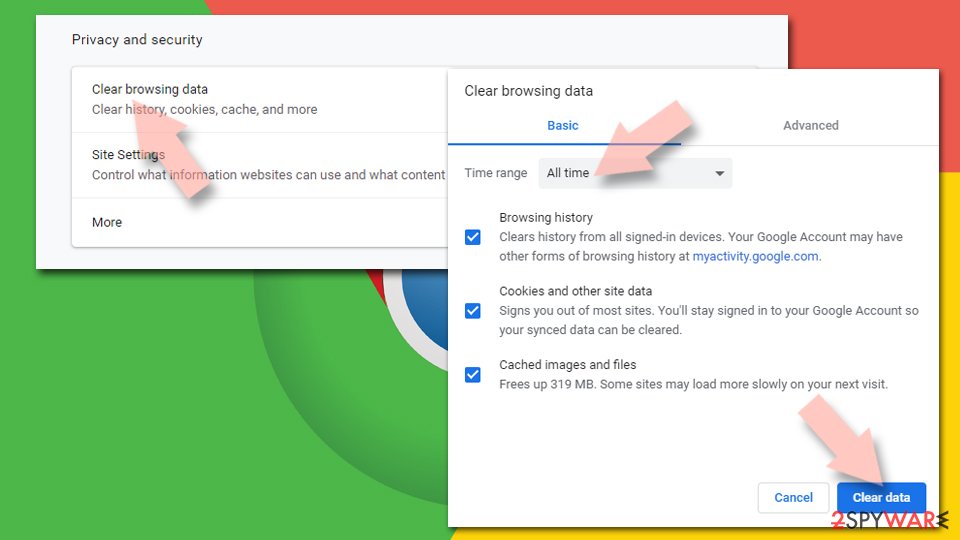
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
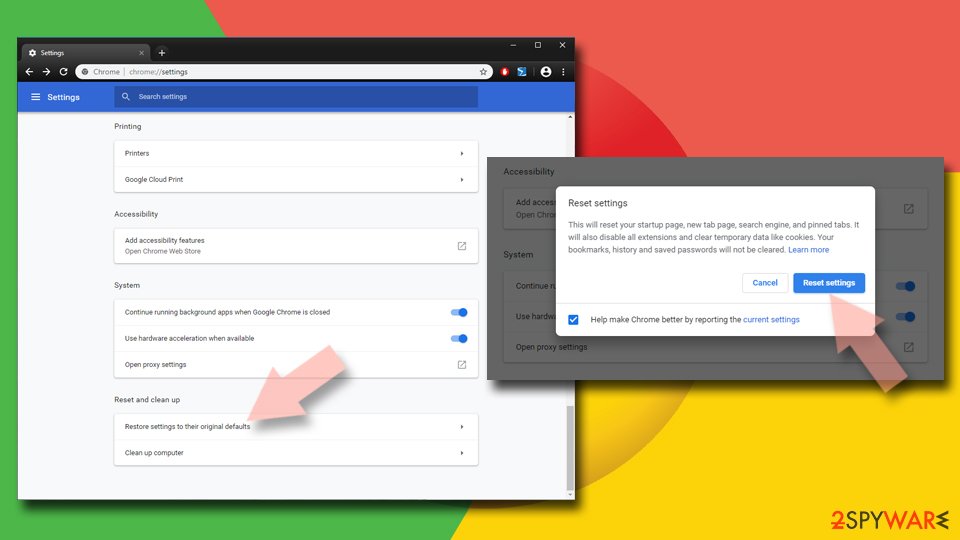
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Mozilla Firefox (FF)
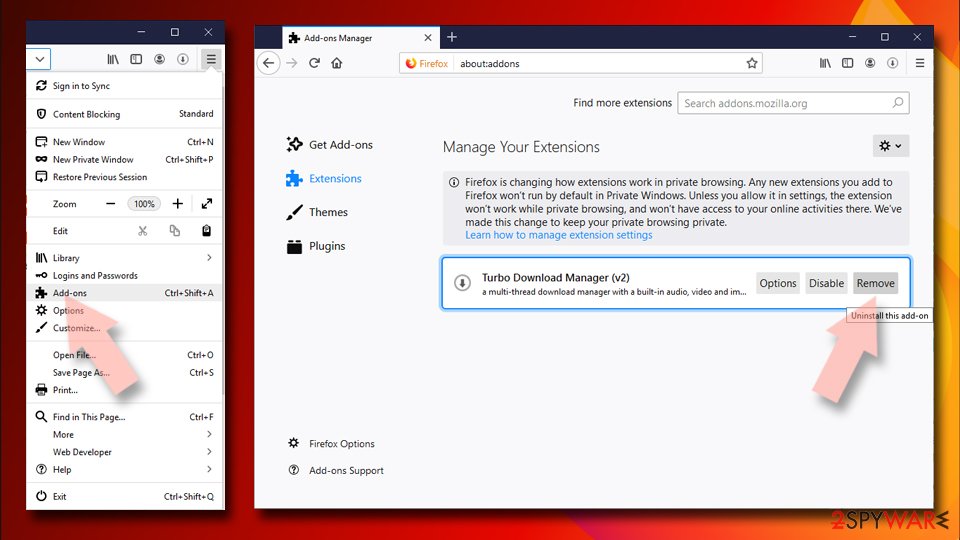
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
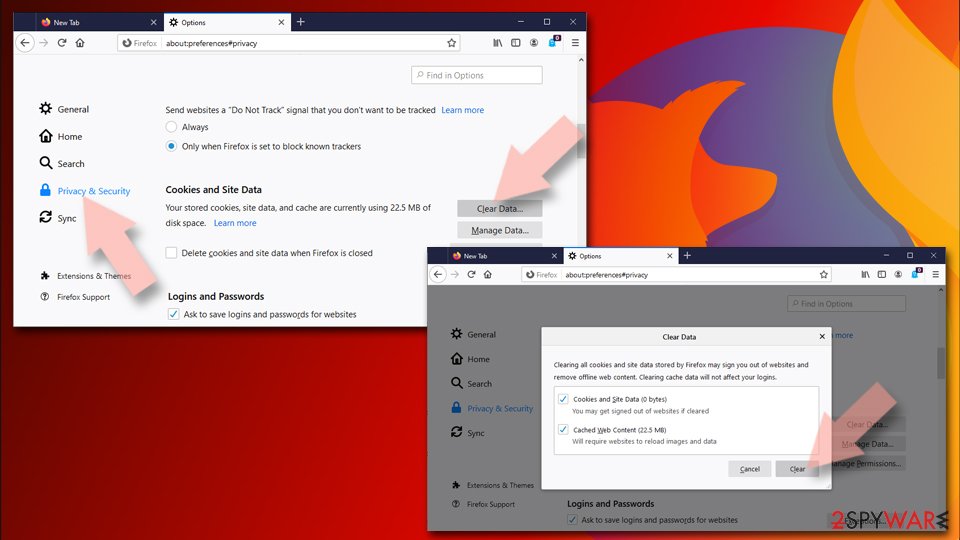
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
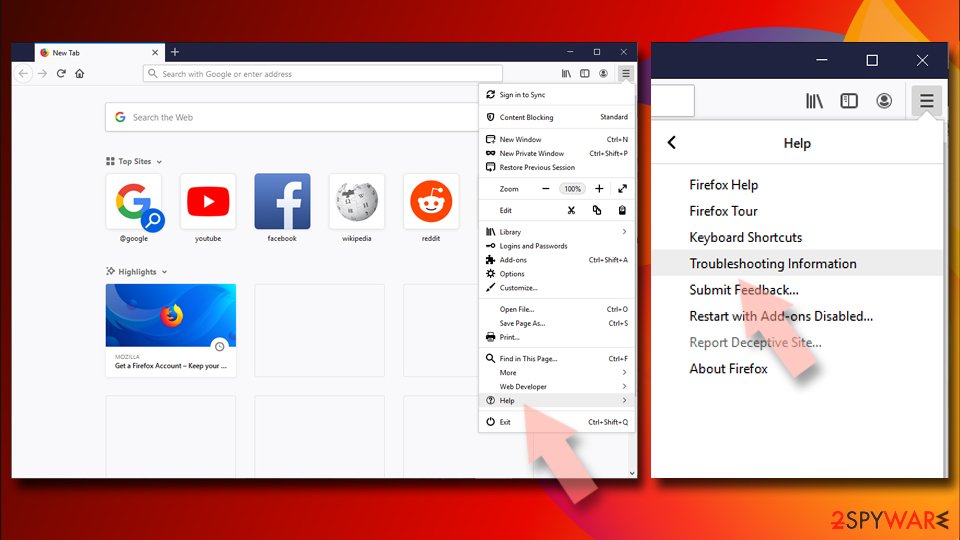
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
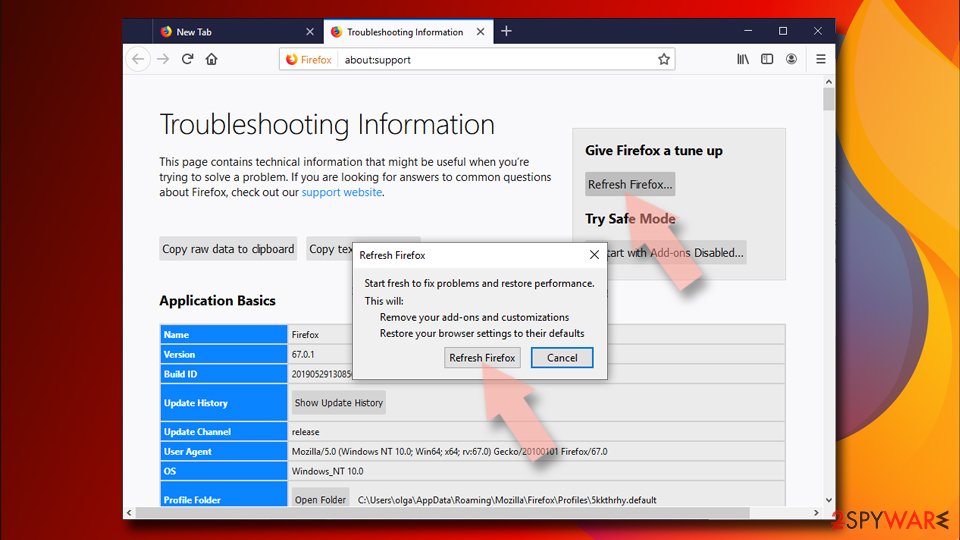
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Make sure you uninstall Any Search extension from your Safari web browser, along with other suspicious ones. If the need arises, you can reset your web browser to bring it to its default state:
Remove dangerous extensions:
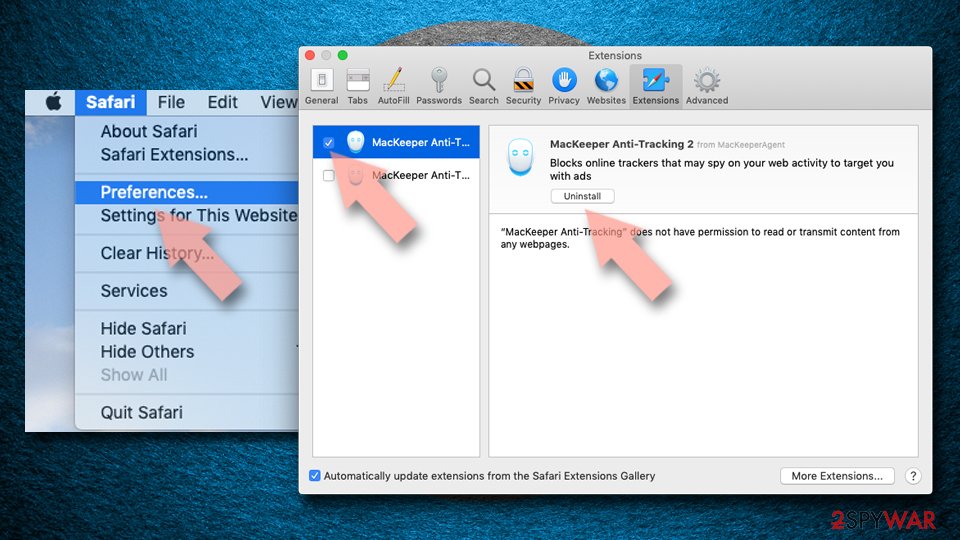
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
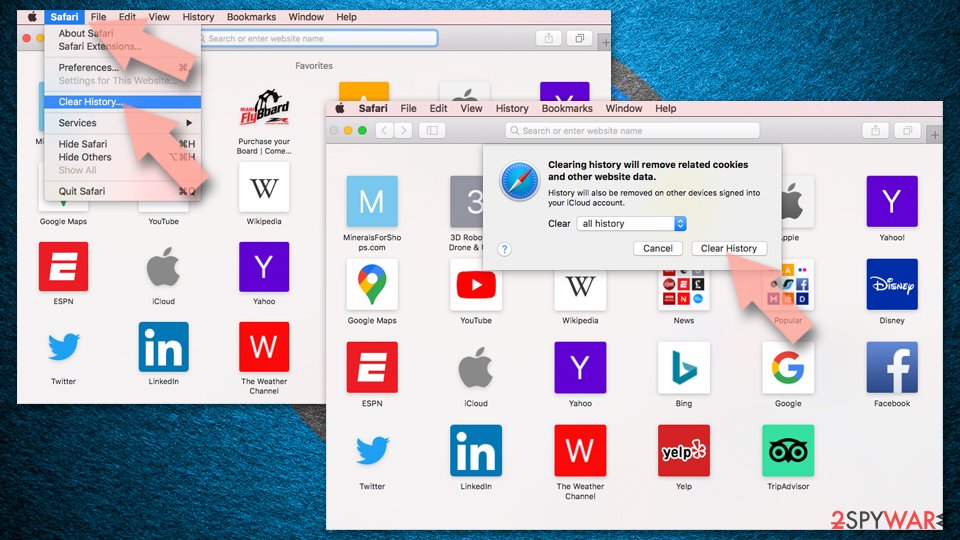
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
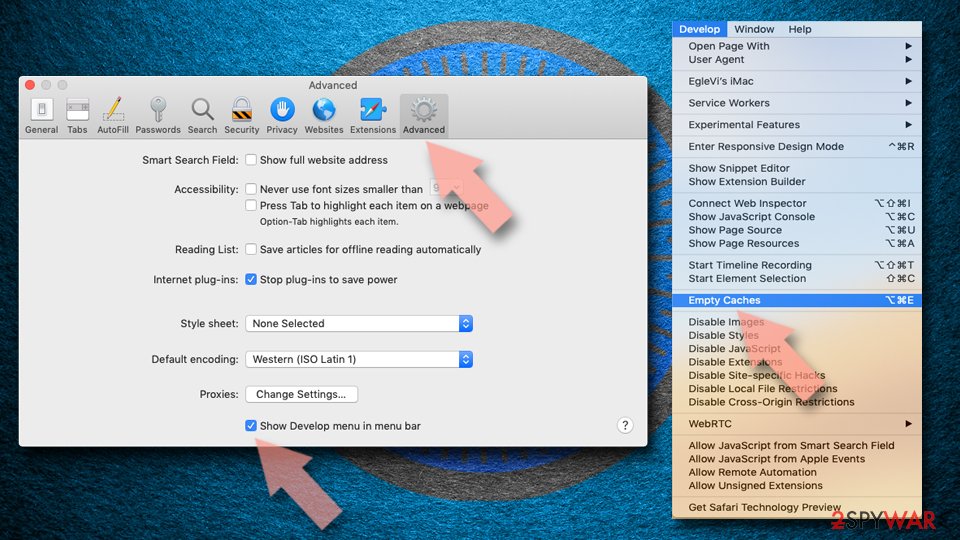
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Choose a proper web browser and improve your safety with a VPN tool
Online spying has got momentum in recent years and people are getting more and more interested in how to protect their privacy online.
One of the basic means to add a layer of security - choose the most private and secure web browser. Although web browsers can't grant full privacy protection and security, some of them are much better at sandboxing, HTTPS upgrading, active content blocking, tracking blocking, phishing protection, and similar privacy-oriented features.
However, if you want true anonymity, we suggest you employ a powerful VPN - it can encrypt all the traffic that comes and goes out of your computer, preventing tracking completely.
Lost your files? Use data recovery software
While some files located on any computer are replaceable or useless, others can be extremely valuable.
Family photos, work documents, school projects - these are types of files that we don't want to lose. Unfortunately, there are many ways how unexpected data loss can occur:
- power cuts
- Blue Screen of Death errors
- hardware failures
- crypto-malware attack
- even accidental deletion
To ensure that all the files remain intact, you should prepare regular data backups. You can choose cloud-based or physical copies you could restore from later in case of a disaster. If your backups were lost as well or you never bothered to prepare any, can be your only hope to retrieve your invaluable files.
From our report of Jan 2021 · not reviewed since
Manual Mughthesec removal might not be a straightforward process
In order to remove Mughthesec virus from your device, you need to eliminate all of its components, along with those that were brought in during the infection of the system.
It includes the following files and folders:
You also need to use launchctl to unload the payload that is running in the background with the following command:
Finally, you need to uninstall Any Search extension, along with all other unrecognized components on your browsers.
However, if you are a novice computer user, we highly recommend performing automatic Mughthesec removal with an updated anti-malware software. You will not have to worry about malicious .plist files, and other components dropped by malware, as security applications are capable of automatically finding and deleting them.
Questions about Mughthesec ads
Why does my browser keep going to a.akamaihd.net?
Something is sending it there. On one site only, that site's ads are the cause and leaving the site ends it.
On many different sites, the usual causes are an extension you installed with something else, a site you once allowed to send notifications, or an ad-supported program in Windows that changes how the browser behaves. a.akamaihd.net itself is only a stop on the way: it records the visit and forwards you to whatever advertiser pays most.
Check the extensions page, then the list of sites allowed to send notifications, then Installed apps sorted by date. Removing the cause stops the redirects; blocking the domain alone usually does not, because the network moves to a new one.
Is it safe that my browser was redirected to a.akamaihd.net?
Landing on a.akamaihd.net does not infect the PC by itself. A browser does not run programs from a page without your action. The danger is in the pages that come next:
- some ask you to allow notifications
- some show fake virus warnings
- some offer downloads
- ask for card details
If you only saw those pages and closed them, nothing more is needed than removing whatever caused the redirect. If you allowed notifications, remove that permission.
If you downloaded a file, delete it unopened, or uninstall it if you ran it. If you typed a password or card number on one of the pages, change the password and call your bank.
Why does Mughthesec show me ads?
Because that is its whole purpose. Mughthesec is an adware extension, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Do I have to clean every browser?
Yes, if you use more than one. We saw Mughthesec in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from Mughthesec?
Look for redirects to a.akamaihd.net. That is the trace Mughthesec leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
Can adware slow down my PC?
Yes. Adware runs in the background, loads ad scripts, opens extra tabs and contacts its servers, all of which use processor time, memory and bandwidth. Ad-heavy extensions also slow down every page, because they inspect and change it before you see it.
The effect is strongest on older PCs and when several adware programs arrived together. After removal, restart the PC and check Task Manager for anything still using a lot of resources that you do not recognise. Speed usually returns to normal once the ads stop.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
Does adware steal passwords?
Ordinary adware is built to show ads, not to steal logins, and most of it never touches saved passwords. The line is blurry, though. Extensions that can read every page could capture what you type, and adware ads sometimes lead to phishing pages that ask for passwords directly.
If you entered credentials on a page reached through an ad, change that password from a clean device and turn on two-step verification. Otherwise, removing adware extension and clearing cookies is usually enough.
Will Fortect remove Mughthesec?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For Mughthesec, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Wikipedia: Scareware (read October 6, 2026)
- Objective-See: WTF is Mughthesec!? (read October 6, 2026)
- Windows Latest: Windows 10 update to kill off Adobe Flash Player permanently (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)