
Backdoor:MSIL/AsyncRAT: what it is and how to remove it from Windows
Backdoor:MSIL/AsyncRAT is Microsoft's detection name for AsyncRAT, a free remote control tool that attackers use to watch the screen, log typing and run programs on a Windows PC. If an alert names it or you find it, change your passwords from another device and follow the removal steps.
Facts checked October 13, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Programs like a Defender alert naming Backdoor:MSIL/AsyncRAT, or an unknown program in AppData or Public usually arrive in groups; a free scan lists the companions that are easy to miss.
Do it yourself · free Remove Backdoor:MSIL/AsyncRAT yourself 5 steps, about 15 minutes, no software needed.
Start the steps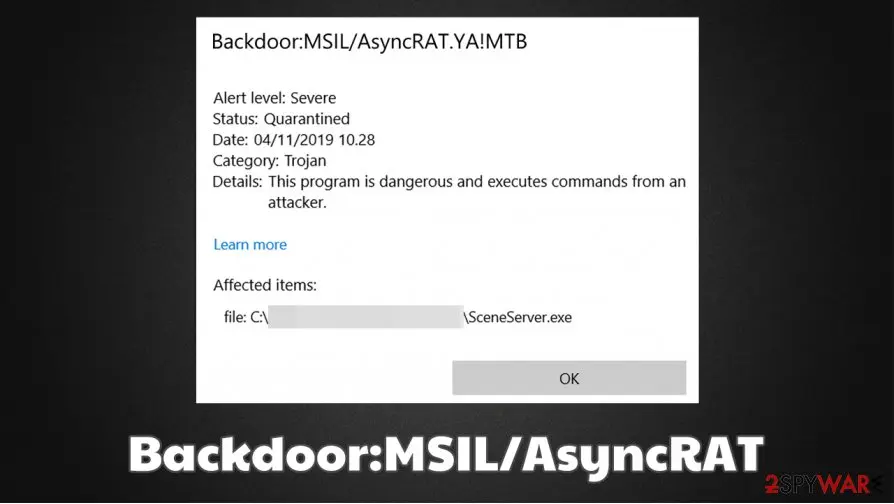
Backdoor:MSIL/AsyncRAT: summary
| Type | Remote access trojan (open-source remote administration tool for Windows, used by attackers as a backdoor) |
|---|---|
| Risk | High: a person can see your screen, record what you type and run programs; Microsoft documents theft of saved passwords and wallet files |
| Symptoms | Often none. A Defender alert, an unknown scheduled task or Run entry, or a new .exe in AppData or Public can show it |
| How to get rid of it | Disconnect, change passwords from another device, Safe Mode, Windows Security full scan, Defender Offline, check startup, tasks and exclusions, reset Windows if unsure |
| Our check (6 October 2026) | No PC test: we read Microsoft, MITRE, the project page, Proofpoint and FortiGuard reporting; we ran no sample |
| Running since / first seen | Public since 19 January 2019; Microsoft entries May 2019 and May 2020; used by criminal groups since 2020; our guide 30 September 2020 |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 10 more facts
| Detection | Microsoft: Backdoor:MSIL/AsyncRAT!MTB, Backdoor:MSIL/AsyncRAT.YA!MTB and Trojan:Win32/AsyncRAT.SA (a 32-bit build, entry of November 2025); edited builds get other names |
|---|---|
| Language and platform | C#, Windows only, needs .NET Framework |
| Not to be confused with | Other remote tools such as NanoCore, Remcos and Quasar, which are other families |
| Name | Backdoor:MSIL/AsyncRAT |
| Evidence | 0 write-ups by security sites; details still limited |
| First seen | 30 September 2020 |
| Microsoft Defender name | Backdoor:MSIL/AsyncRAT!MTB, Backdoor:MSIL/AsyncRAT.YA!MTB and Trojan:Win32/AsyncRAT.SA |
| Distribution | Typically e-mail attachments, fake installers, cracked games, tech support scams and compromised updates |
| Damage | Full remote control of the PC, theft of files and passwords, further infections |
| Facts checked | 6 October 2026 |
Facts checked on 6 October 2026 against Microsoft's entries for Backdoor:MSIL/AsyncRAT!MTB, Backdoor:MSIL/AsyncRAT.YA!MTB and Trojan:Win32/AsyncRAT.SA, MITRE ATT&CK S1087, the project page, Proofpoint's 2020 report on TA2719, a June 2026 report on FortiGuard's AsyncRAT campaign and Microsoft's pages for Safe Mode, Windows Security and Defender Offline.
We ran no sample and tested no PC; the removal steps were not tried on a live infection. Not confirmed: the Spamhaus botnet that our 2020 guide named, the group name Mo Lou Qi, Wacatac and Copa ransomware as AsyncRAT payloads, and AsyncRAT delivery by fake updates, web injects or Remote Desktop break-ins.
What Backdoor:MSIL/AsyncRAT is, and what it is not
Backdoor:MSIL/AsyncRAT is the name Microsoft Defender gives to a file built from AsyncRAT, a free remote control program for Windows. The program was written to watch and control other computers, and on a PC where nobody asked for it, it works as a backdoor that lets a stranger in.
- 1
What the author says it is
The project page on GitHub calls AsyncRAT a remote administration tool for Windows written in C#, designed to monitor and control other computers over an encrypted connection. It is free and open source under the MIT License, so anyone can download it, change it and build their own copy. The author's legal disclaimer says the software was made for educational purposes only and must not be used on any system you do not own or have permission to operate.
- 2
What MITRE and Microsoft say it is
MITRE ATT&CK (software S1087) describes AsyncRAT as an open-source remote access tool, first shared through the NYAN-x-CAT repository, that has been used in malicious campaigns. Microsoft calls its detections a sophisticated and persistent backdoor whose central goal is a hidden and lasting channel for remote control. Our 2020 guide described the same thing: a surveillance or educational tool that criminals turned into malware.
- 3
How it works
AsyncRAT has a server and a client. The person in control runs the server, uses its builder to produce the client file, and sees every connected PC in a list. The client is the file that runs on the victim's PC, calls home and waits for commands. The project says the client needs .NET Framework 4 and the server 4.6 or newer, and that extra functions arrive as plugins sent from the server.
- 4
What a backdoor and a RAT are
A backdoor is a way into a computer that goes around the normal checks, such as a sign-in. A remote access tool (RAT) is a program that lets one person operate another computer from a distance. Help desks use such tools legitimately. A remote access trojan is the same kind of program delivered secretly, which is why one name can describe both a lab tool and an intruder.
- 5
Why Microsoft's name looks like code
In Backdoor:MSIL/AsyncRAT, Backdoor is the category and MSIL means Microsoft Intermediate Language, the form .NET programs are compiled to. AsyncRAT is the family. The suffix after the exclamation mark, !MTB, stands for Machine Threat Behavior: Microsoft says it means the file was flagged by behavior or machine-learning models, not by one fixed signature. A letter group such as .YA marks a variant.
- 6
What our 2020 guide got wrong or left out
It said the malware mainly targets organizations; Proofpoint's reports show mass email to ordinary recipients as well. It said a backdoor grants administrator permissions; AsyncRAT only checks whether the current user is an administrator. It also named a Spamhaus botnet and a group called Mo Lou Qi that we could not confirm. Each point is corrected in the chapter where it belongs.
- Also called
- AsyncRAT; AsyncRAT-C-Sharp (the repository name); Backdoor:MSIL/AsyncRAT!MTB and Backdoor:MSIL/AsyncRAT.YA!MTB (Microsoft's two names for the detections our 2020 guide listed)
- Made by
- GitHub user NYAN-x-CAT; open source under the MIT License, so copies and edited builds circulate widely
- Project start
- First commit on 19 January 2019; latest release v0.5.8 on 16 October 2023 (the page we read showed 430 commits)
- Language and platform
- C#; Windows only; needs the .NET Framework
- Microsoft entries
- Backdoor:MSIL/AsyncRAT.YA!MTB, published 21 May 2019; Backdoor:MSIL/AsyncRAT!MTB, published 18 May 2020 (both updated in December 2025); Trojan:Win32/AsyncRAT.SA, published 18 November 2025, for a 32-bit build, with a separate 64-bit family named Trojan:Win64/AsyncRat
- Groups named in MITRE
- TA2541, APT-C-36 (a customised version) and MirrorFace; Proofpoint separately tracked TA2719 using AsyncRAT in 2020
Trojan:MSIL/AsyncRAT!rfn: is it the same as Backdoor:MSIL/AsyncRAT?
Trojan:MSIL/AsyncRAT!rfn is most likely another Microsoft Defender label for the same AsyncRAT remote access tool, but we could not confirm that.
We found no Microsoft encyclopedia entry for this exact name, so the reading in this section is ours and not a Microsoft statement. Treat the alert as real until you have checked the file.
The first part of a Microsoft name, such as Trojan or Backdoor, is the category Microsoft gives a detection. MSIL means the file is a .NET program, and AsyncRAT is written in C#. That fits our reading that Trojan:MSIL/AsyncRAT and Backdoor:MSIL/AsyncRAT point at the same family, only under different category labels.
The text after the exclamation mark, here rfn, is a suffix that Microsoft adds to a detection. We found no Microsoft page that explains rfn, so we will not guess what it means. Suffixes like !MTB are described in this guide, and the steps below do not depend on which suffix your alert shows.
If Defender shows this name, open Windows Security, then Protection history, and note the file path and what action Defender took. Then follow the removal steps in this guide from the top, starting with disconnecting the PC and changing your passwords from another device.
What Backdoor:MSIL/AsyncRAT does on an infected PC
What we checked on 6 October 2026, and what we could not
There is no website to test here and we did not run a sample. We read Microsoft's three entries, MITRE ATT&CK, the project page, Proofpoint's 2020 report and a June 2026 report on a new campaign. We ran nothing on a PC.
Our reading of the sources, 6 October 2026
- The tool is real and publicThe project page, MITRE ATT&CK and Microsoft all describe the same open-source remote access tool, with source code public since January 2019.
- Attackers use itProofpoint saw TA2719 deliver it in 2020. MITRE lists TA2541, APT-C-36 and MirrorFace as users. A campaign reported in June 2026 still used it.
- Which copy is on your PCUnknown from the name. Microsoft says the open-source origin led to many obfuscated variants, so file names, folders and servers in old reports may not match your build.
- Your own caseWe cannot tell from here whether an alert on a given PC is a real intruder, a researcher's lab or a mistaken detection. The file's path and where it came from decide that.
- Steps on this pageThe removal steps follow Microsoft's entries and Windows support pages. We did not run them against a live infection.
- A clean scanDoes not clear a PC. A remote access trojan lets a person act on the PC, and a scan that finds nothing says only that nothing matched on that one run.
Treat an unexplained AsyncRAT detection as someone else being in control No test of ours can clear a PC. If Defender or another product named AsyncRAT and you do not know the file, assume a person could see your screen and passwords, change your passwords from another device, and follow the removal chapter.
AsyncRAT from open-source tool to commodity malware, 2019 to 2026
Our guide dates from 30 September 2020. Its newest facts were Proofpoint's 2020 report and the two Microsoft names; the entries from 2021 on are new here.
19 January 2019
The project starts
The first commit in the AsyncRAT-C-Sharp repository is dated 19 January 2019. The code stays public under the MIT License.
21 May 2019
Microsoft publishes Backdoor:MSIL/AsyncRAT.YA!MTB
This is the earlier of Microsoft's two entries. The alert in our 2020 lead picture carried this name.
From our 2020 guide: a Defender alert for Backdoor:MSIL/AsyncRAT.YA!MTB, alert level Severe, status Quarantined, date 04/11/2019 as written (the day and month order is not shown), affected file SceneServer.exe with the folder blurred. Late March 2020
TA2719 starts with NanoCore
Proofpoint began tracking a new actor, TA2719, that sent localized lures with colorful images impersonating local banks, police and shipping services. From March to early July it spread NanoCore, mostly as ISO attachments.
10 May 2020
New features released
Proofpoint noted that AsyncRAT still looked under active development, with new features released on 10 May 2020.
18 May 2020
Microsoft publishes Backdoor:MSIL/AsyncRAT!MTB
The second entry, now the one most alerts quote. Microsoft updated both entries on 2 and 3 December 2025.
Mid-July 2020
TA2719 switches to AsyncRAT
Proofpoint's report of 26 August 2020 says the actor pivoted from NanoCore to AsyncRAT, still by email attachment, in low-volume campaigns that reached recipients in countries from Chile to Taiwan. Its command servers changed roughly once a month.
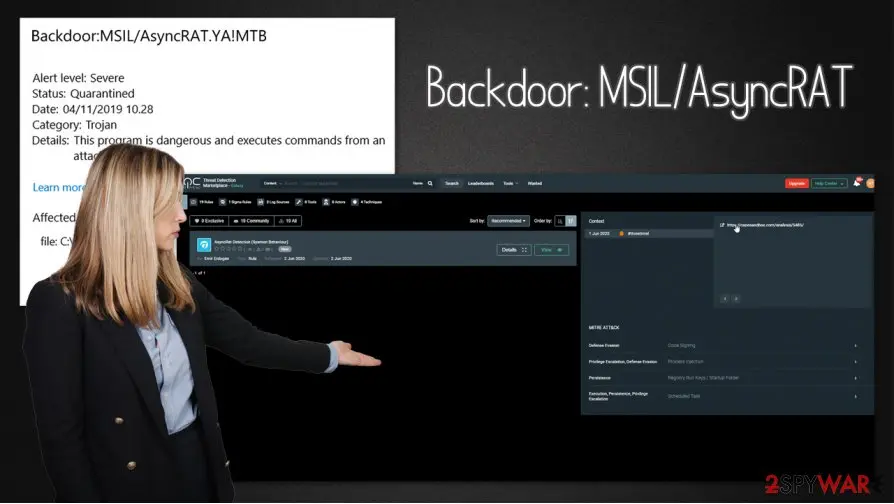
From our 2020 guide: the same alert beside a detection-rule catalogue page that lists ATT&CK techniques such as process injection, registry Run keys and scheduled tasks. The woman is a stock photo. 30 September 2020
Our first guide
The 2020 guide treated AsyncRAT as a dangerous backdoor, listed its functions and named TA2719, a group called Mo Lou Qi and a Spamhaus botnet. TA2719 is confirmed; the other two we could not find in the sources we read.
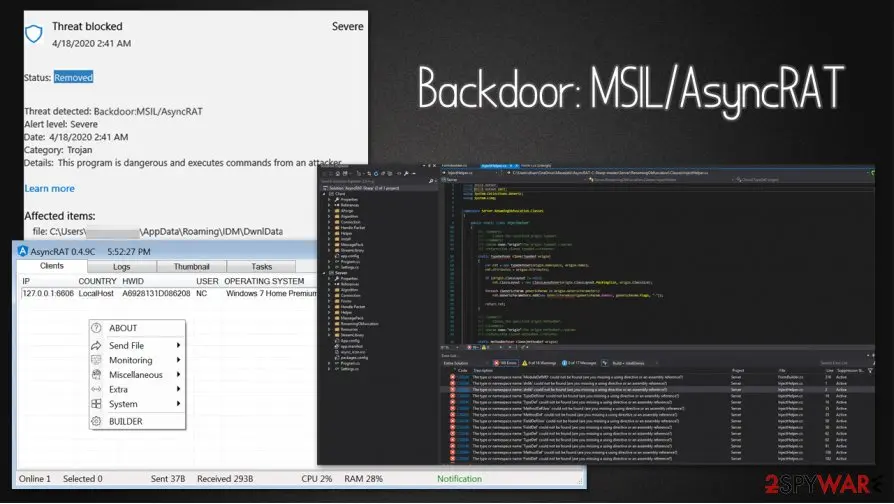
From our 2020 guide: a Defender notice (Threat blocked, Severe, status Removed, 4/18/2020, a file under AppData\Roaming\IDM\DwnlData) next to an AsyncRAT 0.4.9C server window with one client at 127.0.0.1, the same PC, and a code editor. The server window is the controller's side, not what a victim sees. 2021 to 2022
AsyncRAT inside loaders and long campaigns
MITRE's references for AsyncRAT include Morphisec's May 2021 report on the Snip3 crypter, which it calls a highly evasive RAT loader, Cisco Talos on a five-year attack on the aviation industry and Proofpoint's February 2022 report on TA2541.
16 October 2023
Last release so far
Version v0.5.8 is the latest release on the project page we read. Edited builds do not depend on it.
2024 and 2025
State-linked groups use custom builds
MITRE lists a customised AsyncRAT used by APT-C-36 (Kaspersky, 19 August 2024; Check Point, March 2025; Recorded Future, 26 August 2025) and custom versions used by MirrorFace in Operation AkaiRyu, reported by ESET on 18 March 2025, where it was deployed by batch script.
June 2026
Fake AI guides carry it
FortiGuard Labs, as reported on 18 June 2026, described 7z archives posing as AI learning material, with titles such as AI-Ready PostgreSQL 18, that start a long chain of scripts and end in a .NET remote access trojan, with one branch delivering AsyncRAT.
What AsyncRAT can do on a PC
One person, from one window, controls many PCs. These are the functions the project lists and the ones MITRE and Microsoft documented. Our 2020 guide listed screenshots, keylogging, password theft, anti-analysis and installing other malware; all of them are documented. An edited build may have more or fewer.
| Function | What it means for you | Where documented |
|---|---|---|
| Client screen viewer and recorder | The controller sees your screen and can record it; the server also shows thumbnails of every connected PC | Project page, MITRE |
| Keylogger | Everything typed is recorded, passwords included | Project page, MITRE, Microsoft |
| Password recovery | Passwords saved in browsers, email programs and messengers can be read; Microsoft also lists cryptocurrency wallet files | Project page, Microsoft |
| File transfer over SFTP | Files can be downloaded from your PC and others uploaded to it, including more malware | Project page, MITRE |
| Plugins and JIT compiler | Functions are added after infection from the server; Microsoft names exploits, proxy use and ransomware deployment as examples | Project page, Microsoft |
| Antivirus and integrity manager, and security status | The client reports which security software runs; our 2020 guide described this as viewing the status of your antivirus | Project page, Microsoft |
| Anti-analysis (configurable) | The client can look for debuggers and for strings such as Virtual, vmware or VirtualBox and behave differently | Project page, MITRE |
| Dynamic DNS, multi-server and Tor | The controller's address can change, and traffic can be routed through Tor, which makes blocking harder | Project page, MITRE |
| Audio and camera | Microsoft says the controller can capture audio and video from the PC | Microsoft |
| Chat window | The server has a window to write to the client | Project page |
| Switching off security software | Microsoft's 2025 entry says it can deactivate security software; the project lists an antimalware start-up option for the client | Microsoft, project page |
| Server-controlled updates | The controller can replace the client with a newer build | Project page |
What Backdoor:MSIL/AsyncRAT can steal or download
What a hidden AsyncRAT can cost you
The risk is a person, not a program: whatever the controller decides to do. These are the documented functions turned into outcomes.
- High
Stolen passwords, accounts and wallets
The keylogger and password recovery read what you type and what browsers, email programs and messengers have saved, and Microsoft lists wallet files. Treat email, banking, work and crypto accounts as exposed from the day the file first ran. This is the money and identity theft that our 2020 guide warned of.
- High
Other malware, including ransomware
Plugins and file transfer let the controller add anything. Microsoft names ransomware deployment as a possible plugin. Our 2020 guide named Wacatac and Copa ransomware as examples; we found no source linking those two to AsyncRAT, so we keep the general risk and not the names.
- High
Your screen, camera, microphone and files
Screen viewing and recording, audio and video capture and the file manager show and take what is on the PC.
- Medium
A way into the rest of your network
Our old guide said a backdoor gives administrator permissions and lets criminals move across the network. AsyncRAT itself only checks whether the user is an administrator (MITRE). But Microsoft's advice on least privilege and on blocking PsExec and WMI is aimed at lateral movement, so on a work network tell IT before you clean anything.
- Medium
Your connection used for someone else
Microsoft says an infected device can become a proxy for more attacks. Our old guide went further and described botnets for spam and DDoS. Botnets are a real use of backdoors, but we found no source for AsyncRAT doing exactly that.
- Low
Damaged Windows files
Our old guide said serious infections can damage system files. Microsoft lists unexpected changes to system files such as the hosts file among the symptoms, but no source says AsyncRAT breaks Windows itself. Check, then reset only if you cannot be sure.
What you may notice, and why you often notice nothing
The most common sign is an alert. Microsoft's entries list the other signs, and none of them is exclusive to this threat.
| Sign | What we found |
|---|---|
| A security alert naming AsyncRAT | The most common sign. Our 2020 guide said many people had seen Defender flag and stop it. Microsoft's names are Backdoor:MSIL/AsyncRAT!MTB and Backdoor:MSIL/AsyncRAT.YA!MTB; other products use their own names |
| Unknown entries in Task Scheduler or unfamiliar background processes | Microsoft's first listed sign; this is how AsyncRAT restarts |
| A new .exe, script or archive in Temp, Public or AppData | Matches the folders Microsoft lists for its payload and for dropped files |
| Unexplained outgoing network connections | A call home to a command server; hard to see without a tool |
| Changed hosts file or startup programs you did not install | Listed by Microsoft as possible signs |
| A slow PC, freezing or crashing programs | Microsoft lists these for the threat; they have many other causes |
| Nothing at all | Common. The client is built to be quiet, and a scan alone can miss an edited build |
How to check the PC for Backdoor:MSIL/AsyncRAT
Where AsyncRAT leaves traces on a PC
These come from Microsoft's two entries, Proofpoint and FortiGuard. Whoever builds a client can change names, folders and servers, so use them as places to look, not as a test that clears you.
- Program file
- An unexpected .exe in a user-writable folder,
%AppData%or%Public%(Microsoft); the name can be anything - Startup
- A scheduled task that starts it at Windows startup or log on, or a value under
HKCU\Software\Microsoft\Windows\CurrentVersion\Run(Microsoft) - Hiding in a trusted process
- Microsoft says the code is injected into a legitimate .NET process such as
RegSvcs.exe; Microsoft's sign is network connections from such local .NET processes to unfamiliar outside addresses - Network
- An encrypted call home to a command server; Proofpoint saw addresses change about monthly and free dynamic DNS used
- Delivery files
- ISO files with generic names such as
Document.isoorpdf.iso(Proofpoint, 2020); an archive with one shortcut and hidden PDFs (FortiGuard, 2026) - Disguised tasks
- In the 2026 campaign, scheduled tasks posing as Realtek audio services and a copy of AutoHotkey renamed to look like audio components
- Defender settings
- The same campaign added
C:\andpowershell.exeto Defender's exclusion lists
Examples of names seen in reports
- SceneServer.exe
- IDM\DwnlData
- AppData\Roaming
- Public folder
- RegSvcs.exe
- Document.iso
- pdf.iso
- Realtek-named scheduled task
- AutoHotkey.exe in an odd folder
- Defender exclusion for C:\
The first two names come from the two alerts in our 2020 pictures and are examples, not signs of every infection. A name from a Windows component is not proof of a clean file: check the folder it runs from.
Which name will your scanner show?
Microsoft's name for Backdoor:MSIL/AsyncRAT is Backdoor:MSIL/AsyncRAT!MTB, Backdoor:MSIL/AsyncRAT.YA!MTB and Trojan:Win32/AsyncRAT.SA.
Defender sorts threats by category first, so the word before the colon tells you what kind of program was found, even if the family name means nothing to you.
Do not search for a removal tool by the detection name alone; fake "removal tools" use the same keywords. How the naming works is explained in our guide to antivirus detection names.
How AsyncRAT gets onto a PC, and why home users are hit too
The sources we read show AsyncRAT being delivered by people, not spreading on its own across the internet (Microsoft's 2025 entry adds that it can propagate through networks once inside). Criminal groups use several routes. Our 2020 guide said it mainly targets organizations; Proofpoint's reports show messages sent to a wide range of recipients, with no industry focus, so home users are affected.
- 1
Phishing email with an attachment
Phishing has been used for years and remains one of the main attack routes for the most common malware. Proofpoint saw TA2719 send ISO attachments named like Document.iso behind lures that spoofed police, banks and parcel services in local languages. MITRE also lists spearphishing attachments and users opening them.
- 2
Archives, shortcuts and scripts
FortiGuard's June 2026 report describes a 7z archive named after an AI guide that holds one shortcut and hidden PDFs; opening the shortcut starts the script chain. MITRE notes that AsyncRAT has been deployed by batch script.
- 3
Software bundles and repacked installers
Microsoft says infection often starts with phishing campaigns or software bundles where the payload pretends to be a legitimate file. Our 2020 guide listed repacked installers and cracks on websites pretending to be legitimate or pirated programs, which fits.
- 4
A second payload from another infection
Our old guide said another backdoor can drop it, and that groups work together. A backdoor does download other malware, and Microsoft names plugins and additional payloads, but we found no report that proves this route for AsyncRAT.
- 5
Software flaws and open Remote Desktop
Our old guide named unpatched software and insecure Remote Desktop connections open to the internet. None of the AsyncRAT sources we read ties it to a particular flaw or to Remote Desktop break-ins. These are real routes for other malware, so they stay in the prevention list, but we do not claim them for AsyncRAT.
Our old guide also named botnets, fake updates and web injects as ways in. We found no source for fake updates or web injects delivering AsyncRAT, so we leave them out of the list above.
Check your PC before you clean it
Our 2020 guide said to read your security software's logs first. Look first, delete later: the folder of the file and the name of its startup entry are what a helper or your IT team will want.
- 1
Read what your security software did
Open Windows Security > Virus & threat protection > Protection history and open the entry. Note the threat name, the file path and whether the status says removed or quarantined. A detection can happen at any time, because the file can arrive by several routes. If another product ran, read its log too.
- 2
Look for leftovers
If the log shows a component that was not removed or was blocked only, the removal is not complete. Keep a screenshot with the exact name, path and time.
- 3
Open Task Manager
Press Ctrl + Shift + Esc, choose Details and look for programs you do not know. Right-click one and choose Open file location. A path under
AppData,PublicorTempfor a program that is not yours is more worrying than one under a program you installed. - 4
Check startup apps and scheduled tasks
In Task Manager choose Startup apps and note entries you do not know. Then press Windows logo + R, type
taskschd.mscand press Enter, open Task Scheduler Library and look for tasks that start at log on with names you do not know, including ones that pose as audio or driver services. - 5
Look at the Run key, without changing it
Press Windows logo + R, type
regedit, openHKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Runand read the values. Note any that point to AppData or Public folders. Leave them until the scans are finished. - 6
Check Defender's exclusions
Open Windows Security > Virus & threat protection > Manage settings > Add or remove exclusions. Our old guide warned that malware may switch Defender off; FortiGuard's 2026 campaign added
C:\andpowershell.exeto the exclusions. An exclusion you did not add is a reason to treat the PC as compromised. Also check that Real-time protection is on. - 7
Look at the connections
Open Command Prompt and run
netstat -ano. An ESTABLISHED line to an address you do not know is worth noting; runtasklist /fi "PID eq 1234"with the number from the last column to see which program owns it. The server address can change, so a clean list proves nothing. - 8
Ask where it came from
A file from an email attachment, an ISO or archive, a cracked program or a download just before the first alert is the likely route. A PC at work is a case for your IT team, not for a clean-up on your own.
How to remove Backdoor:MSIL/AsyncRAT
How to remove Backdoor:MSIL/AsyncRAT and lock the attacker out
Someone may have had remote control of the PC.
Cut the connection first, then remove the trojan and secure your accounts.
Step 1: Remove remote access tools and lock the attacker out
Attackers keep access through remote control tools and extra user accounts. Disconnect the PC from the internet, then remove every remote access program you did not install yourself from the installed apps list in Windows 11 or Windows 10.
Look for a user account you do not know and delete it, and switch off Remote Desktop in Settings > System. Reconnect only for the scan.
Full procedure with screenshots: Uninstall a program or app in Windows On uGetFix
Step 2: Delete scheduled tasks that bring it back
Programs like Backdoor:MSIL/AsyncRAT add a scheduled task so they return after an uninstall or reopen a page at every sign-in. Start Task Scheduler, open Task Scheduler Library and sort by Last Run Time to see what ran recently.
On the Actions tab, a program in a user folder, a script or a web address is a warning sign; right-click such a task and choose Delete.
Tasks with names copying Google, Edge or Windows updaters but pointing to an odd folder are typical. The tool looks the same in Windows 11 and Windows 10.

Windows 11: Task Scheduler Library, the task selected, the Actions tab shows the file it runs. Full procedure with screenshots: Remove what malware leaves behind in Windows
Step 3: Remove it from startup
Press Ctrl + Shift + Esc to open Task Manager and select Startup apps (Windows 11) or the Startup tab (Windows 10). Disable entries you do not recognise, especially ones with no publisher or with a name that copies a Windows component.
Right-click an entry and choose Open file location to see where it runs from: programs in
%AppData%or%Temp%deserve a closer look. Some entries are not listed there but in the registry Run keys, which the procedure below shows how to check.Full procedure with screenshots: Stop apps from opening at startup On uGetFix
Step 4: Scan the PC, then run the offline scan
A scan finds the parts of Backdoor:MSIL/AsyncRAT that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Step 5: Change passwords from another device and sign out other sessions
Backdoor:MSIL/AsyncRAT can copy saved passwords, cookies and session tokens and send them out in seconds, so cleaning the PC does not undo the theft.
Change your passwords on a device that was never infected, starting with the e-mail account, since every other reset goes through it. On each account, end all other sessions and check the recovery e-mail, phone number and forwarding rules.
Then turn on two-step verification. Sign in on the Windows 11 or Windows 10 PC again only after the offline scan is clean.
Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Remove Backdoor:MSIL/AsyncRAT from Windows 11 and Windows 10
Do the steps in order. We did not run them against a live infection; they follow Microsoft's entries and Windows support pages. Because a person may have been in control of the PC, the account steps in the next chapter are not optional.
- 1
Disconnect the PC from the network
Turn off Wi-Fi and unplug the cable. Microsoft's first step is to disconnect from all networks, which also cuts the controller off. Our old guide gave the same advice. On a work network, call IT first so other PCs can be checked.
- 2
Change your passwords from another device
Use a phone or another PC that has never been near the infected one. Change your email first, then banking and everything else, and turn on two-step sign-in. Microsoft says to change all passwords used or stored on the infected device from a clean one. If the PC logged your keys, new passwords typed on it go to the controller.
- 3
Back up documents only
Copy documents and photos, not programs, to an external drive that you unplug afterwards. Programs and files in downloads can carry the infection.
- 4
Start in Safe Mode with Networking
Open Settings > System > Recovery, click Restart now beside Advanced startup, then choose Troubleshoot > Advanced options > Startup Settings > Restart and press 5 for Safe Mode with Networking. Microsoft says it adds the network drivers you need to reach the internet. Our old guide used it so the security program cannot be interrupted if malware is tampering with it.
- 5
Update the definitions and run a full scan
Open Windows Security > Virus & threat protection > Protection updates > Check for updates. Then go to Scan options, select Full scan and click Scan now. Microsoft says Defender removes threats it detects but that many infections leave remnant files and changes, and that updated definitions and a full scan might help address them. Follow what the scan finds and do not restore what it quarantines.
- 6
Run Microsoft Defender Offline
In Scan options choose Microsoft Defender Offline scan and Scan now. Save your work first: Microsoft says you are signed out and Windows restarts into an isolated environment to look for persistent malware. Afterwards open Protection history to read the result.
- 7
Scan once with a second scanner
Microsoft's built-in scanner may miss components, and our old guide said to scan with a second program as well. Use one on-demand scanner from a known vendor, from its own site, and do not run two with live protection at once. A second clean result still does not prove the PC is clean.
- 8
Delete what you found, carefully
Microsoft's list: remove startup entries under the Run key that point to malicious files, and delete malicious tasks in Task Scheduler. Delete only what leads to a file you do not know. If you are unsure, leave it and use the reset below.
- 9
Update Windows and your programs
Open Settings > Windows Update and install everything offered, and update Office, your browsers and PDF readers.
- 10
Reset Windows if you cannot be sure
Our old guide said victims sometimes have to reinstall Windows, and that malware can damage Windows parts in ways security programs do not always repair. If the PC holds banking, work or private data, or the alert came back, back up documents and use Settings > System > Recovery > Reset this PC and choose Remove everything. Restore documents only.
System Restore: our old guide offered it as a second method. We did not find Microsoft or any vendor naming it for this threat, and a restore point made after the infection can bring the malware back with it. Use it only as a last step, and scan again straight after. Do not install a removal tool from a pop-up message, and never pay or call a number shown in an alert.
After removal: passwords, accounts and prevention
Your passwords after Backdoor:MSIL/AsyncRAT
Removing Backdoor:MSIL/AsyncRAT does not undo what it may already have sent out while the PC showed A Defender alert naming Backdoor:MSIL/AsyncRAT, or an unknown program in AppData or Public in the list of installed apps. Treat saved browser passwords and logged-in sessions on this PC as known to the attacker.
From another device, change the e-mail password first and end all its sessions. Then do the same for the bank, PayPal, Microsoft, Google and Apple accounts. Stolen session cookies keep working after a password change until you sign out everywhere.
Move crypto to a new wallet created on a clean device. A step-by-step order for every kind of account is in our guide to account security after an infection.
If it was real: what to do about your accounts
The scans deal with the PC. These steps deal with what the controller may have seen, and they matter most if you ran the file.
- 1
Sign out everywhere
Use the sign out of all sessions option in your Google, Microsoft, social and work accounts so stolen cookies and tokens stop working.
- 2
Look at your email rules and recovery details
In your email account, check forwarding rules, the recovery email and phone number, and the list of signed-in devices. Remove what you did not set.
- 3
Check your money and wallets
Look at card statements for payments you did not make and ask your bank if you typed card details on that PC. Microsoft lists cryptocurrency wallet files among the data it can take: move funds to a new wallet created on a clean device.
- 4
Watch for phishing and identity theft
Our 2020 guide warned of phishing and identity theft after a leak. Expect messages that use details taken from your PC, and be careful with calls claiming to be your bank.
- 5
Look for other malware and ransomware
Check whether documents were renamed or a note file appeared. If so, do not pay and do not reinstall yet; identify the family first.
- 6
Tell the people who may be affected
If the PC is used for work, tell your employer. If you used saved passwords for a shared account, tell its other users.
- 7
Scan again in a week
Run a full scan and a Microsoft Defender Offline scan again, and look at the startup entries and exclusions once more.
Could AsyncRAT be there on purpose?
Possibly, in a lab or by an administrator. Our 2020 guide said remote access tools are legitimate and can be misused. What matters is who installed it and whether you were told.
| Points to a legitimate use | Points to an intruder |
|---|---|
| You or your IT team set it up and a record of the install exists | You never installed it and nobody told you |
| It runs on a test PC or lab machine that holds no private data | It sits on a PC with banking, work or private accounts |
| The file is in a folder you chose, from a build you made | The file is in AppData, Public or Temp with an odd name, or arrived by attachment, ISO or download |
| The project's own disclaimer is met: you own the system or have explicit permission | The software came from a crack, a repacked installer or a fake AI guide |
The author's disclaimer says the software must not be used on systems you do not own or have permission to operate. A tool that hides itself on a PC where nobody was told is not a monitoring policy. If you cannot find who put it there, treat it as an intruder.
Keep a remote access trojan off your PC
Our 2020 advice was to use security software, patch and learn to spot phishing. It still holds; here it is with Microsoft's current list.
Do
- Keep Microsoft Defender or another security product with Real-time protection on, and keep it up to date.
- Install Windows Update monthly and update Office, browsers and PDF readers.
- Open attachments only when you expected them. Be wary of ISO files, archives with a single shortcut and parcel or bank notices you did not expect.
- Use a standard Windows account for daily work, not an administrator account (Microsoft's least-privilege advice).
- On a business network, block Office programs from starting other programs and restrict PsExec and WMI, as Microsoft advises.
- If you use Remote Desktop, do not expose it to the internet; put it behind a VPN and give those accounts strong passwords.
- Keep a backup of documents on a disk you unplug (File History or OneDrive), so you can reset Windows without losing them.
- Use a password manager and two-step sign-in so one stolen password does not open every account.
Don't
- Do not run cracked programs, repacked installers or files from torrents.
- Do not open a shortcut inside an archive that claims to be a book or guide.
- Do not add an exclusion in Defender for a file until its maker has confirmed that it is clean.
- Do not leave Remote Desktop open to the world.
- Do not run two antivirus programs with live protection at once.
- Do not pay for a removal program that appears in a pop-up; the scan tools in Windows are free.
Questions about Backdoor:MSIL/AsyncRAT
What is Backdoor:MSIL/AsyncRAT?
Backdoor:MSIL/AsyncRAT is Microsoft Defender's name for a file built from AsyncRAT, a free, open-source remote access tool for Windows written in C#. The author says it was made to monitor and control other computers over an encrypted connection, and the project has been public on GitHub since January 2019.
Microsoft calls its detections a persistent backdoor whose goal is a hidden, lasting channel for remote control. MSIL means the program is .NET code, and the exclamation mark and MTB mean it was flagged by behavior. On a PC you do not manage yourself, it is an intruder, because someone has to deliver the file for it to run.
Is AsyncRAT a virus?
AsyncRAT is a remote access trojan, not a virus in the strict sense, because the reports we read show it delivered by people, for example by an email attachment, an archive or a software bundle, and not spreading by itself between PCs (Microsoft adds that it can propagate through a network once inside).
The program is not malicious by design: the author's disclaimer calls it educational and says it must be used only on systems you own or may operate. What makes it malware is how it is used.
When a copy runs on your PC without your knowledge, it gives the person in control your screen, your keystrokes and your files, so security products treat it as a trojan.
What does the !MTB at the end of the name mean?
The !MTB suffix stands for Machine Threat Behavior. Microsoft explains that it means the antivirus engine flagged the file by what it does, its sequence of actions or code patterns, and not by one known file signature. That is why the name appears on many different files: Microsoft says the open-source origin led to many obfuscated variants.
A detection with this suffix is a strong warning, but it can occasionally fire on a harmless program, so check the file path and where the file came from. A file in AppData or Public that you did not install is more worrying than one in a program folder you know.
How do I know if AsyncRAT is on my PC?
You may not know, because the client is built to run quietly. The signs Microsoft lists are an alert naming the threat, unknown entries in Task Scheduler or the Run key, new .exe files in Temp, Public or AppData folders, unexplained outgoing connections, a changed hosts file and sometimes a slow PC.
Open Task Manager, check Startup apps and Task Scheduler, and run netstat -ano. Also look at Defender's exclusions for entries you did not add.
A clean look proves nothing, because edited builds change names and servers. If you suspect it, change your passwords from another device and scan.
How do I remove AsyncRAT from Windows 11 or 10?
Disconnect the PC from the network, change your passwords from another device and start Windows in Safe Mode with Networking. Then update Defender's definitions, run a Full scan and a Microsoft Defender Offline scan, and read Protection history.
Remove startup entries and scheduled tasks that point to files you do not know. Scan once more with a second on-demand scanner from a known vendor. Because a person may have controlled the PC, finish with the account steps:
- sign out everywhere
- check email rules
- your money
If you cannot be sure, back up documents and use Reset this PC with Remove everything.
Did Microsoft Defender already remove it?
Possibly, but do not assume so. Microsoft says Defender removes threats as it detects them, yet many infections leave remnant files and system changes, and updated definitions plus a full scan might help address them. Open Windows Security, then Virus and threat protection, then Protection history and read the entry: the status should say removed, not only quarantined or blocked.
If a component was not removed, the removal is not complete. Our 2020 guide warned that some malware also disables Defender, and a 2026 campaign added exclusions to it, so check that real-time protection is on and that no exclusions are yours to explain.
What can AsyncRAT see and steal?
AsyncRAT can show the controller your screen, record it, log every key you press and read passwords saved in browsers, email programs and messengers. Microsoft also lists cryptocurrency wallet files and audio and video capture.
It can send and receive files over SFTP, report which security software you run and add plugins, which Microsoft says can bring exploits, proxy use or ransomware. Not every build keeps every function.
Treat your email, banking, work and crypto accounts as exposed if the file ran, and move to new passwords and a new wallet from a clean device before you do anything else on the infected PC.
How does AsyncRAT get onto a computer?
Someone has to deliver the file. Proofpoint saw ISO attachments sent in local languages, with lures that spoofed police, banks and parcel services.
A June 2026 campaign hid it in 7z archives named after AI guides, containing one shortcut that starts a script chain. Microsoft names phishing campaigns and software bundles, and MITRE adds batch scripts. Our 2020 guide also listed cracks and repacked installers.
We found no source tying it to a particular software flaw or to Remote Desktop break-ins, so those stay as general advice. Home users are targeted as well as companies, because the emails go to wide lists.
Do I need to reinstall Windows after an AsyncRAT infection?
Not always, but it is the safest choice when the PC holds banking, work or private data. A remote access trojan lets a person act on the PC, and edited builds are made to be missed, so a clean scan does not prove that everything is gone.
If the alert came back after cleaning, or you find a task, an exclusion or a startup entry you cannot explain, reset. Back up documents only, open Settings, System, Recovery, Reset this PC, and choose Remove everything. Then restore documents, install Windows updates and change your passwords again from the clean system.
Will Fortect remove Backdoor:MSIL/AsyncRAT?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Backdoor:MSIL/AsyncRAT, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Microsoft Security Intelligence: Backdoor:MSIL/AsyncRAT!MTB (published 18 May 2020, updated 2 December 2025) (read October 6, 2026)
- Microsoft Security Intelligence: Backdoor:MSIL/AsyncRAT.YA!MTB (published 21 May 2019, updated 3 December 2025) (read October 6, 2026)
- Microsoft Security Intelligence: Trojan:Win32/AsyncRAT.SA (published 18 November 2025) (read October 6, 2026)
- MITRE ATT&CK: AsyncRAT, software S1087 (last modified 12 May 2026) (read October 6, 2026)
- GitHub: NYAN-x-CAT/AsyncRAT-C-Sharp, project page (read October 6, 2026)
- Proofpoint: Threat Actor Profile: TA2719 Uses Colorful Lures to Deliver RATs in Local Languages (26 August 2020) (read October 6, 2026)
- Daily CyberSecurity: AsyncRAT AI Lures Target Users Hunting AI Skills (18 June 2026, on FortiGuard Labs' research) (read October 6, 2026)
- Spamhaus: Botnet Threat Update Q2 2020 (read to check our 2020 botnet claim; AsyncRAT is not named in the text) (read October 6, 2026)
- Microsoft Support: Windows startup settings (Safe Mode with Networking) (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline scan in Windows (read October 6, 2026)
- Microsoft Support: Virus and threat protection in the Windows Security app (read October 6, 2026)