
Christmas virus: how to spot it and what to do
Christmas virus describes seasonal cyber threats including ransomware and trojans exploiting holiday themes for distribution.
Facts checked October 11, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
Do it yourself · free Remove Christmas virus yourself 4 steps, about 12 minutes, no software needed.
Start the steps
Christmas virus: summary
| Name | Christmas virus |
|---|---|
| Type | Phishing message |
| Symptoms | A phishing e-mail asking you to sign in |
| Evidence | 8 write-ups by security sites; details still limited |
| Arrives as | |
| Pretends to be | A well-known company |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 5 more facts
| Claim | Your account needs urgent attention |
|---|---|
| Sender domain | customer.support@amazonn.com |
| Asks for | Your password |
| First seen | 18 December 2018 |
| Facts checked | 5 October 2026 |
What the Christmas virus message looks like
Text of a phishing e-mail asking you to sign in, as people saw it
From the heart, Happy new year!
Lascivious Christmas infection and the merry christmas.apk virus: what these names mean
We found no reliable source that names a virus called Lascivious Christmas infection, also searched as lasciviouschristmasinfection.
No security vendor, Microsoft detection name or abuse.ch record uses it. Our reading: it is a joke label, a prank file name or a lure in a seasonal message, not a separate malware family. Treat any file, link or message carrying that name like the other Christmas lures on this page: do not open it, and scan the device if you already did.
A file called merry christmas.apk is an Android app package, so it cannot run on a Windows PC. We found no vendor report on an APK with exactly that name.
SonicWall Capture Labs did analyse Christmas themed Android apps in 2019: a live wallpaper flagged as AirPush adware, and a holiday game that placed a shortcut on the home screen and then tried to install another APK from outside Google Play.
If you installed an unknown Christmas APK on Android, open Settings, then Apps, find the app and tap Uninstall. Then open Settings and search for Install unknown apps, and switch that permission off for your browser and messaging apps.
Also check Device admin apps in the security settings and remove anything you do not recognise. Run Google Play Protect from the Play Store menu. Only install seasonal games and wallpapers from Google Play.
From our report of Dec 2018 · not reviewed since
Christmas virus distribution methods
As evident, the main culprit in Christmas virus distribution is the fake emails.
Users are sometimes redirected to a malicious website via a hyperlink or click on an attachment that holds macro scripts. We suggest you follow these simple tips if you want to avoid being tricked by a phishing email:
All in all, experts advise users to be vigilant, and always go by the rule "If it is too good to be true, it probably is."
- Do not jump into the email contents straight away. First, example the email address of the sender, as well as the subject line. These two simple checks might straight away disclose the deception. For example, an email from customer.support@amazonn.com might be easily interpreted as an original one.
- The contents of the email might look very legit, with correct logos and formatting. However, make sure you carefully read through it and make some conclusions. You can ask yourself these questions: "why did this company send me an email? was I expecting it?." In some cases, you will answer yes, but then you should proceed with the more advanced examination.
- Phishing emails usually contain a link or n attachment that might be disguised as a .pdf, .doc, .txt, .html, and other documents. Before opening them, make sure you scan them using reputable security software.
- When it comes clicking on hyperlinks, hover your mouse over it and see where it is actually bringing you.
- Call the company that is trying to contact you or go to the official website, and use the email address provided there.
How to tell the Christmas virus message is fake
What readers reported about Christmas virus
Some company installed protection software on my computer. I was contacted by phone a company claiming over 2000 hacking attempts over Christmas and New Year. They claimed to install a special software to protect my system. Am I infected? I am using Toshiba laptop.
Help. It's not funny. Got hit by MerryChristmas ransomware. So I have just accidentally infected my computer with some ridiculous merrychristmas ransomware, guys. It replaced by desktop wallpaper with a huge christmas-themed picture. It wants me to write to for help. What am I supposed to do??
Files corrupted. .merry file extensions?. Hi, can you explain what happened? I see a suspicious screen with Christmas uncle on it. My files are somehow corrupted, and I cannot open them. they also have .merry file extensions now. how do i delete this .merry virus and fix my files? thnx
What is Christmas ransomware?. Christmas ransomware? Is it real?! I think I got infected with this virus. How can I remove it?
From the comments under our earlier guide; names and contact details removed.
- Sender:
customer.support@amazonn.com
From our report of Dec 2018 · not reviewed since
More from our earlier report on Christmas virus
- Ransomware, worm, trojan, scam, etc.
- Spam emails, although can use brute-force attacks, fake updates, malicious executables, etc.
- Vary, depending on the infection
- Use anti-malware software like or
Is Christmas virus dangerous? What the senders want
From our report of Dec 2018 · not reviewed since
Christmas virus is a set of cyber infections that are related to festive period
Christmas virus is a term used to describe multiple different cyber threats that are related to Christmas.
Therefore, the array of infections can vary, including worms, ransomware, trojans, as well as social engineering attacks via emails and social networks. The variety of viruses have a different goal, but, nevertheless, most of them are malicious and should be avoided at all costs. The majority of Christmas viruses are spread with the help of spam emails, although other propagation methods, like fake updates, can be used as well.
Because the term describes multiple different infections, there are different ways of dealing with it. However, the best way to remove Christmas virus is by employing reputable security software that can detect and clean the system from malicious software. We highly recommend using or for the job, although any other powerful anti-malware tool should do the job.
Some infections, such as ransomware, leave the devastation behind, even after victims remove Christmas virus. Ransomware locks up personal data and demands a ransom to be paid for its release. Thus, file recovery needs to be performed in order to get access to the encoded data.
Below are some of the examples of Christmas virus, and we hope that you will be able to protect your privacy and online security this Christmas with the help of this article!
From our report of Dec 2018 · not reviewed since
Christmas Tree EXEC
The very first holiday season malware appeared back in 1987 when a German student who initially claimed that he only wanted to wish Season's Greetings to friends.
The worm, written in Rexx language, used to be sent to an inbox with the subject line "Let this exec run and enjoy yourself!", and, once the victim typed CHRISTMAS as instructed, the virus sent drew a Christmas Tree as text graphics, and sent out its copies to everybody in the target's contact's file.
Ultimately, the Christmas Tree EXEC worm managed to paralyze international networks, and some 350,000 machines were shut down by IBM.
From our report of Dec 2018 · not reviewed since
WM97/Melissa-AG or Prilissa
Prilissa is one of the old Christmas viruses, that was first detected back in 1999.
It is as well propagated with the help of spam emails with the subject line "Message from ." The malicious DOC file, once executed, infects the machine with malware that would trigger on 25th of December.
Prilissa opens pop-up windows, inserts randomly colored squares into the opened MS Word document, and attempts to wipe out the C: drive upon next reboot.
From our report of Dec 2018 · not reviewed since
The Maldal virus
The Maldal virus was injected into victims' machines once they opened a Christmas.exe file.
The phishing email came with "Happy New Year" subject line and seemed like a Season's Greetings electronic card, which most people fell for.
Once executed, the malware opened a window that displayed a Santa Claus with a reindeer, sliding on his skis with a message at the bottom:
From our report of Dec 2018 · not reviewed since
Koobface worm
Koobface malware was targeting users of social networks like Facebook, Skype, Twitter, and redirected victims to a spoofed Santa-themed web page.
Soon after the infiltration, it starts its malicious activity - it is capable of stealing login information of various accounts, as well as banking information, which can result in money loss for victims.
Additionally, Koobface forms a peer-to-peer botnet that propagates the malware even further.
From our report of Dec 2018 · not reviewed since
MerryChristmas ransomware
MerryChristmas ransomware is a file locking virus, as well as data stealing malware that first appeared in January 2017.
While it is strange that malware with such name appeared in January, it is believed that it is of Orthodox origin, as Christmas is celebrated on 7th of January.
The virus was distributed with the help of spam campaign - one came from the alleged Federal Trade Commission, while the other one pretended to be a notice from the court. The email embedded a hyperlink that downloaded a zip file disguised as a PDF document.
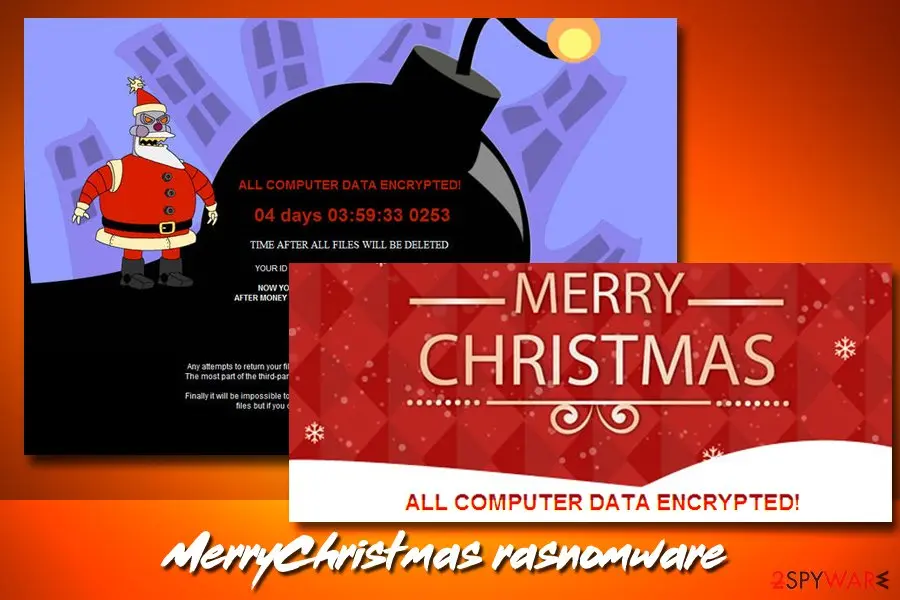
As soon as the machine gets infected, all personal videos, music, pictures and similar files are encoded, and an appendix is added. Additionally, users can view a ransom note that shows Santa Claus from Futurama and displays a timer.
Allegedly, after it expires and no payment in Bitcoin will be transferred, all the data on the machine will be erased. Nevertheless, users should not pay the ransom and instead use official decryptor that is available to download on our main article page.
From our report of Dec 2018 · not reviewed since
Stay away from Christmas gift and similar scams
Low profile cyber criminals and people who want an easy profit often rely on scams.
The following are most prominent Christmas virus scams that should not be overlooked this Christmas.
From our report of Dec 2018 · not reviewed since
Christmas Day Bonus Gift email virus
Christmas Day Bonus Gift email virus is a spam email campaign that aims to distribute a data-stealing trojan Ursnif.
Users receive an email into their inboxes that claims that they are entitled to a Christmas bonus. In order to claim it, they are meant to click on a provided link. As soon as they click on the link, they are led to a Google doc, which is an executable file. Once executed, it will install Ursnif trojan that can record keystrokes, system information, and other sensitive data.
From our report of Dec 2018 · not reviewed since
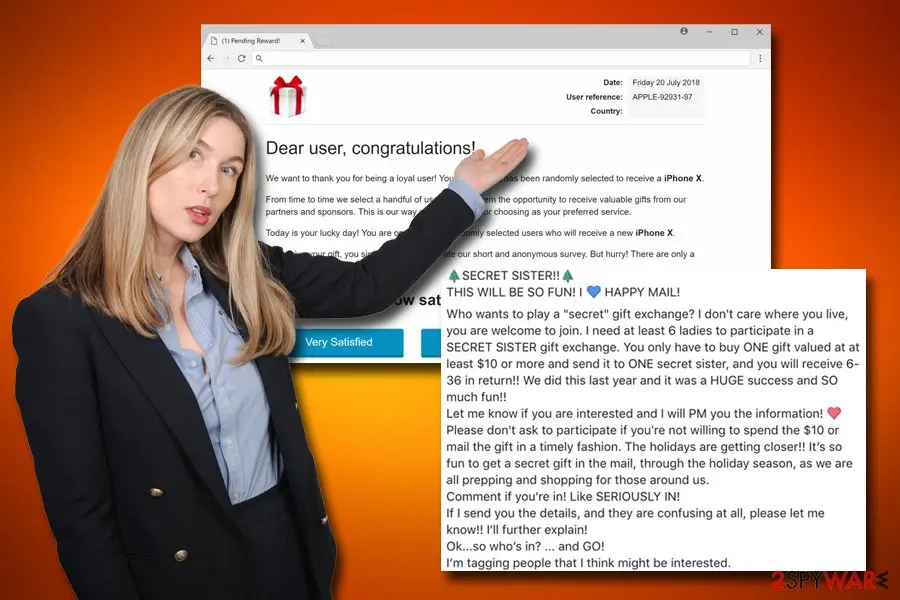
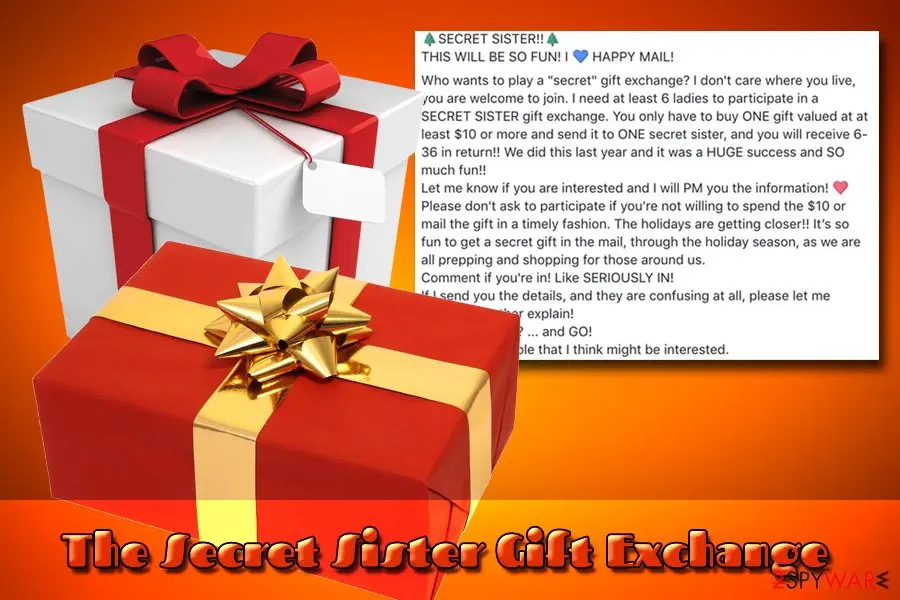
The Secret Sister Gift Exchange scam
This Christmas scam has been active since 2015, and it seems like it is not going away three years later.
The hoax is prevalent on social media platforms like Facebook or Twitter. It operates a "pyramid scheme." It promises that you will be able to receive 36 gifts in exchange for just one. While it sounds too good to be true, it really is.
In reality, it is merely a scam that asks victims to send $10 via the spoofed website. Do not participate in The Secret Sister Gift exchange scam, and rather buy presents who you actually care about this festive season.
From our report of Dec 2018 · not reviewed since
Amazon scams
Amazon scams, such as Amazon Gift Card, Amazon Membership Rewards, Congratulations Amazon User and many others, are designed to trick people into either providing sensitive information that can be used for marketing purposes, or installing bogus software, subscribing for useless services, and such. Ultimately, users end up wasting money and simply being scammed by cyber crooks.
The most recent Amazon scam which you might encounter while shopping for presents is masked as an email coming from the industry giant itself. Allegedly, users are informed that a Prime membership was purchased, and, in order to cancel it, they have to log in using their Amazon account credentials. As evident, bad actors' goal is to get access to the official account.
From our report of Dec 2018 · not reviewed since
Extortion scams
Extortion scams have been extremely prevalent since mid-2018, and the number of users reporting these incidents increased drastically.
Initially, sextortion scams were employed for blackmail. The crooks claim that they injected malware into the targeted computer, which allowed them to record users via the camera while they were watching porn online.
Crooks typically use information that was obtained from previous data breaches (such as email address and password) to make the hoax email more believable. Malicious actors ask users to pay a certain amount of Bitcoin, or else the recorded shameful videos would be sent to victims' friends and family.
The most recent scam evolves bomb threats and asks users to pay as much as $20,000 in order to save hundreds of people from bomb's detonation.
What to do after the Christmas virus e-mail
If you only received the message and clicked nothing, step 3 is all you need.
If you clicked the link or typed anything on the page it opened, do every step, starting with the password.
Step 1: Change the password you typed on the fake page
If you typed a password on the page the Christmas virus message opened, assume the sender has it. Go to the real site by typing its address yourself and change the password there, choosing one you have never used.
Change it anywhere else the same password was used, and sign out all other sessions if the service offers it. Any browser on Windows 11 or Windows 10 will do, as long as you do not follow the e-mail's link.
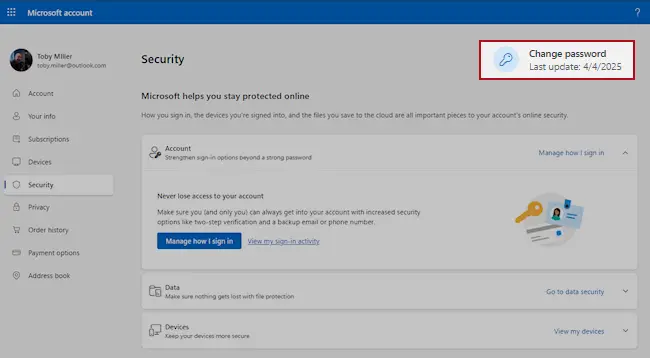
Microsoft account, Security page (account.microsoft.com/security): Change password. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 2: Turn on two-step verification
With two-step verification on, a stolen password alone no longer opens the account, because a sign-in from a new device also needs a code from your phone.
Switch it on for the e-mail account first, then for banking, shopping and social accounts that use that address.
Check the recovery phone, the recovery e-mail and any forwarding rules while you are in the settings, since attackers change them to come back. The pages are the same on Windows 11 and Windows 10.
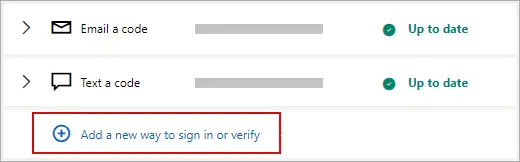
Microsoft account: Manage how I sign in, where two-step verification and the sign-in methods are. Full procedure with screenshots: Turn on two-step verification / secure a hacked account
Step 3: Report the e-mail and delete it
Do not reply and do not click anything else in the message. In Outlook select the e-mail and choose Report > Report phishing; in Gmail open the three-dot menu next to Reply and pick Report phishing.
That trains the filter for everyone on the service, and the message goes to the junk folder. If the e-mail came to a work address, forward it to your IT team as an attachment first.
The steps are the same in the web mail and the mail apps on Windows 11 and Windows 10.
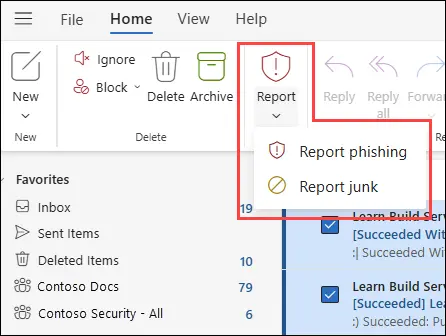
New Outlook for Windows and Outlook on the web: Report > Report phishing. Full procedure with screenshots: Report a phishing e-mail
Step 4: Scan the PC if you opened a file from the message
A fake sign-in page only steals what you type, so most readers can skip this step. If the Christmas virus e-mail made you download or open a file, delete it and scan the PC.
In Windows Security > Virus & threat protection > Scan options, run a Full scan and then Microsoft Defender Antivirus (offline scan) > Scan now. The offline scan restarts Windows 11 or Windows 10 and takes about 15 minutes.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Manual removal using Safe Mode
Important! →
Manual removal guide might be too complicated for regular computer users. It requires advanced IT knowledge to be performed correctly (if vital system files are removed or damaged, it might result in full Windows compromise), and it also might take hours to complete. Therefore, we highly advise using the automatic method provided above instead.
Step 1. Access Safe Mode with Networking
Manual malware removal should be best performed in the Safe Mode environment.
Windows 7 / Vista / XP
- Click Start > Shutdown > Restart > OK.
- When your computer becomes active, start pressing F8 button (if that does not work, try F2, F12, Del, etc. - it all depends on your motherboard model) multiple times until you see the Advanced Boot Options window.
- Select Safe Mode with Networking from the list.

Windows 10 / Windows 8
- Right-click on Start button and select Settings.

- Scroll down to pick Update & Security.

- On the left side of the window, pick Recovery.
- Now scroll down to find Advanced Startup section.
- Click Restart now.

- Select Troubleshoot.

- Go to Advanced options.

- Select Startup Settings.

- Press Restart.
- Now press 5 or click 5) Enable Safe Mode with Networking.

Step 2. Shut down suspicious processes
Windows Task Manager is a useful tool that shows all the processes running in the background. If malware is running a process, you need to shut it down:
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Click on More details.

- Scroll down to Background processes section, and look for anything suspicious.
- Right-click and select Open file location.

- Go back to the process, right-click and pick End Task.

- Delete the contents of the malicious folder.
Step 3. Check program Startup
- Press Ctrl + Shift + Esc on your keyboard to open Windows Task Manager.
- Go to Startup tab.
- Right-click on the suspicious program and pick Disable.

Step 4. Delete virus files
Malware-related files can be found in various places within your computer. Here are instructions that could help you find them:
- Type in Disk Cleanup in Windows search and press Enter.

- Select the drive you want to clean (C: is your main drive by default and is likely to be the one that has malicious files in).
- Scroll through the Files to delete list and select the following:
Temporary Internet Files
Downloads
Recycle Bin
Temporary files - Pick Clean up system files.

- You can also look for other malicious files hidden in the following folders (type these entries in Windows Search and press Enter):
%AppData%
%LocalAppData%
%ProgramData%
%WinDir%
After you are finished, reboot the PC in normal mode.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
From our report of Dec 2018 · outdated details corrected in October 2026
Get rid of Christmas virus and protect yourself from cyber infections in the future
In most cases, scamming attempts can be noticed straight away, as fake messages are usually littered with grammar and spelling mistakes, or terrible formatting.
However, some hoax messages sent via Facebook or other platforms might seem legitimate, and some people might fall for the trick. To avoid such consequences, we suggest you search online for the information. Simply copy the first line of the email or message and search for it. There will be plenty of blogs, forums posts, articles, and similar data regarding the threat.
Do not forget that scam messages often trick users into installing viruses. In such a case, Christmas virus removal must be performed. However, because Christmas malware can be related to so many different threats, it's elimination instructions can differ.
Nevertheless, the most optimal solution would be scanning your machine with security software like , , or . The scans will find any malicious files embedded into the system and safely eliminate them.
In some cases, you can remove the Christmas virus manually. In case you installed bloatware like Power System Care, MyShopcoupon, Safe PC Cleaner, and similar, you can get rid of all the files manually via the Control Panel (Windows) or Applications folder (macOS). Additionally, you might have to reset each of the affected browsers, such as Google Chrome, Mozilla Firefox, Safari, Opera, or others.
Nevertheless, if you are dealing with a severe Christmas virus infection, you should enter Safe Mode with Networking in case malware is interfering with AV engine's operation.
[GI=method-1]To remove Christmas virus from your machine safely, enter Safe Mode with Networking on your Windows device:
[GI=method-2]System Restore is also a very useful feature that might get rid of the Christmas virus:
Questions about Christmas virus
What is Christmas virus?
Christmas virus is an umbrella term describing multiple seasonal cyber threats including ransomware, trojans, worms, and social engineering attacks. The category encompasses diverse infections sharing festive-themed delivery methods or content. Threats range from file-locking ransomware (MerryChristmas 2017) to info-stealing trojans (Ursnif).
Distribution methods include spam emails with deceptive subject lines, fake software updates, and social engineering via social media. The first documented instance was the 1987 Christmas Tree EXEC worm sent to inboxes as a greeting that paralyzed international networks affecting 350,000 machines. Modern Christmas viruses exploit holiday shopping and gift-giving psychology to trick users into clicking dangerous links.
Are there many types of Christmas viruses?
Yes, Christmas virus refers to multiple threat families rather than single malware. Historical examples include the 1999 Prilissa virus delivered via email and the Maldal virus disguised as digital greeting cards.
Modern threats include MerryChristmas ransomware (first seen January 2017), Koobface worm targeting social networks, and numerous Christmas-themed scams. Each variant operates differently—some encrypt files, others steal credentials, some spread worms. Distribution methods vary from email attachments to social media exploitation.
Scams range from fake gift exchanges to bomb threat extortion demands. The diversity makes Christmas virus a category description rather than specific threat identifier. Comprehensive security software protects against all variants through multiple detection engines.
What are the most famous Christmas viruses in history?
The 1987 Christmas Tree EXEC worm was the first documented seasonal virus, paralyzing international networks and shutting down 350,000 IBM machines. The 1999 Prilissa virus executed on December 25th after spreading via email.
The Maldal virus (1990s) appeared in fake greeting card executables displaying Santa Claus with skis. Koobface malware (2008) targeted Facebook and Skype users, stealing credentials and forming botnets. MerryChristmas ransomware (2017) encrypted files and displayed timers with Santa imagery, demanding Bitcoin ransom.
The Christmas Day Bonus Gift trojan (2016) distributed Ursnif data-stealing malware through fake bonus emails. Each demonstrated increasingly sophisticated social engineering exploiting holiday emotions and expectations to spread infections.
How does Christmas virus spread to computers?
Christmas viruses primarily spread through spam emails with festive subject lines like "Holiday Greeting" or "Christmas Gift." Email attachments contain malicious executables, Word documents with macros, or PDF files triggering drive-by downloads.
Phishing emails impersonate legitimate organizations or individuals. Compromised websites hosting malware downloads provide infection vectors. Social media spreads scams through fake gift exchange or financial opportunity messages.
Fake software updates on legitimate-appearing websites trick users into downloading trojans. Social engineering exploits holiday shopping and financial stress to create urgency. Exploit kits automatically deploy malware without user interaction on vulnerable systems.
Weak passwords enable brute-force access during holiday neglect. To prevent infection, avoid email attachments from unknown senders, skip suspicious links, update software for patches, and maintain antimalware protection.
Should I be concerned about Christmas scams online?
Yes, Christmas scams increase significantly during holiday seasons. The Secret Sister Gift Exchange scam promises receiving 36 gifts for one, operating as pyramid scheme requiring $10 payments through spoofed websites. Amazon impersonation scams trick users into entering credentials for fake membership purchases.
Sextortion scams use data from previous breaches claiming malware recorded users watching pornography, demanding Bitcoin under threats of exposure. Bomb threat extortion demands $20,000 in Bitcoin to prevent alleged detonations. These scams prey on holiday shopping mentality and good will toward gift exchange.
Financial losses result from direct payments or credential theft. Protect yourself by avoiding promises that sound too good, verifying sender authenticity, never sharing personal information unsolicited, and reporting suspicious emails to appropriate authorities.
How do I protect my computer from Christmas viruses?
Employ comprehensive security measures during holiday season. Download reputable antimalware software with real-time protection and keep it updated. Update Windows and all applications regularly for security patches.
Use strong, unique passwords with two-factor authentication. Be suspicious of emails with holiday-themed subject lines from unknown senders. Avoid clicking links or opening attachments from unverified sources.
Don't download files from unfamiliar websites. Use Advanced installation settings for software to avoid bundled threats. Enable browser security features and pop-up blockers.
Perform regular system scans and backups. Educate yourself about common scams and social engineering. When in doubt about emails or links, contact organizations directly through verified phone numbers or official websites rather than using provided links.
Can I recover files from Christmas ransomware like MerryChristmas?
Recovery depends on infection type and available backups. MerryChristmas ransomware encrypts files making them inaccessible without decryption keys.
No official MerryChristmas decryptor has been released as of the old guide's publication. Recovery options include:
- using files from backups made before infection
- applying System Restore to revert to previous states
- using Windows Previous Versions for individual file recovery
- employing ShadowExplorer if shadow copies remain untouched
Professional data recovery companies charge substantial fees with uncertain outcomes. Authorities recommend against ransom payment—criminals frequently don't provide working keys.
Preventing infection through regular backups remains most effective protection. If infected, focus on removing malware and recovering from backups rather than attempting decryption without official tools.
How do I remove Christmas virus from my system?
Removal depends on infection type. Download reputable antimalware software on a clean device if your system is heavily compromised. Run full system scans in Safe Mode with Networking to limit malware's capabilities.
Professional security tools automatically detect and remove Christmas viruses and associated threats. Some infections require manual intervention and professional IT support.
After removal, restart normally and run additional scans to verify complete infection elimination. Check System Restore for pre-infection points to revert system state.
Restore files from backups. Update all software immediately for security patch installation. Change passwords for critical accounts.
Monitor accounts for unauthorized activity. Monitor system performance—removal should restore stability and speed. For ransomware or persistent threats, professional help ensures complete removal.
Will Fortect remove Christmas virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Christmas virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Webroot: What is Social Engineering? (read October 5, 2026)
- Wikipedia: Rexx (read October 5, 2026)
- WhatIs: Peer-to-peer botnet (P2P botnet) (read October 5, 2026)
- Independent: Secret Sister Exchange: (read October 5, 2026)
- 2-spyware: A new Bitcoin scam: bomb threats wreak panic in the US (read October 5, 2026)
- SonicWall: Christmas themed Android malware/adware for 2019 (read October 11, 2026)