
Study General ads: what it is and how to remove it
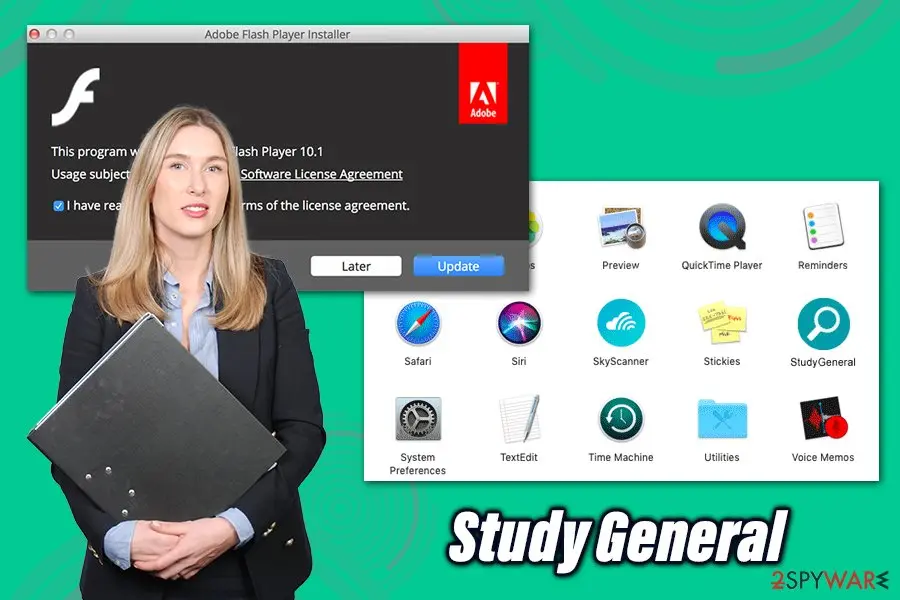
Study General, otherwise known as StudyGeneral, is a potentially unwanted application designed for macOS or Mac OS X platforms. Mostly distributed via fake Flash Player installers or freeware bundles, the Study General virus belongs to a well-known Adload campaign - an interconnected network of malicious apps designed to utilize AppleScript for malicious purposes.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
A scan of the PC is a quick way to confirm that nothing installed is behind the novirus.uk redirects.
Do it yourself · free Remove Study General ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps
Study General ads: summary
| Damage | Other malware/PUP installation, sensitive information disclosure to unknown parties/cybercriminals, financial losses, identity theft/fraud |
|---|---|
| Name | Study General |
| Also known as | StudyGeneral virus |
| Type | Mac virus, adware |
| Related | Safe Finder, akamaihd.net, home.searchpulse.net, etc. |
| Infiltration | The app belongs to the infamous AdLoad virus family, members of which are typically delivered via fake Adobe Flash Player update prompts and software bundle packages downloaded from third-party websites |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Symptoms | Unknown browser extensions and applications installed on the machine seemingly out of nowhere and difficulty with their termination, extensive ads on all visited websites, changes to a new tab/homepage URLs, a slowdown of computer operation, etc. |
|---|---|
| Detection names | No Microsoft detection name is known |
| Distribution | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| Domains | novirus.uk |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 20 April 2020 |
| Facts checked | 6 October 2026 |
What the Study General ads ads look like
Can read sensitive information from webpages, including passwords, phone numbers, and credit cards on all webpages
Is Study General ads dangerous?
From our report of Apr 2020 · not reviewed since
Don't give in to the fake update notifications encountered on the web
While Macs are considered to be a much safe operating system due to built-in tools like the GateKeeper and XProtect, it is not immune to infections.
In most cases, however, users unknowingly allow the infection to occur, whether it happens due to negligence or lack of awareness. As a result, there are thousands of users who get infected with Mac malware daily, although they are several methods to diminish that probability.
As mentioned previously, there are two main methods that Mac malware and adware is distributed - fake updates and software bundles. Both use deception, so security experts from novirus.uk have the following tips to share:
- 99% of the Adobe Flash update prompts are fake, as the technology has been replaced by HTML 5 several years ago and is no longer used by most websites;
- If you are still inclined on using Flash, go to the official Adobe website and download the plugin and its updates from there;
- If downloading applications, opt for official sources, such as App Store, Amazon, etc.;
- If you choose third-parties as a source for your apps, never rush the installation process and read the instructions carefully;
- When prompted, choose Advanced/Custom settings instead of Recommended/Quick ones;
- Watch out for pre-ticked boxes, fine print text, misleading deals and other tricks used by third-party sites and freeware authors;
- Employ anti-malware software with a PUP detection feature.
From our report of Apr 2020 · not reviewed since
More from our earlier report on Study General
- You can eliminate malware by scanning the machine with security software such as
- For best results and system recovery to its original state, scan the machine with
- StudyGeneral 1.0 Permissions for "StudyGeneral": Webpage contents Can read sensitive information from webpages, including passwords, phone numbers, and credit cards on all webpages Browsing history Can see when you visit all webpages
From our report of Apr 2020 · not reviewed since
Study General virus - an unsafe Mac application that can steal personal information and display intrusive ads without permission
Study General, otherwise known as StudyGeneral, is a potentially unwanted application designed for macOS or Mac OS X platforms.
Mostly distributed via fake Flash Player installers or freeware bundles, the Study General virus belongs to a well-known Adload campaign - an interconnected network of malicious apps designed to utilize AppleScript for malicious purposes. As a result, users might find several suspicious applications on their Macs, even though they did not approve the installation of them in the first place.
Once installed, the StudyGeneral virus will perform a variety of changes in the system in order to begin its operation. While the symptoms of the infection vary, users typically notice unknown web browser extensions installed on Safari, Google Chrome, Mozilla Firefox, or another web browser.
Another prominent change to browsers includes their homepage modification, which is typically set to the Safe Finder, Search Pulse, or others. Once used, these search tools will deliver sponsored ads on all visited sites, gather sensitive information via the browser, and prevent users from Study General removal altogether.
While previously considered non-existent, adware, and malware on Mac platforms is becoming an increasing threat to users. In fact, according to researchers' findings, Malware malware was being delivered at a more rapid pace than Windows malware at the start of 2020. Without a doubt, StudyGeneral is one of the threats that should not be ignored, as its distribution and operation techniques are closer to those of malware.
As previously mentioned, Study General adware is typically spread if two different ways:
While the latter can be considered somewhat legitimate, fake Flash Player updates have been long used to deliver all types of malware and is propagation method that users should be well aware of when browsing the internet, as Study General virus is just one of many threats that are distributed in such a way (the notorious Shlayer Trojan and Crescent Core come to mind).
Once inside the system, StudyGeneral will place a browser extension on the used browsers, which will be impossible to eliminate regularly. With this and other browser changes, users will be forced to browse the web via a fake search engine such as Safe Finder, which will deliver sponsored search results.
Study General infected users will also frequently encounter redirects to suspicious or malicious sites, as well as ads in various forms: pop-ups, auto-play, in-text links, deals, banners, offers, and other commercial content will be present on all visited websites (even those that do not typically serve ads).
With redirects, users can be exposed to more fake updates and other online scams, which would increase the chance of being infected with more malware besides Study General.
Besides displaying intrusive ads, redirecting to suspicious sites, and exposing users to a variety of online dangers, users might also see additional apps installed on their system without permission. With the help of AppleScript, StudyGeneral virus might also install its sister applications (SearchWebSvc, DataQuest, MainReady, and many others), as well as other malware in the background.
Another reason to remove Study General virus as soon as possible is its information tracking practices. Upon installation, the web browser extension grants itself elevated permission that no third-party software (with a few exceptions) should be able to get:
As evident, such permissions should never be granted to an app that is considered borderline malware (most of the security tools would detect it as potentially unwanted program). If abused, this harvested information can be used for malicious purposes or sold on the underground hacking forums for profit. As a result, Study General virus-infected users might suffer from monetary losses or even identity theft.
The most terrifying is the fact that, because the StudyGeneral infiltration is stealthy, users will not be aware that such permissions are granted in the first place unless they check the installed software list. Thus, it is always important to monitor your Mac system or at least scan it with anti-malware regularly.
To eliminate StudyGeneral and all its components, you will have to locate them in particular parts of the system or perform a full system scan with anti-malware software such as . For best results, we also recommend using to ensure that the computer is running just as well as it previously did.
- Fake Flash Player updates encountered of random sites;
- Software bundle packages downloaded from third-parties.
Check your browser and PC
- Address:
novirus.uk
How to remove Study General ads
How to remove Study General from a Mac
Remove the app and what starts it, then check the browsers.
Step 1: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from Study General or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 2: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 3: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 4: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Reset Google Chrome if you are unable to eliminate the extension in a regular way:
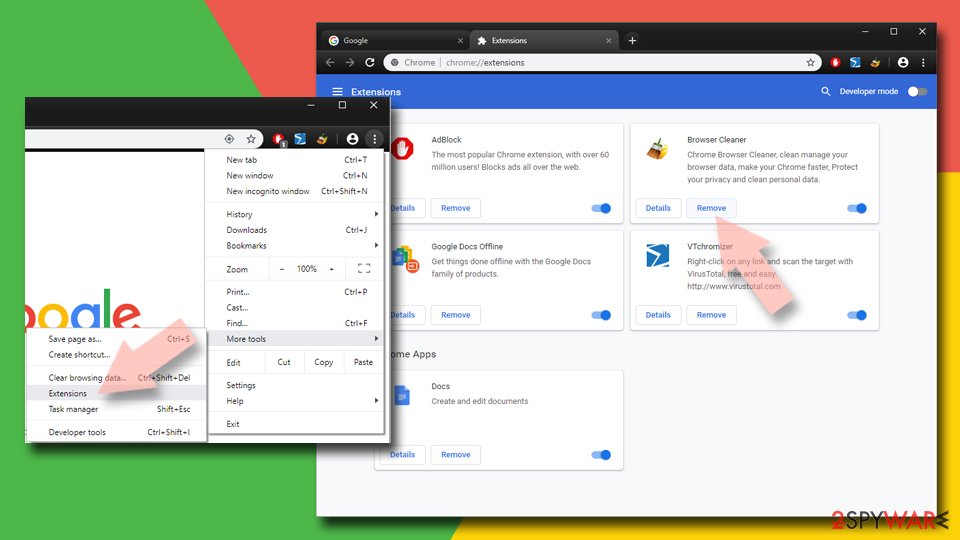
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.
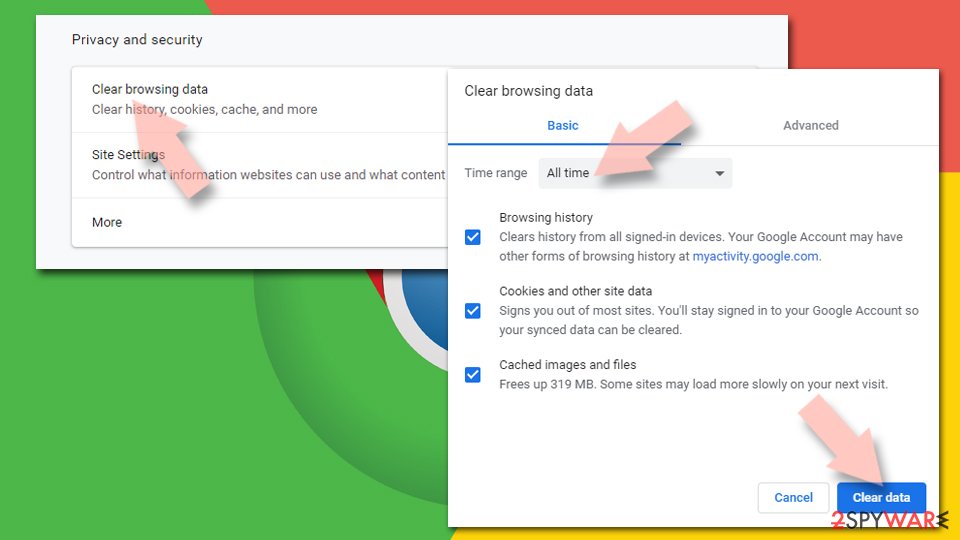
Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.
Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
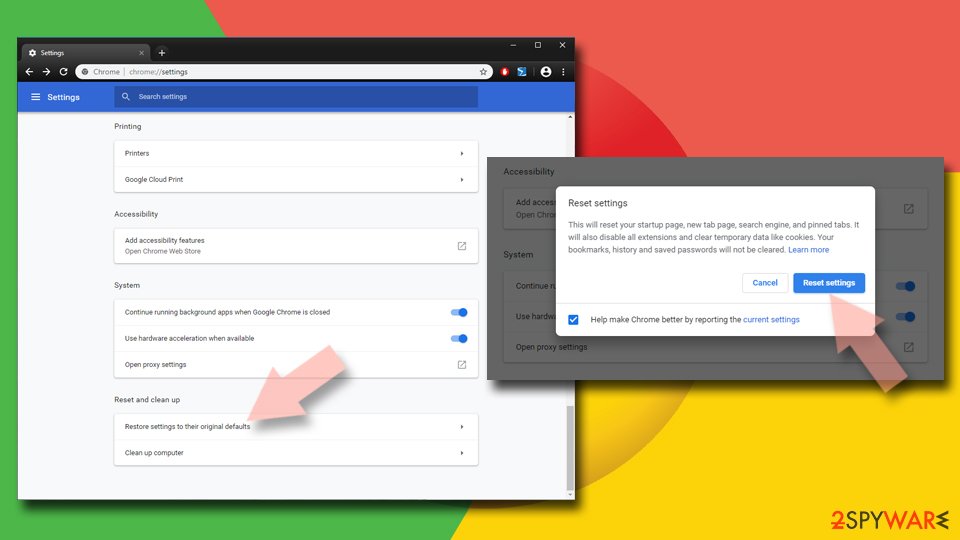
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.
Remove from Mozilla Firefox (FF)
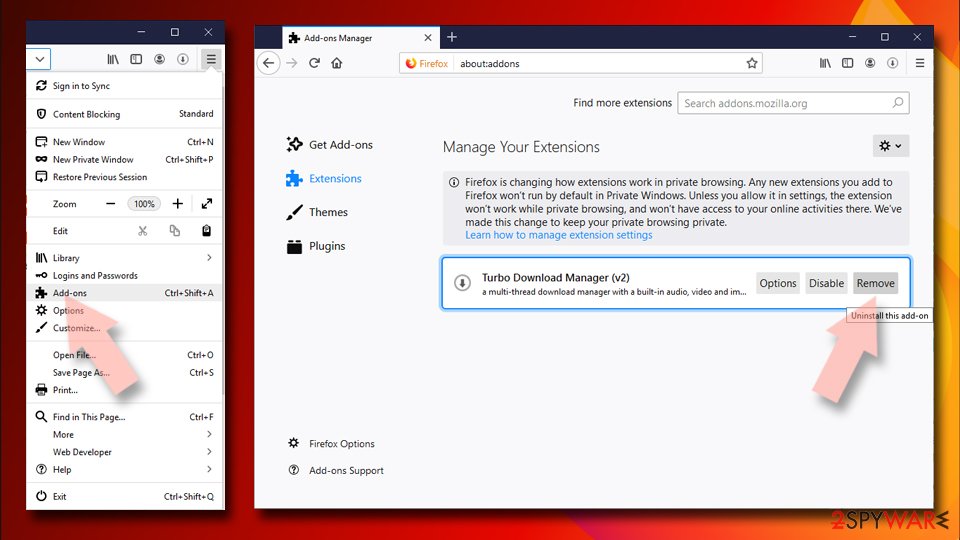
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.
Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
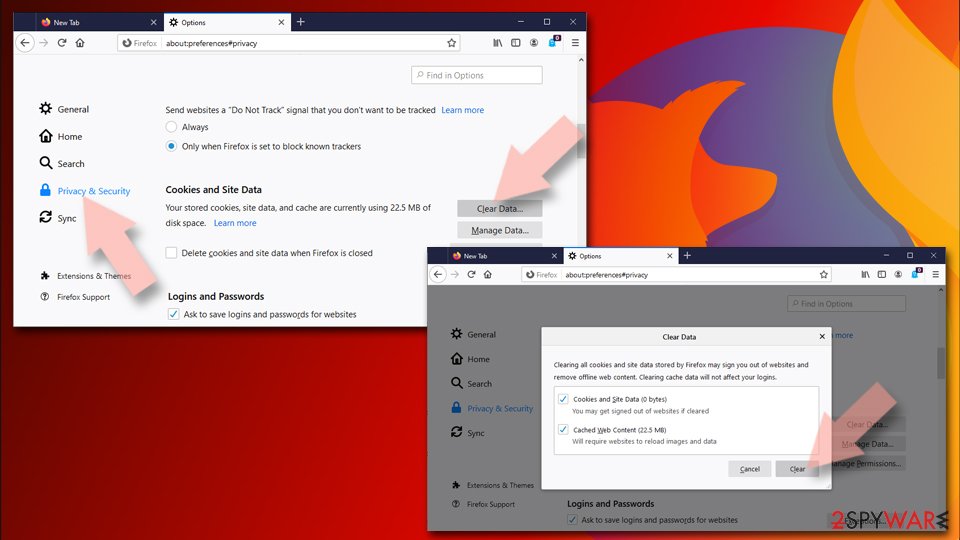
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.
Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
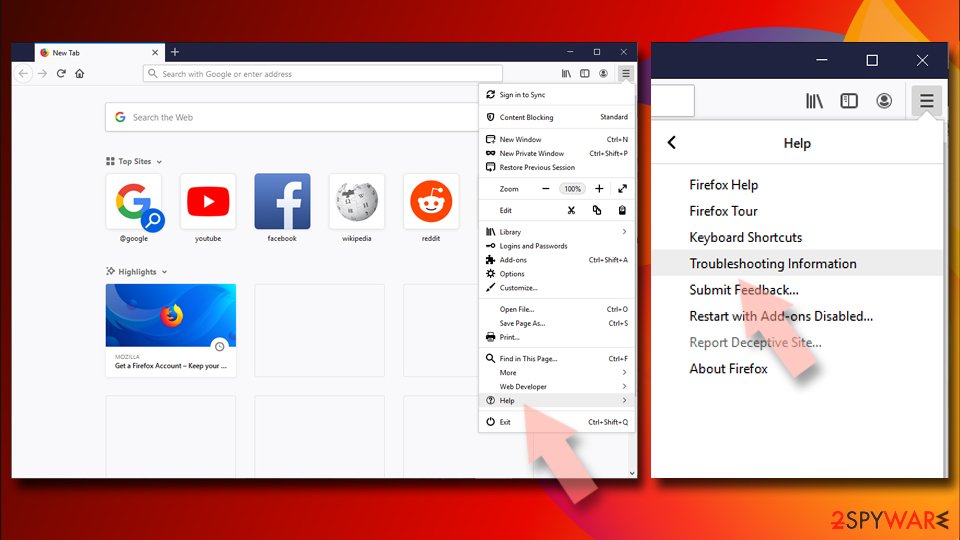
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.
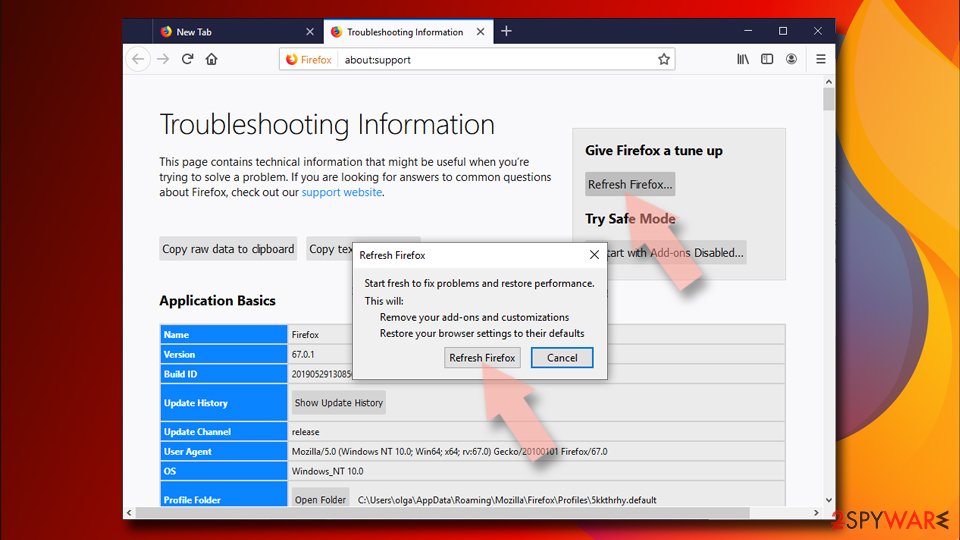
- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.
Delete from Safari
Remove dangerous extensions:
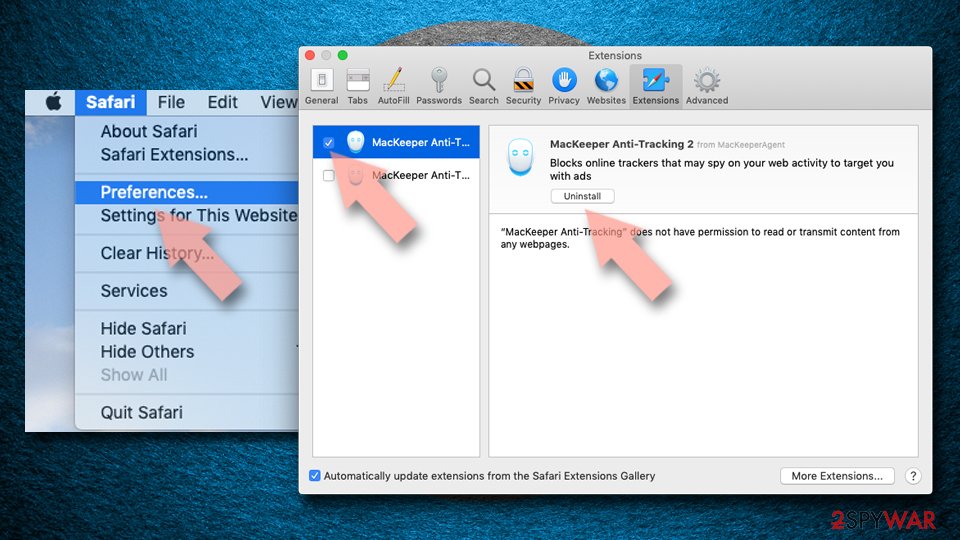
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
Clear history and website data:
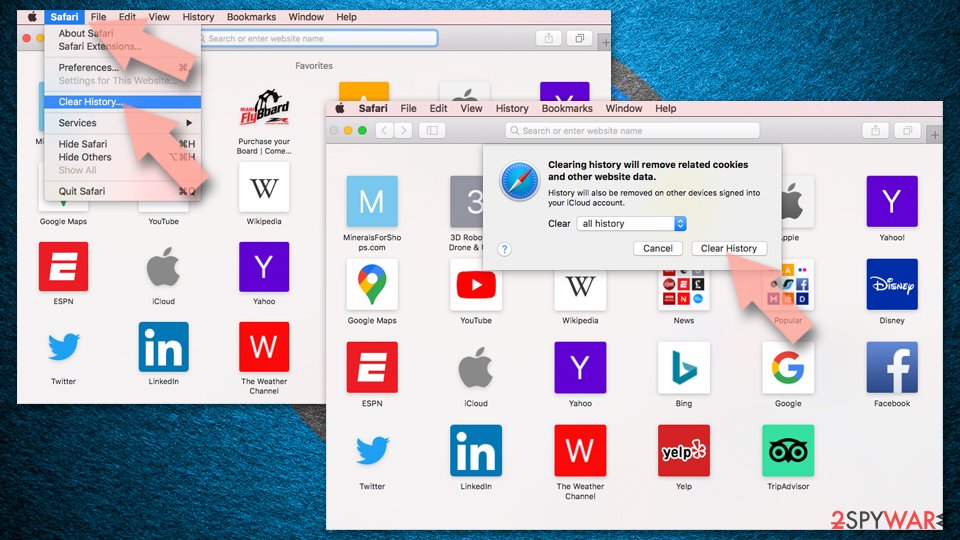
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
Reset Safari:
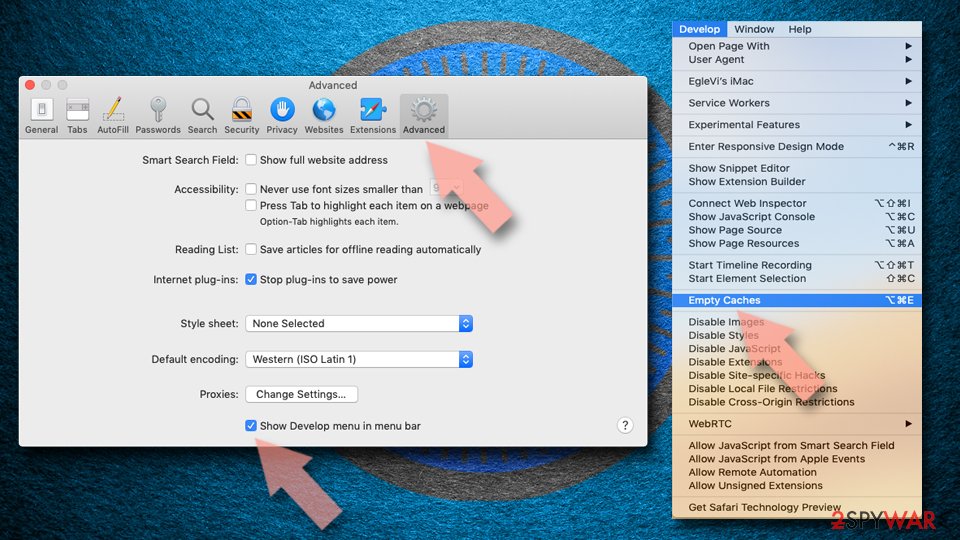
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
To get rid of StudyGeneral, you should locate the unwanted app and move it to Trash:
Remove the unwanted application:
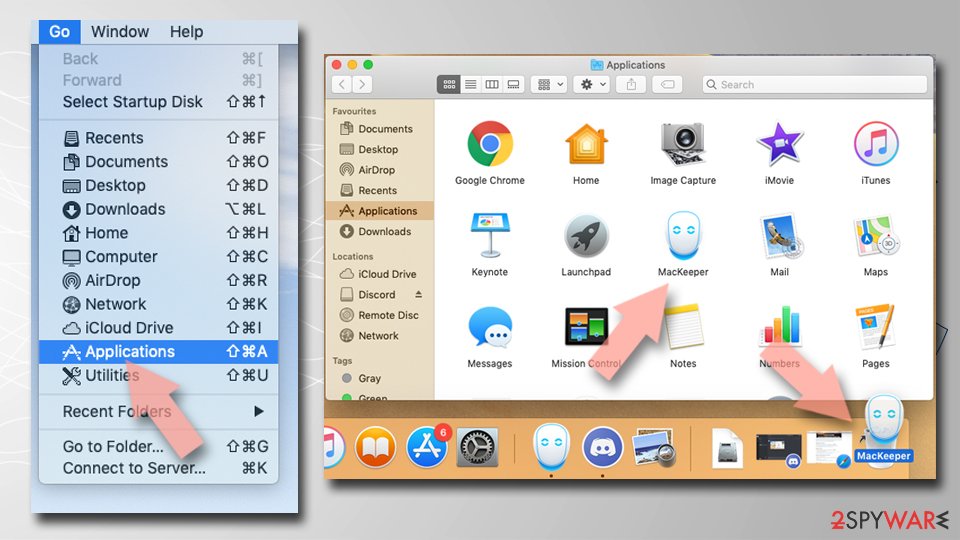
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
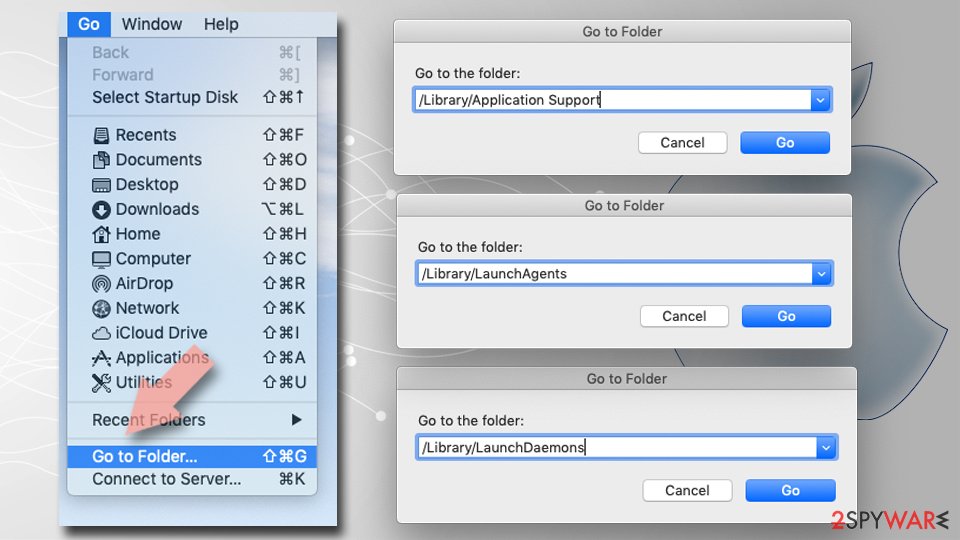
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of Apr 2020 · not reviewed since
Study General virus termination instructions
Study General virus removal might be sometimes complicated, as the infection might stop users from getting rid of the app in a regular way (users reported that the extension uninstall button and the pre-set homepage are both grayed out). To bypass this, users need to locate and remove Study General related files, which can be located in the following sections on macOS:
After that, you can eliminate the StudyGeneral extension from the web browsers and eliminate the associated app by moving it to trash. However, if you do not wish to tamper with files and you are a less experienced computer user, you can simply employ a reputable anti-malware tool and perform a full system scan with it.
Regardless of which StudyGeneral virus termination method you choose, it is advisable to reset all the installed browsers to get rid of the Safe Finder or other unwanted components that hide within the settings.
Questions about Study General ads
How do I stop novirus.uk from opening?
Find and remove whatever opens it. Start with the browser's extensions page and remove anything you do not remember adding. Next, open the notification settings and take away permission from sites you do not recognise.
Then check Settings > Apps > Installed apps for programs added around the day the redirects began, and uninstall those. Restart the browser and test a few links after each step.
If novirus.uk still appears, reset the browser, which restores the default search engine, start page and permissions without deleting bookmarks or saved passwords. Redirects that survive a reset in every browser point to a program in Windows, and a full scan is the next step.
Should I worry about redirects to novirus.uk?
Worry less about novirus.uk itself and more about what keeps sending you there. A single redirect from a free streaming or download site is normal and harmless once the tab is closed.
Repeated redirects on sites that used to work fine mean something in the browser or in Windows changed, often an extension or program installed alongside other software. It may also collect the pages you visit. Remove the cause with the steps in this guide, and do not act on anything the redirected pages ask:
- no Allow clicks
- no downloads
- no calls
If you already did one of those, the matching section of this guide explains what to do next.
What is Study General?
Study General is an adware extension, a kind of adware. It earns money by showing redirects through ad pages, and each view, click or redirect pays whoever runs it. It is not something people usually choose; it arrives through a free download, a fake button or a misleading prompt.
Study General does not encrypt files or take control of Windows, but its ads are sold to anyone, including scam operators, so they can lead to fake virus warnings and unwanted downloads. The steps in this guide remove it from Windows and from each browser.
Which browsers does Study General affect?
In the cases we checked, Study General showed up in Chrome, Edge and Firefox. That does not rule out others on your PC, since adware installers often target every browser they find, and permissions and extensions sync across computers signed in to the same browser account.
Open each browser you have, go to its extensions page and its notification settings, and remove anything you do not recognise. Profiles count separately: Chrome and Edge can each hold several, and each one needs checking on its own.
Are the pop-ups I see really from Study General?
Compare them with the details in the table above. Study General produces redirects through ad pages, and the clearest sign of it is redirects to novirus.uk. Other adware looks similar, so check the name of the sending site at the bottom of a notification, the address in the tab that opened, or the newest entries on the extensions page.
If those match, this guide fits. If you see a different name, the same kind of steps apply, but remove the item you actually find rather than guessing.
Can an adware pop-up infect my PC just by appearing?
No. A pop-up, a notification or a new tab is only a web page or a message. It cannot run programs on Windows by itself, provided the browser and Windows are up to date. Infection needs a step from you:
- running a downloaded file
- installing an extension
- giving a stranger remote access
That is why scam pages work so hard to make you click. Close such pages with the tab's X or by closing the browser, not with buttons inside the page, which may start a download.
My scan found nothing, but the ads continue. Why?
Because the source may not be a file a scanner looks for. Browser notifications are a permission stored in the browser, and many adware extensions are not flagged because they come from an official store.
Some ad-supported programs are only reported if you enable detection of potentially unwanted apps. So a clean scan does not mean the job is done. Check each browser's notification permissions and extension list by hand, and turn on Potentially unwanted app blocking in Windows Security before scanning again.
Why is my browser so slow since the ads started?
Each page now does extra work. An adware extension reads the page, decides where to put ads, loads them from ad servers and reports your visit, and that happens on every tab. Ad-supported programs add their own background activity.
Removing the extension or program usually makes the browser fast again at once. If it stays slow, open the browser's own task manager with Shift+Esc in Chrome or Edge and look for extensions using a lot of memory or processor time.
Did Study General collect my data?
Adware typically collects what it needs to choose ads:
- the sites you visit
- search terms
- approximate location
- browser and system details
Extensions with permission to read and change data on all websites can technically see everything on those pages, including forms. That is a privacy problem rather than proof of theft.
If you typed card details or passwords while it was active, changing the most important passwords is a reasonable precaution. Clearing cookies after removal ends the tracking sessions it may have started.
Will Fortect remove Study General?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For Study General, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- AppleInsider: Mac malware outpaced Windows PCs threats for first time in 2019, report says (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)
- Microsoft Learn: Microsoft Defender Offline (read October 6, 2026)
- Microsoft Learn: How Microsoft names malware (read October 6, 2026)