
Google virus: what it is and how to remove it
Google virus is a term for various cyber infections using Google's name for legitimacy, ranging from adware to ransomware. The 2019 guide identified multiple propagation methods including email attachments, bundled software, and fake updates.
Facts checked October 5, 2026. Removal steps tested on Windows 11 (26H2) and checked against Microsoft's and the browser makers' current documentation. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your PC is infected.
Fortect finds malware, unwanted programs and the Windows damage they leave behind, and repairs it in one pass.
If the "We are not affiliated with or related to Google Lead Services™ in any way." warning keeps returning, an automatic scan can check browsers, extensions and installed programs in one pass.
Do it yourself · free Remove Google virus yourself 3 steps, about 9 minutes, no software needed.
Google virus: summary
| Name | Google virus |
|---|---|
| Type | Trojan horse/backdoor/malware/potentially unwanted program/survey scam/tech support scam |
| Infection means | Software bundling, third-party sites, spam emails, fake updates, misleading pop-ups, etc. |
| Symptoms | Symptoms of Google virus may vary: PUP infections usually concentrate on advertising by redirecting to suspicious sites and displaying ads on all visited sites; Ransomware viruses lock personal files and prevent their access; Backdoors and trojans usually show no symptoms, although users might experience computer slowdowns, software/system crashes, unknown processes running in the background, etc. |
| Main dangers | Malware infections, installation of potentially unwanted programs, sensitive information disclosure to cybercriminals |
| Examples | Chrome redirect virus The HoeflerText font wasn't found Chrome Update Center Google Chrome Critical Error Google Chrome Support Centre |
| Removal | Scan the PC with security software to find and remove the malware and anything installed with it. Fortect scans Windows for malware and repairs the system files and settings it damaged. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 8 more facts
| Termination | You can delete some of the infections manually, although most serious threats should be terminated with anti-malware software |
|---|---|
| Detection names | No Microsoft detection name is known |
| Distribution | Not recorded in the old report |
| Damage | Not recorded in the old report |
| Evidence | 10 write-ups by security sites; details still limited |
| Domains | googleleadservice[.]com |
| First seen | 17 June 2019 |
| Facts checked | 5 October 2026 |
What the Google virus pop-up looks like
We are not affiliated with or related to Google Lead Services™ in any way. The term "Google" is used as a synonym for "Search"
Is the Google virus warning real?
What readers reported about Google virus
How to get rid of Funmoods???. Hello guys! I have been using my PC for ages and one day this thing managed to take it over. I can't use Google or Bing anymore! How can I uninstall Funmoods from my computer, help!
How to get rid of incredibar?. I ve got a problem, everytime i start firefox it redirects me to other search engine 'MyStart' by IncrediBar. mystart.incredibar.com I'm trying to fing the answers in google, on incredibar virus removal, but it seems there is no information.. how do I get rid of it?
How to get rid of incredibar?. My home PC is infected with search.incredibar.com, which automatically redirects my internet browser to the search.incredibar.com browser. This one looks like Google. How can I get rid of this annoying page?Hope that you can assist. Thanks!
From the comments under our earlier guide; names and contact details removed.
- Address:
googleleadservice[.]com
From our report of Jun 2019 · not reviewed since
More from our earlier report on Google virus
- To fix virus damage, we highly recommend scanning the device with
What the Google virus scammers want
From our report of Jun 2019 · not reviewed since
Google virus - a term used to describe a variety of cyber infections and scams related to the name of the tech giant
Google virus is a set of computer infections and scams that use Google's name in order to steal personal user data, trick into installing malicious software, or spend money on useless programs.
Of course, the malicious actors have nothing to do with Google, which probably the best-known company in the world, employing almost 100k employees. Nevertheless, the massive corporation sometimes slips too by failing to block phishing links or letting in malicious apps into Chrome store or Google Play.
Google virus is not tight to one browser or a type of the operating system and can affect Windows, Mac, iOS, and Android users. The broad term also includes a variety of computer infections and, while some, like browser hijackers and adware, are less harmful, threats like trojans, backdoors, ransomware or rootkits can result in serious consequences, such money loss, personal file destruction, or even identity theft.
Besides, many crooks rely on Google's name to make their Google virus scams believable, claiming that the system is infected with viruses, or that users' personal information is at risk. Additionally, survey scams might promise expensive gifts, but in reality, seek users' payment details or make them subscribe for useless services.
All in all, Google virus should be underestimated, and, if you are affected, you should take adequate measures to protect your computer from damage, as well as yourself from hackers who might abuse your sensitive information for evil deeds.
From our report of Jun 2019 · not reviewed since
Propagation techniques used by Google virus
Malware can be transmitted in a variety of methods, as hackers behind it are usually sophisticated and look to multiple ways that are less noticeable.
Additionally, malware can use a variety of evasion techniques, making Google virus removal complicated in some cases. Nevertheless, there is always the way to remediate infected machine and get rid of the threat for good.
Malware authors that spread Google virus might use the following propagation techniques:
Nevertheless, most of Google virus variants are mostly cases of adware infections, which are far less threatening.
Some Google viruses might alter the way Windows OS operates, changing its registry or altering the boot sequence.
It is not safe to use your machine until you remove Google virus, as some infections, such as trojans, might be able to steal your personal information that you enter into certain fields (for example, credit card details) or record all your keystrokes.
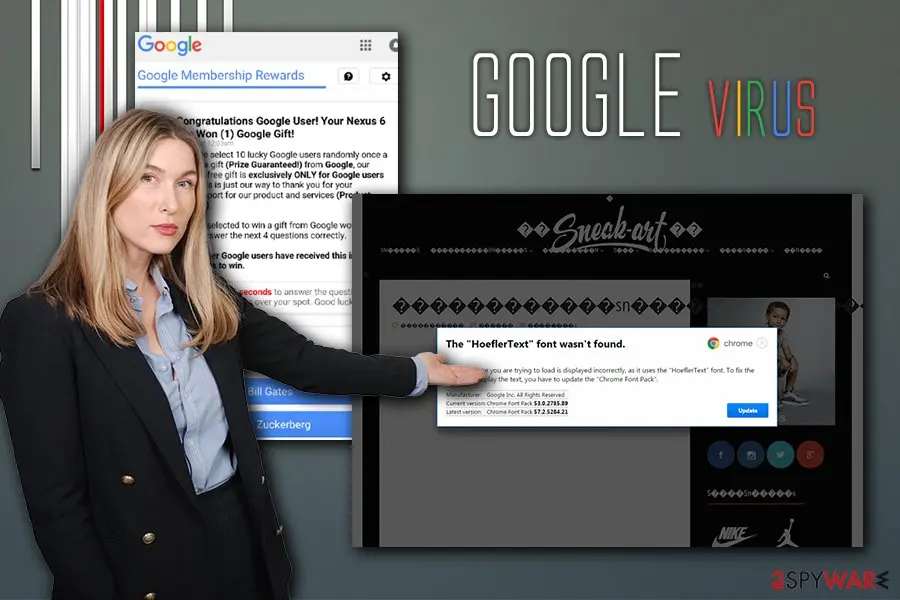
Alternatively, adware might lead you to phishing and scam sites that either will prompt you to install bogus software and then pay for its licensed version or deceptively subscribe you for some kind of service you do not want or need. On the other hand, threats like The HoeflerText font wasn't found are using a simple trick to install such threats like Locky ransomware, Spora ransomware, or Zeus banking trojan.
- Malicious spam email attachments or hyperlinks
- Software bundles
- Unprotected Remote Desktop connections
- Exploits
- Fake updates
- Pirated or cracked software, etc.
From our report of Jun 2019 · not reviewed since
Google virus variants
There are many types of infections that might refer to the Google virus term.
In this section, we will describe some of the versions you might encounter in the wild.
From our report of Jun 2019 · not reviewed since
Google redirect
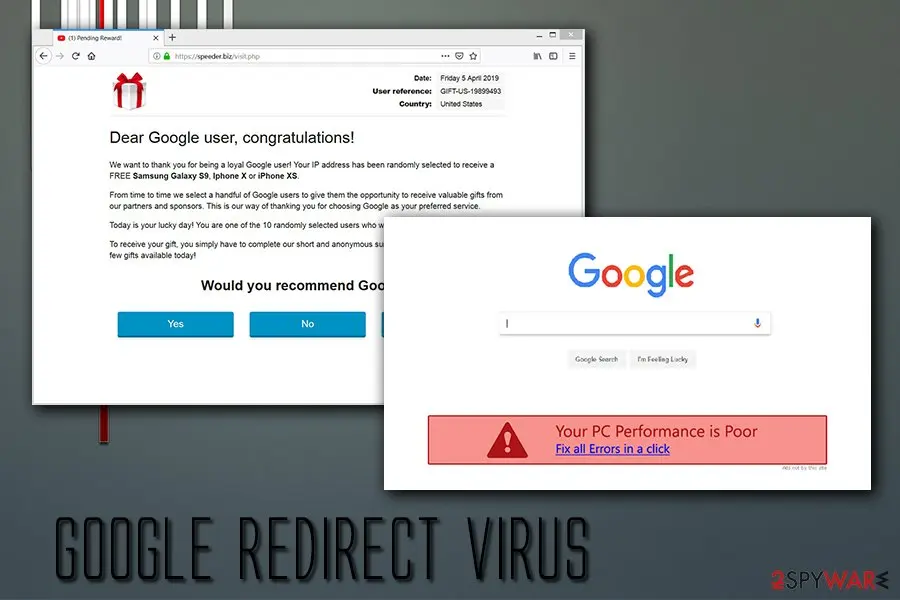
Google redirect virus is probably one of the most common Google virus variants, and it usually indicates adware, or other potentially unwanted program infection.
PUPs often travel within software bundles or are downloaded from third-party sites intentionally, without knowing that the program is potentially dangerous.
As soon as Google redirect virus settles, it takes over the browser and starts displaying alternative search results, which usually come in the form of sponsored links that are located and the top. In such cases, users are often misled by this behavior and click on sponsored links - not genuine Google results, but the links that adware or other PUP is promoting.
This might not only prevent users from finding relevant information but also increase traffic to unknown websites, as well as artificially inflate their rankings. Additionally, not all of the links are secure, and users might end up on malware-compromised sites resulting in Google virus infiltration.
Google redirect virus can also be extremely annoying to deal with, as it can add a layer of pop-ups, deals, banners, offers, and other ads into all sites that users visit. Clicking on such advertisements is not recommended as ad space can be bought by cybercriminals that insert malicious code into the website.
From our report of Jun 2019 · not reviewed since
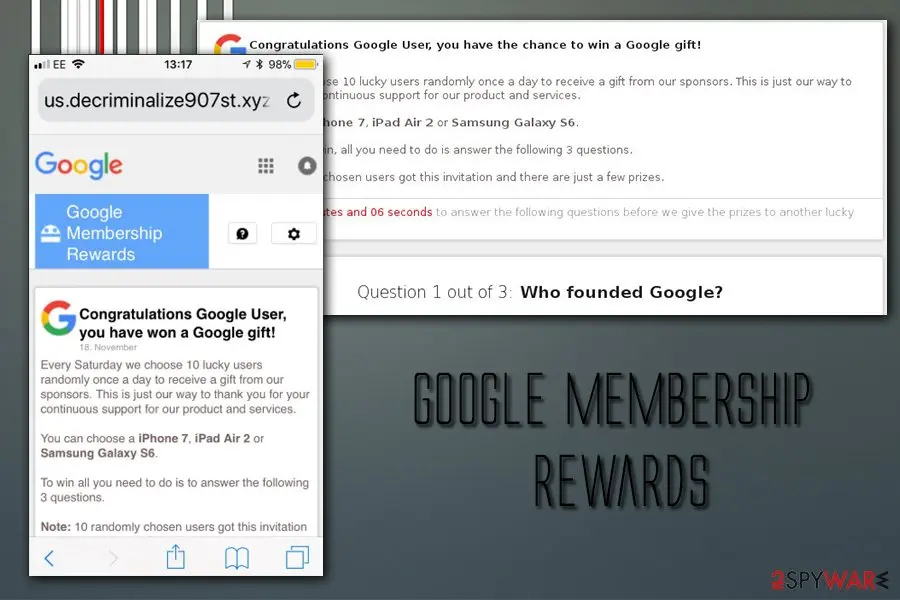
Google Membership Reward
Google Membership Reward belongs to survey scam category.
While it has many similarities with technical support scams, it uses different techniques to make users either disclose their personal information, such as credit card data or make them subscribe to a service they did not intend to. Nevertheless, both categories use deception and social engineering to work.
Most usually, users land on the Google Membership Reward accidentally when they visit a suspicious website or are redirected due to adware or PUP infection.
There, users are informed that they are selected few among other Google users (which is a lie - the message is shown to every visitor), and are eligible to valuable prizes for free - all they have to do is allegedly answer very primitive questions in a survey. The offered gifts vary, but some examples include:
What is more, users are also informed that they only have a mere few minutes to take the survey, as the prize will allegedly be given to somebody else. This tactic is often used by tech support scams too, providing a fake timer that creates an "immediate action" situation where users simply do not have time to think whether or not the claims are true.
However, there is no gift, and all the promises are fake. Do not trust Google Membership Reward if you encounter it, as nobody is trying to give you $1,000 or similar expensive gift for free.
- $1000 Walmart Giftcard,
- iPhone X 256 G
- Samsung Galaxy S8
- PlayStation 4
From our report of Jun 2019 · not reviewed since
Google Lead Services
Google Lead Services, which is also known as GoogleLeadService.com, is a fraudulent website that promotes its advertising services, such as Zip Code Lookup.
Nevertheless, this shady site has nothing to do with the original company, as it only uses the name of it in the hopes of providing a sense of legitimacy.
Thankfully, the developers of the servers are at least decent enough to describe what they actually are, as the fine print reads:
The service itself offers to display banners and another type of ads, that might range from regular size to full page ones. In most cases, these pop-ups, banners, deals, etc., are delivered with the help of adware application that is secretly infiltrated during freeware installation.
Thus, to remove Google Lead Services ads from their browsers, they need to locate and delete adware that is installed on their devices. As usual, we suggest scanning the device with security software or delete the application manually with the help of our instructions.
From our report of Jun 2019 · not reviewed since
Google Chrome 1111 virus
Google Chrome 1111 virus is possibly one of the strangest Google virus variants.
Once infected, the web browsers start displaying strange pop-ups with nothing by "111" or "1111" in them. While the dialogue can be closed, it can often return and spam the web browser.
Nevertheless, this is not the only activity that Google Chrome 1111 virus does. Allegedly, it can also spawn pop-ups that advertise a variety of services or display fake online job offerings, promising earnings of $20,000. However, please do not get lured by these advertisements, as they are all fake or might even be dangerous.
To stop the annoying behavior which constantly disturbs web browsing sessions, you will have to determine what type of malware is installed on your device and terminate it. The best way to do it is by using reputable security software.
From our report of Jun 2019 · not reviewed since
To stay away from malware, use extra caution
While the internet has become much safer in the past 20 years, it does not mean that it is entirely secure.
Nevertheless, some users are simply unaware of that or do not care about the consequences of a cyber infection, thinking that it will not affect them in any way.
While it is true that most potentially unwanted applications will not cause major harm as long as they are deleted on time, other viruses, such as trojans, ransomware or info stealers might result in permanent file/money loss or even identity theft. Besides, careless usage of the computer while infected with an adware might result in exact same consequences.
Staying away from potentially unwanted programs is relatively simple - you need to make sure you look at the installation instructions of shareware carefully and always opt for Advanced/Custom settings. This will allow you to terminate browser add-ons, system optimizers, uninstallers, driver updaters, and similar crapware.
On the other hand, to protect yourself from more sophisticated threats, you need also to do the following, as advised by experts:
- Install anti-malware software and keep it updated;
- Patch your operating system as soon as updates become available (do not postpone);
- Enable Firewall;
- Only use Remote Desktop services with VPN enabled and select a secure port for it;
- Make sure you use strong passwords for all your accounts and enable two-factor authentication where possible;
- Do now download pirated software or its cracks;
- Make sure all your software updates are set to automatic setting;
- Use ad-blocker;
- Be careful with spam emails, as malicious attachments or hyperlinks might result in malware infections.
How to get rid of the Google virus pop-up
The warning is a web page and your PC is not infected by it.
Close it, then remove what keeps bringing it back.
Which browser shows the ads?
Step 1: Remove googleleadservice[.]com from Chrome's notification list
Chrome keeps a list of every site you once allowed to send notifications, and
googleleadservice[.]comis on it. Pastechrome://settings/content/notificationsinto the address bar, find googleleadservice[.]com under Allowed to send notifications, open the three-dot menu next to it and pick Remove.Then click Add next to Not allowed to send notifications and type googleleadservice[.]com, so the site cannot ask a second time. Repeat it in every Chrome profile you use on Windows 11 or Windows 10, since each profile has its own list.
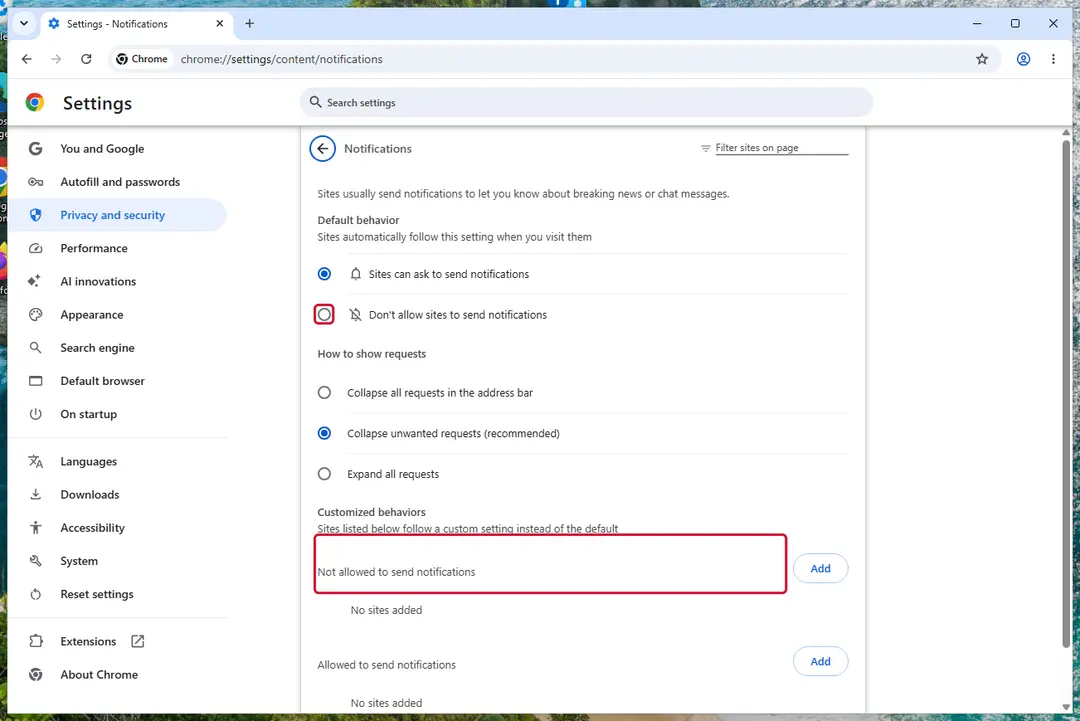
Chrome on Windows 11: Settings > Privacy and security > Site settings > Notifications. Full procedure with screenshots: Stop website notifications and pop-ups
Instructions for Google Chrome
Remove from Google Chrome
To make sure the virus does not return, Reset Google Chrome browser as explained below:
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Step 1: Remove googleleadservice[.]com from Edge's notification list
Open Settings and more (the three dots) > Settings > Privacy, search, and services > Site permissions > All permissions > Notifications. Remove
googleleadservice[.]comfrom the Allowed list, then click Add site next to Not allowed to send notifications and enter it there.Edge is built into both Windows 11 and Windows 10, so check it even if you normally use another browser. If the notifications came with the Edge logo, this is the browser that holds the permission.
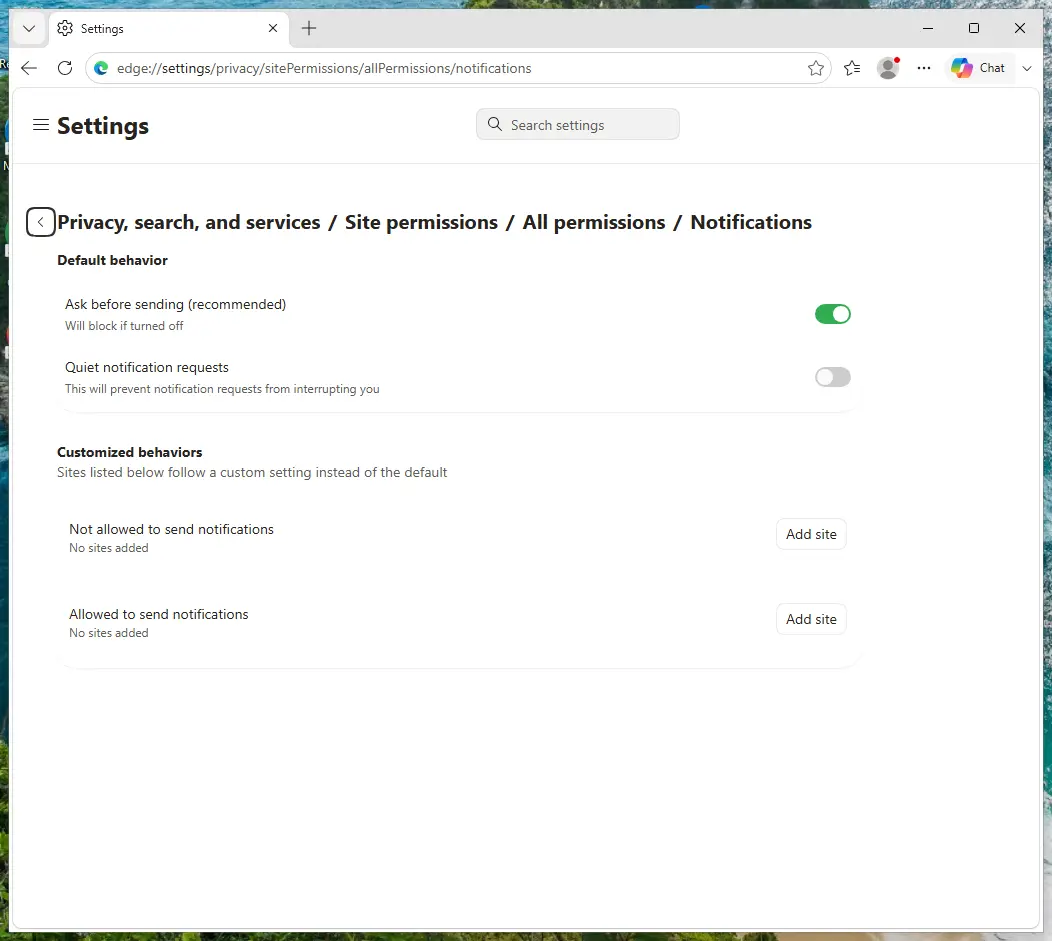
Edge on Windows 11: Site permissions > All permissions > Notifications. Full procedure with screenshots: Stop website notifications and pop-ups
Instructions for Microsoft Edge
Remove from Microsoft Edge
Delete unwanted extensions from MS Edge:
- Select Menu (three horizontal dots at the top-right of the browser window) and pick Extensions.
- From the list, pick the extension and click on the Gear icon.
- Click Remove.

Clear cookies and other browser data:
- Click on the Menu (three horizontal dots at the top-right of the browser window) and select Settings > Privacy, search, and services..
- Under Clear browsing data, pick Choose what to clear.
- Select Cookies and other site data and Cached images and files. (apart from passwords, although you might want to include Media licenses as well, if applicable) and click on Clear.

Restore new tab and homepage settings:
- Click the menu icon and choose Settings.
- Then find On startup section.
- Click Remove next to any suspicious startup page.
Reset MS Edge if the above steps did not work:
- Press on Ctrl + Shift + Esc to open Task Manager.
- Click on More details arrow at the bottom of the window.
- Select Details tab.
- Now scroll down and locate every entry with Microsoft Edge name in it. Right-click on each of them and select End Task to stop MS Edge from running.

Delete extensions from MS Edge (Chromium):
- Open Edge and click select Settings > Extensions.
- Delete unwanted extensions by clicking Remove.

Clear cache and site data:
- Click on Menu and go to Settings.
- Select Privacy, search and services.
- Under Clear browsing data, pick Choose what to clear.
- Under Time range, pick All time.
- Select Clear now.

Reset Chromium-based MS Edge:
- Click on Menu and select Settings.
- On the left side, pick Reset settings.
- Select Restore settings to their default values.
- Confirm with Reset.
- This will disable extensions and reset startup pages but will not delete bookmarks, saved passwords, or browsing history.

Step 1: Remove googleleadservice[.]com from Firefox's notification permissions
Open the menu (three lines) > Settings and click Permissions and data in the left list, then Notifications. Select
googleleadservice[.]com, click Remove Website and confirm with Save Changes.In versions older than Firefox 152 the same list sits under Privacy & Security, behind a Settings button next to Notifications. Firefox shows these notifications only while it is running, on Windows 11 and Windows 10 alike.
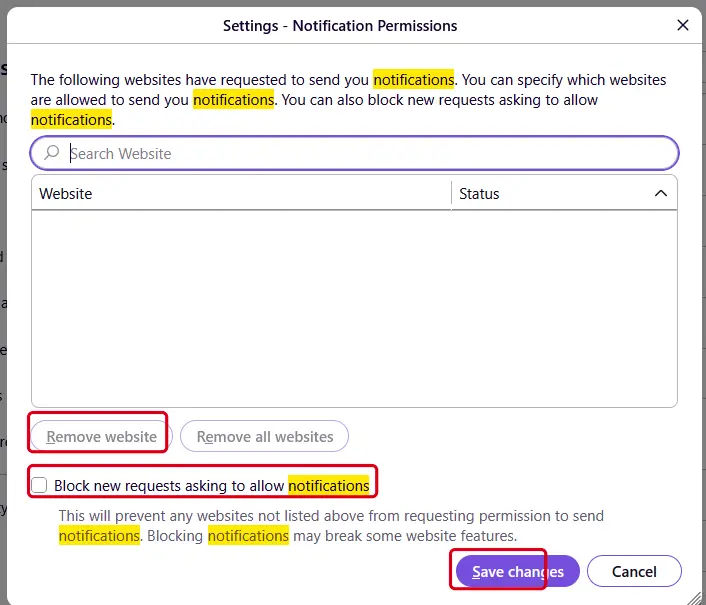
Firefox on Windows 11: the Notification Permissions window. Full procedure with screenshots: Stop website notifications and pop-ups
Instructions for Mozilla Firefox
Remove from Mozilla Firefox (FF)
Firefox is not immune to Google virus as the scam misusing its name can appear on this browser as well. Make sure you reset it if you were involved into this scam somehow.
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Our tested steps are for Windows 11 and 10. For Safari (Mac), use the instructions below.
Instructions for Safari (Mac)
Delete from Safari
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
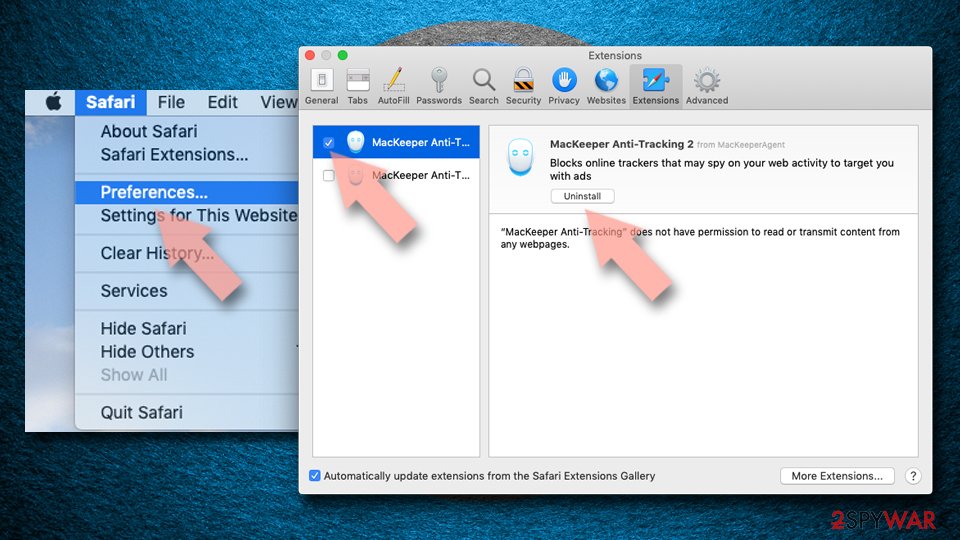
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
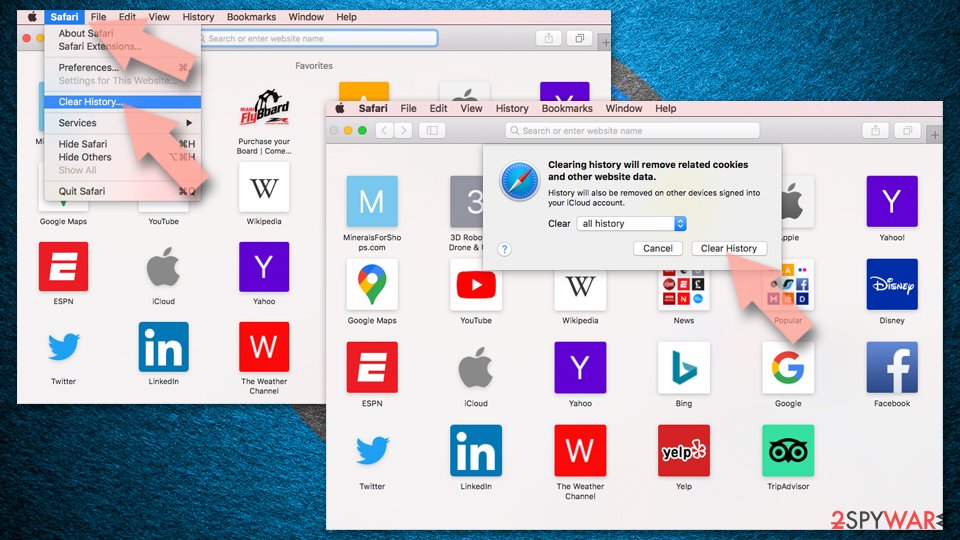
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
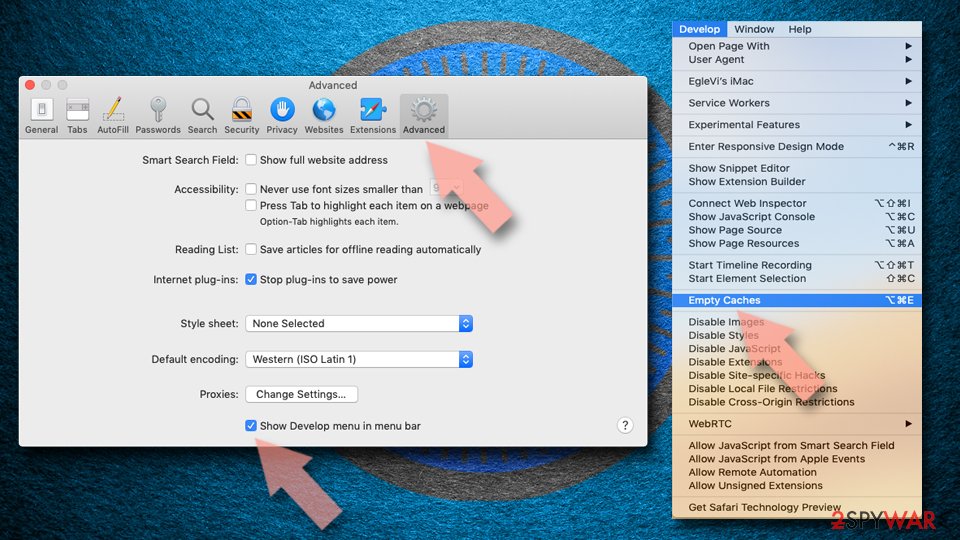
Delete from macOS
Macs are not immune to cyber infections - the myth has been debunked many times. Thus, if your browsers show strange behavior, delete the potentially unwanted app from your device as follows:
Remove the unwanted application:
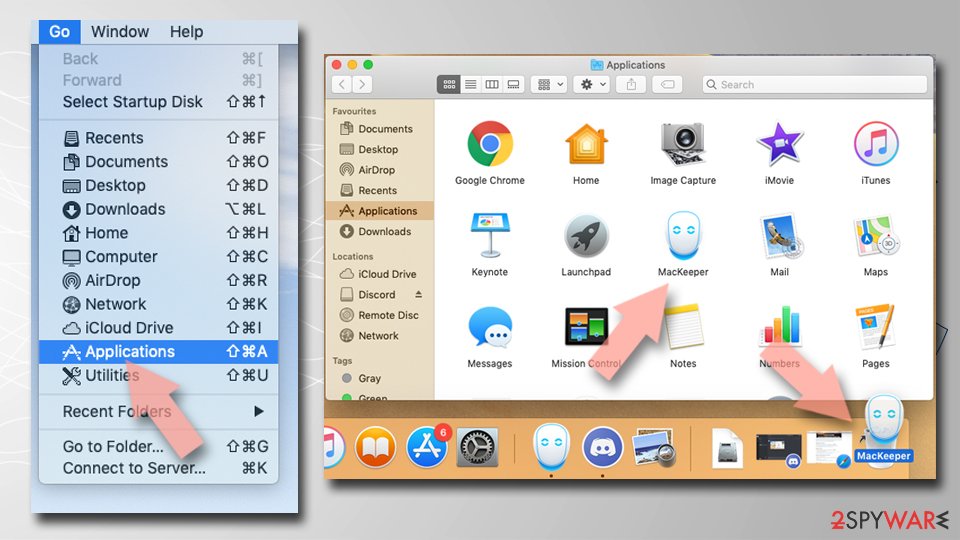
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
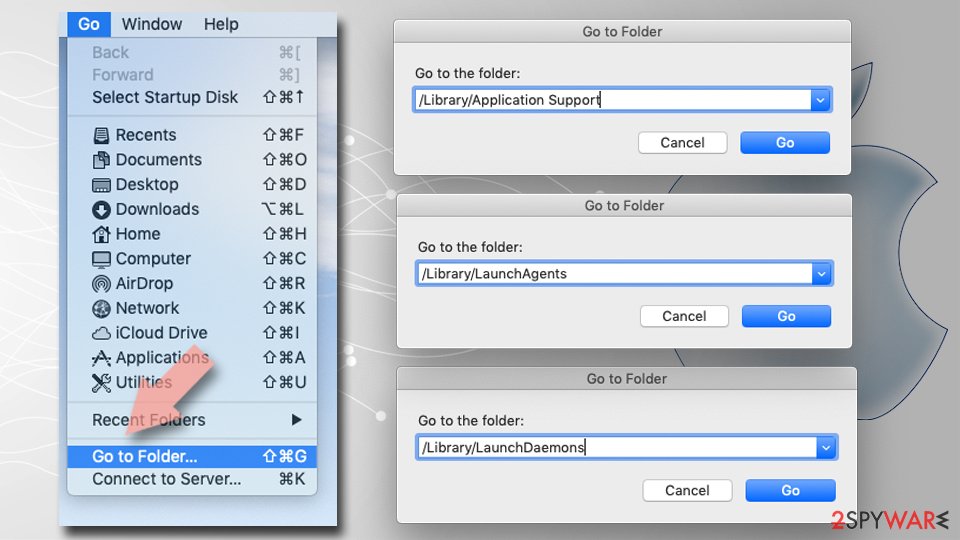
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
- Finally, empty the Trash to permanently remove the leftovers.
Then, whichever browser you use
Step 2: Close the page without touching its buttons
Press Ctrl + Shift + Esc to open Task Manager, select the browser on Processes and click End task: buttons on the page, including Close and Cancel, can trigger downloads or more pop-ups. When you reopen the browser, do not restore the previous tabs.
Warning: Never call a number shown in a browser warning; Microsoft and antivirus companies do not put phone numbers in warnings.
If the page opens again by itself, notifications or an extension are bringing it back. Task Manager works the same in Windows 11 and Windows 10.
Full procedure with screenshots: Close a frozen app (Task Manager, Force Quit) On uGetFix
Step 3: Scan the PC, then run the offline scan
A scan finds the parts of Google virus that the manual steps cannot see. In Windows Security > Virus & threat protection > Scan options, start a Full scan and quarantine what it reports.
Follow it with Microsoft Defender Antivirus (offline scan) > Scan now, which restarts the PC and checks the disk while Windows and the malware are not running.
It takes about 15 minutes and works the same in Windows 11 and Windows 10. If either scan finds something, run the full scan again after removal until it comes back clean.

Windows 11: Windows Security > Virus & threat protection > Scan options. Full procedure with screenshots: Run a Microsoft Defender Offline scan
More removal instructions
For programs installed on the PC and older browsers. Open the one you need.
Delete Google virus from your computer to ensure its safe operation
Depending on the type of infection, Google virus removal will vary.
In most cases, simple browser hijackers, adware and other PUPs can be uninstalled via the installed application list manually. Nevertheless, problems might arise even with unwanted programs, as it might not instantly be clear which program is the culprit of redirects and persistent ads.
However, if you downloaded some executable files or installed fake updates, you will have to use reputable security software to remove Google virus from your device altogether. Make sure you perform a full system scan with tools like , or similar.
Once you delete Google virus, you should also reset each of the installed browsers, as traces might still be present, and redirects might not stop right away.
Uninstall from Windows
To terminate Google virus from Windows manually, please follow these instructions:
Uninstall from Windows 10/8:
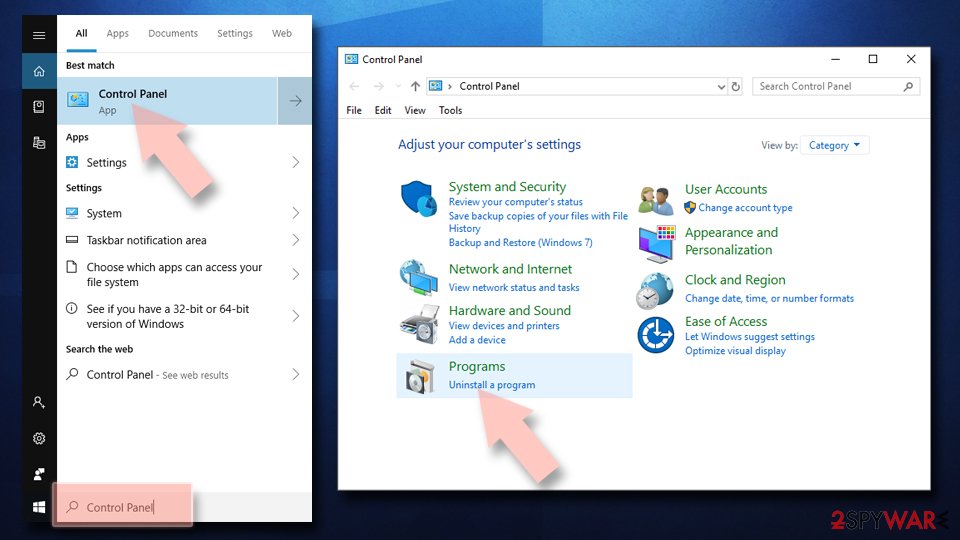
- Type Control Panel into the Windows search box and open the result.
- Under Programs, select Uninstall a program.
Uninstall from Windows 7/XP:
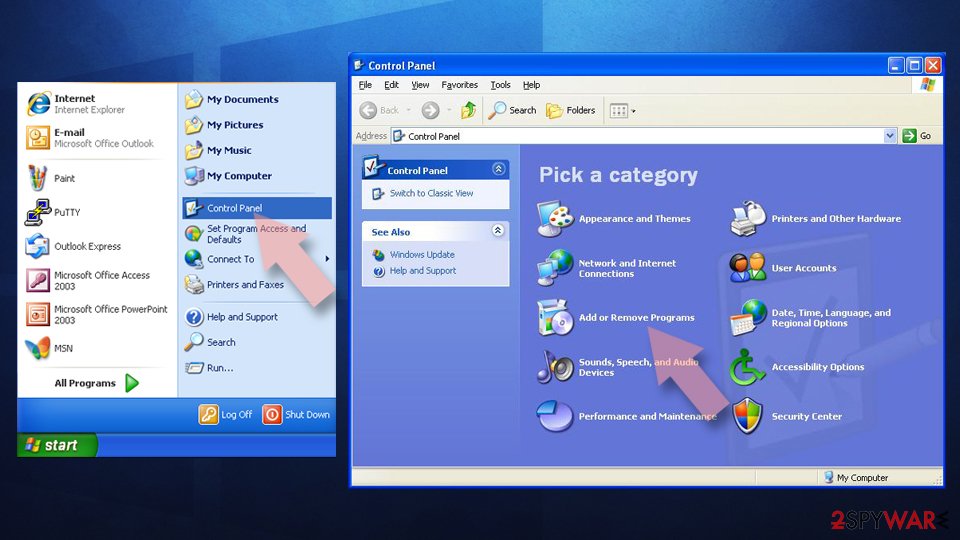
- Click on Windows Start > Control Panel (Windows XP users should click on Add/Remove Programs).
- In Control Panel, select Programs > Uninstall a program.
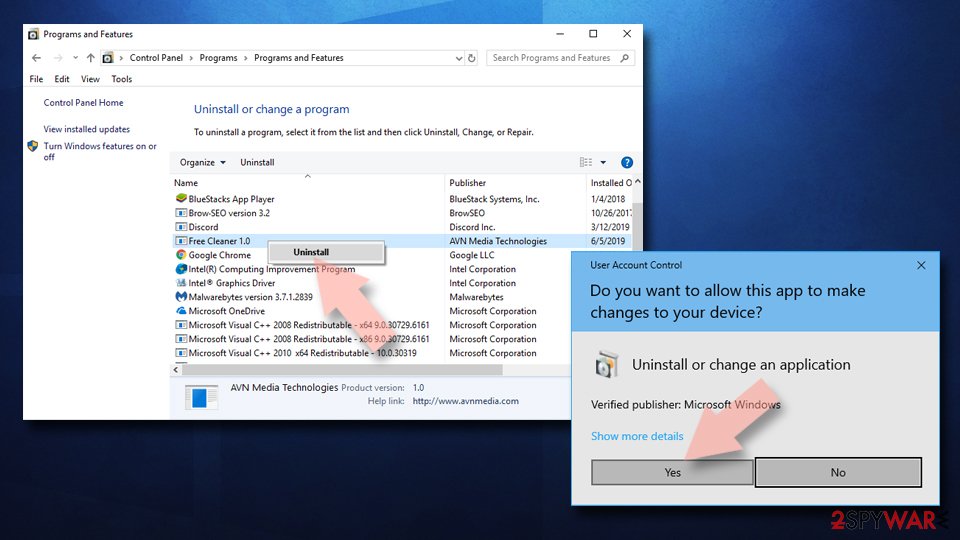
Remove the unwanted program:
- In the Programs and Features window, look for any recently installed suspicious entries, select them, and click Uninstall.
- If User Account Control appears, click Yes to confirm, then complete the removal.
Reset Internet Explorer
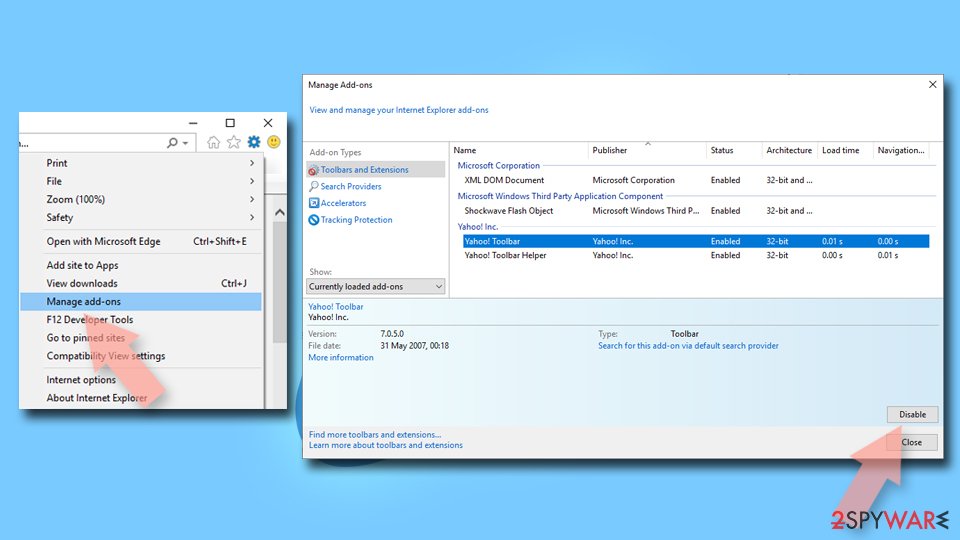
Remove dangerous add-ons:
- Open Internet Explorer, click on the Gear icon (IE menu) on the top-right corner of the browser
- Pick Manage Add-ons.
- You will see a Manage Add-ons window. Here, look for suspicious plugins. Click on these entries and select Disable.
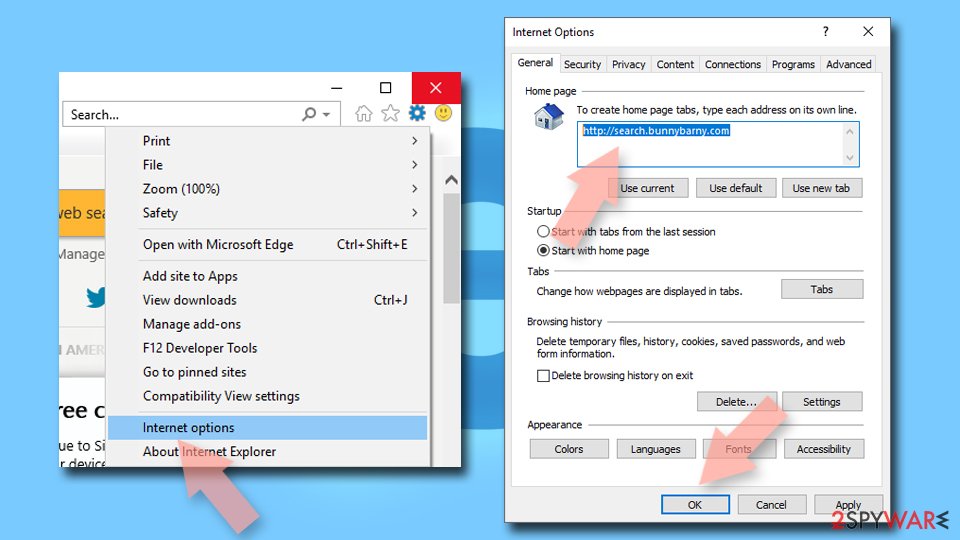
Change your homepage if it was altered:
- Open IE and click on the Gear icon.
- Select Internet Options.
- In the General tab, delete the Home page address and replace it by your preferred one (for example, Google.com).
- Click Apply and then select OK.
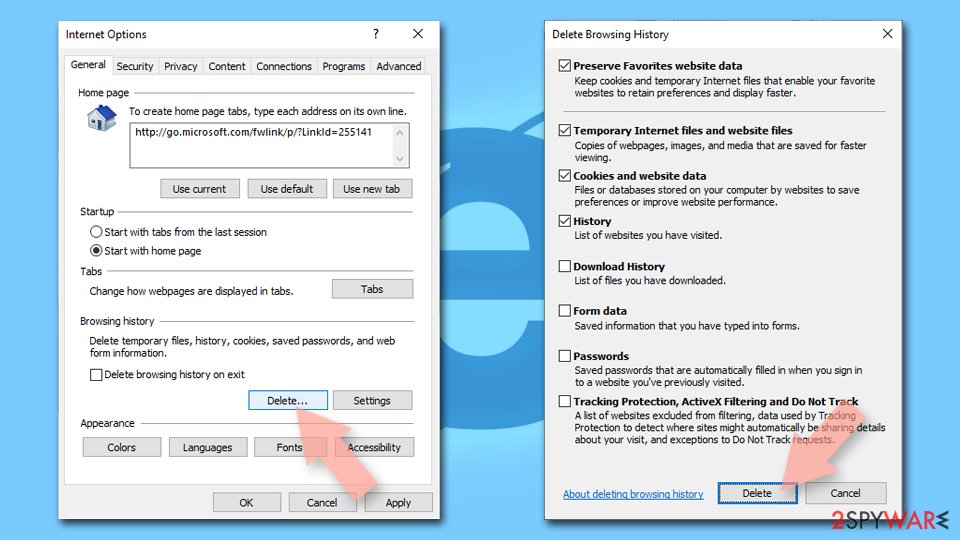
Delete temporary files:
- Press on the Gear icon and select Internet Options.
- Under Browsing history, click Delete...
- Select relevant fields and press Delete.
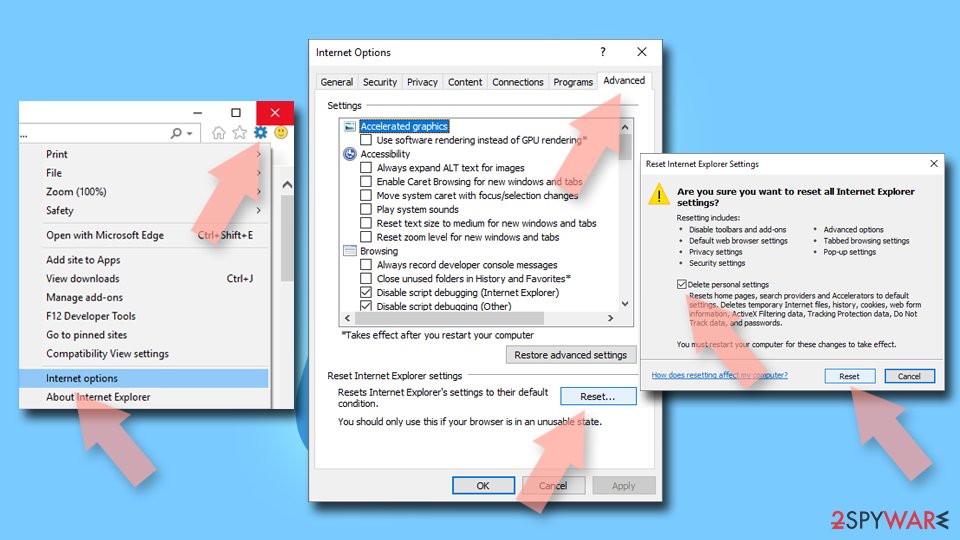
Reset Internet Explorer:
- Click on Gear icon > Internet options and select Advanced tab.
- Select Reset.
- In the new window, check Delete personal settings and select Reset.
Stream videos without limitations, no matter where you are
There are multiple parties that could find out almost anything about you by checking your online activity.
While this is highly unlikely, advertisers and tech companies are constantly tracking you online. The first step to privacy should be a secure browser that focuses on tracker reduction to a minimum.
Even if you employ a secure browser, you will not be able to access websites that are restricted due to local government laws or other reasons. In other words, you may not be able to stream Disney+ or US-based Netflix in some countries. To bypass these restrictions, you can employ a powerful VPN, which provides dedicated servers for torrenting and streaming, not slowing you down in the process.
Data backups are important - recover your lost files
Ransomware is one of the biggest threats to personal data.
Once it is executed on a machine, it launches a sophisticated encryption algorithm that locks all your files, although it does not destroy them. The most common misconception is that anti-malware software can return files to their previous states. This is not true, however, and data remains locked after the malicious payload is deleted.
While regular data backups are the only secure method to recover your files after a ransomware attack, tools such as can also be effective and restore at least some of your lost data.
Questions about Google virus
What is Google virus?
Google virus is a broad term describing various cyber infections and scams that use Google's name to appear legitimate. These include browser hijackers, adware, ransomware, trojans, backdoors, and tech support scams.
The 2019 guide noted that Google's name is exploited by malicious actors because the company is well-known and trusted worldwide. None of these infections actually originate from Google itself; scammers simply misuse the company's reputation to deceive victims.
Is Google virus safe or dangerous?
Danger depends on the specific infection type. Browser hijackers and adware are less harmful but still problematic, causing redirects and intrusive ads. However, trojans, backdoors, ransomware, and rootkits pose serious threats including money loss, file destruction, and identity theft.
Some infections show no visible symptoms while stealing data in the background. All variants should be treated as security threats requiring immediate removal.
What symptoms indicate Google virus infection?
Symptoms vary by infection type. Adware shows excessive ads and redirects to suspicious sites. Ransomware locks personal files and prevents access.
Trojans and backdoors may cause computer slowdowns, software crashes, and unknown background processes. Some infections produce no obvious symptoms while actively stealing data.
Users may experience degraded browser performance, unexpected pop-ups, or changes to browser settings. Noticing any of these warrants a full system scan.
How does Google virus get installed on my computer?
The 2019 guide identified multiple propagation methods:
- malicious spam email attachments
- pirated or cracked software
- fake software updates
- misleading pop-ups
- software bundling
Third-party websites and peer-to-peer networks are common distribution points. Users often install Google virus variants unknowingly when downloading freeware with bundled PUPs. Choosing Quick/Default installation settings increases the risk of accidental infection.
Can Google virus steal my passwords and credit card information?
Yes. Some Google virus variants like trojans and backdoors can record your keystrokes or steal data you enter into forms. The old guide confirmed that sensitive information including passwords and credit card details can be compromised.
Remote access trojans allow attackers to steal directly from your machine. This is why immediate removal is critical—leaving the infection active exposes you to ongoing data theft.
What is Google redirect virus?
Google redirect virus is one of the most common Google virus variants, typically indicating adware or potentially unwanted program infection. It forces your browser to display altered search results filled with sponsored links instead of genuine Google results.
Users are misled into clicking fake ads promoting adware or malicious sites. The infection travels within software bundles or is downloaded from third-party sites intentionally without understanding the danger.
Is Google Membership Reward legitimate?
No. Google Membership Reward is a survey scam using deception to steal personal information or trick people into subscribing to unwanted services. The old guide noted it falsely claims users are selected among Google users to receive valuable prizes for free.
In reality, no prizes exist and all promises are fake. Users typically land on this scam after visiting suspicious websites or being redirected by adware infections.
How do I remove Google virus?
Run a full system scan with anti-malware software to detect and remove infections. Some infections can be deleted manually, but serious threats like trojans and ransomware require professional security tools.
After removal, reset all browsers to default settings. For ransomware, isolation is critical to prevent further file encryption. The 2019 guide recommended using reputable anti-malware solutions rather than attempting dangerous manual removal that could compromise your system.
Will Fortect remove Google virus?
Fortect scans Windows for malware and unwanted programs and repairs the system files and settings they change, and its free scan shows what it finds on your PC before you decide anything.
For Google virus, follow the plan above as well: the browser steps take back permissions and settings that no scanner treats as a threat, and uninstalling the program that brought it removes the source.
Run Microsoft Defender's full scan and, if anything was found, its offline scan as a second opinion. If the symptoms are gone after the plan and both scans are clean, there is nothing more to do.
Sources
- Wikipedia: Google (read October 5, 2026)
- ZDNet: Google: Malware in Google Play doubled in 2018 because of click-fraud apps (read October 5, 2026)
- Threat Post: 'HoeflerText' Popups Target Browsers With RAT and Locky Ransomware (read October 5, 2026)
- SearchSecurity: Computer exploit (read October 5, 2026)
- Microsoft: Protect yourself from tech support scams (read October 5, 2026)
- Lesvirus: Lesvirus (read October 5, 2026)
- TruGrid: How To Secure Microsoft Remote Desktop Protocol (RDP) and Remote Desktop Services (RDS) (read October 5, 2026)