
SearchMainInfo ads: what it is and how to remove it
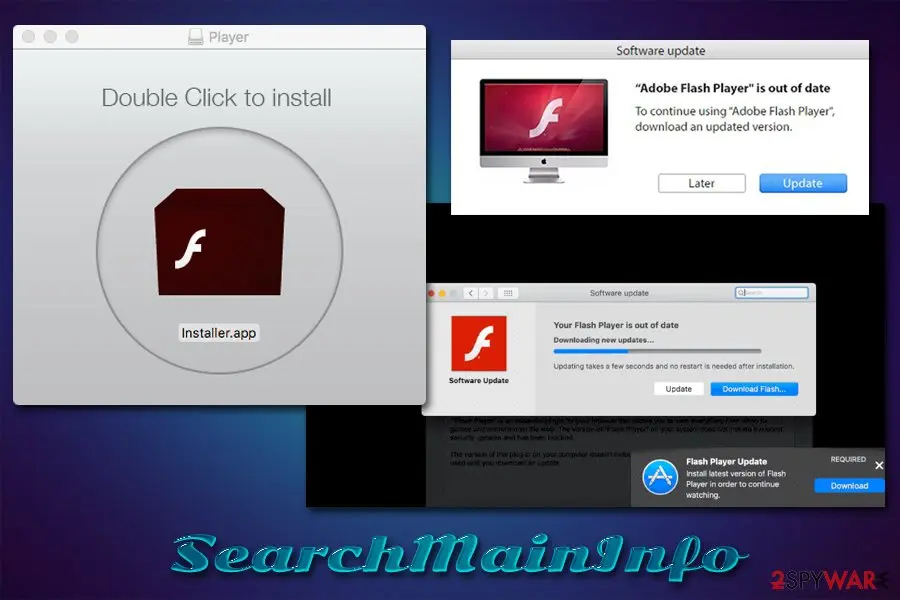
SearchMainInfo is a potentially unwanted application that is typically downloaded via fake Flash Player update prompts or software bundle packages downloaded from insecure torrent websites. The virus belongs to a well-known Adload malware family that includes such apps like MainReady, AgileHelp, IdeaShared, and many others, and targets macOS users exclusively.
Facts checked October 6, 2026. Removal steps checked against Apple's current documentation and the security vendors' reports. We have not run the malware on a Mac. Sections marked as our earlier report are the original text: they describe the threat as it was then and have not been reviewed since. The 2026 status, the removal steps and the questions are current.
Automatic
Get a free scan and check if your Mac is infected.
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds before you decide anything.
If redirects to home.searchpulse.net keep coming back, a free scan can check extensions, programs and browser settings in one pass.
Do it yourself · free Remove SearchMainInfo ads yourself 4 steps, about 12 minutes, no software needed.
Start the steps
SearchMainInfo ads: summary
| Distribution | All applications delivered by this campaign use unfair distribution practices that are more common to malware. Users can get infected after downloading software cracks and similar unsafe software from torrent/warez websites or after being tricked by a fake Flash Player update prompt |
|---|---|
| Name | SearchMainInfo |
| Type | Mac virus, adware, Trojan |
| Malware family | Adload |
| Targeted systems | macOS, Mac OS X |
| Symptoms | SearchMainInfo extension installed on Google Chrome, Safari, or another web browser Homepage and new tab address is set to searchpulse.net or another suspicious URL Unknown applications installed without permission Difficulty when trying to eliminate the extension and other malicious apps Search results are filled with sponsored links and ads Redirects lead to ad-filled, phishing, scam, or malware-laden sites |
| Removal | Scan the Mac with security software to find the malware and anything installed with it. Fortect for Mac scans for malware and unwanted programs. Remove it nowTo use the full-featured product, you have to purchase a license for Fortect. The scan is free. |
Show 9 more facts
| Dangers | Infection of malware such as CrescentCore, sensitive information disclosure to unknown parties/cybercriminals, financial losses, identity theft |
|---|---|
| Detection names | No Microsoft detection name is known |
| Damage | Not recorded in the old report |
| Evidence | 4 write-ups by security sites; details still limited |
| Domains | home.searchpulse.net |
| Ads shown as | Redirects through ad pages |
| Browsers | Chrome, Edge and Firefox |
| First seen | 25 June 2020 |
| Facts checked | 6 October 2026 |
Is SearchMainInfo ads dangerous?
From our report of Jun 2020 · not reviewed since
Mac malware is a serious thereat: learn to avoid unwanted apps that clutter your system and reduce its security
Adware, potentially unwanted programs such as scareware, as well as malware, are increasing threats to Mac systems.
As mentioned above, Adload apps are usually delivered via fake updates. The trick is usually used by malware or scareware developers to make users believe that something is missing from their computers (Adobe Flash) or that the computer is infected with viruses.
Flash Player is an obsolete component currently, as many modern browsers use different technology to display multimedia content. Unfortunately, many are not aware of that and still believe that Flash is needed for certain websites to be displayed.
These claims are nothing but a hoax, and you should never download anything that is offered to like that via the web browser, as you can infect your machine with very nasty malware. Flash Player is being shut down by Adobe at the end of 2020, and no more security updates will be available - just another reason to get rid of this useless plugin.
Additionally, we strongly advise you to stay away from third-party sources that allow you to download pirated software or software cracks. Both of these can be dangerous, so you should always stick to Apple Store or other reputable sites when looking for new apps to install. If you choose third-party sources for your downloads, make sure you always read the installation instructions properly and pick Advanced/Custom settings when prompted.
From our report of Jun 2020 · not reviewed since
SearchMainInfo - adware designed for macOS that also changes web browser settings and reads personal information
SearchMainInfo is a potentially unwanted application that is typically downloaded via fake Flash Player update prompts or software bundle packages downloaded from insecure torrent websites.
The virus belongs to a well-known Adload malware family that includes such apps like MainReady, AgileHelp, IdeaShared, and many others, and targets macOS users exclusively. SearchMainInfo abuses the built-in AppleScript in order to acquire elevated permissions on the system, which would allow the app to read sensitive information and install other malware without permission.
SearchMainInfo gains access to users' computers without permission, hence not everyone can immediately notice it installed. Visually, the PUA appends a browser extension to Safari, Google Chrome, or Mozilla Firefox, which can read such data like passwords collected via the web browser.
Additionally, the developers of the SearchMainInfo virus also monetize on ads by setting the homepage to home.searchpulse.net (in some cases, Yahoo or Safe Finder is used as well) and redirect all searches via akamaihd.net.
As a result, users see pop-ups, in-text links, banners, deals, offers, coupons, and other commercial content on a regular basis. Besides, homepage modification ensures that all the search results are modified, i.e., filled with sponsored links that direct users to random websites. In some cases, however, SearchMainInfo redirects or ads might lead to scam, malware-laden, phishing, spoofing, or another type of malicious websites.
However, web browser modifications and intrusive advertisements are just one of many problems that SearchMainInfo hijack might bring. Since the app abuses built-in scripts, it can grant itself elevated permissions, which would allow it to perform actions without asking for user approval first. Such changes are also often used to prevent SearchMainInfo removal, as multiple malicious .plist files are dropped on the system.
The best way to remove SearchMainInfo is by scanning the machine with powerful anti-malware software. This way, you will be able to eliminate the malicious entries automatically and won't have to dig through files and folders.
Besides, while many users claim that Macs don't need extra protection, security experts advise the complete opposite. Zero-day exploits (software vulnerabilities that have not been patched by Apple yet and exploited in the wild) are prime examples that every macOS needs third-party protection.
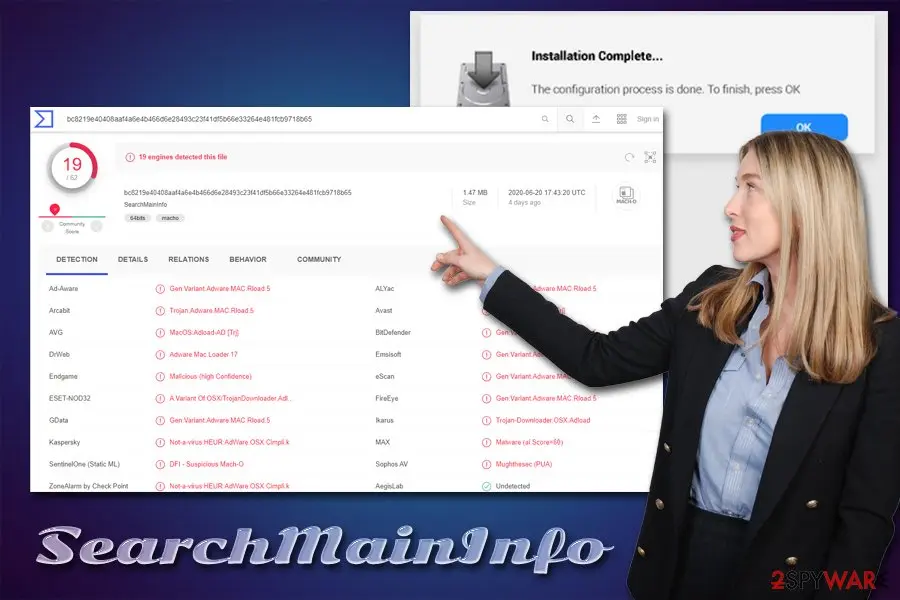
Note that security software is the most efficient way of protecting your computer from viruses. SearchMainInfo can be detected by multiple security vendors as follows:
If you want to get rid of SearchMainInfo manually, we provide the instructions for that as well. In such a case, you are highly recommended resetting all the installed web browsers and scanning the machine with for the best results.
- Gen:Variant.Adware.MAC.Rload.5
- A Variant Of OSX/TrojanDownloader.Adload
- Trojan-Downloader.OSX.Adload
- Not-a-virus:HEUR:AdWare.OSX.Cimpli.k
- Mughthesec (PUA)
- Adware.Mac.Loader.17
From our report of Jun 2020 · not reviewed since
More from our earlier report on SearchMainInfo
- The best way to get rid of malicious applications is by employing a powerful security application such as .
- Adware and malware can oftentimes significantly reduce the performance of the infected computer.
- In case issues arise post-infection, we also recommend resetting the installed web browsers and perform a full system scan with
- Kaspersky security researchers discovered that one in ten Macs are infected with Shlayer Trojan, , and Malwarebytes experts concluded that Mac malware is being developed at a more rapid pace than Windows malware.
Check your browser and PC
- Address:
home.searchpulse.net
How to remove SearchMainInfo ads
How to remove SearchMainInfo from a Mac
Remove the app and what starts it, then check the browsers.
Step 1: Delete apps and downloads you did not intend to install
Open the Applications folder and your Downloads folder. Drag any app you did not install, and any disk image (
.dmg), installer (.pkg) or archive (.zip) that came from SearchMainInfo or a site you do not trust, to the Bin, then empty the Bin.Also check
~/Library/Application Supportfor a folder with the same name as the app you removed.Step 2: Remove unknown login items and background items
Open System Settings > General > Login Items & Extensions. Under Open at Login and Allow in the Background, switch off or remove anything you do not recognize, especially items whose developer is shown as an unknown name or that appeared on the day you ran the command.
Then open Finder, choose Go > Go to Folder and check
~/Library/LaunchAgents,/Library/LaunchAgentsand /Library/LaunchDaemons for property list (.plist) files you did not add. Drag suspicious ones to the Bin, then restart the Mac.Step 3: Check the browsers for extensions and changed settings
In Safari open Settings > Extensions and General (homepage). In Chrome open
chrome://extensions, in Firefoxabout:addons.Remove any extension you did not add, and reset the homepage and search engine if they changed. Browsers hold saved passwords and cookies, which is why the password step comes first.
Step 4: Quit what is running that you do not recognize
Open Activity Monitor (in Applications > Utilities, or search for it with Command + Space).
In the CPU or Network tab, look for a process you did not install or whose name is random, select it, click the stop button (the octagon with an X) and choose Quit or Force Quit.
Note the name first: you will look for the same name in the next steps. Malware that comes back after a restart is handled in the next two steps.
Instructions for each browser and system
The detailed steps for every browser and system this guide covers. Open the one you use.
Remove from Google Chrome
Delete malicious extensions from Google Chrome:
- Open Google Chrome, click on the Menu (three vertical dots at the top-right corner) and select More tools > Extensions.
- In the newly opened window, you will see all the installed extensions. Uninstall all suspicious extensions related to the unwanted program by clicking Remove.

Clear cache and web data from Chrome:
- Click on Menu and pick Settings.
- Under Privacy and security, select Clear browsing data.
- Select Browsing history, Cookies and other site data, as well as Cached images and files.
- Click Clear data.

Change your homepage:
- Click menu and choose Settings.
- Look for a suspicious site in the On startup section.
- Click on Open a specific or set of pages and click on three dots to find the Remove option.
Reset Google Chrome:
If the previous methods did not help you, reset Google Chrome to eliminate all the unwanted components:
- Click on Menu and select Settings.
- In the Settings, scroll down and click Advanced.
- Scroll down and locate Reset and clean up section.
- Now click Restore settings to their original defaults.
- Confirm with Reset settings.

Remove from Mozilla Firefox (FF)
Remove dangerous extensions:
- Open Mozilla Firefox browser and click on the Menu (three horizontal lines at the top-right of the window).
- Select Add-ons.
- In here, select the unwanted extension and click Remove.

Reset the homepage:
- Click three horizontal lines at the top right corner to open the menu.
- Choose Settings.
- Under Home, set your preferred homepage and new tab settings.
Clear cookies and site data:
- Click Menu and pick Settings.
- Go to Privacy & Security section.
- Scroll down to locate Cookies and Site Data.
- Click on Clear Data...
- Select Cookies and Site Data and Temporary cached files and pages, then click Clear.

Reset Mozilla Firefox
If clearing the browser as explained above did not help, reset Mozilla Firefox:
- Open Mozilla Firefox browser and click the Menu.
- Go to Help and then choose Troubleshooting Information.

- Under Give Firefox a tune up section, click on Refresh Firefox...
- Once the pop-up shows up, confirm the action by pressing on Refresh Firefox.

Delete from Safari
If you could not eliminate the browser extension successfully, you can reset Safari to get rid of it:
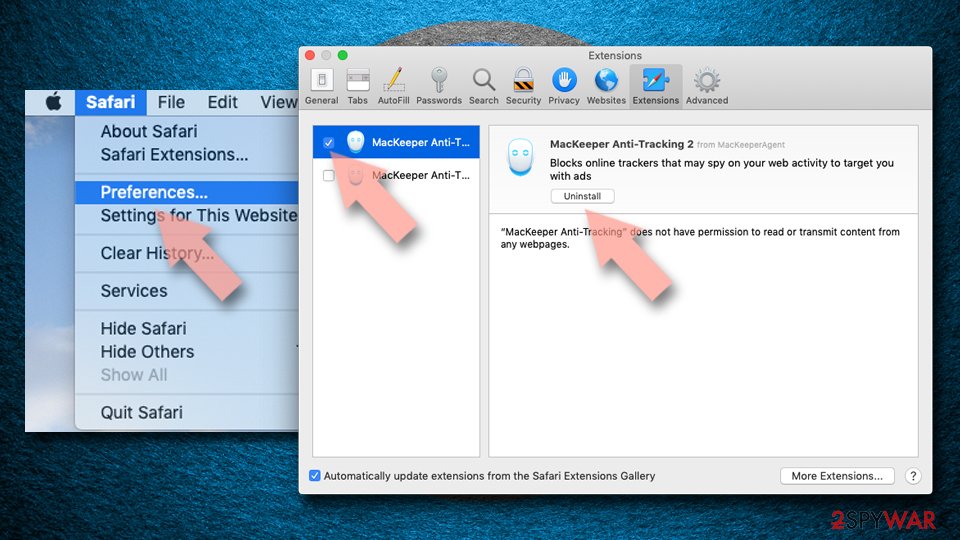
Remove dangerous extensions:
- Open Safari, click Safari in the menu at the top-left of the screen, and select Preferences.
- Go to the Extensions tab, look for any suspicious entries, and click Uninstall to remove them.
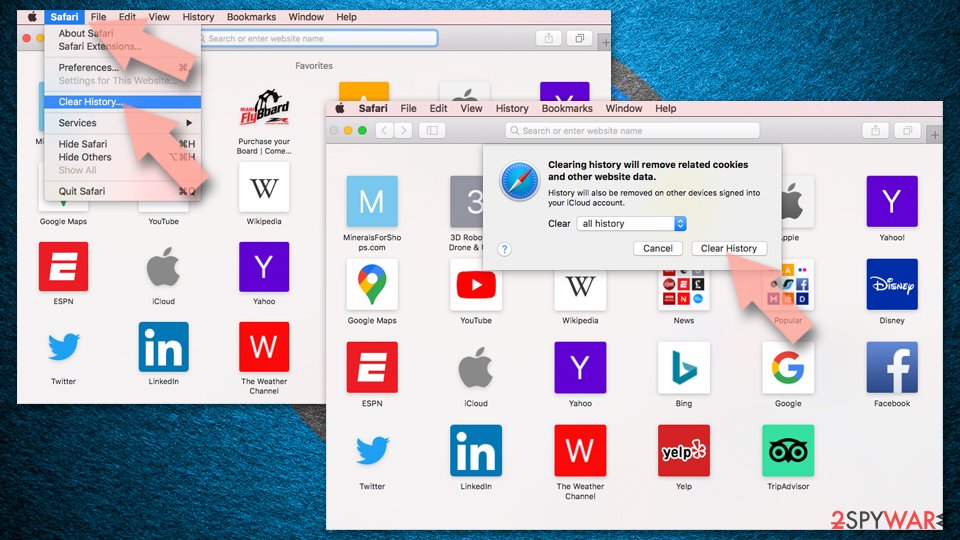
Clear history and website data:
- Click Safari in the menu and pick Clear History.
- Set Clear to all history and confirm with Clear History.
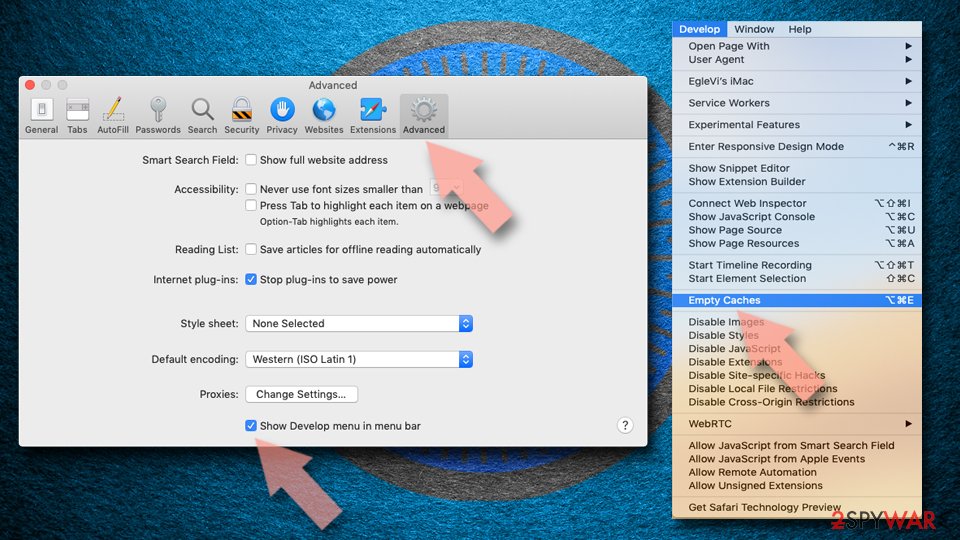
Reset Safari:
- Click Safari in the menu and select Preferences > Advanced.
- Enable Show Develop menu in menu bar.
- From the menu bar, click Develop and select Empty Caches.
Delete from macOS
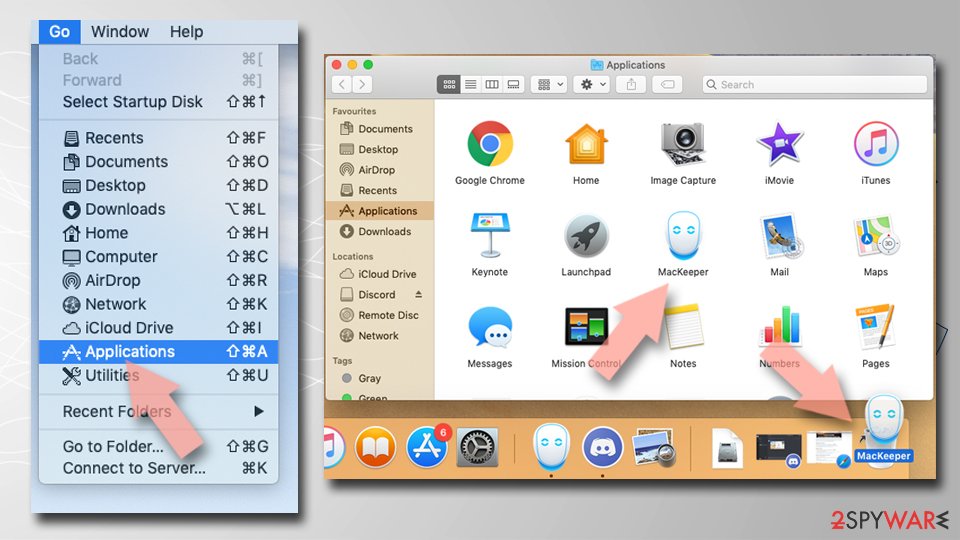
To get rid of unwanted apps on macOS, place it in Trash:
Remove the unwanted application:
- From the menu bar, select Go > Applications.
- In the Applications folder, look for any suspicious entries, then drag them to Trash (or right-click and pick Move to Trash).
Delete leftover files and folders:
- Select Go > Go to Folder.
- Enter /Library/Application Support and remove any suspicious folders related to the unwanted program.
- Repeat the same check in the /Library/LaunchAgents and /Library/LaunchDaemons folders, deleting any suspicious entries.
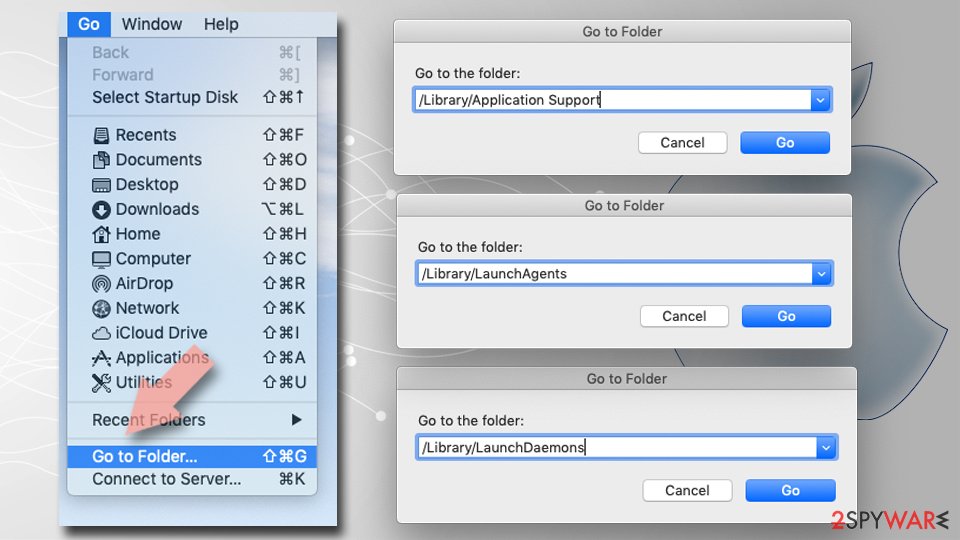
- Finally, empty the Trash to permanently remove the leftovers.
Do not let government spy on you
The government has many issues in regards to tracking users' data and spying on citizens, so you should take this into consideration and learn more about shady information gathering practices.
Avoid any unwanted government tracking or spying by going totally anonymous on the internet.
You can choose a different location when you go online and access any material you want without particular content restrictions. You can easily enjoy internet connection without any risks of being hacked by using VPN.
Control the information that can be accessed by government any other unwanted party and surf online without being spied on. Even if you are not involved in illegal activities or trust your selection of services, platforms, be suspicious for your own security and take precautionary measures by using the VPN service.
Backup files for the later use, in case of the malware attack
Computer users can suffer from data losses due to cyber infections or their own faulty doings.
Ransomware can encrypt and hold files hostage, while unforeseen power cuts might cause a loss of important documents. If you have proper up-to-date backups, you can easily recover after such an incident and get back to work. It is also equally important to update backups on a regular basis so that the newest information remains intact - you can set this process to be performed automatically.
When you have the previous version of every important document or project you can avoid frustration and breakdowns. It comes in handy when malware strikes out of nowhere. Use for the data restoration process.
From our report of Jun 2020 · not reviewed since
Get rid of SearchMainInfo and other malicious apps
As mentioned above, it is best to avoid computer infections in the first place, so you would not have to deal with SearchMainInfo removal and its consequences.
To remove SearchMainInfo, you can employ reputable anti-malware software and perform a full system scan - we suggest using or . This way, you will be able to eliminate all the unwanted and leftover components automatically.
Nonetheless, if you do not wish to install other apps on your Mac, you can also uninstall the SearchMainInfo virus manually as well. For that, you should access the following locations and delete all the malicious files:
To ensure that the elimination of the extension is also successful, you should reset all the installed web browsers, as we explain below.
- System Preferences > Accounts> Login Items
- System Preferences > Users&Groups > Profiles
- ~/Library/LaunchAgents
- ~/Library/Application Support
- ~/Library/LaunchDaemons
Questions about SearchMainInfo ads
Why does my browser keep going to home.searchpulse.net?
Something is sending it there. On one site only, that site's ads are the cause and leaving the site ends it.
On many different sites, the usual causes are an extension you installed with something else, a site you once allowed to send notifications, or an ad-supported program in Windows that changes how the browser behaves. home.searchpulse.net itself is only a stop on the way: it records the visit and forwards you to whatever advertiser pays most.
Check the extensions page, then the list of sites allowed to send notifications, then Installed apps sorted by date. Removing the cause stops the redirects; blocking the domain alone usually does not, because the network moves to a new one.
Should I worry about redirects to home.searchpulse.net?
Worry less about home.searchpulse.net itself and more about what keeps sending you there. A single redirect from a free streaming or download site is normal and harmless once the tab is closed.
Repeated redirects on sites that used to work fine mean something in the browser or in Windows changed, often an extension or program installed alongside other software. It may also collect the pages you visit. Remove the cause with the steps in this guide, and do not act on anything the redirected pages ask:
- no Allow clicks
- no downloads
- no calls
If you already did one of those, the matching section of this guide explains what to do next.
Why does SearchMainInfo show me ads?
Because that is its whole purpose. SearchMainInfo is an adware extension, and its operators are paid for every ad it displays and every click it gets. In this case the ads take the form of redirects through ad pages.
They are chosen by ad networks that accept almost any advertiser, which is why so many look like warnings or prizes. The ads are not a sign that your PC is broken or infected with something worse; they are a sign that something on it, or in the browser, has permission to advertise. Removing that permission or program stops them.
Do I have to clean every browser?
Yes, if you use more than one. We saw SearchMainInfo in Chrome, Edge and Firefox, and each browser keeps its own extensions, notification permissions and settings. Chrome and Edge share the same extension format, so one installer can add the same adware to both, while Firefox has its own add-ons.
Check every browser on the PC, including ones you rarely open. If you sync a browser with an account, clean it while signed in, so that the removal reaches your other computers rather than the adware returning from them.
How do I know the ads come from SearchMainInfo?
Look for redirects to home.searchpulse.net. That is the trace SearchMainInfo leaves, and it shows up as redirects through ad pages. Ads that appear on every site, including ones that never carried ads before, point to something on your PC or in the browser rather than to the sites themselves.
A quick test is a private window, where extensions are off by default: if the ads disappear there, an extension is responsible. If they appear even with the browser closed, the source is a notification permission or a program in Windows.
An ad showed a phone number and I called it. What now?
The number belongs to scammers, not to Microsoft or an antivirus company. If you only talked, hang up and do not call back. If you let them connect to the PC, disconnect it from the internet, uninstall the remote access program they used, such as AnyDesk, TeamViewer, ScreenConnect or UltraViewer, and run a full and offline scan.
If you paid or gave bank details, call your bank at once on the number printed on your card. Change any passwords you typed while they were connected, and report the call.
I clicked on one of the ads. Am I infected?
Probably not. Clicking an ad usually only opens a page, and a page cannot install programs on an up-to-date Windows PC without your help.
You are at risk only if you then downloaded and ran a file, allowed notifications, entered card or login details, or called a phone number shown on the page. Delete any download and run a full and offline scan.
Change passwords you typed, from a clean device. Call your bank if you gave card details. If you called a number or allowed remote access, see the next question.
Does adware steal passwords?
Ordinary adware is built to show ads, not to steal logins, and most of it never touches saved passwords. The line is blurry, though. Extensions that can read every page could capture what you type, and adware ads sometimes lead to phishing pages that ask for passwords directly.
If you entered credentials on a page reached through an ad, change that password from a clean device and turn on two-step verification. Otherwise, removing adware extension and clearing cookies is usually enough.
Can adware slow down my PC?
Yes. Adware runs in the background, loads ad scripts, opens extra tabs and contacts its servers, all of which use processor time, memory and bandwidth. Ad-heavy extensions also slow down every page, because they inspect and change it before you see it.
The effect is strongest on older PCs and when several adware programs arrived together. After removal, restart the PC and check Task Manager for anything still using a lot of resources that you do not recognise. Speed usually returns to normal once the ads stop.
Will Fortect remove SearchMainInfo?
Fortect for Mac scans for malware and unwanted programs, and its free scan shows what it finds on your Mac before you decide anything.
For SearchMainInfo, follow the plan on this page as well: removing a launch item or an app is done in macOS itself, and a scanner cannot undo what was typed or entered on the infected Mac, such as saved passwords that were copied.
Change your passwords from another device first, and if the page tells you to erase the Mac, a scan is not a substitute. The free scan costs nothing and the full-featured product needs a license.
Sources
- Intego: Do Macs need antivirus software? (read October 6, 2026)
- Virus Total: bc8219e40408aaf4a6e4b466d6e28493c23f41df5b66e33264e481fcb9718b65 (read October 6, 2026)
- Kaspersky: Shlayer Trojan attacks one in ten macOS users (read October 6, 2026)
- Google Chrome Help: Use notifications to get alerts (no longer online) (read October 6, 2026)
- FTC: How to recognize, remove and avoid malware (read October 6, 2026)