
Viruses · 307 guides

Trojans removal guides, page 11 of 12

Hidden programs that give attackers remote access, and how to find and remove them.
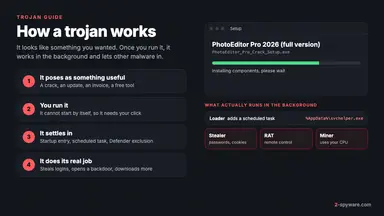
Start hereWhat is a trojan and how to remove itA trojan is malware disguised as something you wanted, such as a cracked program, a fake update or an invoice. It does nothing until you run it, then steals passwords, gives a stranger remote access or downloads more malware. To remove it, cut the startup entries it added, run a full and an offline scan, then change your passwords from a clean device.

Most searched trojans guides

  1. 1Remove Csrss.exe trojan
  2. 2Remove Memz virus
  3. 3Remove Wcupdater
  4. 4Remove Win32/Lodi
  5. 5Remove Chrome.7z
  6. 6Remove Iplogger.org

Trojans removal guides 271–297 of 307

Remove HM Revenue & Customs Outstanding Amount virus

HM Revenue & Customs Outstanding Amount virus is a scam email message that delivers TrickBot banking trojan HMRC virus is a malspam campaign recently spotted by security researchers. The fakeTrojansHigh riskOlivia Morelli ·

Remove RegBack Trojan

RegBack is a Trojan horse which might infiltrate the system with malware RegBack Trojan is a dangerous computer infection which can infect the system without user's notice. Usually, this typeTrojansHigh riskJake Doevan ·

Remove Trojan:Win32/Bluteal.B!rfn

Trojan:Win32/Bluteal.B!rfn - a false positive by Windows Defender, although users should not let their guard down Trojan:Win32/Bluteal.B!rfn might be a malicious application that infected your machine without you noticing, suchTrojansHigh riskAlice Woods ·

Remove Assasin Trojan

Assasin Trojan is dangerous malware that steals your personal data Assasin Trojan is a malicious application that aims to take over targeted victim's device. Trojan horses[ref en-1] are especially dangerousTrojansHigh riskJulie Splinters ·

Remove Trojan.AOL.WAOL

Trojan.AOL.WAOL is a Trojan horse which operates under the name of the legitimate America Online telecommunications company Trojan.AOL.WAOL is a virus which is also categorized as a Trojan horse. ThisTrojansHigh riskJake Doevan ·

Remove Betabot virus

BetaBot - a trojan with an enhanced list of features Betabot is a malicious trojan that shifted its functionality throughout the years. It was first spotted in March 2013 withTrojansHigh riskJulie Splinters ·

Remove JS:ScriptIP-inf [Trj]

JS:ScriptIP-inf - a trojan horse that can be used for malicious activities JS:ScriptIP-inf is a malicious program that operates as a trojan horse. It means that this cyber threat mightTrojansHigh riskUgnius Kiguolis ·

Remove Trojan-spy.win32.agent

Trojan-spy.win32.agent.gen - dangerous malware that can be untraceable for a long time Trojan-spy.win32.agent is a generic name that describes a group of dangerous trojan horses that can perform malicious activitiesTrojansHigh riskAlice Woods ·

Remove CryptoShuffler Trojan

CryptoShuffler - a silent crypto-jacking trojan CryptoShuffler[ref en-1] is a Trojan horse which was first spotted in 2016. The malicious program is used for stealing money by changing cryptocurrency[ref en-2]TrojansHigh riskOlivia Morelli ·

Remove Ethdcrminer64

Ethdcrminer64 is a virus that mines various cryptocurrencies on users' machines for cybercriminals Ethdcrminer64 is a crypto-miner that is dedicated to mine[ref en-1] digital currency using targeted machines. The cryptocurrencyTrojansHigh riskLinas Kiguolis ·

Remove Panda Banker

Panda Banker Trojan switches its target to Japanese institutions Panda Banker is a Trojan horse, which has been released in 2016. It's based on the Zeus Trojan, which has beenTrojansHigh riskJake Doevan ·

Remove JackServn Trojan

JackServn is a trojan that might irreversibly harm your computer JackServn Trojan[ref en-1] is a dangerous computer threat which might be programmed to perform multiple malicious actions to harm victim'sTrojansHigh riskJake Doevan ·

Remove Drive.bat virus

Drive.bat virus is a dangerous Trojan horse which is capable of damaging victim's data and making it useless Drive.bat virus is a malicious cyber infection classified as a Trojan horse.[refTrojansHigh riskOlivia Morelli ·

Remove Relieve Stress Paint

Relieve Stress Paint - freeware that hides Stresspaint Trojan Relieve Stress Paint is a free tool that pretends to be a painting program for kids and adults that contain MandalaTrojansHigh riskOlivia Morelli ·

Remove Trojan:vbs/mutuodo.a

Trojan:vbs/mutuodo.a is a malicious Trojan horse related to PriceFountain adware Trojan:vbs/mutuodo.a is a malicious file that is recognized as a Trojan horse[ref en-1] by most of the reputable AV-Engines. WindowsTrojansHigh riskJake Doevan ·

Remove Trojan:BAT/Poweliks.A

Trojan:BAT/Poweliks.A is a detection of a malicious Poweliks Trojan Trojan:BAT/Poweliks.A is a name of a Trojan[ref en-1] horse returned to PC users by an AV-engine. This name can be usedTrojansHigh riskJulie Splinters ·

Remove Torpig

Torpig - a malicious Trojan Horse that can steal sensitive data   Torpig is a severely malicious Trojan Horse,[ref en-1] which has been revealed in 2005. Since then, cybersecurity expertsTrojansHigh riskLucia Danes ·

Remove TrojanDownloader:PowerShell/Falsip.A

TrojanDownloader:PowerShell/Falsip.A is designed to download malware on your computer TrojanDownloader:PowerShell/Falsip.A is a detection of a Trojan Horse[ref en-1] by Microsoft Windows Defender. Programs with Trojan-like features are capable of multipleTrojansHigh riskAlice Woods ·

Remove Small.CA virus

Small.CA aims to infect computers with Windows OS Small.CA virus belongs to the category of trojans that are designed to work as backdoors to infiltrate malware, and monitor user's browsing behaviorTrojansHigh riskUgnius Kiguolis ·

Remove Fake Adobe Flash Player install

Fake Adobe Flash Player install spreads malicious programs Fake Adobe Flash Player install or update pop-up might show up on the screen out of nowhere. While Flash Player is aTrojansHigh riskGabriel E. Hall ·

Remove Cloud Packager virus

Cloud Packager miner hides under the names of Windows processes Cloud Packager is a Trojan horse that is designed to mine digital currency (Bitcoin, Monero, Dashcoint, etc.) by using affectedTrojansHigh riskLinas Kiguolis ·

Remove Shadowsocks Miner

Shadowsocks CPU Trojan aims to leverage your CPU power to mine cryptocurrency Shadowsocks Miner is a malicious computer virus classified as a Trojan[ref en-1]. It was developed for unacceptable purposeTrojansHigh riskUgnius Kiguolis ·

Remove Trojan.Pidief.x

Trojan.Pidief.X malware links to ransomware Trojan.Pidief.X virus defines a computer virus, specifically, a trojan horse. Regarding its original purpose, it behaves the same way in the cyber space. It isTrojansHigh riskLinas Kiguolis ·

Remove Poweliks virus

Poweliks virus is a fileless infection that is hard to remove Powerliks virus (also known as Trojan.Poweliks, Trojan.Poweliks!gm, etc.) is a dangerous trojan horse[ref en-1]. Unlike regular viruses, it doesTrojansHigh riskLucia Danes ·

Remove GameOver Zeus

GameOver Zeus is used for stealing financial data and spreading CryptoLocker ransomware GameOver Zeus is a Trojan that is based on Zeus trojan that has first emerged in 2006. ThenTrojansHigh riskUgnius Kiguolis ·

Remove Magala virus

Magala Trojan exploits victim's computer to generate pay-per-click revenue Magala Trojan is a computer virus that targets Windows OS and uses virtual desktops to click on ads in search results.TrojansHigh riskGabriel E. Hall ·

Remove Neutrino virus

Neutrino virus points its daggers to point-of-sale terminals Neutrino virus functions as a newly detected version of notorious Zeus virus which targets Windows OS. Indeed, there is the exploit kit operatingTrojansHigh riskLinas Kiguolis ·
5,558 members already hereReading, writing, commenting and voting. 0 verified · 283 joined this year