
Viruses · 307 guides

Trojans removal guides, page 9 of 12

Hidden programs that give attackers remote access, and how to find and remove them.
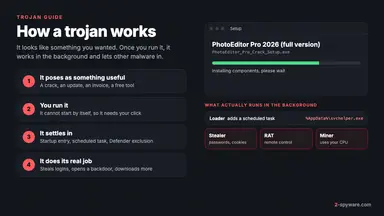
Start hereWhat is a trojan and how to remove itA trojan is malware disguised as something you wanted, such as a cracked program, a fake update or an invoice. It does nothing until you run it, then steals passwords, gives a stranger remote access or downloads more malware. To remove it, cut the startup entries it added, run a full and an offline scan, then change your passwords from a clean device.

Most searched trojans guides

  1. 1Remove Csrss.exe trojan
  2. 2Remove Memz virus
  3. 3Remove Wcupdater
  4. 4Remove Win32/Lodi
  5. 5Remove Chrome.7z
  6. 6Remove Iplogger.org

Trojans removal guides 217–243 of 307

Remove BV:Miner-T

BV:Miner-T is a dangerous crypto-mining virus that abuses victims' devices to gain profit BV:Miner-T is the threat that targets inadequately secured websites and implements cryptocurrency mining by injecting malicious scripts.TrojansHigh riskJake Doevan ·

Remove JS Downloader Virus

JS Downloader virus is a trojan which uses JavaScript to get into systems undetected JS Downloader is a detection of the malware that uses JavaScript code execution and is oftenTrojansHigh riskJulie Splinters ·

Remove Sirefef

Sirefef - prolific malware that seeks to open a backdoor on the host machine Sirefef, or otherwise known as ZeroAccess or max++, is a malware-dropper that is known for itsTrojansHigh riskGabriel E. Hall ·

Remove Skeleton-Key

Skeleton Key is dangerous malware that targets 64-bit Windows machines that are protected with a single-factor authentication method Skeleton Key is a Trojan that mainly attacks corporate networks by bypassingTrojansHigh riskGabriel E. Hall ·

Remove Nodersok malware

Nodersok is the fileless malware that turns systems into proxies to perform click-fraud Nodersok malware is the Trojan already known for its malicious campaigns on thousands of computers. The malwareTrojansHigh riskGabriel E. Hall ·

Remove Apex Legends virus

Apex Legends virus is the remote access tool that disguises as Apex Legends video game cheats and related files online Apex Legends virus is the term used to describe viruses,TrojansHigh riskAlice Woods ·

Remove Clipboard virus

Clipboard virus is an extremely dangerous cryptocurrency virus that is misusing Clipboard to steal people's funds Clipboard virus is the malware used to get profit to criminals from fraudulent cryptocurrencyTrojansHigh riskGabriel E. Hall ·

Remove GozNym virus

GozNym virus is the banking malware targeting businesses and financial institutions in various countries since 2016 GozNym virus is a modified trojan that uses two known malicious programs to stealTrojansHigh riskJake Doevan ·

Remove Varenyky virus

Varenyky virus – spam email campaign that distributes malware on French-based devices via infected Microsoft Word documents Varenyky virus is the trojan that targets French people and records victims' screen. ThisTrojansHigh riskJulie Splinters ·

Remove HTML:RedirME-inf

HTML:RedirME-inf is a false positive by Avast or AVG anti-virus, although it might indicate malware HTML:RedirME-inf is a detection name for a potentially malicious threat when users visit particular websites,TrojansHigh riskOlivia Morelli ·

Remove Alureon

Alureon is a persistent Trojan used to steal data and inject malicious pieces on the system too Alureon is a relatively old cyber threat - it was first spotted byTrojansHigh riskJake Doevan ·

Remove Bitcoin Collector

Bitcoin Collector is the malicious tool that gets advertised as a useful application for generating Bitcoins Bitcoin Collector is the trojan that runs a cryptocurrency generator and distributes additional malwareTrojansHigh riskLinas Kiguolis ·

Remove Fuerboos

Fuerboos is a malicious trojan virus that might steal your banking details and login data, although might also be a false positive Fuerboos trojan is a generic name used byTrojansHigh riskGabriel E. Hall ·

Remove Kovter.C virus

Kovter.C virus is the trojan that performs click-fraud while running on victims computer and using resources Kovter.C is the malware that gets installed on the machine without users permission andTrojansHigh riskGabriel E. Hall ·

Remove Baldr malware

Baldr malware – a trojan that is linked to Russian underground hackers   Baldr malware is a new, cross-platform information-stealing trojan that captures valuable information including passwords and important files. TheTrojansHigh riskUgnius Kiguolis ·

Remove Atilla stealer

Atilla stealer is a Remote Access Trojan that runs in the machine's background and might relate in data theft Atilla stealer is described as a RAT (Remote Access Trojan)[ref en-3]TrojansHigh riskOlivia Morelli ·

Remove NetSupport Manager

NetSupport Manager is a legitimate remote management tool that can be used as a RAT by cybercriminals NetSupport Manager is a cross-platform commercial application that was developed by NetSupport Limited. Initially, itTrojansHigh riskJake Doevan ·

Remove Anubiscrypt ransomware

Anubiscrypt ransomware - is a file locking malware that targets Android users Anubiscrypt ransomware is a file locker that not only locks up personal data by appending .AnubisCrypt file extensionRansomwareHigh riskAlice Woods ·

Remove Trojan.Gen.MBT

Trojan.Gen.MBT is a generic term used to describe malware that comes from Trojan family Trojan.Gen.MBT is a Trojan horse and a type of malware that disguises itself as a usefulTrojansHigh riskJake Doevan ·

Remove Paypal-b Phish

Paypal-b Phish is a well-known false positive that is related to PayPal payment service Paypal-b Phish, also known as HTML:Paypal-B [Phish], is a detection used by AVG and Avast security applications.TrojansHigh riskLucia Danes ·

Remove Trochilus virus

Trochilus virus is a dangerous Remote Access Trojan that was used in Myanmar's political cyber-espionage campaign Trochilus virus is a type of malware that enters the device without any signs,TrojansHigh riskJulie Splinters ·

Remove FedEx tracking email virus

FedEx tracking virus is a malspam campaign that infects users' computers with the dangerous data-stealer Hancitor trojan FedEx tracking email virus is a phishing email strain that is delivered toTrojansHigh riskJulie Splinters ·

Remove RogueRobin trojan horse

RogueRobin trojan horse - malware which has been carried out by DarkHydrus APT RogueRobin trojan horse[ref en-1] is an infamous computer virus which has been developed by a cybercriminal groupTrojansHigh riskJake Doevan ·

Remove PayPal virus

PayPal virus is a phishing campaign when scammers hide the malicious purpose behind a safe-looking email message PayPal virus is a scam which is designed to stealthily infect systems withTrojansHigh riskJulie Splinters ·

Remove LamePyre virus

LamePyre virus is a Mac trojan that disguises itself as Discord messaging app LamePyre virus is a limited functionality trojan that was discovered by security researchers at the end ofMac VirusesMedium riskJulie Splinters ·

Remove Flashback virus

Flashback virus - a malicious Trojan horse which targets Mac OS X users Flashback virus, also known as OSX.Flashback, Fakeflash, Flashback trojan, or Trojan BackDoor.Flashback. This fraudulent Trojan horse[ref en-4]TrojansHigh riskAlice Woods ·

Remove KingMiner

KingMiner is a cryptojacking trojan that loads a background process with a different name to conceal the malicious Monero mining activity KingMiner trojan is a malware that generates cryptocurrency whileTrojansHigh riskUgnius Kiguolis ·
5,558 members already hereReading, writing, commenting and voting. 0 verified · 283 joined this year